> ## Documentation Index
> Fetch the complete documentation index at: https://notes.kodekloud.com/llms.txt
> Use this file to discover all available pages before exploring further.
# What are Containers
> Explains Linux containers, kernel isolation using namespaces and cgroups, benefits like portability and efficiency, and the container ecosystem including Docker, containerd, runc and OCI standards.
Containers are lightweight, isolated user-space environments provided by the host operating system. Each container can run its own processes, expose its own network interfaces, and mount filesystems independently — much like a virtual machine — but all containers on a host share the same OS kernel. This isolation is implemented by Linux kernel primitives such as namespaces (process, network, mount, user) and cgroups (resource control for CPU, memory, I/O).
Containers provide process-level isolation on top of a shared kernel — they are not full virtual machines with separate kernels.
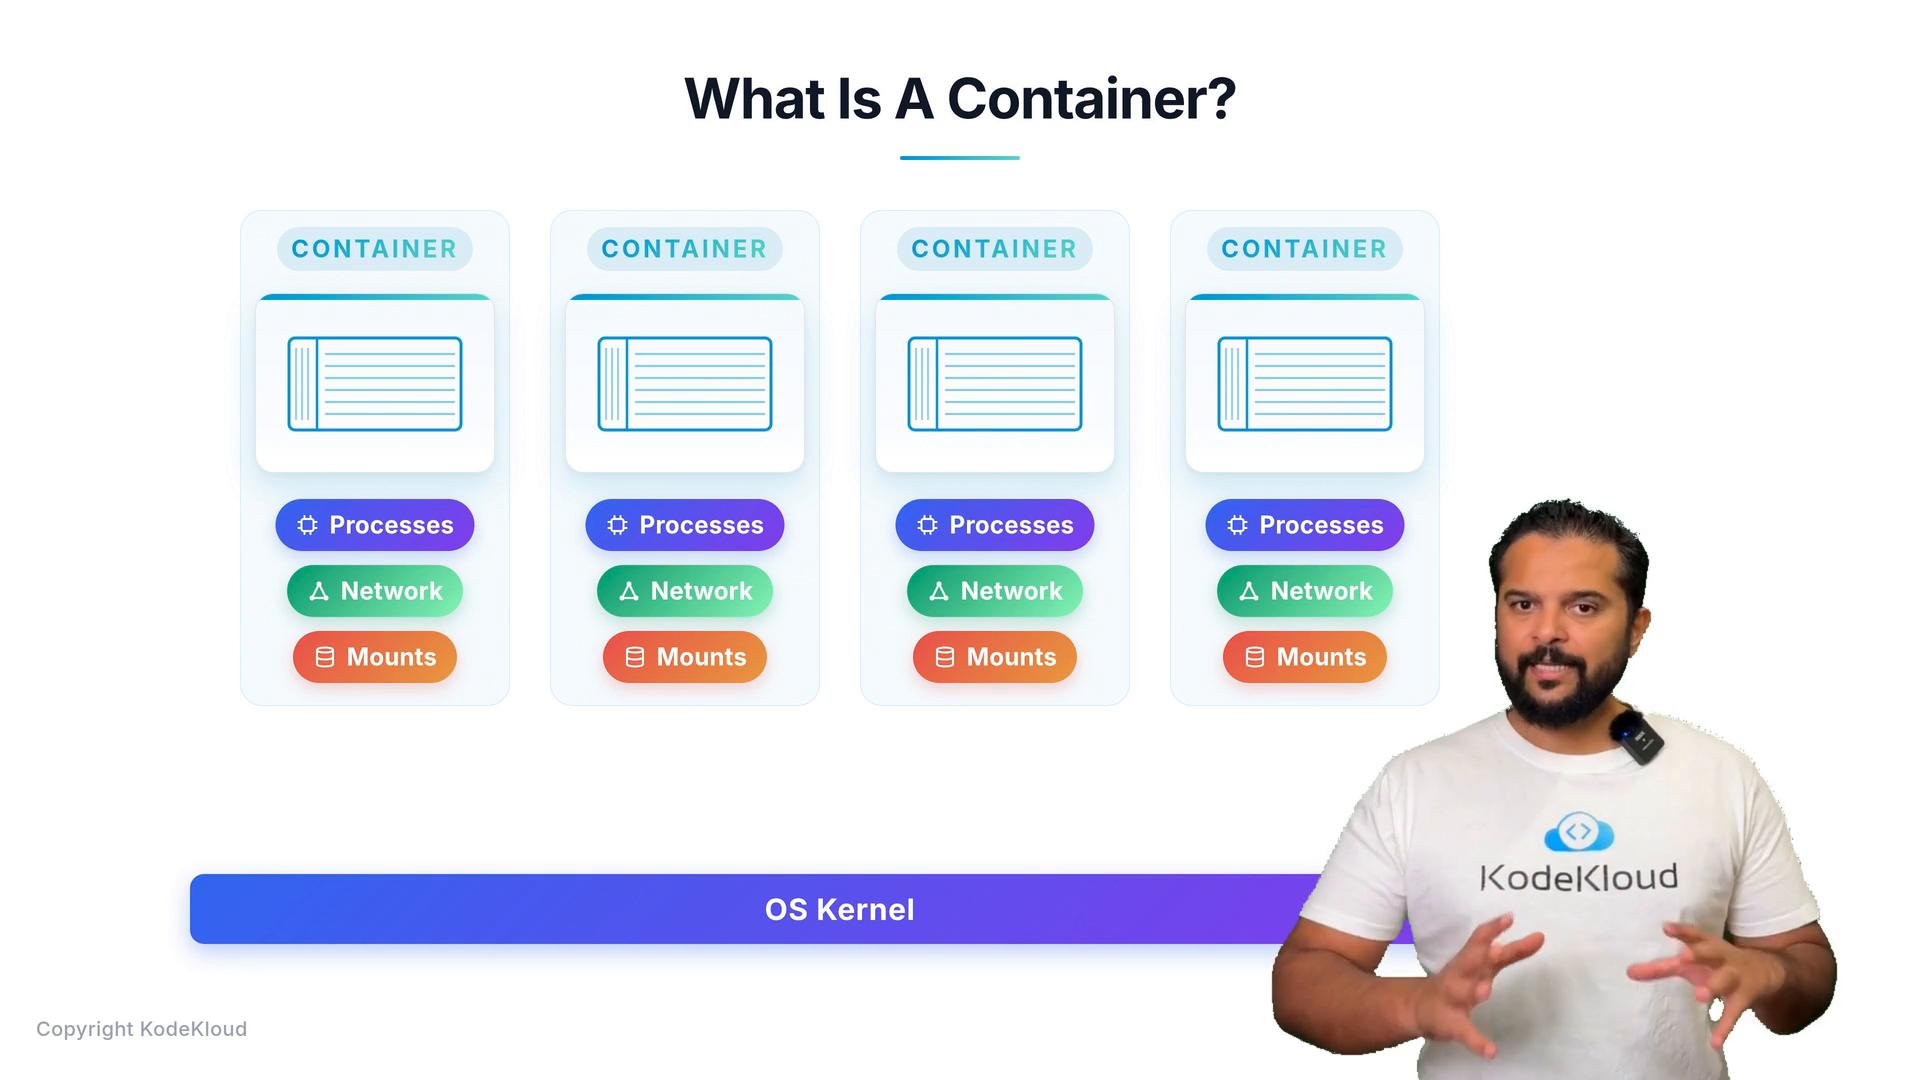 Why this matters
* Lower overhead: Containers share the kernel, so they require less CPU, memory, and disk than full VMs.
* Faster startup: Containers can start in seconds because they don't boot a separate kernel.
* Portability: Container images bundle application code and runtime dependencies, making them portable across environments that run the same container runtime.
Linux kernel features that enable containers
| Kernel feature | Purpose | Example |
| - | -: | - |
| Namespaces | Isolate kernel resources — processes, network, mounts, and users | Process PID isolation with `pid` namespace |
| cgroups (control groups) | Limit and account for resource usage — CPU, memory, block I/O | Restrict memory with `memory.limit_in_bytes` |
| chroot / mount namespaces | Provide per-container filesystem views and mounts | Mount container root filesystem without affecting host |
Container runtime and image ecosystem
Linux container technology has evolved through multiple implementations and standards. Below is a compact overview of notable projects and how they relate:
| Project | Role | Notes |
| - | -: | - |
| [LXC](https://linuxcontainers.org/lxc/) | Early Linux containers implementation | Lightweight OS-level virtualization predating modern container tooling |
| [LXD](https://linuxcontainers.org/lxd/) | System container manager | Higher-level manager built on LXC for system containers |
| [LXCFS](https://linuxcontainers.org/lxcfs/) | Filesystem helpers for container visibility | Improves /proc and other pseudo-filesystem behavior inside containers |
| [Docker](https://www.docker.com/) | Developer-friendly container tooling | Initially used LXC, later introduced its own runtime stack |
| `libcontainer` → `runc` | Low-level OCI runtime | `runc` is the reference implementation of the Open Container Initiative (OCI) runtime spec |
| [containerd](https://containerd.io/) | Container runtime daemon | Manages container lifecycle; used by modern Docker with `runc` for execution |
| OCI (Open Container Initiative) | Standardization body | Defines runtime and image format specifications for interoperability |
A short history and modern stack
* Early: LXC provided the initial Linux container primitives.
* Mid: Docker emerged as an easy-to-use tool for building and distributing container images; it originally used LXC.
* Later: Docker moved to `libcontainer`, which evolved into `runc`. The Open Container Initiative (OCI) standardized runtime and image formats.
* Today: Docker typically uses `containerd` (daemon) + `runc` (OCI runtime) under the hood to create and manage containers.
If you want to work directly with low-level primitives, you can explore LXC/LXD. For application development and distribution, Docker and OCI-compliant runtimes (containerd + runc) are the common choice.
Why use Docker (or similar tooling)?
* Simplifies image creation and distribution with registries.
* Provides a high-level CLI and API for building, running, and managing containers.
* Abstracts complex setup of namespaces, cgroups, and filesystem mounts so developers can focus on applications.
Further reading and references
* [Open Container Initiative (OCI)](https://opencontainers.org) — runtime and image format specifications
* [Docker](https://www.docker.com/) — container platform for building and running containerized apps
* [containerd](https://containerd.io/) — runtime daemon used by Docker and other platforms
* [LXC / LXD](https://linuxcontainers.org/) — alternative system container technologies
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.