> ## Documentation Index
> Fetch the complete documentation index at: https://notes.kodekloud.com/llms.txt
> Use this file to discover all available pages before exploring further.

# GitOps for Application Environments

> Practical GitOps patterns for promoting applications across development, testing, staging, and production, covering environment design, repository strategies, configuration management, security, and observability.

<Callout icon="lightbulb" color="#1CB2FE">
  This lesson covers GitOps patterns for application environment promotion, environment design, repository strategies, configuration management, security, and monitoring. These are practical platform-engineering patterns to enable safe, auditable, and repeatable promotion from development to production.
</Callout>

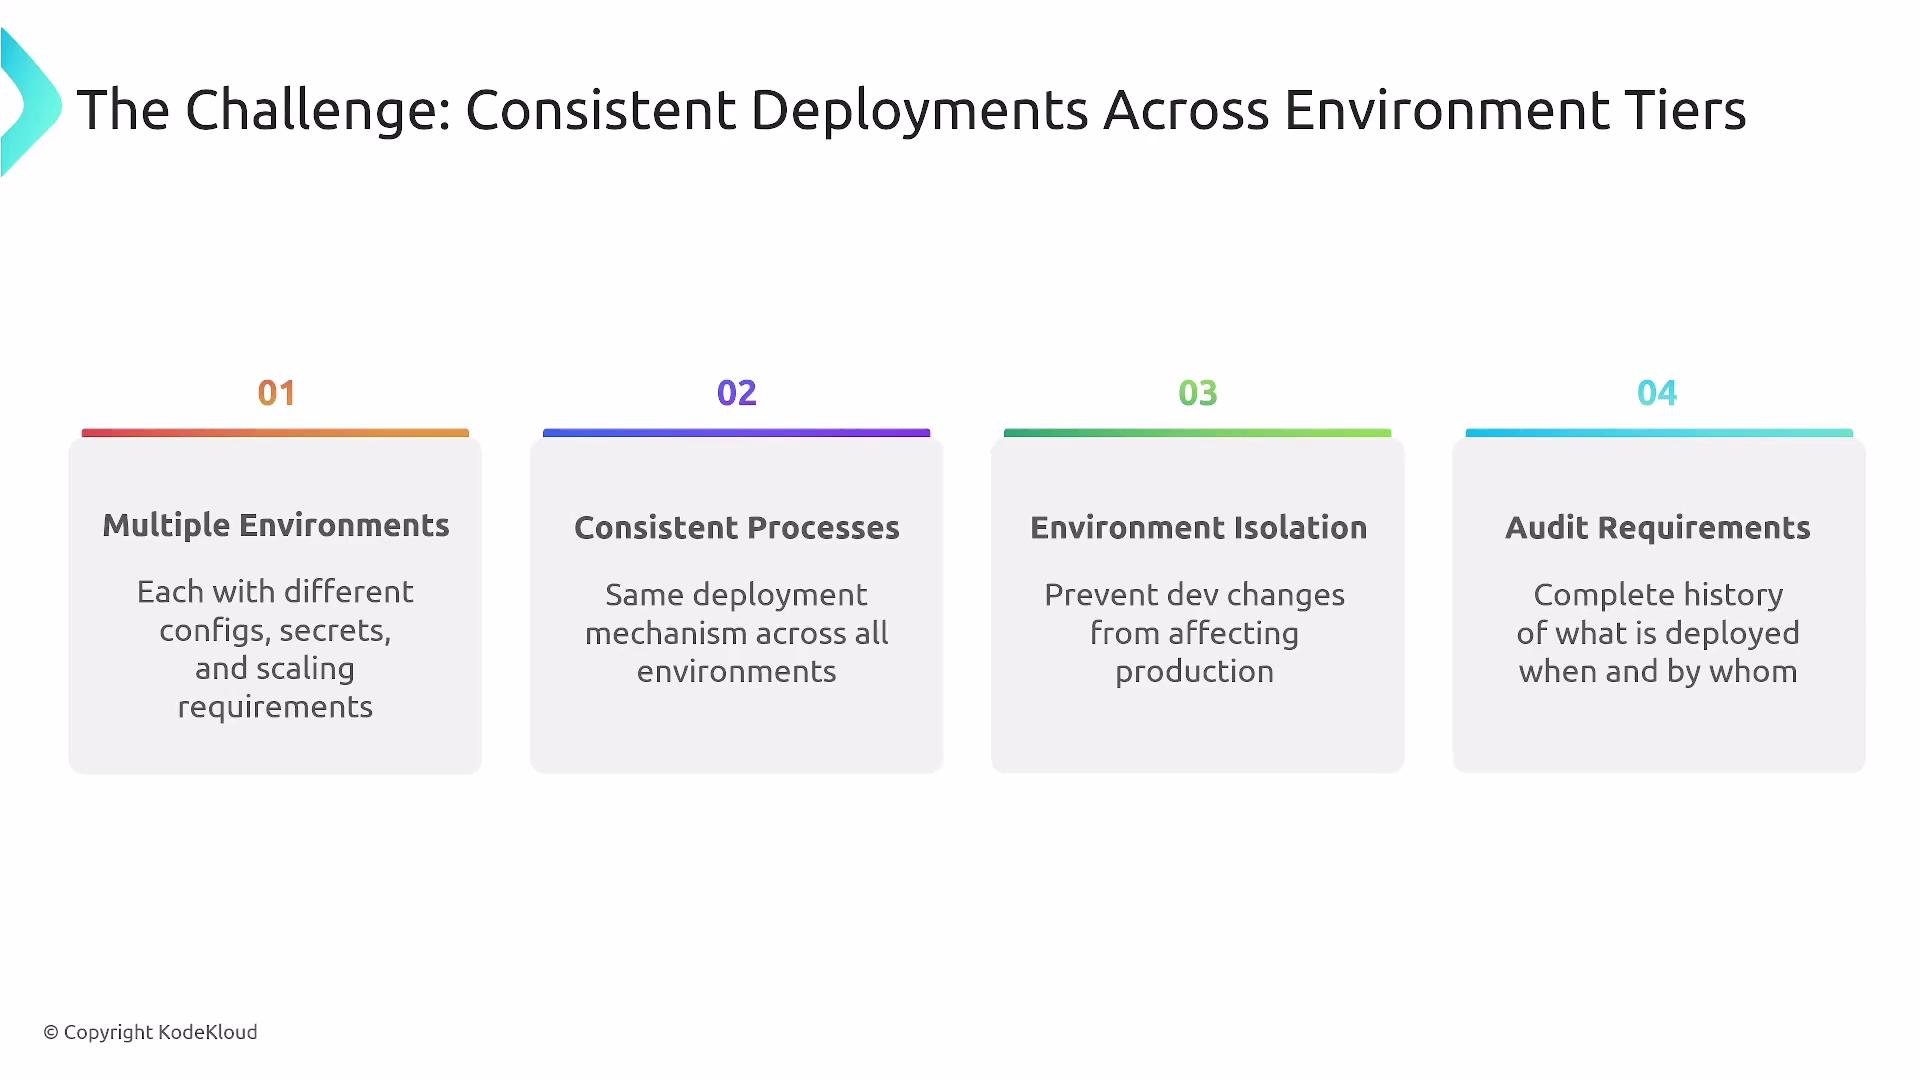
Welcome — in this lesson we explore GitOps for Application Environments: a core platform engineering concern focused on continuous promotion — promoting changes from development through testing and staging into production. The goal is to maintain consistency across multiple environments while preserving isolation, security boundaries, and full auditability.

One critical platform challenge is ensuring non-production environments are reliable and available; outages in development or staging directly slow delivery velocity.
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/consistent-deployments-environment-challenges.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=16c8613b94ece55441669e7be42aac90" alt="The image outlines challenges of ensuring consistent deployments across environment tiers, highlighting issues like multiple environments, consistent processes, environment isolation, and audit requirements." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/consistent-deployments-environment-challenges.jpg" />
</Frame>

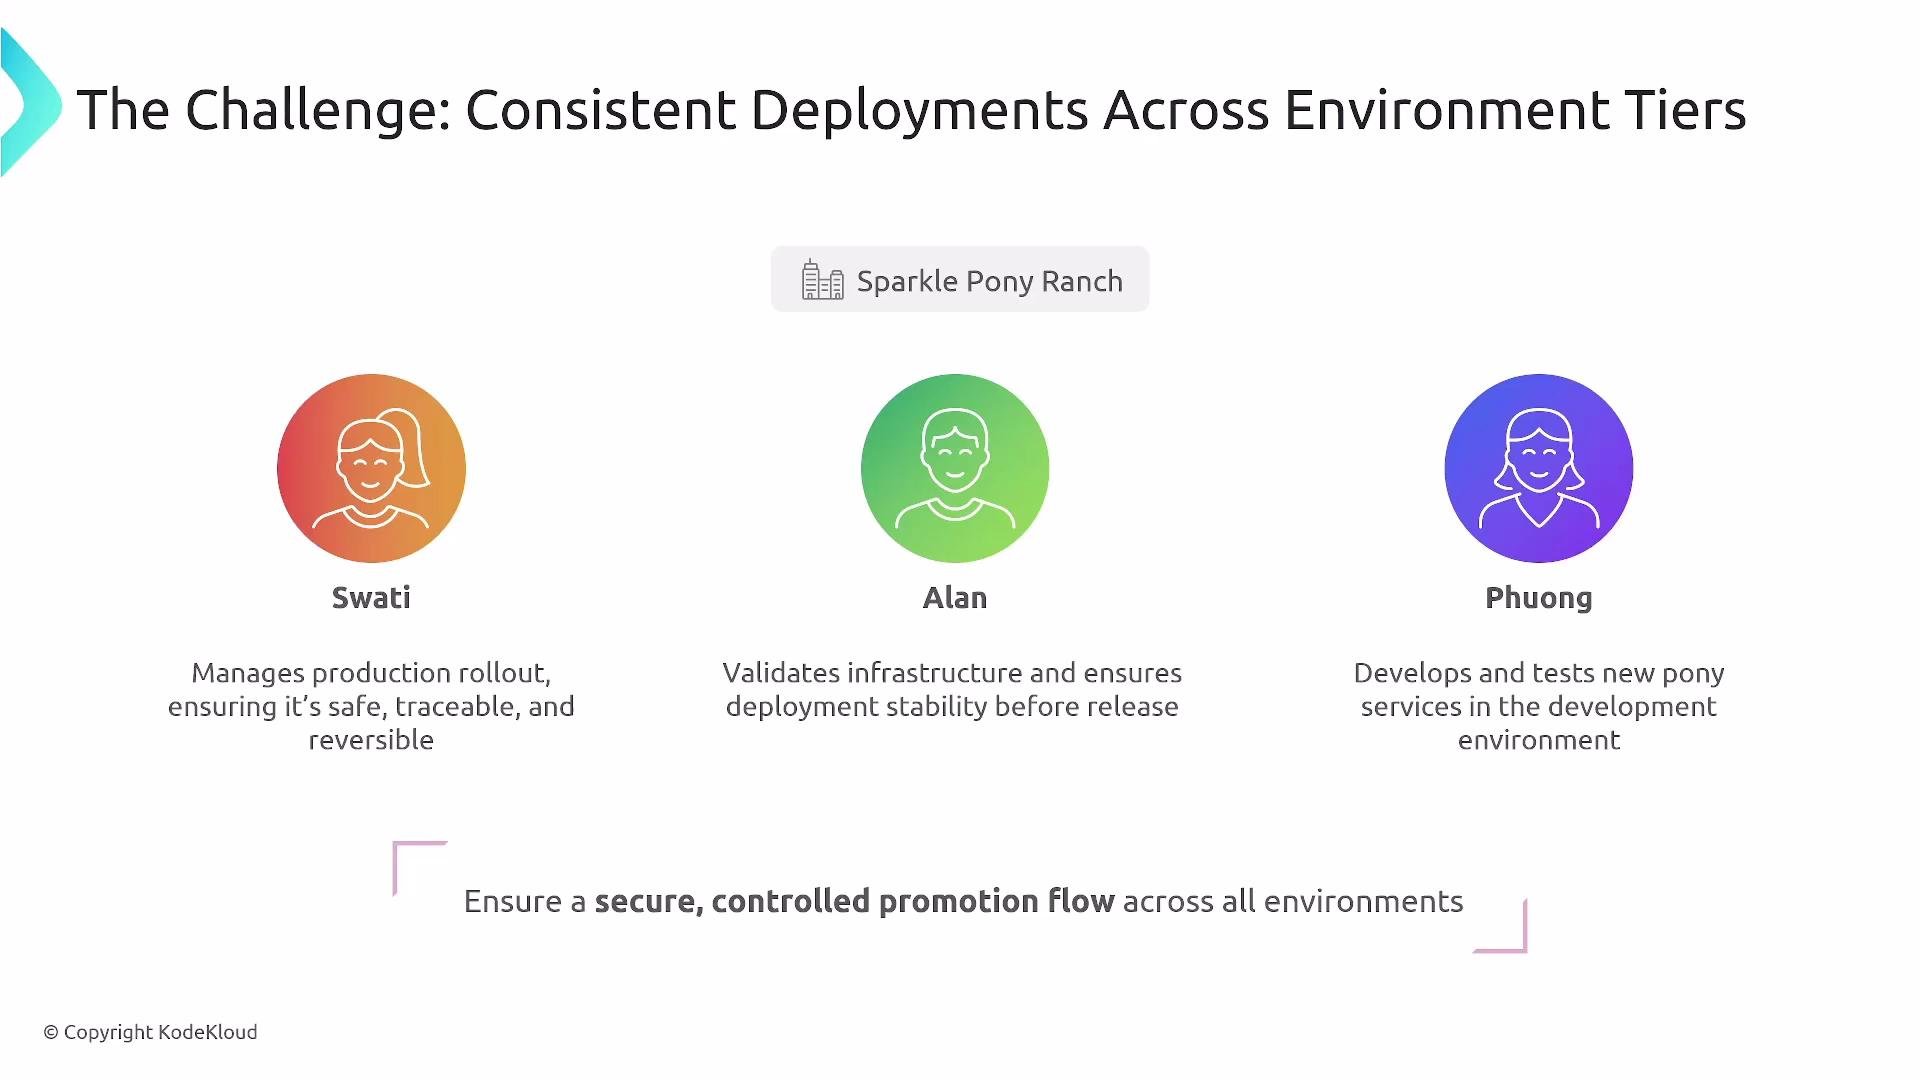
Throughout this lesson we use Sparkle Pony Ranch (SPR) as an example. SPR needs safe, traceable, and reversible promotion flows for pony services. Swati, Alan, and Phong (shown as Phuong in some diagrams) share responsibilities for development feedback, infrastructure validation, and application templates respectively.
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/roles-responsibilities-consistent-deployments.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=16561f5d5d7c3cc1daa61070edf77a35" alt="The image outlines roles and responsibilities for managing consistent deployments across environment tiers, featuring Swati, Alan, and Phuong, each with specific tasks related to production rollout, infrastructure validation, and development." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/roles-responsibilities-consistent-deployments.jpg" />
</Frame>

## Environment tiers and guardrails

A typical environment progression is:
development -> testing/QA -> staging -> production\
(variations often include UAT, performance, or specialized test environments).

As you progress toward production:

* Risk tolerance decreases.
* Controls, RBAC, and approval gates tighten.
* Observability and rollback mechanisms become stricter.

Design for:

* Consistent processes, tools, and deployment mechanisms across environments
* Environment isolation (clusters, namespaces, or access boundaries)
* Auditable promotion trails (commits, PRs, approvals)
* Logical production parity at scale (not necessarily identical capacity)

## Development: rapid feedback and quotas

GitOps supports short feedback loops and reproducible dev environments. Platform features commonly provided:

* One-click or repo-driven environment provisioning
* Resource quotas and guardrails to prevent noisy neighbors
* Feature flags to control runtime behavior

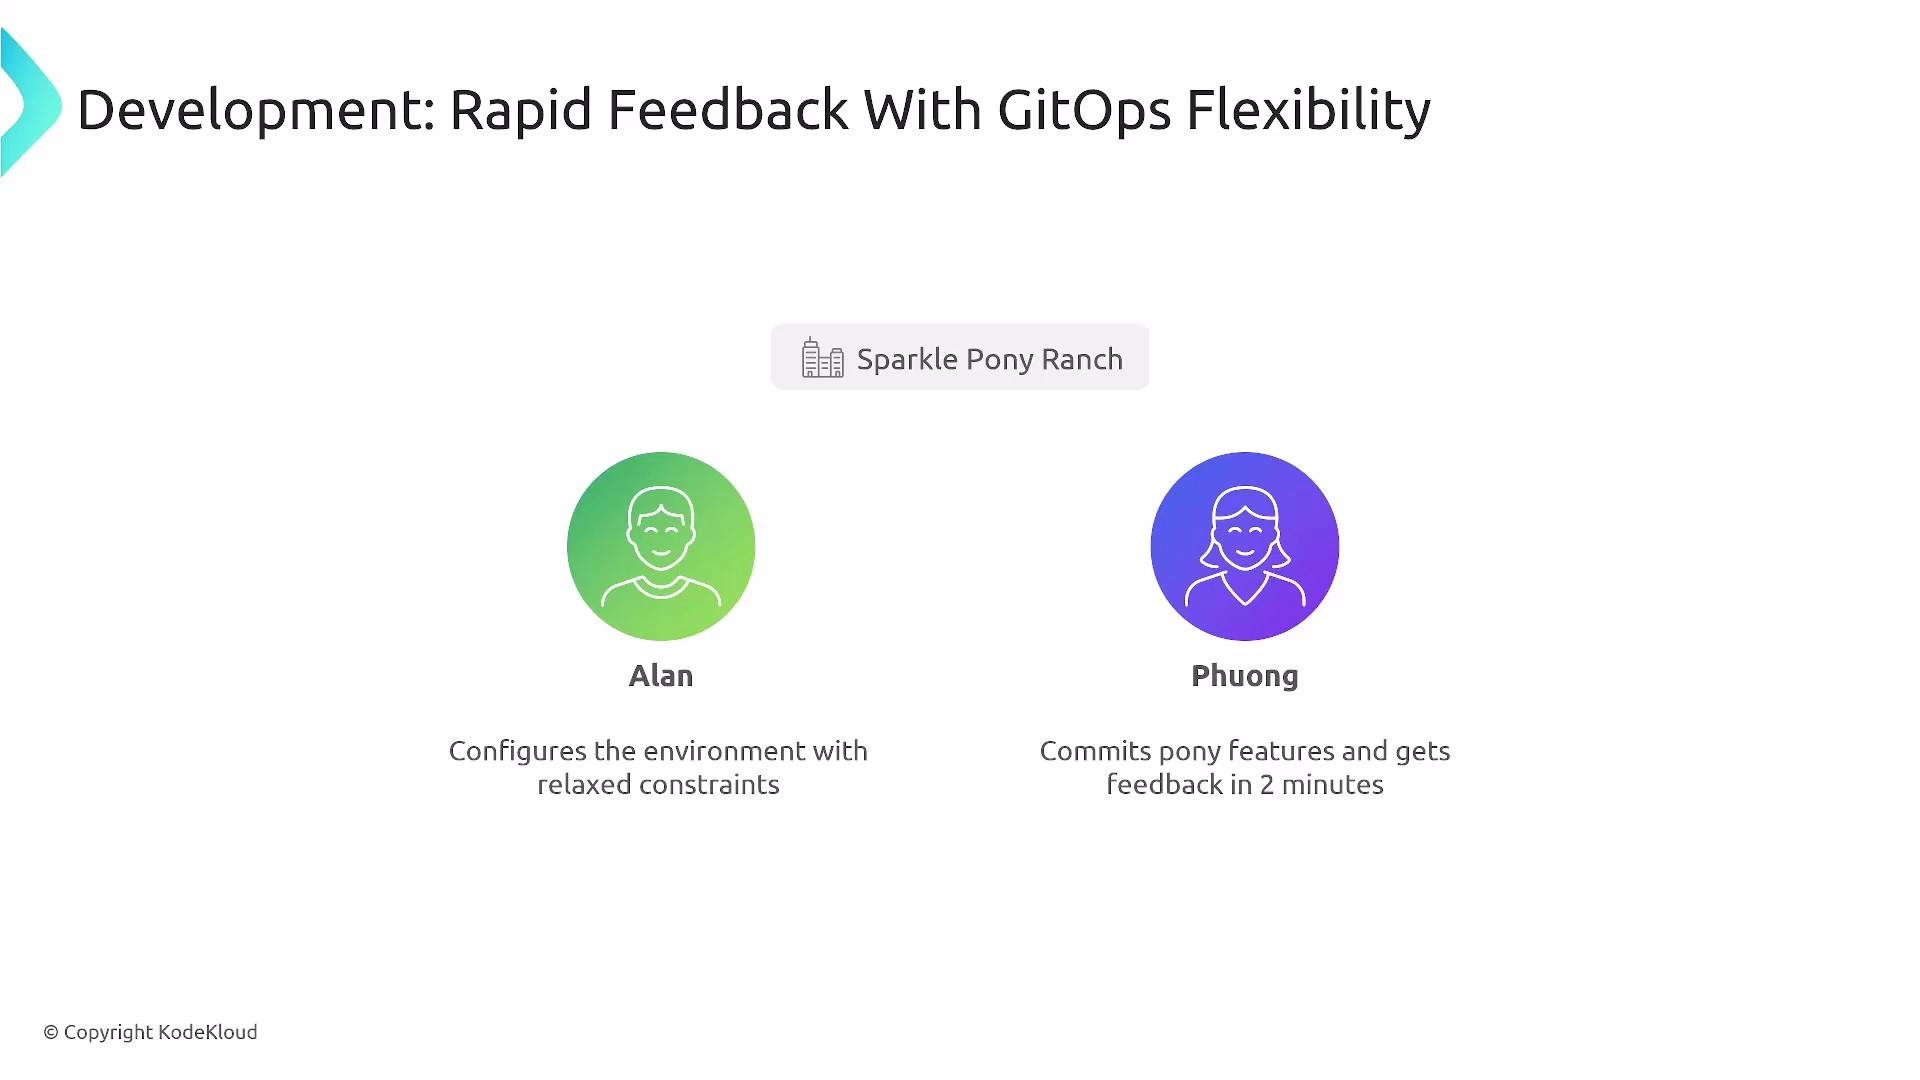
At SPR, Alan configures relaxed constraints in development so developers get two-minute feedback loops while platform policies enforce quotas.
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/development-rapid-feedback-gitops-slide.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=5006a5a64bc5980549a503465bc3ffce" alt="The image depicts a presentation slide titled &#x22;Development: Rapid Feedback With GitOps Flexibility&#x22; featuring two characters, Alan and Phuong, each with a brief description of their roles in the development process." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/development-rapid-feedback-gitops-slide.jpg" />
</Frame>

## Ephemeral environments

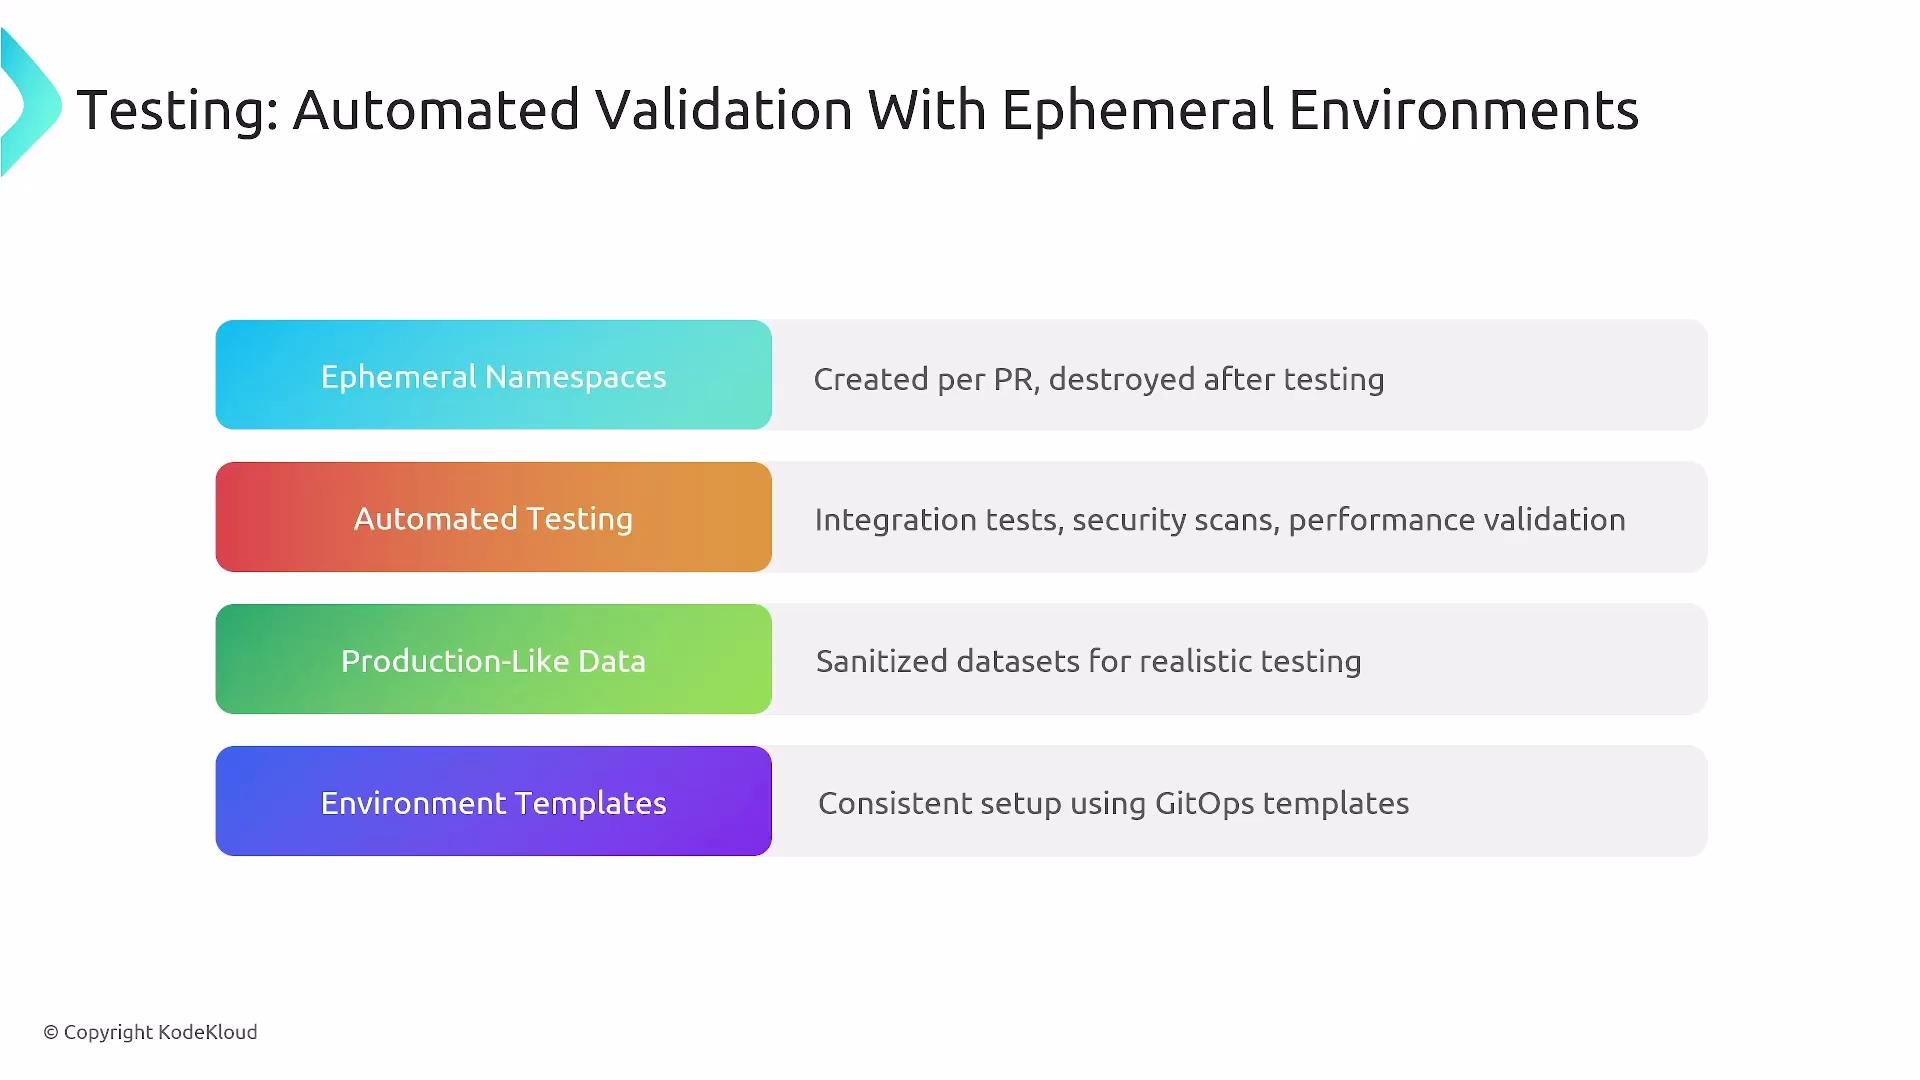
Ephemeral environments are short-lived, production-like environments created per PR, test run, or load test. They provide realistic integration testing, security scans, and exploratory validation on sanitized data.

Key capabilities:

* Templates for consistent ephemeral environment creation
* Automated provisioning and teardown
* Use of sanitized, production-like data for realistic validation
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/automated-validation-ephemeral-environments-diagram.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=edece8290b701d0b940f7cb1d2449fe0" alt="The image outlines components of automated validation with ephemeral environments, including ephemeral namespaces, automated testing, production-like data, and environment templates." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/automated-validation-ephemeral-environments-diagram.jpg" />
</Frame>

Example: an Argo CD Application that maps a PR branch (targetRevision) to an ephemeral namespace. When PR-123 is opened, the platform creates `testing-pr-123`, deploys the PR branch there, runs tests and scans, and then tears it down automatically.

```yaml theme={null}
# Example: PR-based environment creation (Argo CD Application)
apiVersion: argoproj.io/v1alpha1
kind: Application
metadata:
  name: pony-spawner-pr-123
  namespace: argocd
spec:
  source:
    repoURL: https://github.com/spr/gitops-config
    path: environments/testing
    targetRevision: pr-123
  destination:
    server: https://kubernetes.default.svc
    namespace: testing-pr-123
```

Lifecycle automation for ephemeral environments is a high-value platform capability that reduces manual toil and improves confidence.

## Staging: final validation

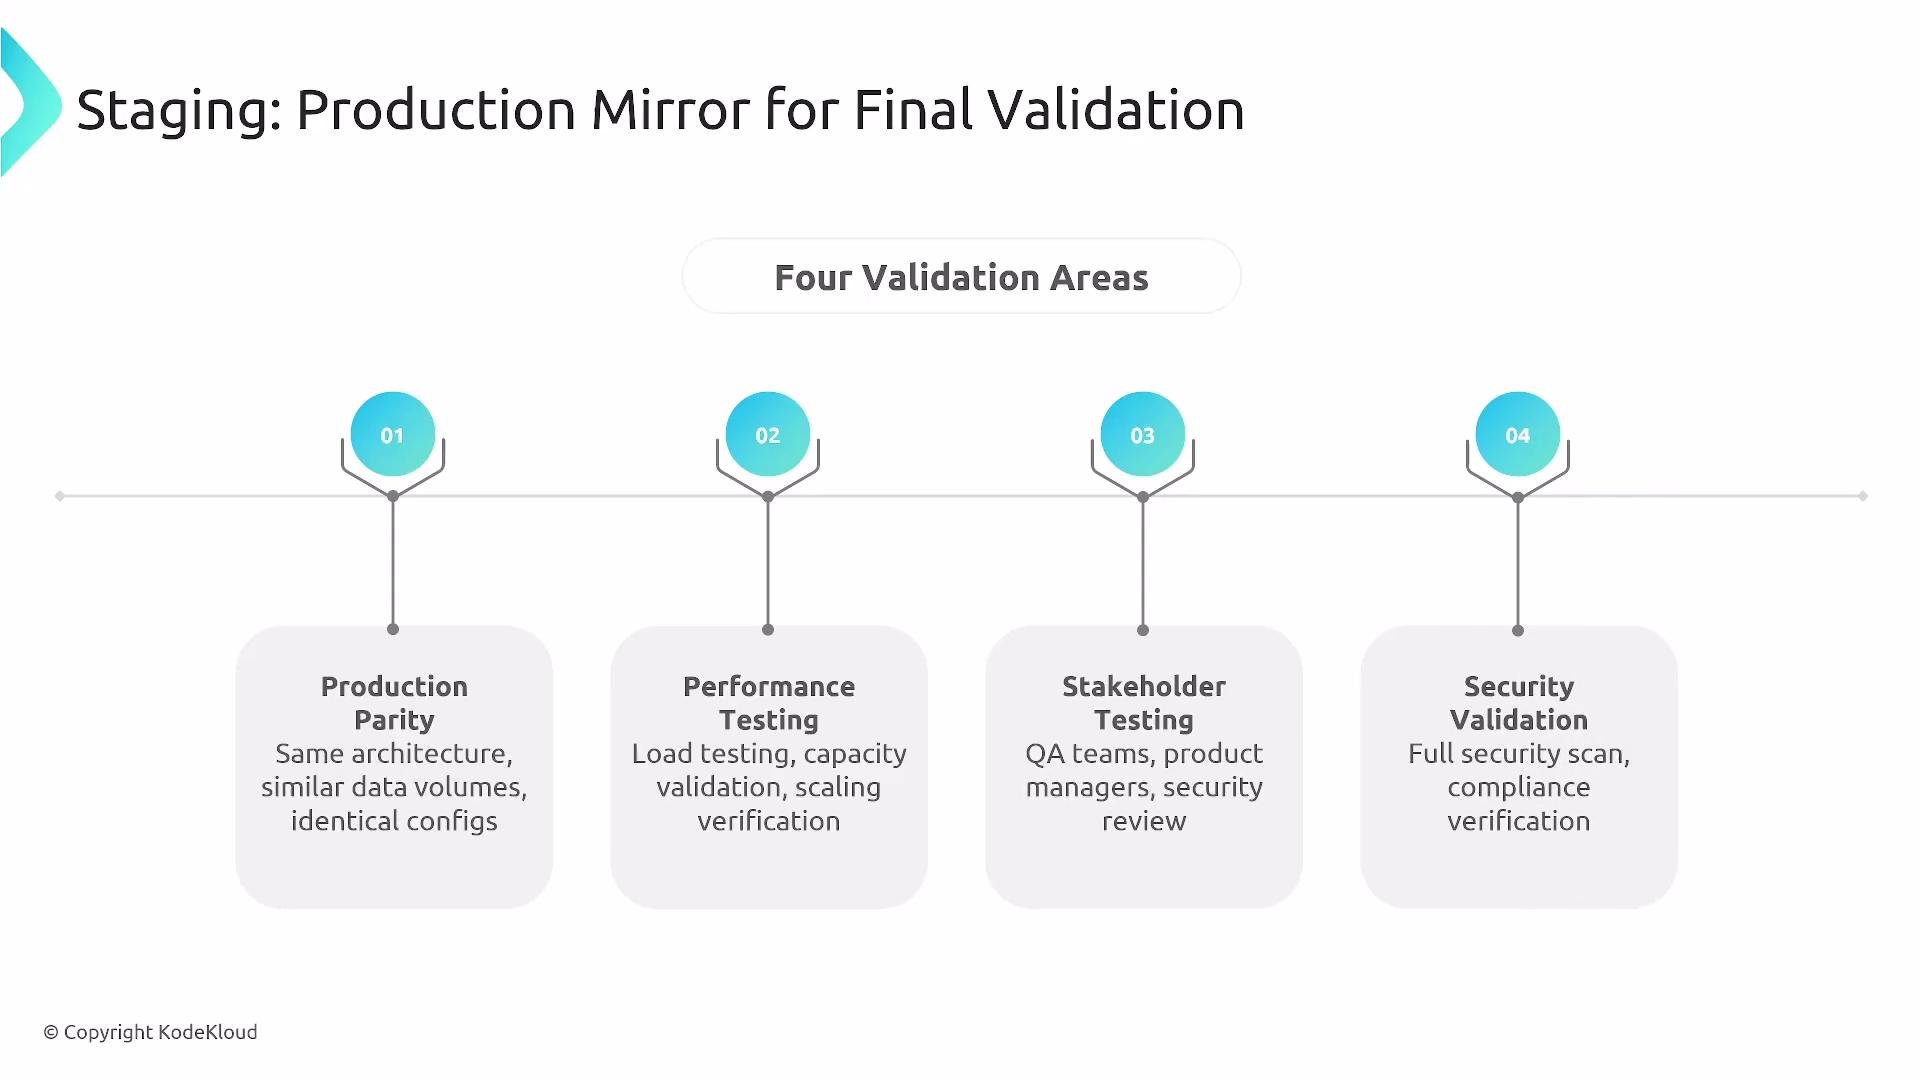
Staging is the final validation gate before production. It typically mirrors production in architecture and configuration (logically or geographically) to allow performance testing, UAT, and security validation.

Design considerations:

* Production parity: What must match production vs. what can be smaller?
* Performance testing: How to extrapolate load/capacity differences?
* Stakeholder testing: Will UAT stakeholders access staging?
* Security validation: Run full policy scans and security tests here
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/validation-areas-final-staging-diagram.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=6b67b6af270feaa40f87626395b329e1" alt="The image is a diagram depicting four validation areas for final staging: Production Parity, Performance Testing, Stakeholder Testing, and Security Validation. Each area focuses on different aspects such as architecture, load testing, QA involvement, and security scans." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/validation-areas-final-staging-diagram.jpg" />
</Frame>

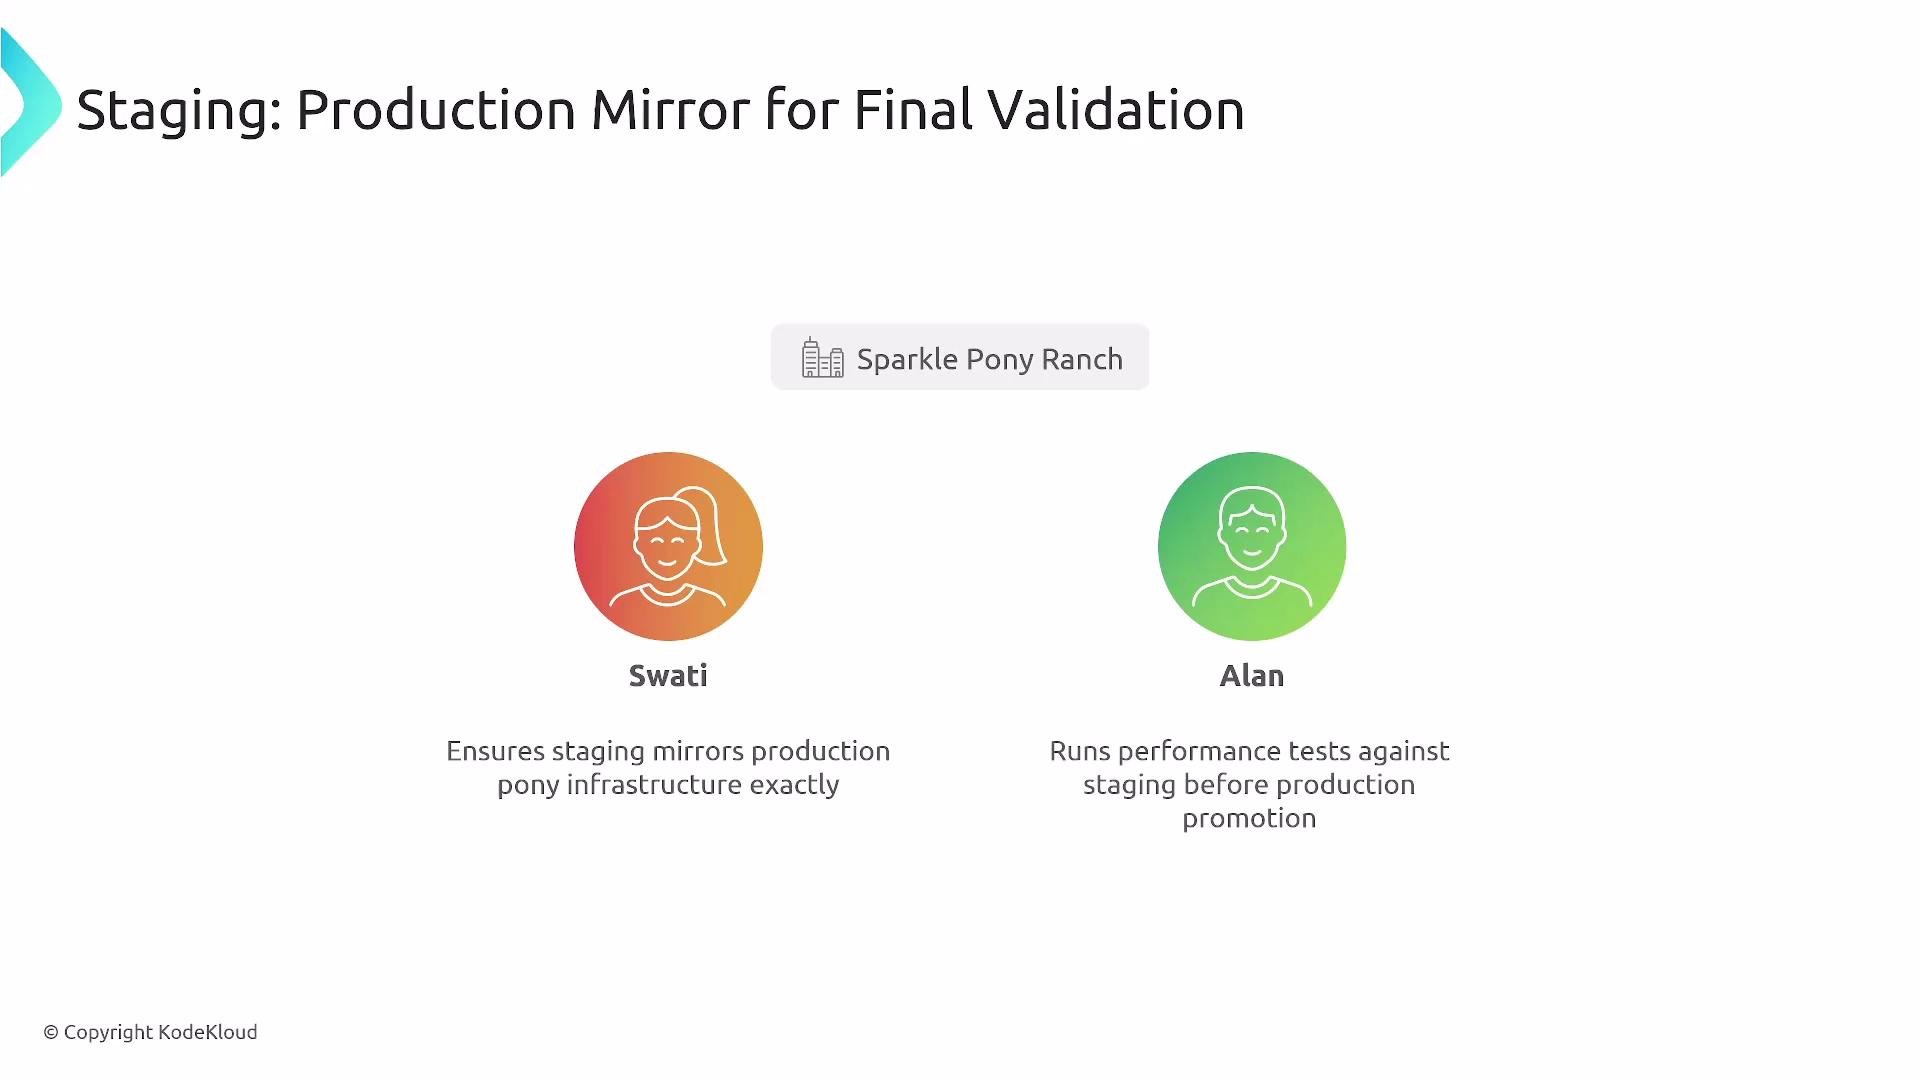
At SPR, Swati ensures staging mirrors production; Alan runs performance and security tests prior to promotion.
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/staging-process-validation-sparkle-pony.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=f10152701ed4c79e6bb3d154e3e76f89" alt="The image is a diagram illustrating a staging process for final validation with two people, Swati and Alan, responsible for ensuring infrastructure mirroring and running performance tests, under the &#x22;Sparkle Pony Ranch&#x22; label." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/staging-process-validation-sparkle-pony.jpg" />
</Frame>

Because staging can be costly, teams often spin up on-demand staging for heavy tests and tear it down when finished.

## Production: restricted, observable, resilient

Production requirements:

* Strict least-privilege access and restricted interactive access
* Approval gates where needed and automated monitored rollouts
* High availability and disaster recovery strategies (multi-AZ/region)
* Comprehensive observability (logs, metrics, traces) and runbooks
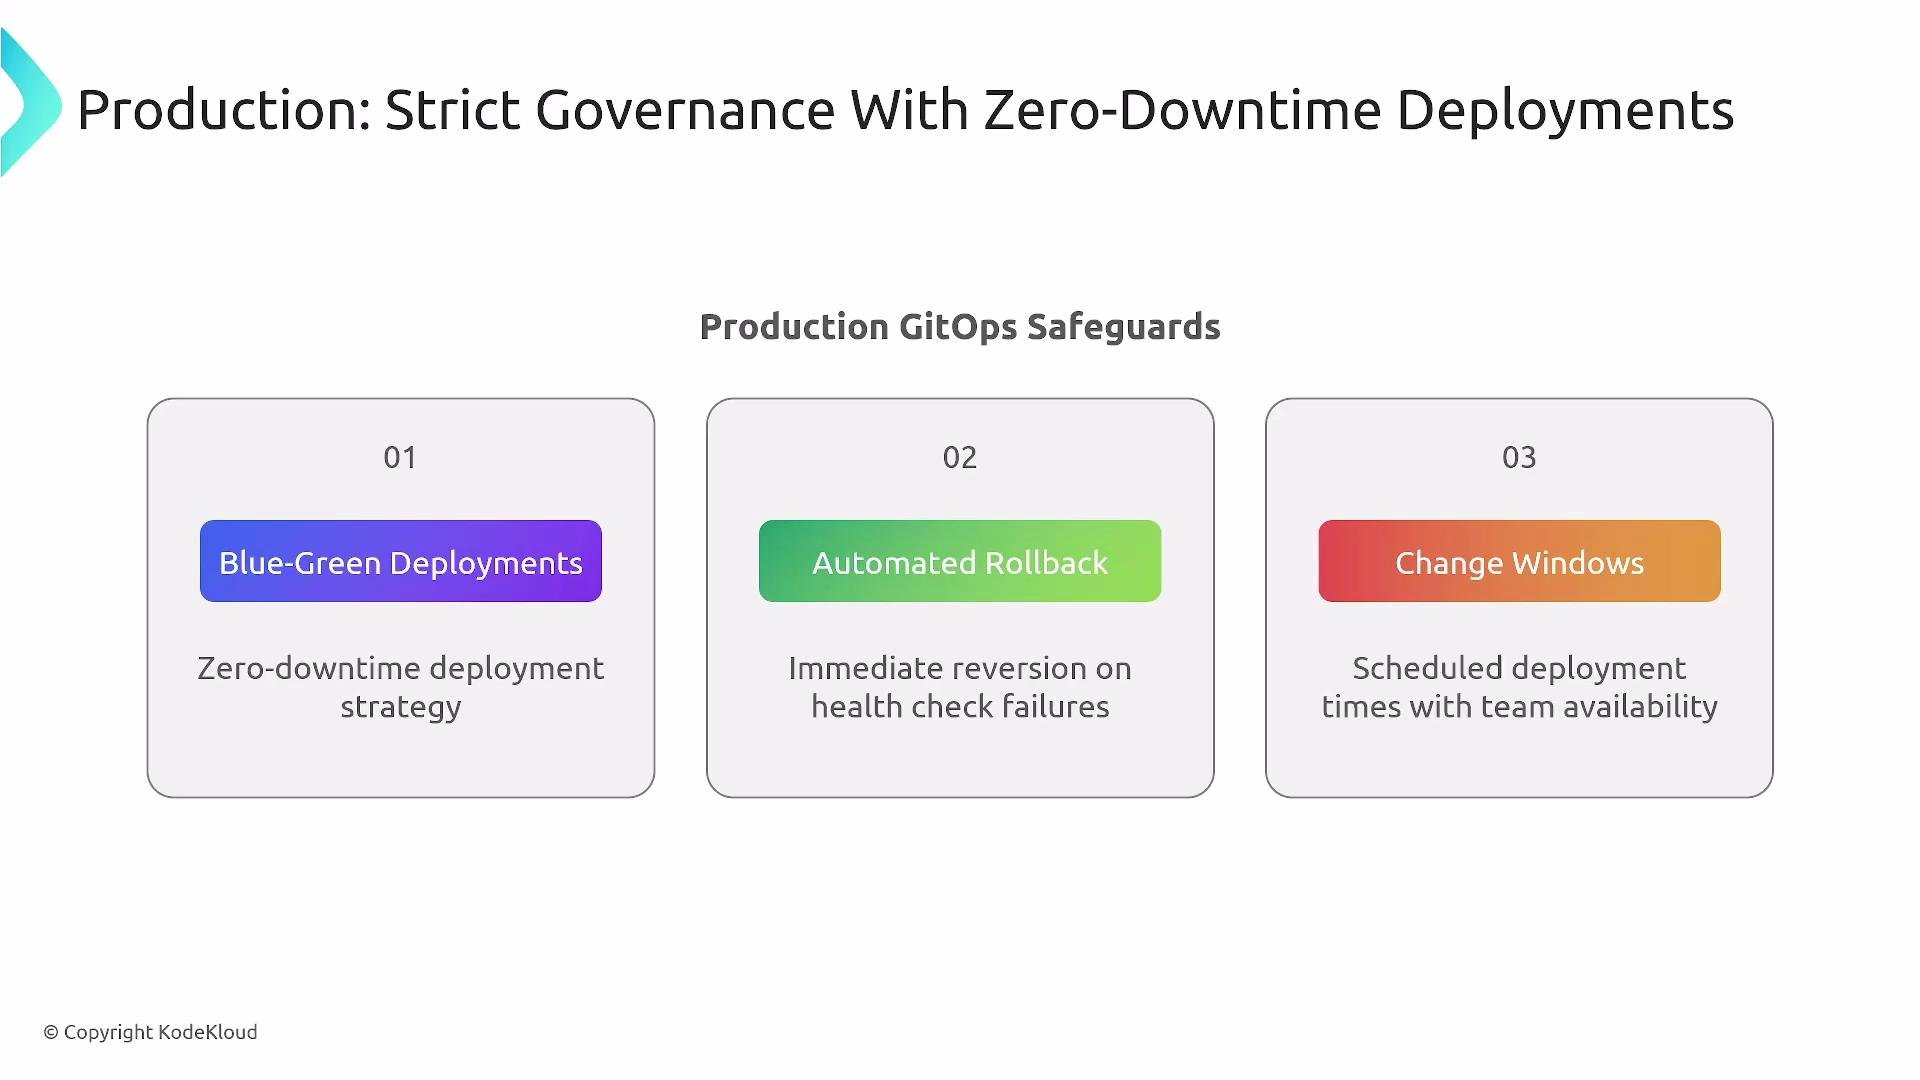
* Automated rollback strategies (blue-green, canary with automated rollback)
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-safeguards-zero-downtime-deployments.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=3e088fc7a4ac591f567ec405dd0f817b" alt="The image outlines production GitOps safeguards for zero-downtime deployments, including blue-green deployments, automated rollback, and change windows." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-safeguards-zero-downtime-deployments.jpg" />
</Frame>

Automated promotion is ideal for speed and consistency, but manual gates remain critical for highly sensitive or poorly tested deployments.

## Repository patterns and scaling

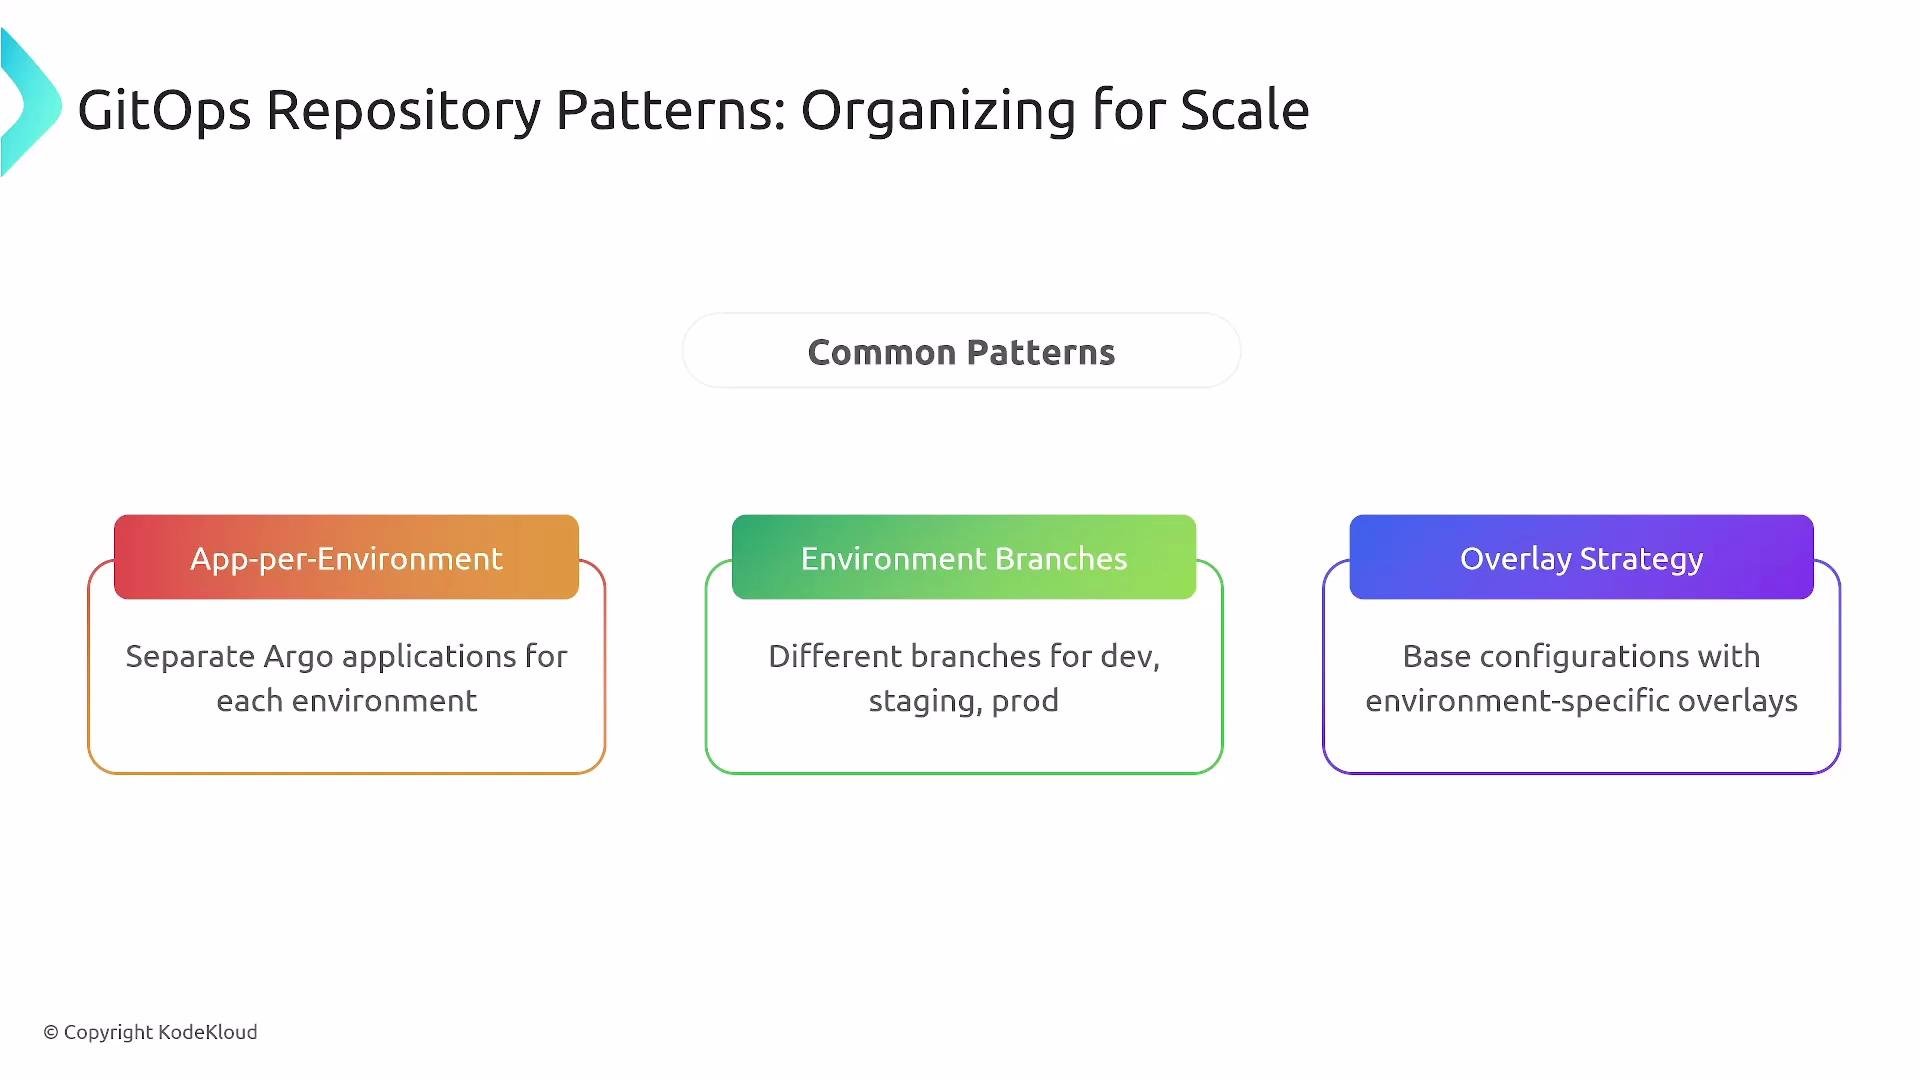
Common GitOps repository patterns:

* App-per-environment (each app has environment-specific manifests)
* Environment branches (branch-per-environment)
* Overlay strategy (Kustomize-style overlays that patch a common base)

Two dominant repository strategies and trade-offs:

| Strategy | Benefits | Trade-offs / Challenges |
| - | - | - |
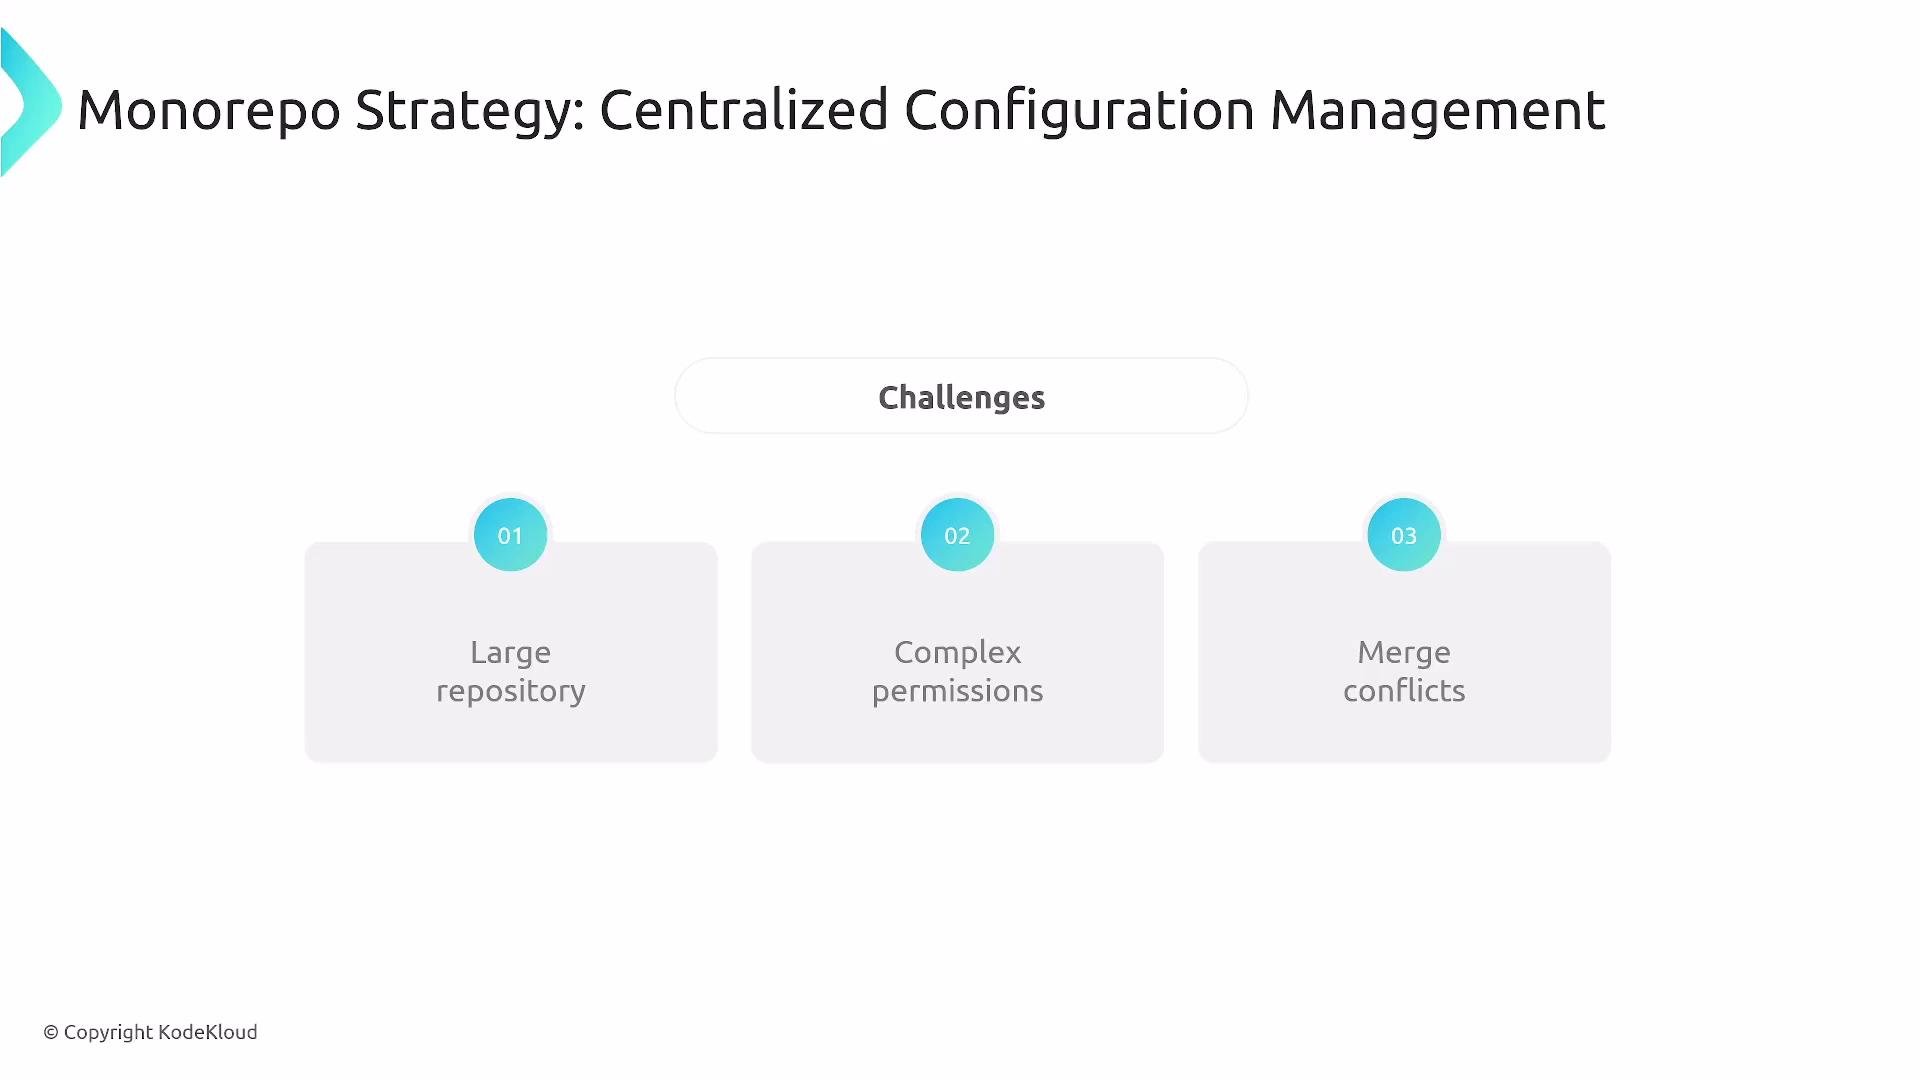
| Monorepo | Centralized change tracking, single pipeline for multiple envs | Large repo size, complex permissions, increased merge conflicts |
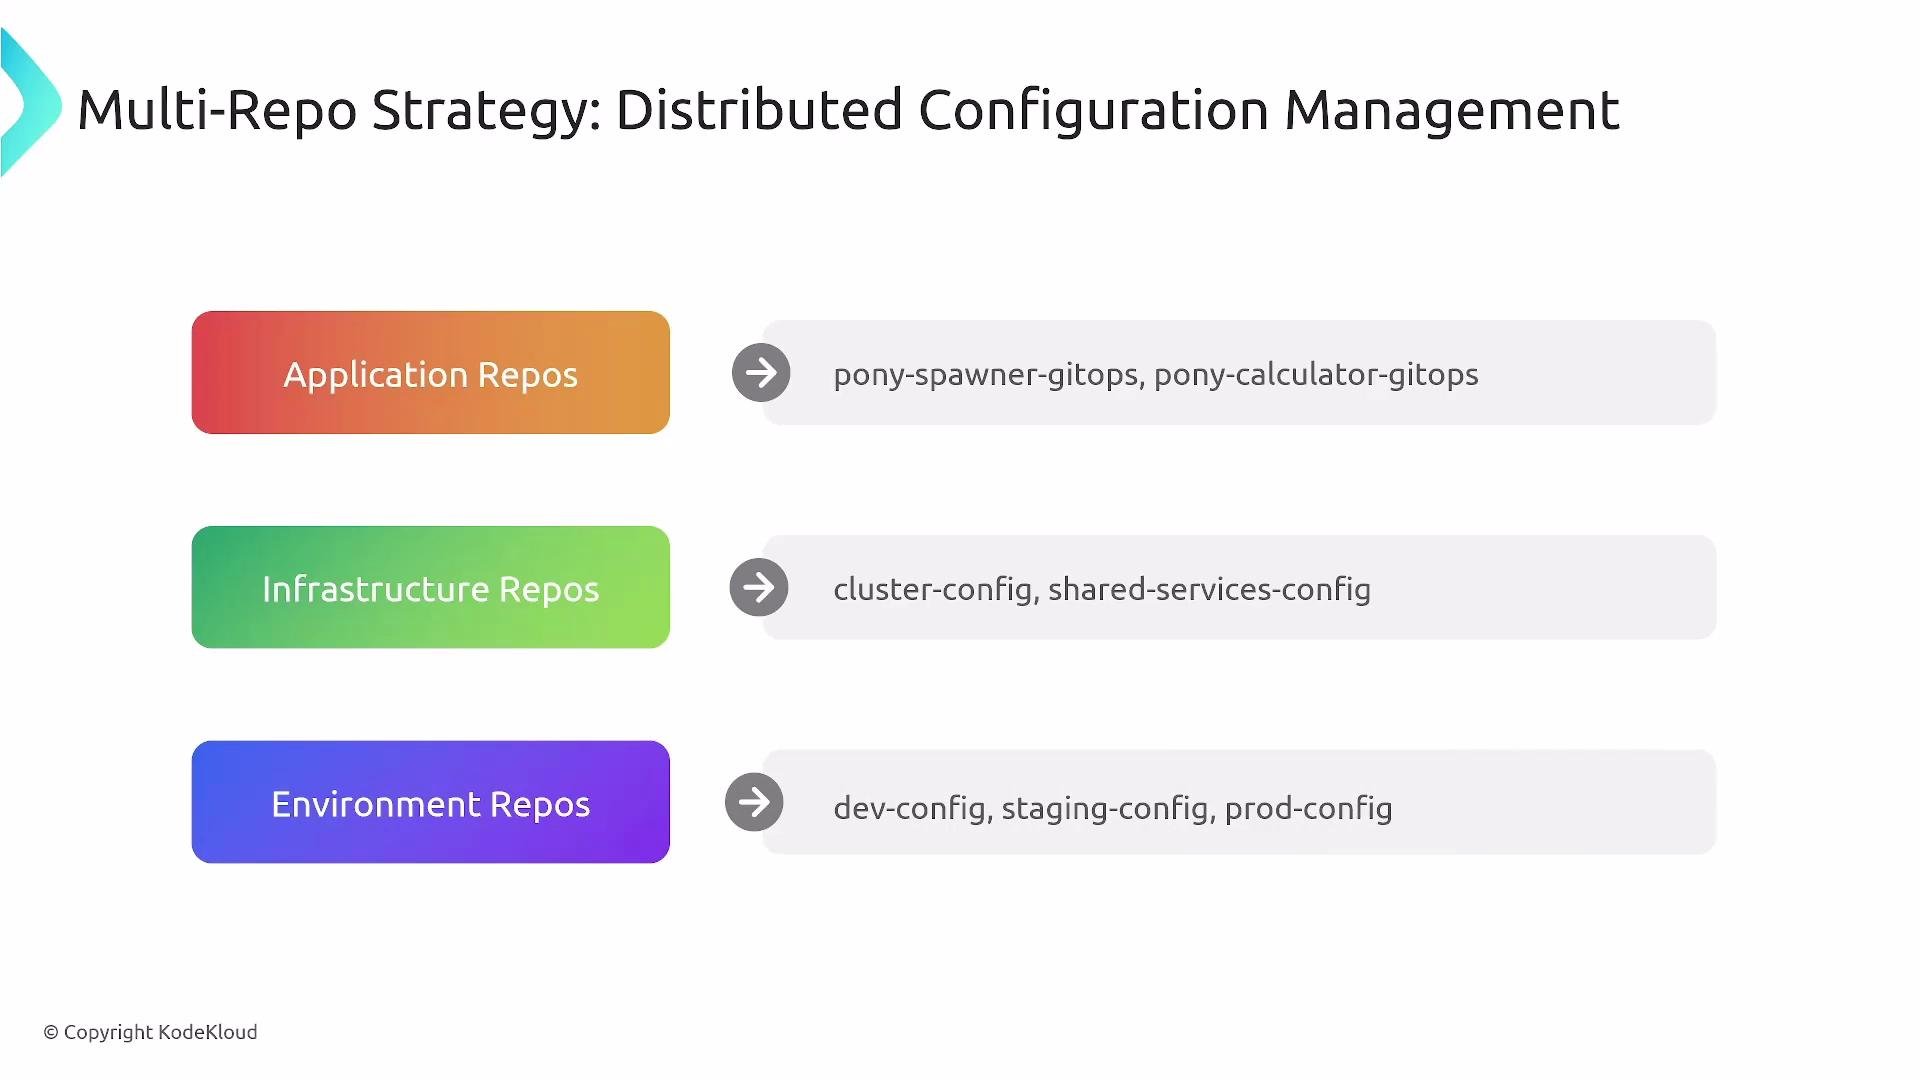
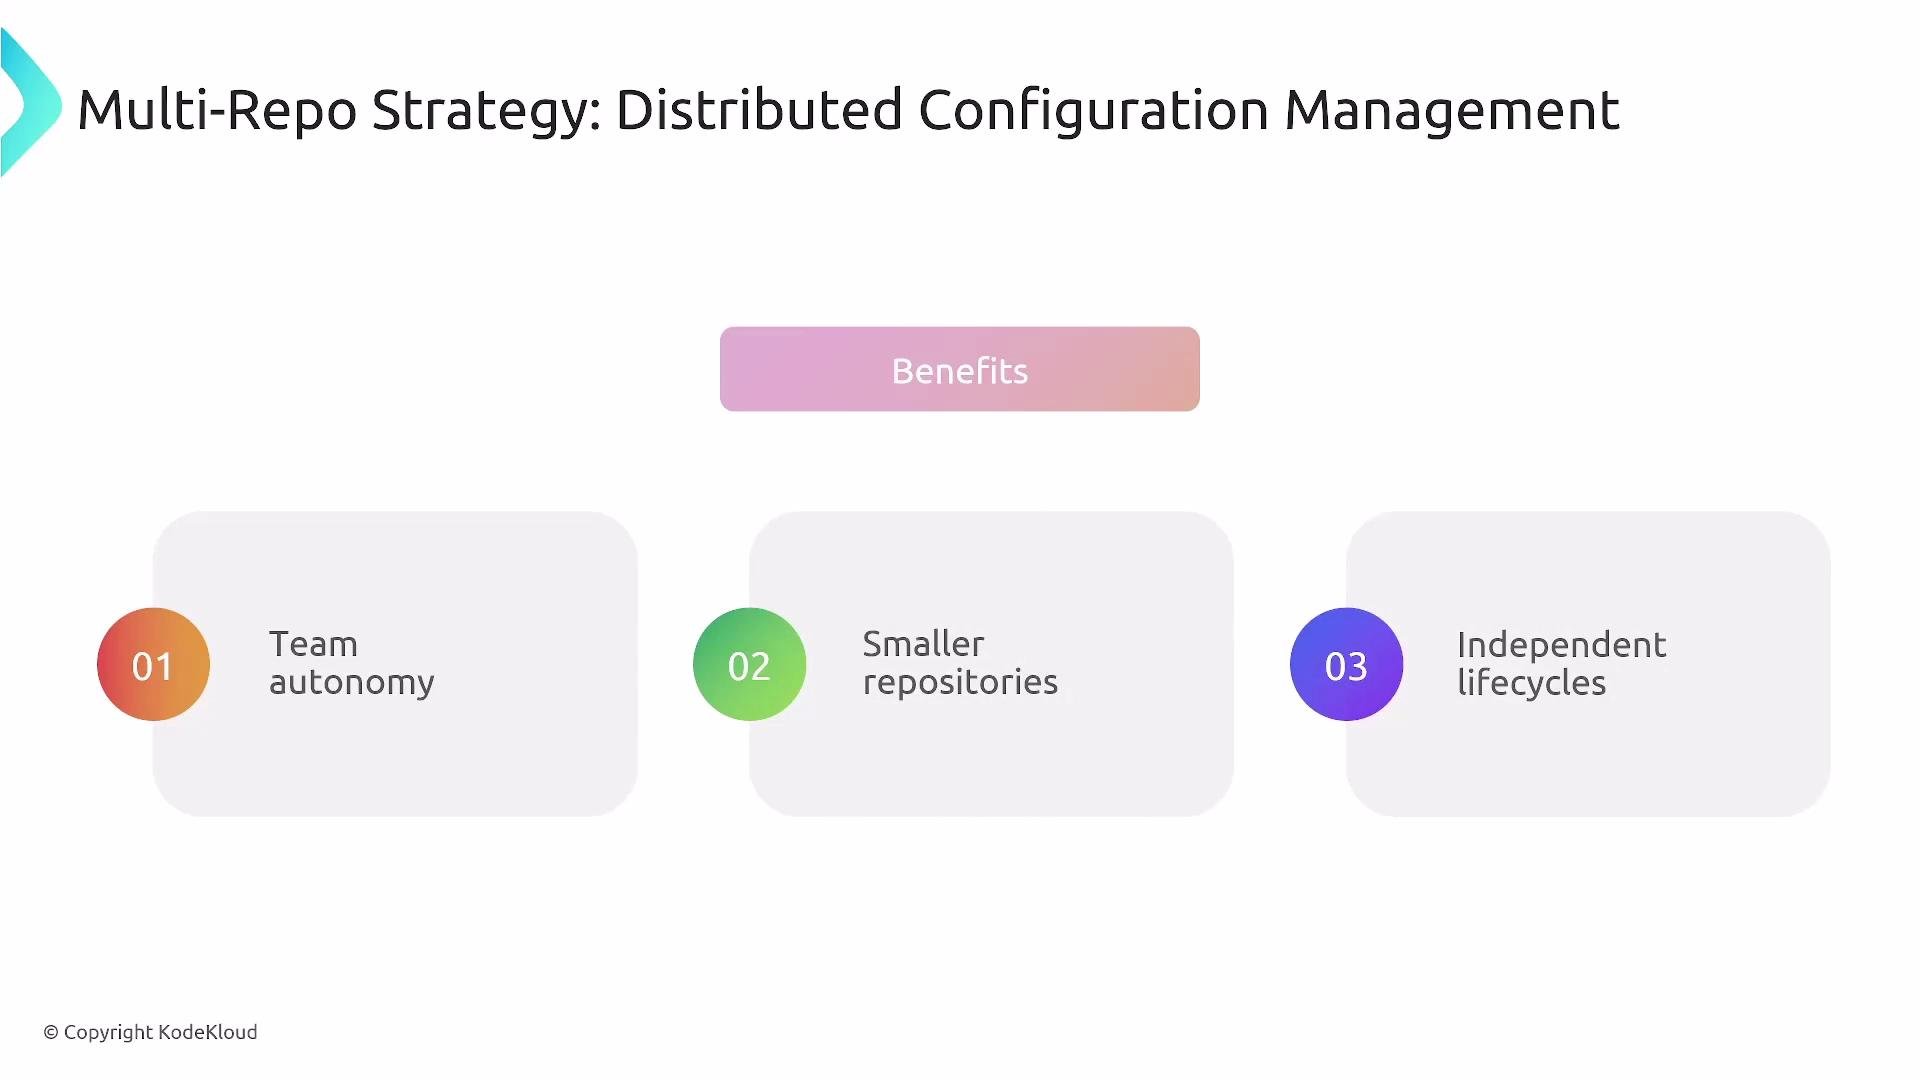
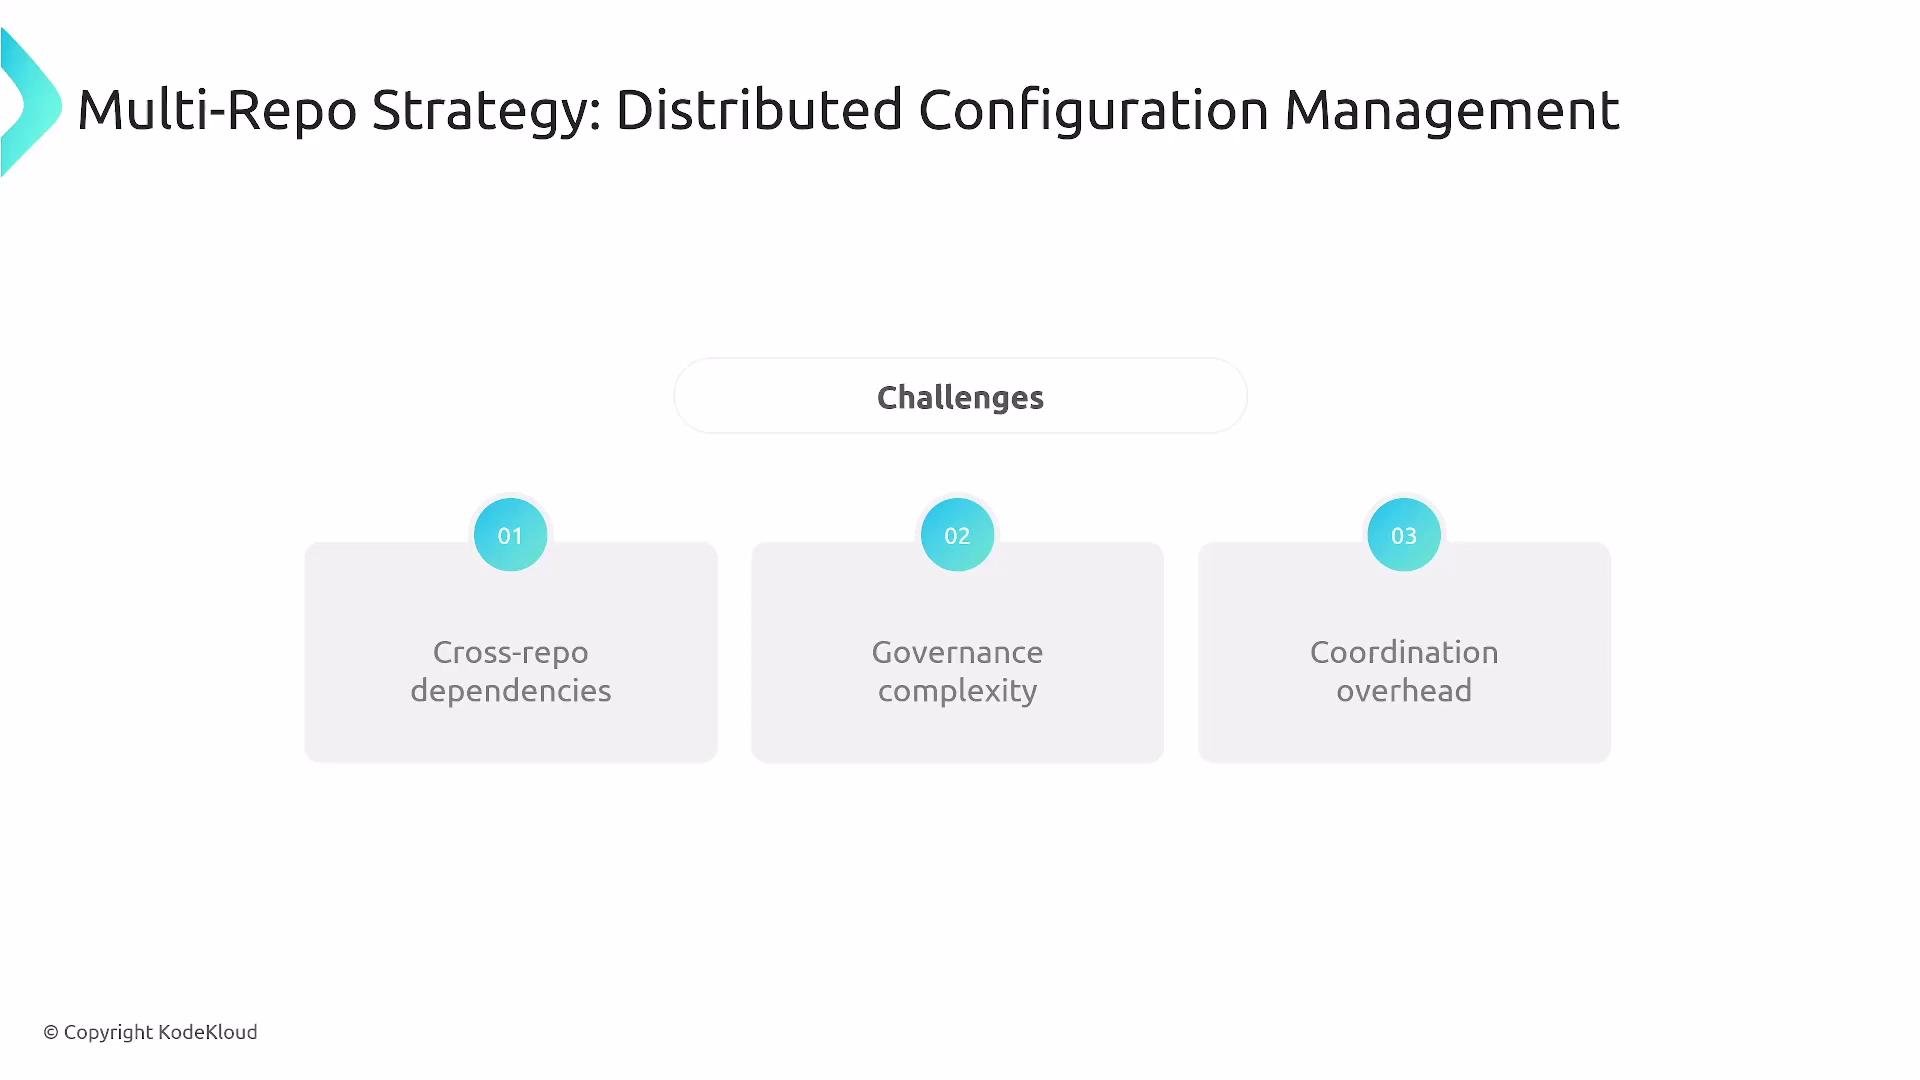
| Multi-repo | Team autonomy, smaller repos, independent lifecycles | Cross-repo dependencies, governance and coordination overhead |
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-repository-patterns-scaling.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=8a092484e7b00a4de43a0ff71a2b1cd9" alt="The image outlines three GitOps repository patterns for scaling: &#x22;App-per-Environment,&#x22; &#x22;Environment Branches,&#x22; and &#x22;Overlay Strategy,&#x22; each describing a different approach to managing environments." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-repository-patterns-scaling.jpg" />
</Frame>

Monorepo characteristics:

<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/monorepo-strategy-issues-overview.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=53382a21f63bebb30a45a48038470067" alt="The image outlines challenges in a &#x22;Monorepo Strategy: Centralized Configuration Management,&#x22; highlighting three issues: large repositories, complex permissions, and merge conflicts." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/monorepo-strategy-issues-overview.jpg" />
</Frame>

Multi-repo characteristics:

<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/multi-repo-strategy-distributed-configuration.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=6b9e67a4198e1ce1c4f63ef61bea0952" alt="The image outlines a multi-repo strategy for distributed configuration management, categorizing repositories into application, infrastructure, and environment types. Each category lists specific repos for managing different aspects of configurations." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/multi-repo-strategy-distributed-configuration.jpg" />
</Frame>

<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/multi-repo-strategy-benefits-diagram.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=44b9972d56f87f1e3431f5718634c70b" alt="The image outlines the benefits of a multi-repo strategy for distributed configuration management, highlighting team autonomy, smaller repositories, and independent lifecycles." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/multi-repo-strategy-benefits-diagram.jpg" />
</Frame>

<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/multi-repo-strategy-challenges-overview.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=656137974bd28469ad578bfaf6b2fa6d" alt="The image outlines challenges in a &#x22;Multi-Repo Strategy: Distributed Configuration Management,&#x22; highlighting cross-repo dependencies, governance complexity, and coordination overhead." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/multi-repo-strategy-challenges-overview.jpg" />
</Frame>

Choose the strategy that matches team size, autonomy needs, and governance capabilities.

## Logical parity vs. scale differences

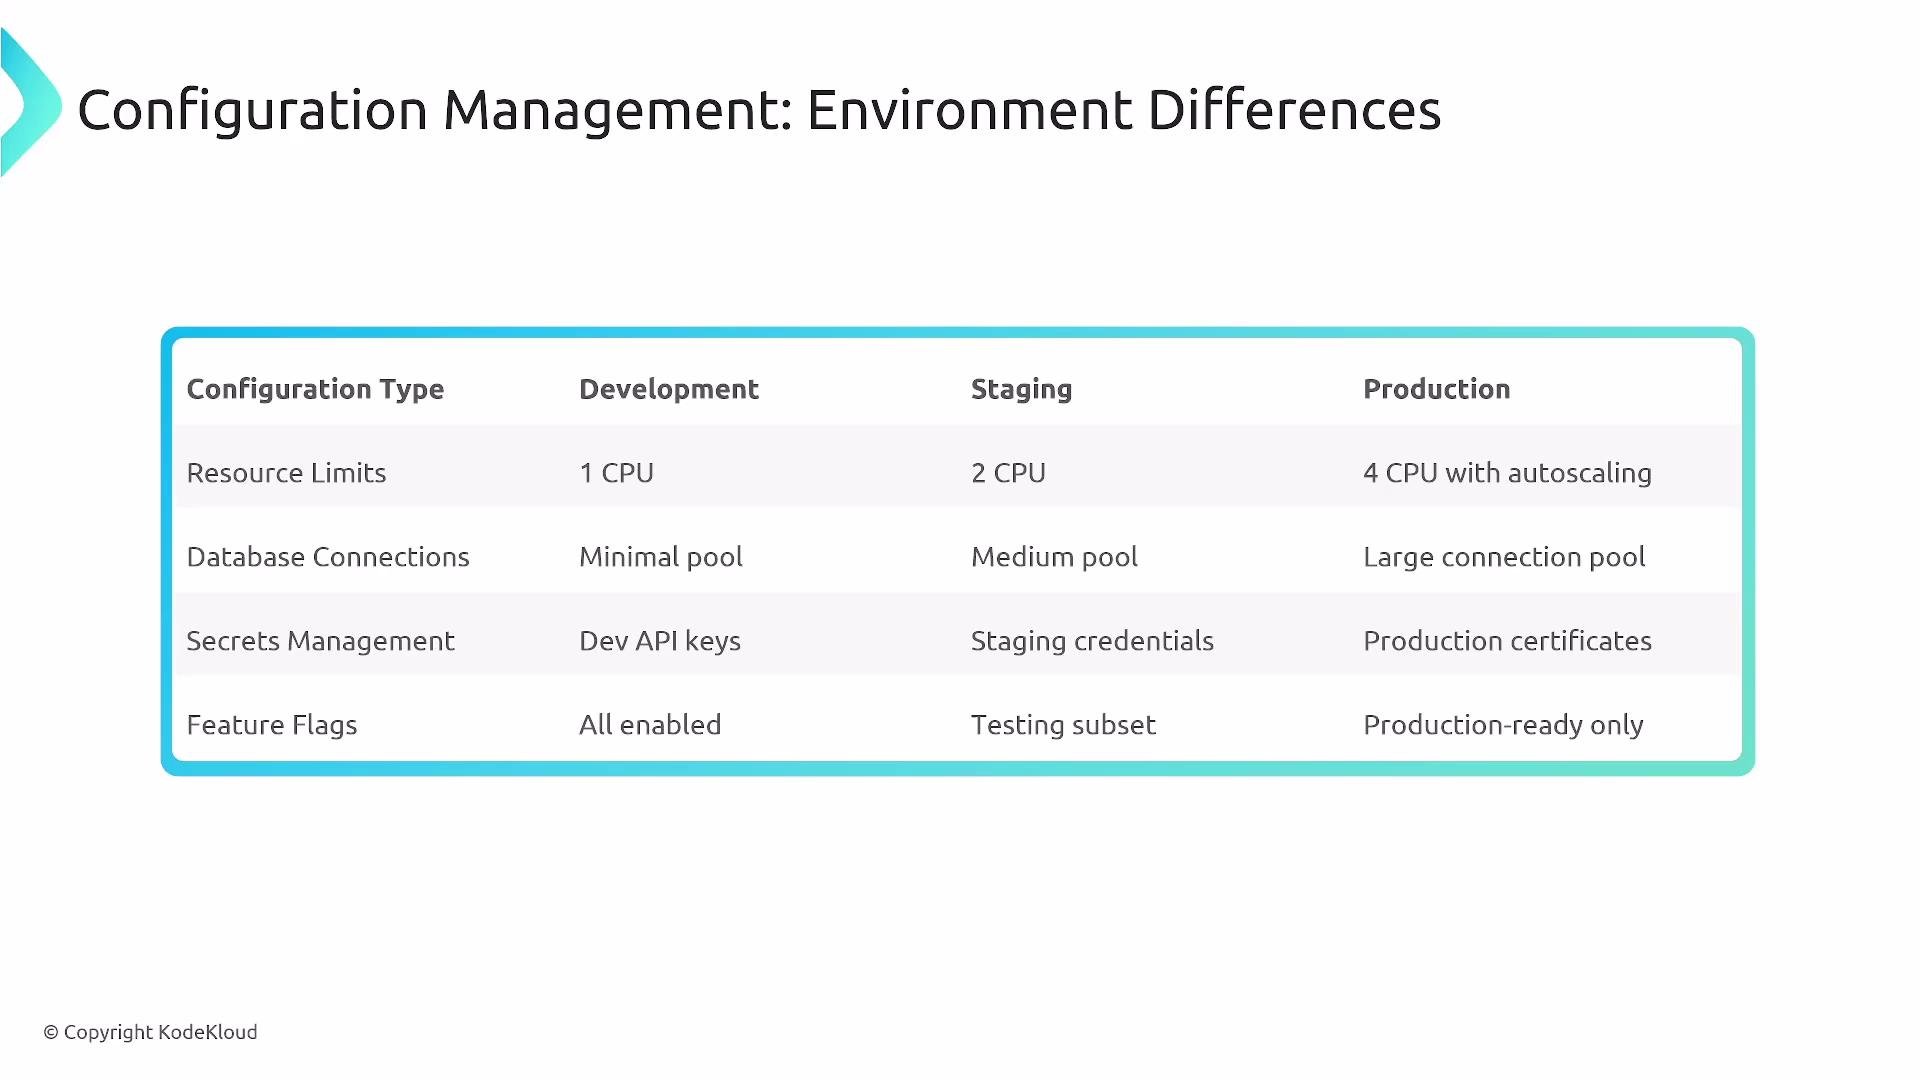
Maintain logical equivalence across environments even if scale differs (replicas, quotas, separate DB hosts). Ensure:

* Secrets and sensitive configuration are environment-specific and auditable
* Feature flags are scoped per environment
* Scaling differences are documented and reflected in test interpretation
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/config-management-comparison-table.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=1d92176bcd864b8c528a2cb17c17f75c" alt="The image is a table comparing configuration management differences across development, staging, and production environments, highlighting variations in resource limits, database connections, secrets management, and feature flags." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/config-management-comparison-table.jpg" />
</Frame>

## Kustomize and Helm: environment-specific configuration

Kustomize follows a base + overlays model. Helm uses templates with values files. Both are valid ways to generate environment-specific manifests.

Example environment differences (illustrative values):

```yaml theme={null}
# environment values example (illustrative)
# dev environment
replicas: 1
resources:
  requests:
    cpu: "100m"
    memory: "128Mi"
database:
  host: "dev-postgres.cluster.local"

# production environment
replicas: 5
resources:
  requests:
    cpu: "500m"
    memory: "512Mi"
database:
  host: "prod-postgres.cluster.local"
```

Kustomize production overlay example:

```yaml theme={null}
# kustomization.yaml for production
apiVersion: kustomize.config.k8s.io/v1beta1
kind: Kustomization

resources:
  - ../../base

patchesStrategicMerge:
  - replica-count.yaml
  - resource-limits.yaml
  - secrets.yaml
```

Helm values example for production:

```yaml theme={null}
# values-prod.yaml
replicaCount: 5
image:
  tag: "v2.1.0"
ingress:
  enabled: true
  host: "ponies.sparkleponyranch.com"
```

At SPR, Alan uses Kustomize for infrastructure overlays and Phong (shown as Phuong in some diagrams) provides Helm templates for developer-facing applications.
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/kustomize-helm-environment-management-diagram.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=ecf18519005a4b59dab858a309ddd67f" alt="The image is a diagram about managing environment configurations with Kustomize and Helm, featuring two individuals, Alan and Phuong, with Alan using Kustomize for infrastructure and Phuong preferring Helm for applications." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/kustomize-helm-environment-management-diagram.jpg" />
</Frame>

## Promotion strategies and CI/CD integration

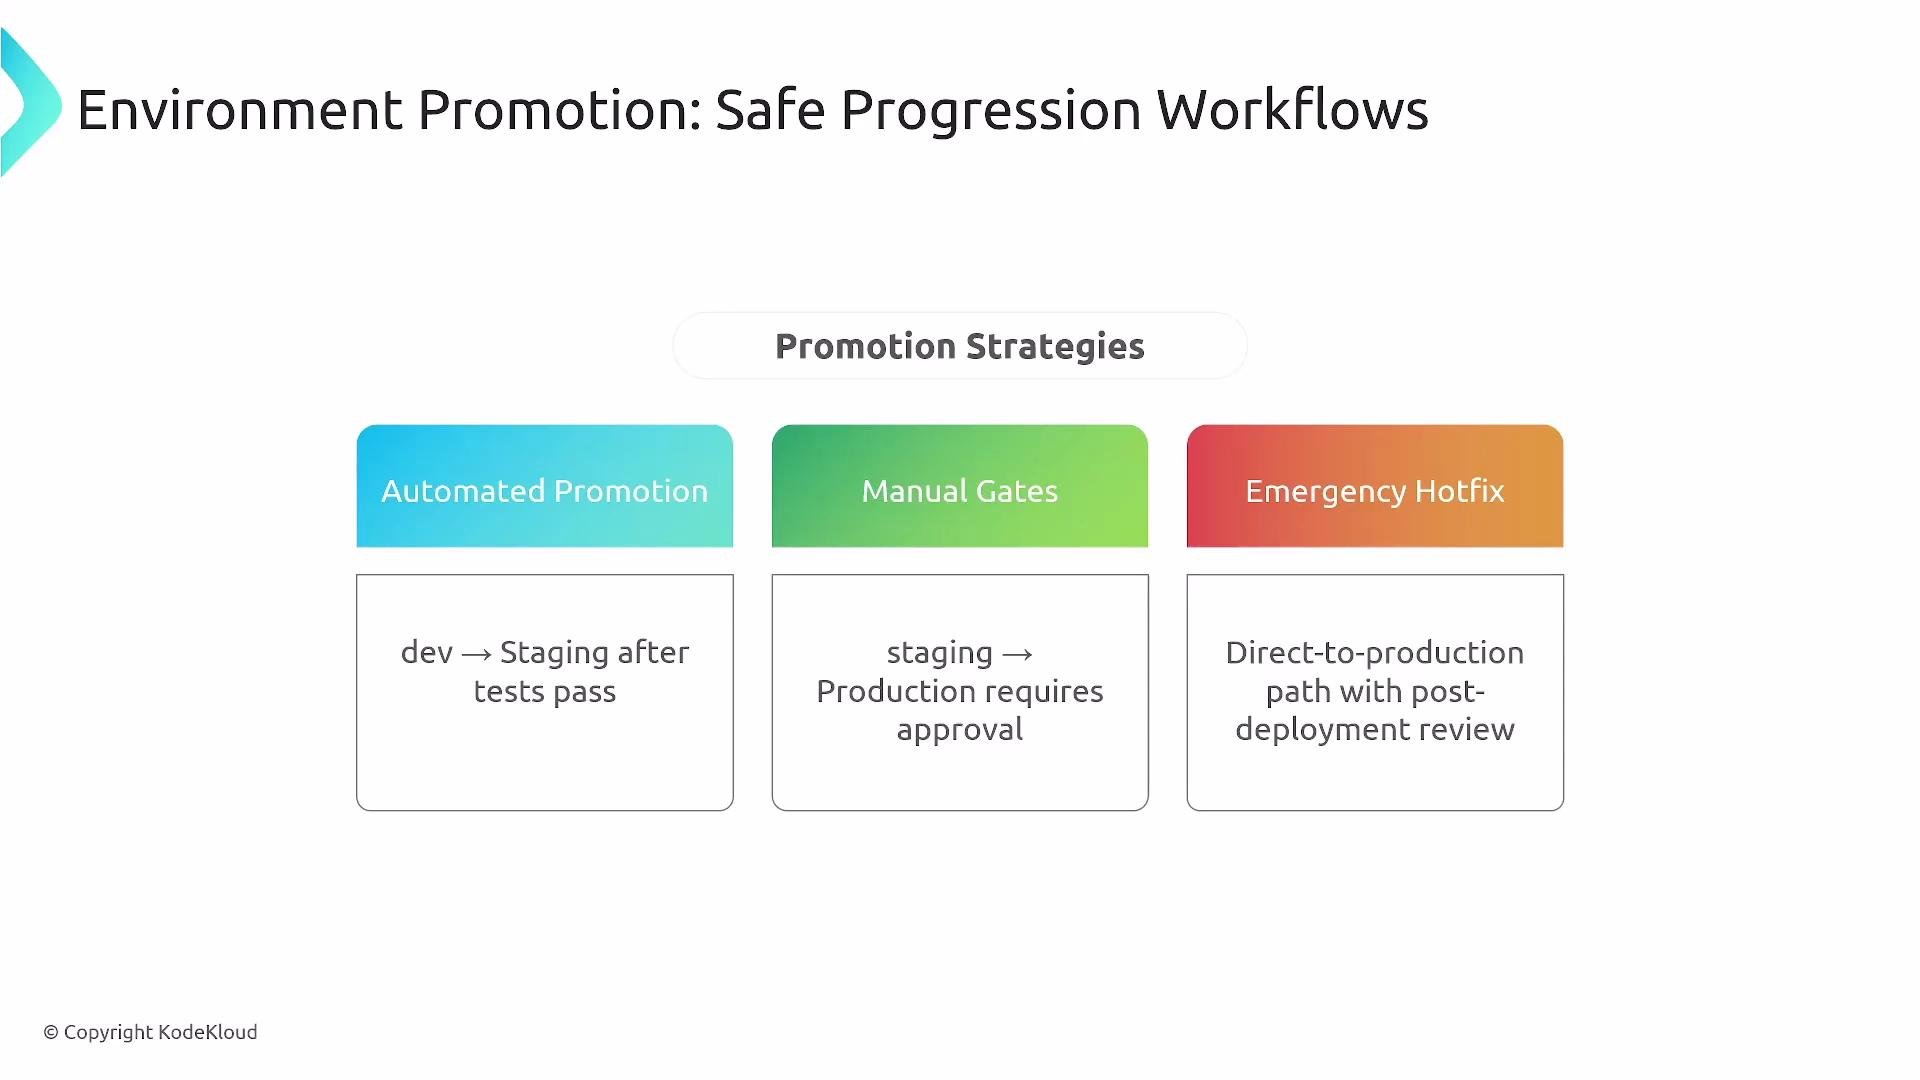
Promotion patterns:

* Automated promotion: CI updates the environment GitOps repo (fast, repeatable)
* Manual gates: human approvals for sensitive releases
* Emergency hotfix: a documented direct-to-prod process with pre/post-review
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/environment-promotion-strategies-diagram.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=d7cf9ee5545e51bc662b2488097c8542" alt="The image outlines environment promotion strategies, including automated promotion, manual gates, and emergency hotfix, detailing each approach for deploying code." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/environment-promotion-strategies-diagram.jpg" />
</Frame>

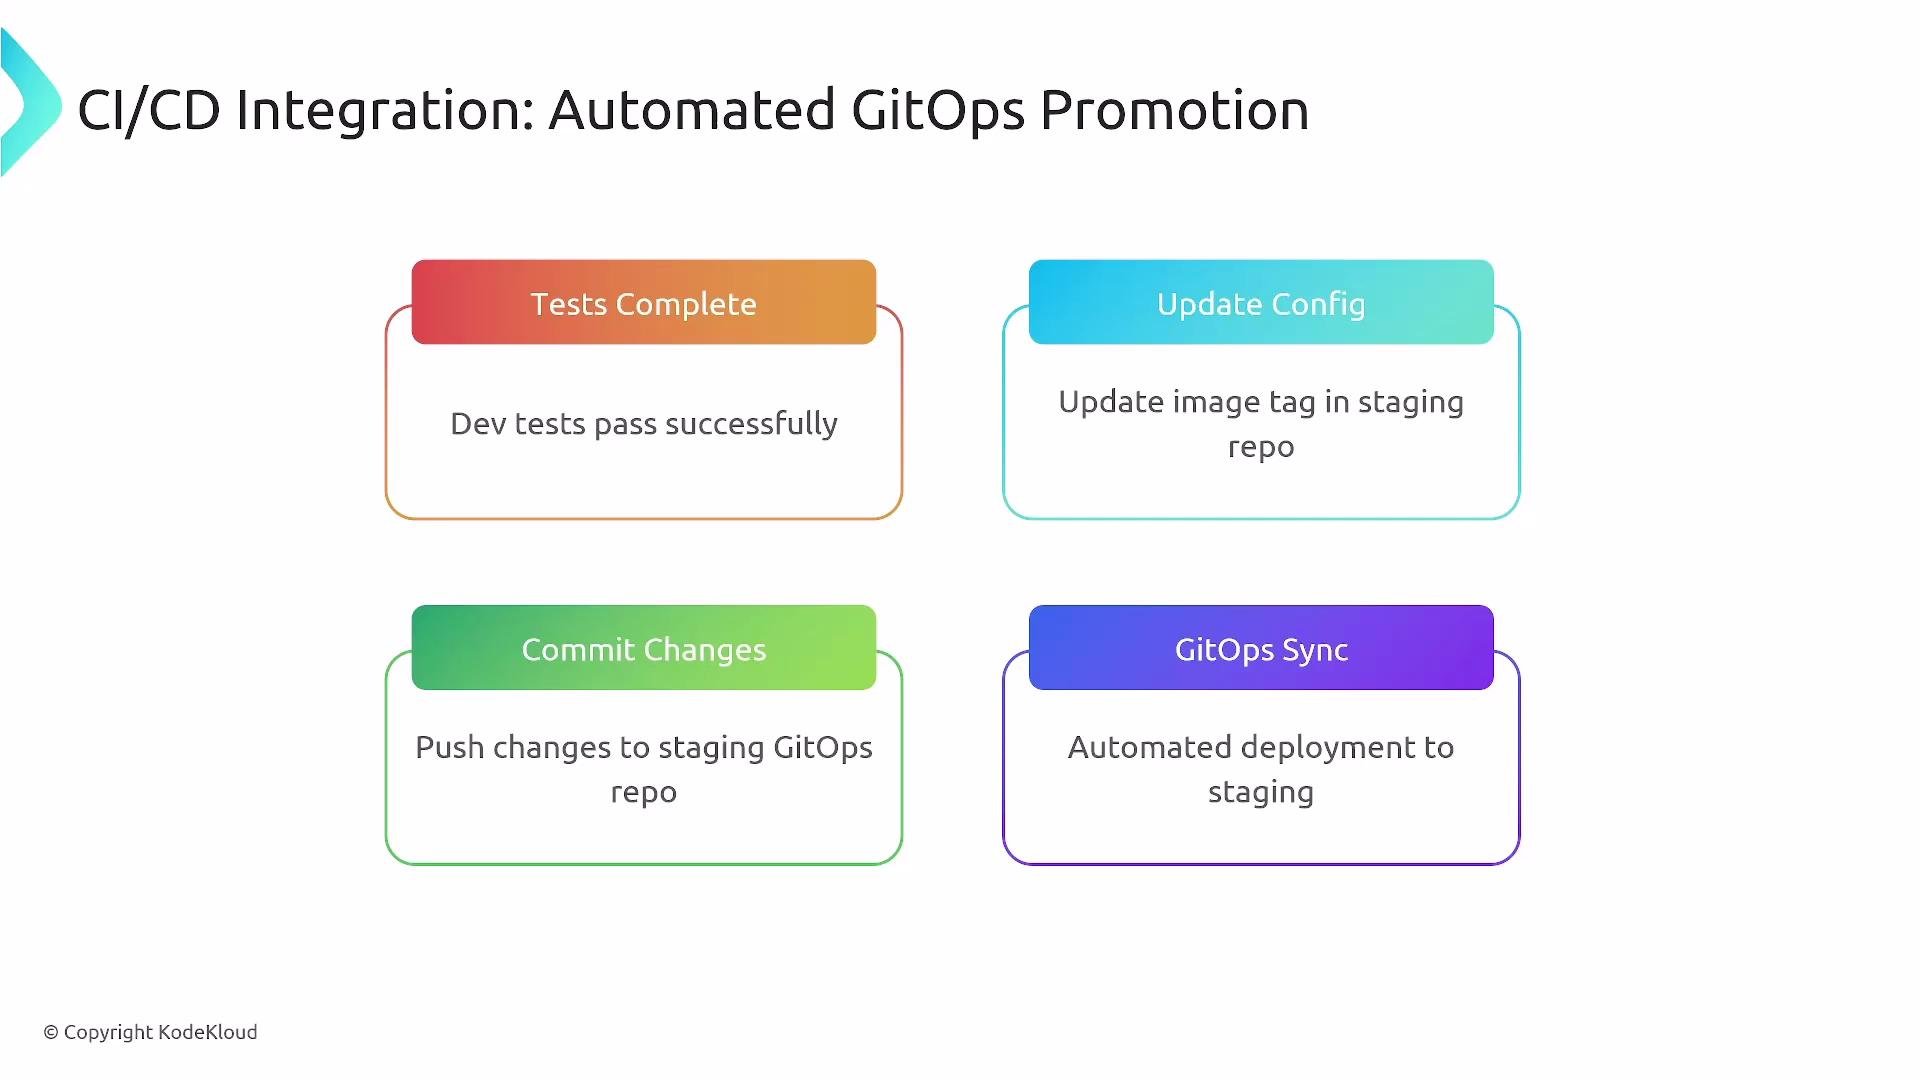
Typical CI/CD flow:

1. Build artifacts and run tests.
2. On success, update the GitOps repository (e.g., bump image tag or update values).
3. GitOps controller (Argo CD / Flux) detects the change and deploys.
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-promotion-process-cicd-pipeline.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=f9b8d8a267781e2ea1b15558551e35b7" alt="The image outlines an automated GitOps promotion process in a CI/CD pipeline, including steps for completing tests, updating configs, committing changes, and syncing GitOps for deployment." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-promotion-process-cicd-pipeline.jpg" />
</Frame>

Example GitHub Actions workflow: promote to staging by updating the staging GitOps repo after Dev Tests complete successfully.

```yaml theme={null}
# GitHub Actions promotion workflow
name: Promote to Staging
on:
  workflow_run:
    workflows: ["Dev Tests"]
    types: [completed]

jobs:
  promote:
    if: ${{ github.event.workflow_run.conclusion == 'success' }}
    runs-on: ubuntu-latest
    steps:
      - name: Checkout staging repo
        uses: actions/checkout@v4
        with:
          repository: spr/staging-gitops
          token: ${{ secrets.GITHUB_TOKEN }}
          path: staging

      - name: Update staging values with new tag
        env:
          NEW_TAG: ${{ github.sha }}
        run: |
          # Example using yq (mikefarah/yq v4+): https://github.com/mikefarah/yq
          yq eval '.image.tag = env(NEW_TAG)' -i staging/values.yaml

      - name: Commit and push change
        run: |
          cd staging
          git add values.yaml
          git commit -m "Promote pony-spawner to staging: $NEW_TAG" || echo "No changes to commit"
          git push origin HEAD:main
```

Note: this workflow requires proper RBAC and repository permissions so CI can push changes to the GitOps repo.

## Environment security, RBAC, and access patterns

Security controls to implement:

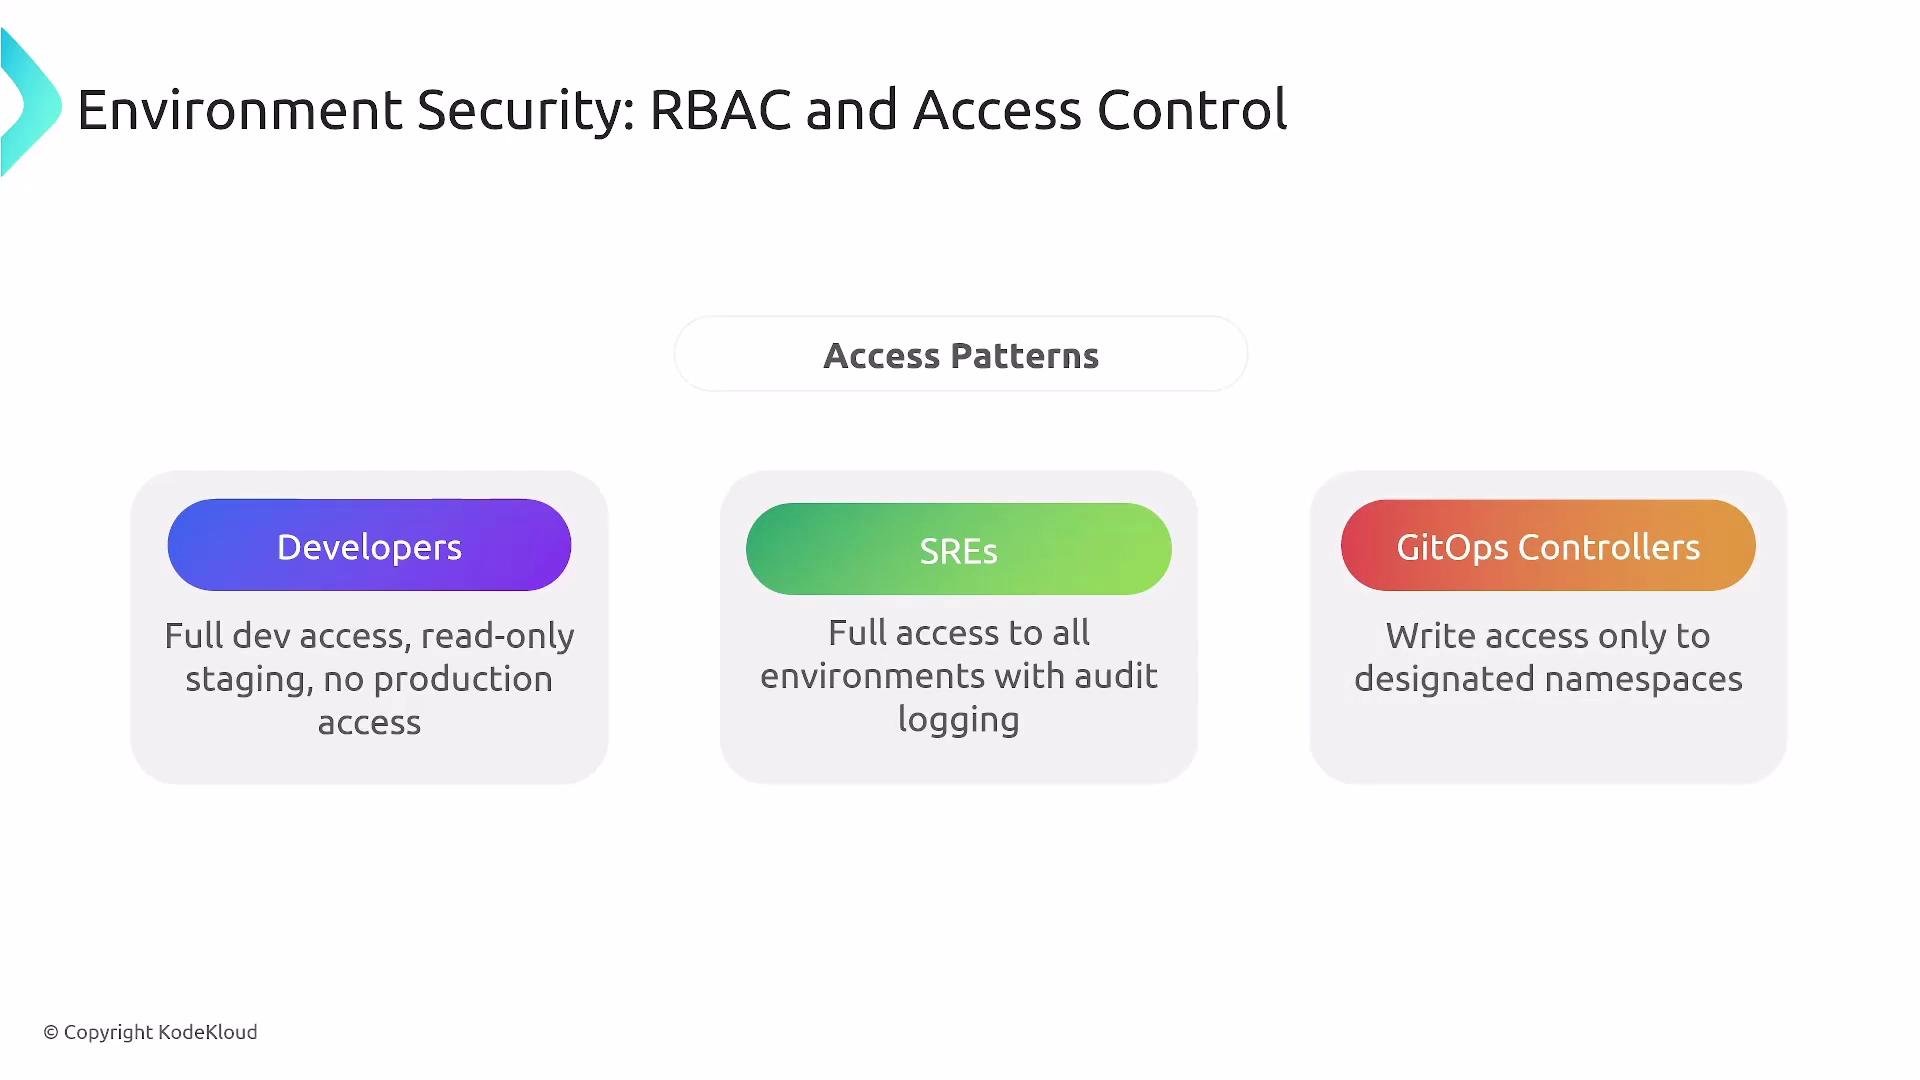
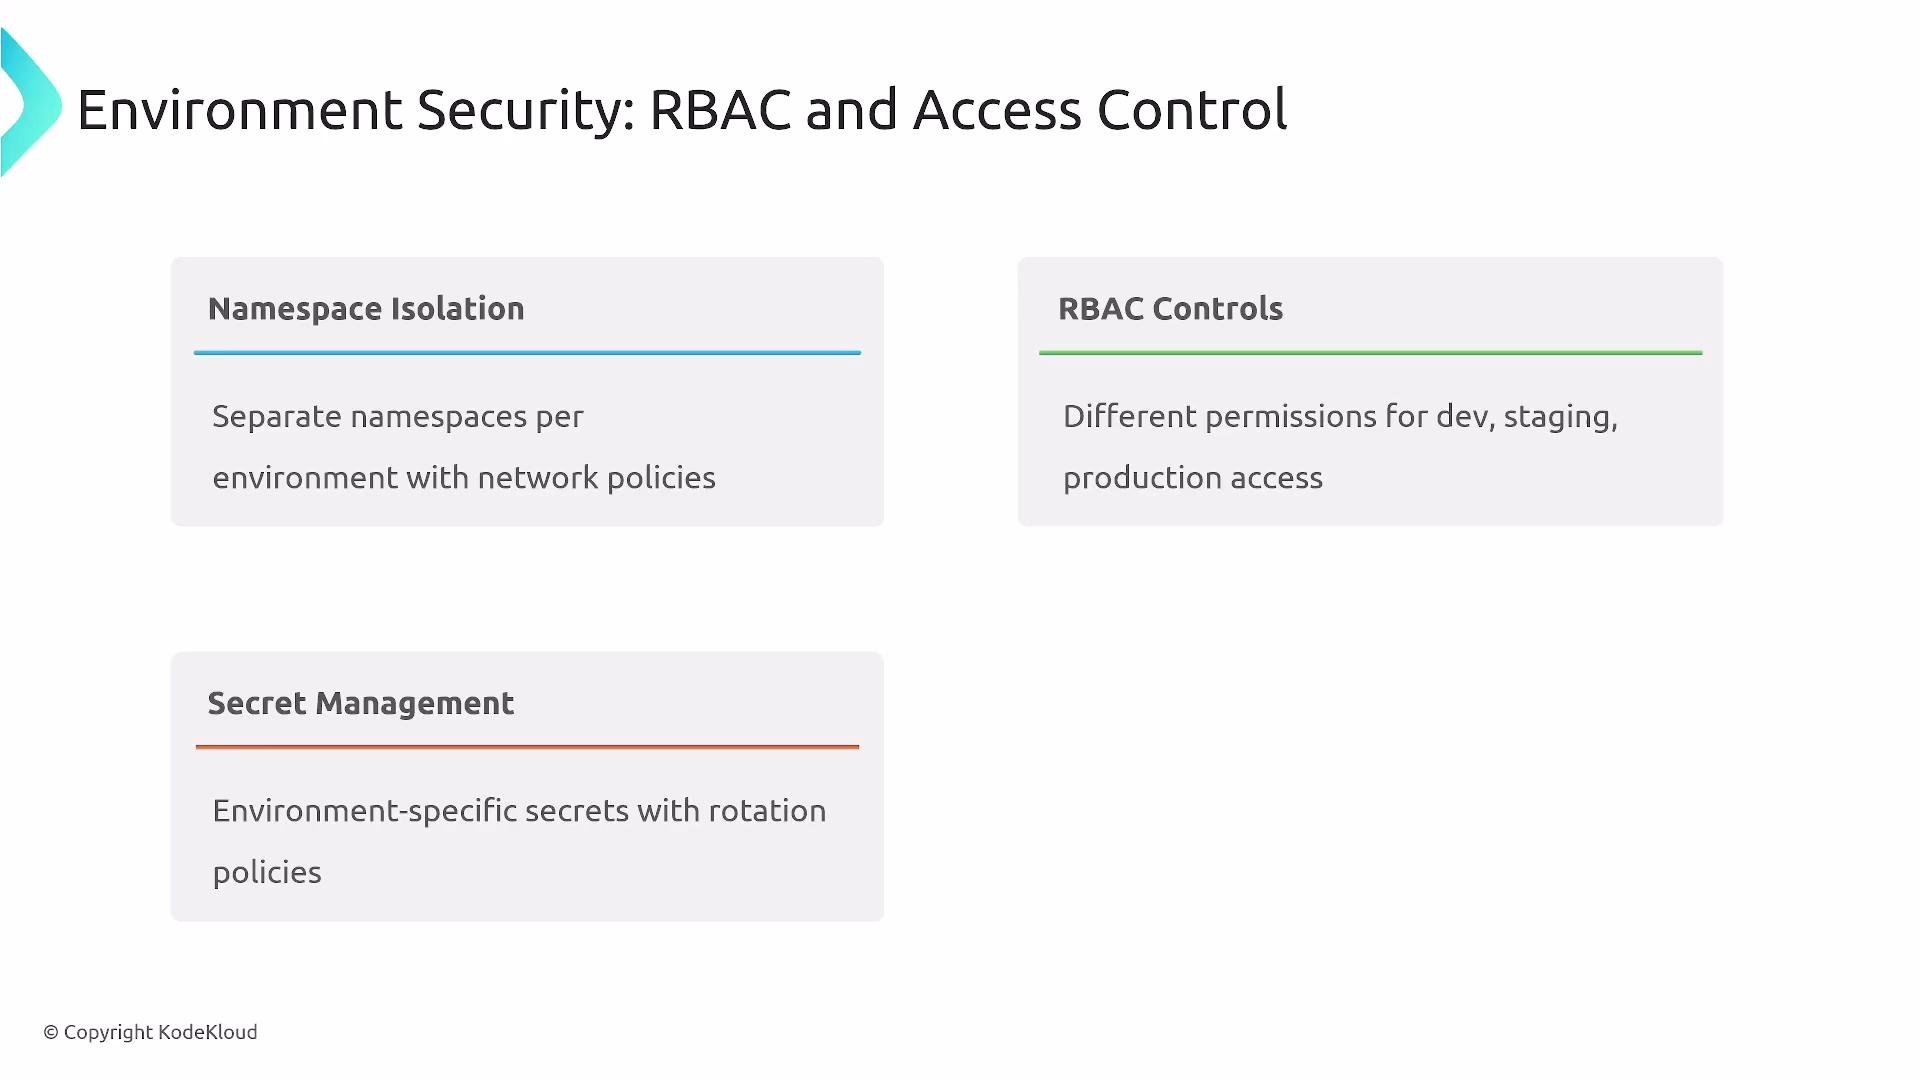
* Namespace isolation combined with RBAC
* Environment-specific secrets management (sealed/sealed-secrets/Vault integration)
* Least-privilege access patterns:
  * Developers: dev access only
  * Test/QA: limited staging access
  * SREs: broader access with audit logging
* Restrict GitOps controllers to the clusters/namespaces they manage
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/environment-security-rbac-access-control.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=855370e585c6d94090366a3bca58b6d8" alt="The image outlines concepts of environment security focusing on RBAC and access control, including namespace isolation, RBAC controls, and secret management." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/environment-security-rbac-access-control.jpg" />
</Frame>

Common access pattern overview:

<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/access-control-patterns-environment-security.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=47aa5e355411e21468d49e8e060877ce" alt="The image outlines access control patterns for environment security, detailing the roles and access levels for Developers, SREs, and GitOps Controllers." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/access-control-patterns-environment-security.jpg" />
</Frame>

Argo CD RBAC example snippet:

```yaml theme={null}
# Argo CD RBAC for environments (policy config)
policy.default: role:readonly

policy.csv: |
  p, role:dev-team, applications, *, dev/*, allow
  p, role:staging-reviewer, applications, sync, staging/*, allow
  p, role:prod-admin, applications, *, prod/*, allow

  g, spr:developers, role:dev-team
  g, spr:sre-team, role:prod-admin
```

Good RBAC both prevents unsafe access and enables teams to perform necessary tasks safely and audibly.

## Monitoring and debugging GitOps

Track high-value GitOps signals:

* Sync status (synced, out-of-sync, drift)
* Time from Git commit to deploy (lead time)
* Deployment cadence per environment
* Failed syncs, rollbacks, and manual interventions
* Error rates and rollback frequency

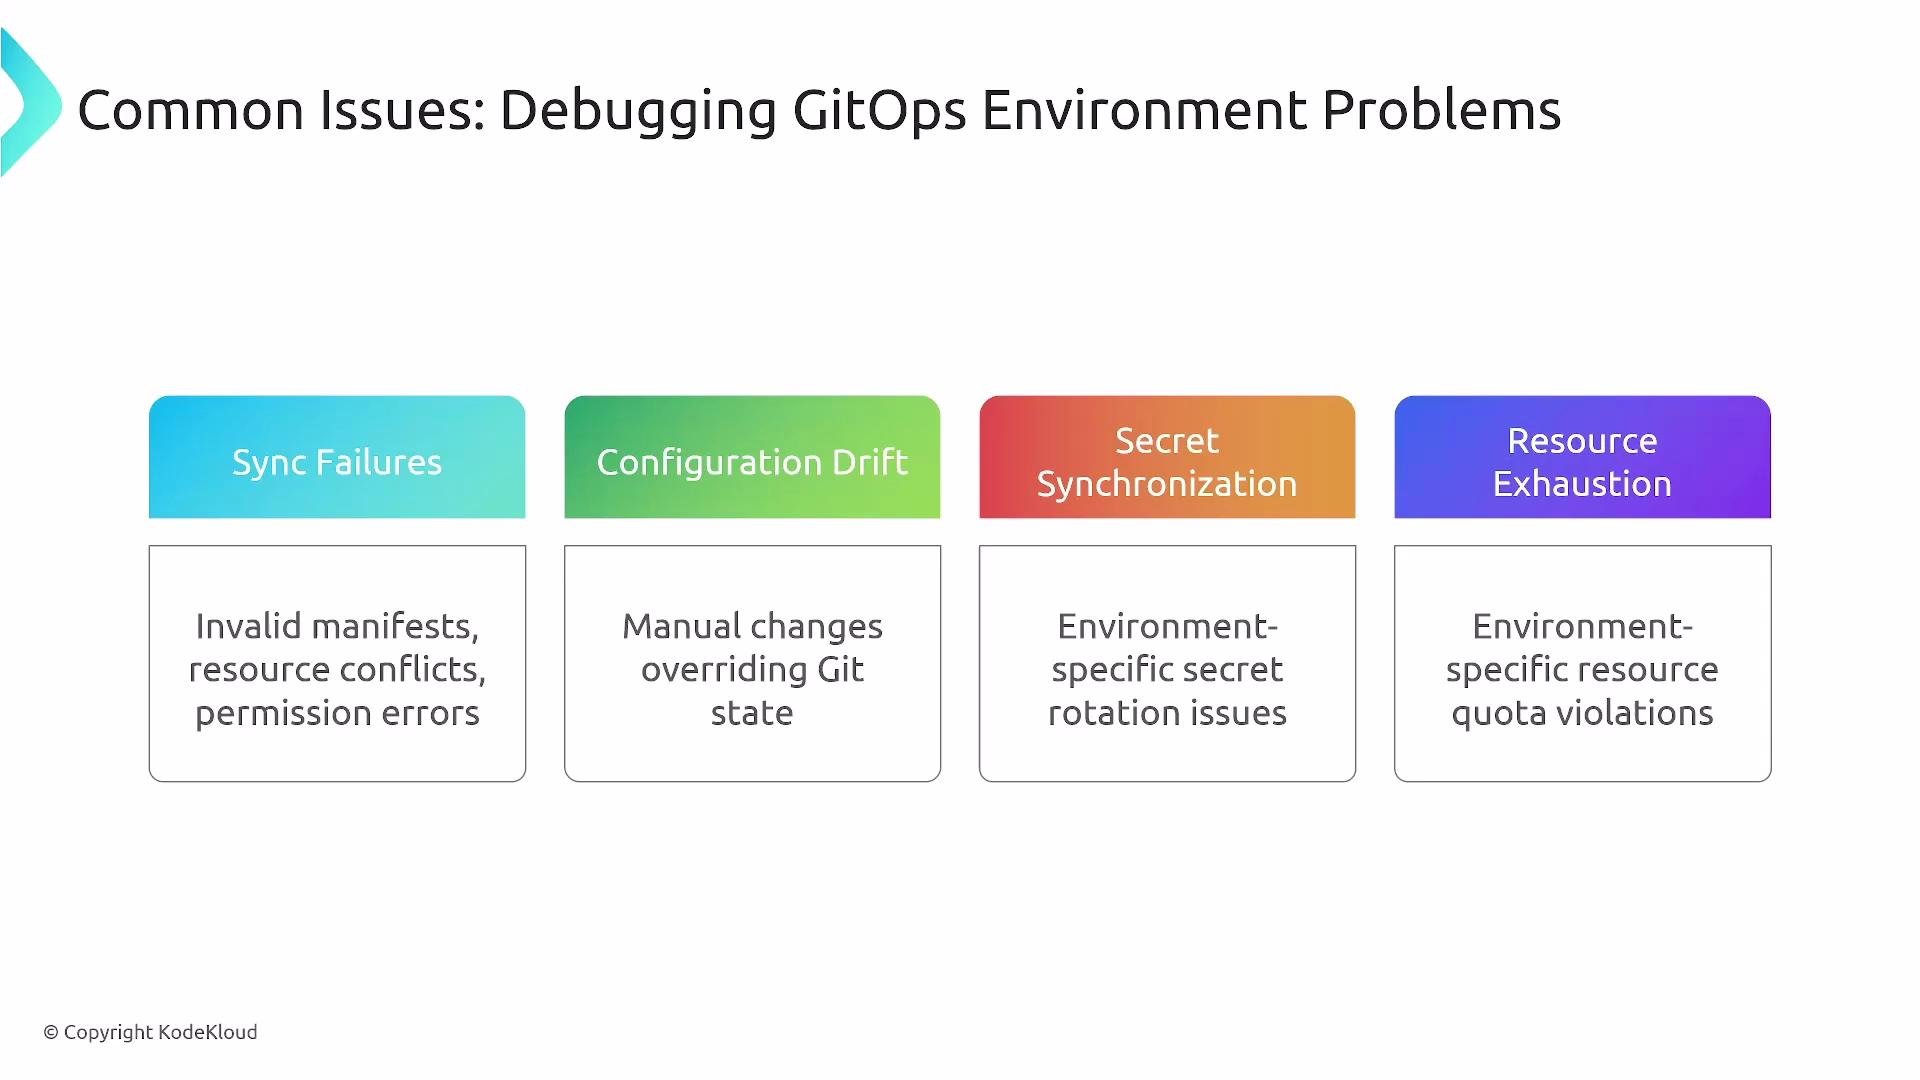
Common debugging issues:

* Sync failures and configuration drift
* Secret synchronization errors
* Resource exhaustion or quota limits
* Misconfigured autoscalers or insufficient capacity

Use the Argo CD UI (or Flux tooling), kubectl, Git history, and your platform monitoring/alerting to investigate. Ensure GitOps controller metrics and failure alerts are integrated into the platform monitoring stack.
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-debugging-issues-list-examples.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=b2e9b6c4b7350ea0661552aea3e9d6dd" alt="The image lists common issues in debugging GitOps environments, including sync failures, configuration drift, secret synchronization, and resource exhaustion, with examples of each." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-debugging-issues-list-examples.jpg" />
</Frame>

<Callout icon="lightbulb" color="#1CB2FE">
  Monitor sync health, failed syncs, and rollback counts. These signals surface gaps in test coverage, configuration issues, and operational risk.
</Callout>

## Key takeaways

* Environments typically progress from multiple dev/test environments to staging and production; ephemeral environments (PR-based, load-testing) improve validation confidence.
* Repository organization (monorepo vs multi-repo) has trade-offs — select the model that fits team size, autonomy, and governance.
* Configuration management: Kustomize (overlay/patch model) and Helm (templated values) both support environment-specific manifests.
* Automated promotion via CI updating GitOps repos is fast and repeatable but requires robust tests; manual gates remain valuable for critical releases.
* Security: enforce least privilege, environment-scoped secrets, and controlled RBAC for controllers and teams.
* Observability of GitOps controllers and environments is essential to detect drift and ensure reliable promotions.
* Apply patterns that suit team tooling, scale, and risk tolerance.
<Frame>
  <img src="https://mintcdn.com/kodekloud-c4ac6d9a/AUEsr5pTA6SA2QbB/images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-scalable-application-delivery-takeaways.jpg?fit=max&auto=format&n=AUEsr5pTA6SA2QbB&q=85&s=bd15e9d78eac7cf156ecf56674787232" alt="The image lists eight key takeaways for GitOps environments related to scalable application delivery, including environment progression, repository organization, and security integration. Each takeaway is numbered and represented with a colored icon." width="1920" height="1080" data-path="images/Prep-Course-Certified-Cloud-Native-Platform-Engineering-Associate-CNPA/Domain-3-Continuous-Delivery-Platform-Engineering/GitOps-for-Application-Environments/gitops-scalable-application-delivery-takeaways.jpg" />
</Frame>

GitOps enables rapid, safe application delivery with auditable promotion paths. With environment templates, RBAC, thorough test coverage, and integrated monitoring, platform teams can accelerate feature delivery while maintaining control and traceability.

Thank you — this concludes the lesson on GitOps for Application Environments.

## Links and references

* Argo CD: [https://argo-cd.readthedocs.io/en/stable/](https://argo-cd.readthedocs.io/en/stable/)
* Flux: [https://fluxcd.io/](https://fluxcd.io/)
* Kustomize: [https://kustomize.io/](https://kustomize.io/)
* Helm: [https://helm.sh/](https://helm.sh/)
* GitHub Actions: [https://docs.github.com/en/actions](https://docs.github.com/en/actions)

<CardGroup>
  <Card title="Watch Video" icon="video" cta="Learn more" href="https://learn.kodekloud.com/user/courses/certified-cloud-native-platform-engineering-associate-cnpa/module/b1af4eef-35d2-47b1-8964-1e80b1f1a739/lesson/53e851ca-9f83-4d41-8925-39fc2900e261" />
</CardGroup>


This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.