

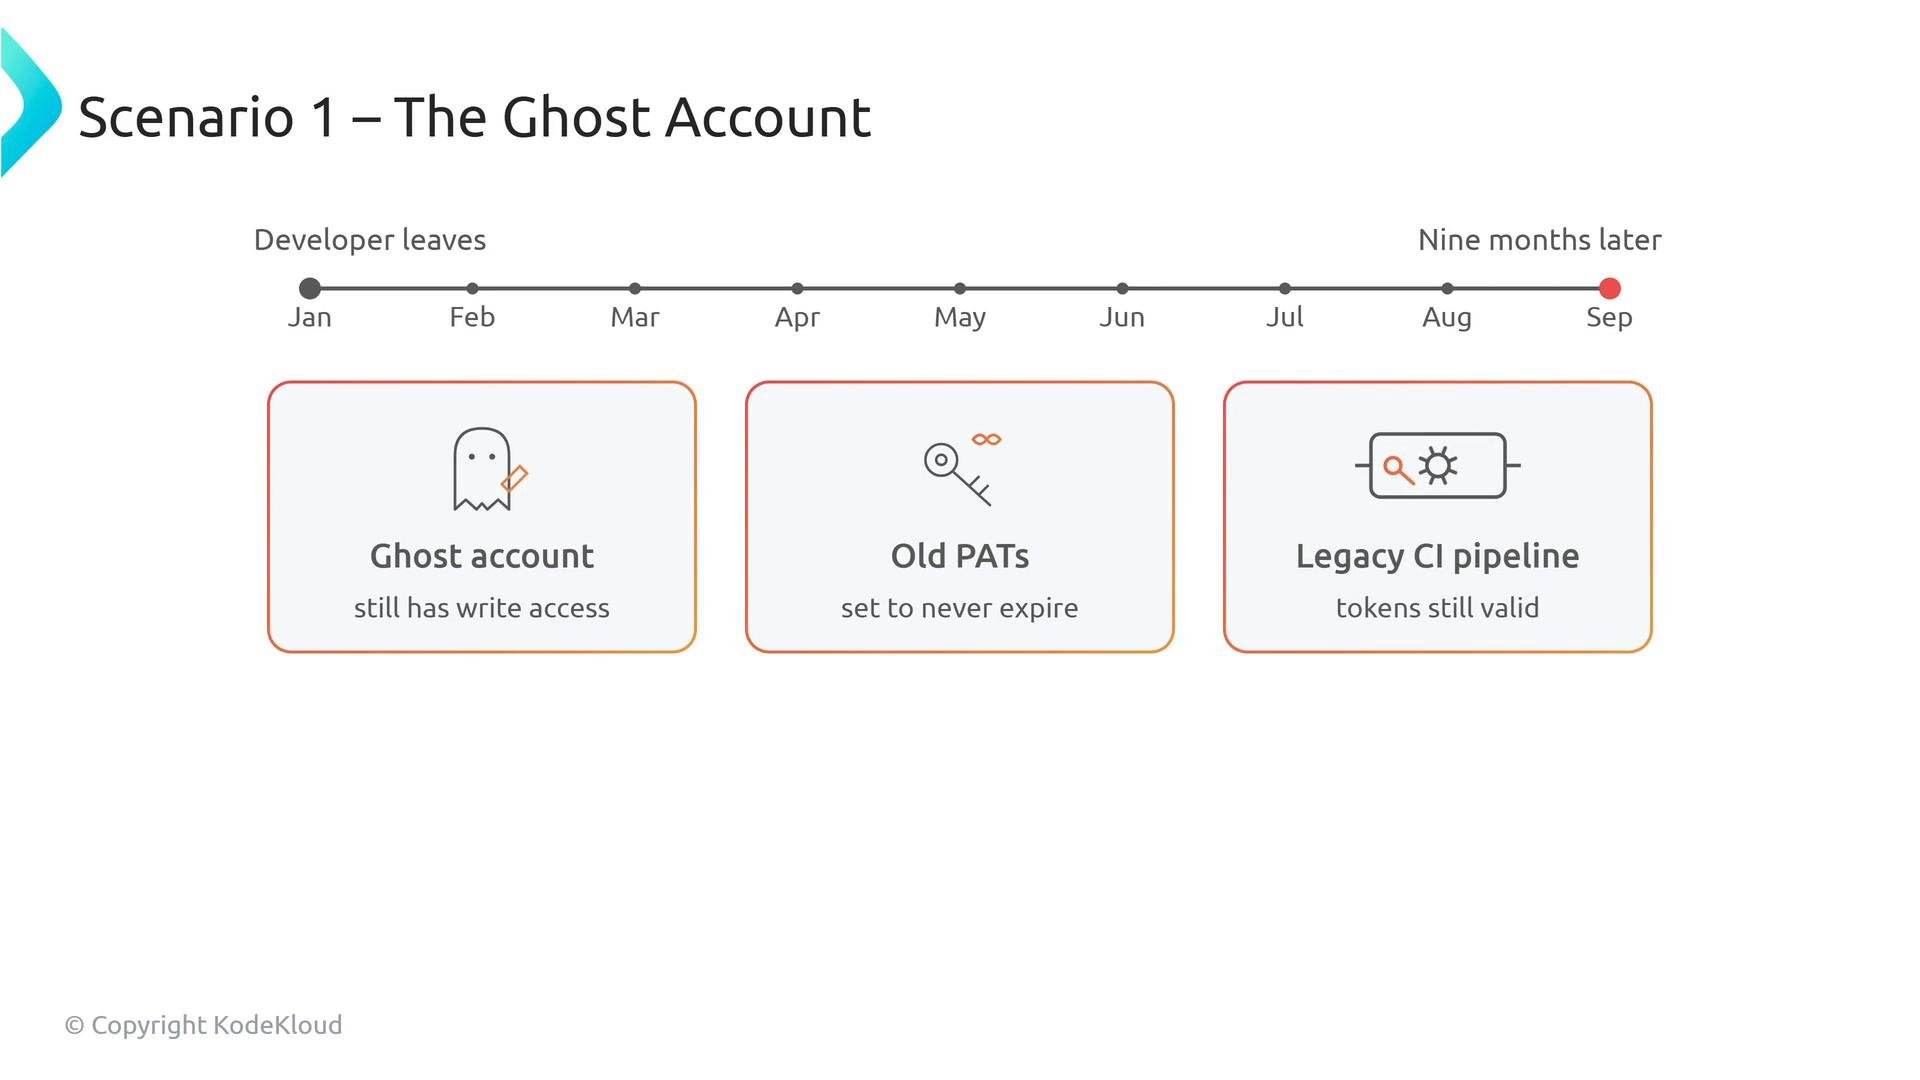
- Stale user accounts and long-lived tokens A developer leaves in January, but their account and API tokens remain active through September because deprovisioning isn’t automated. Their personal access tokens (PATs) were created with no expiry and are still used in a legacy CI pipeline. That creates a nine-month window for an attacker to access repositories, inject malware, or exfiltrate data.
- Accidental secret commits A simple mistake — committing cloud credentials — can turn into a weekend incident. Example:
- Runaway CI/CD costs and unchecked runners Unrestricted use of inexpensive or expensive runners (for example, macOS runners) across thousands of PRs and CI jobs can produce enormous bills. If teams run macOS runners on every comment or PR without governance, GitHub Actions usage can explode and result in large overage charges that impact the finance organization.
A useful mental model: treat GitHub Enterprise like a major airport. Thousands of people and automated processes move through it daily. The GitHub Enterprise administrator is simultaneously the air traffic controller, the security checkpoint, and the operations manager. Without RBAC and least-privilege, SAML single sign-on and automated deprovisioning, secret scanning and push protection, and policy enforcement for CI/CD runners, processes will collide and incidents will follow.
That is exactly why the GitHub Enterprise Administrator role exists — to bring order, reduce attack surface, and limit corporate liability.
Key priorities for GitHub Enterprise administrators: implement RBAC and least privilege, enable SAML/SSO with automated deprovisioning, enforce token lifecycle policies (no never-expiring
PATs — see https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token), enable secret scanning and push protection, and govern CI/CD runner usage and costs.- GitHub SAML SSO: https://docs.github.com/en/authentication/connecting-to-github-with-saml-single-sign-on
- Personal access tokens (PATs): https://docs.github.com/en/authentication/keeping-your-account-and-data-secure/creating-a-personal-access-token
- Secret scanning: https://docs.github.com/en/code-security/secret-scanning
- GitHub Actions runners: https://docs.github.com/en/actions/using-github-hosted-runners/about-github-hosted-runners