

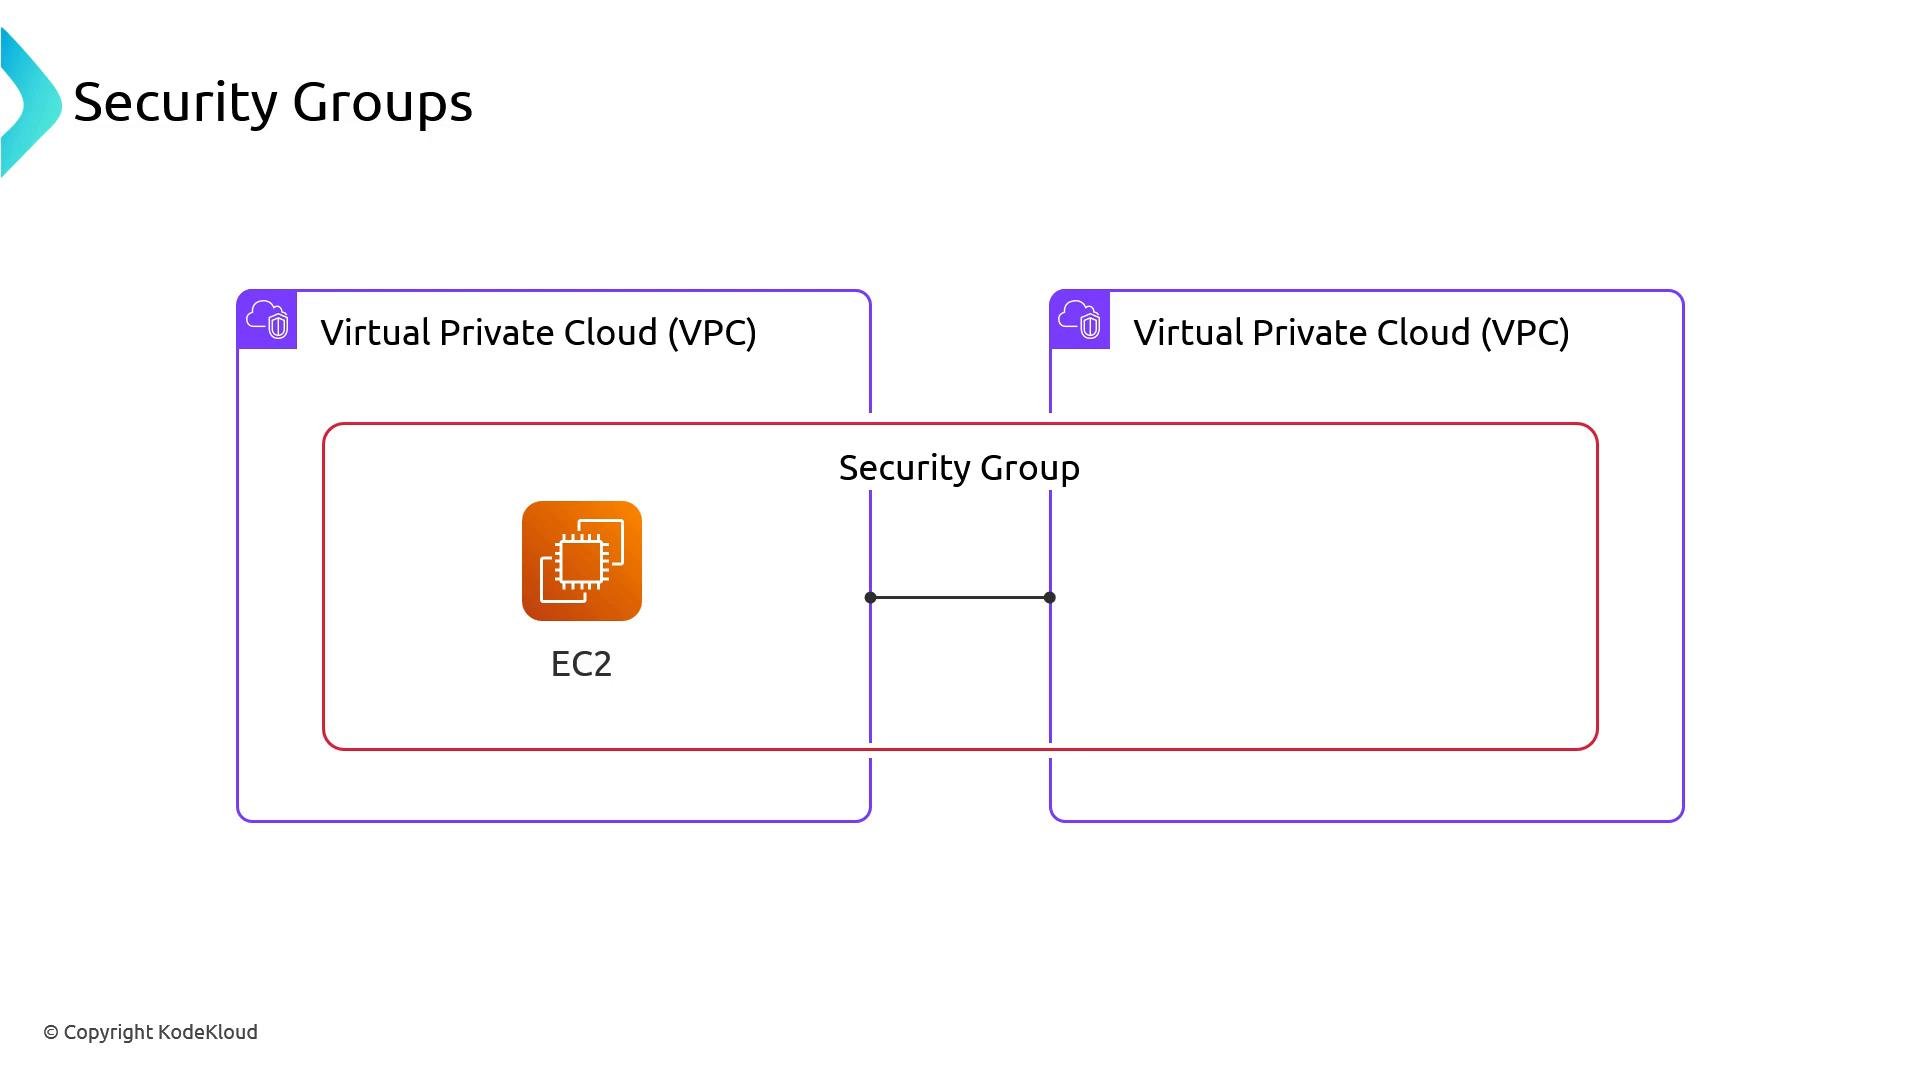
aws-node) assigns pod IPs from ENIs attached to each node. Node ENIs share the node’s security groups, so opening a port between nodes and an AWS resource (for example RDS) effectively allows any pod on those nodes to contact that resource at the network layer. Authentication and authorization must still be enforced with IAM, but the networking allowance is uniform for all pods on the node.
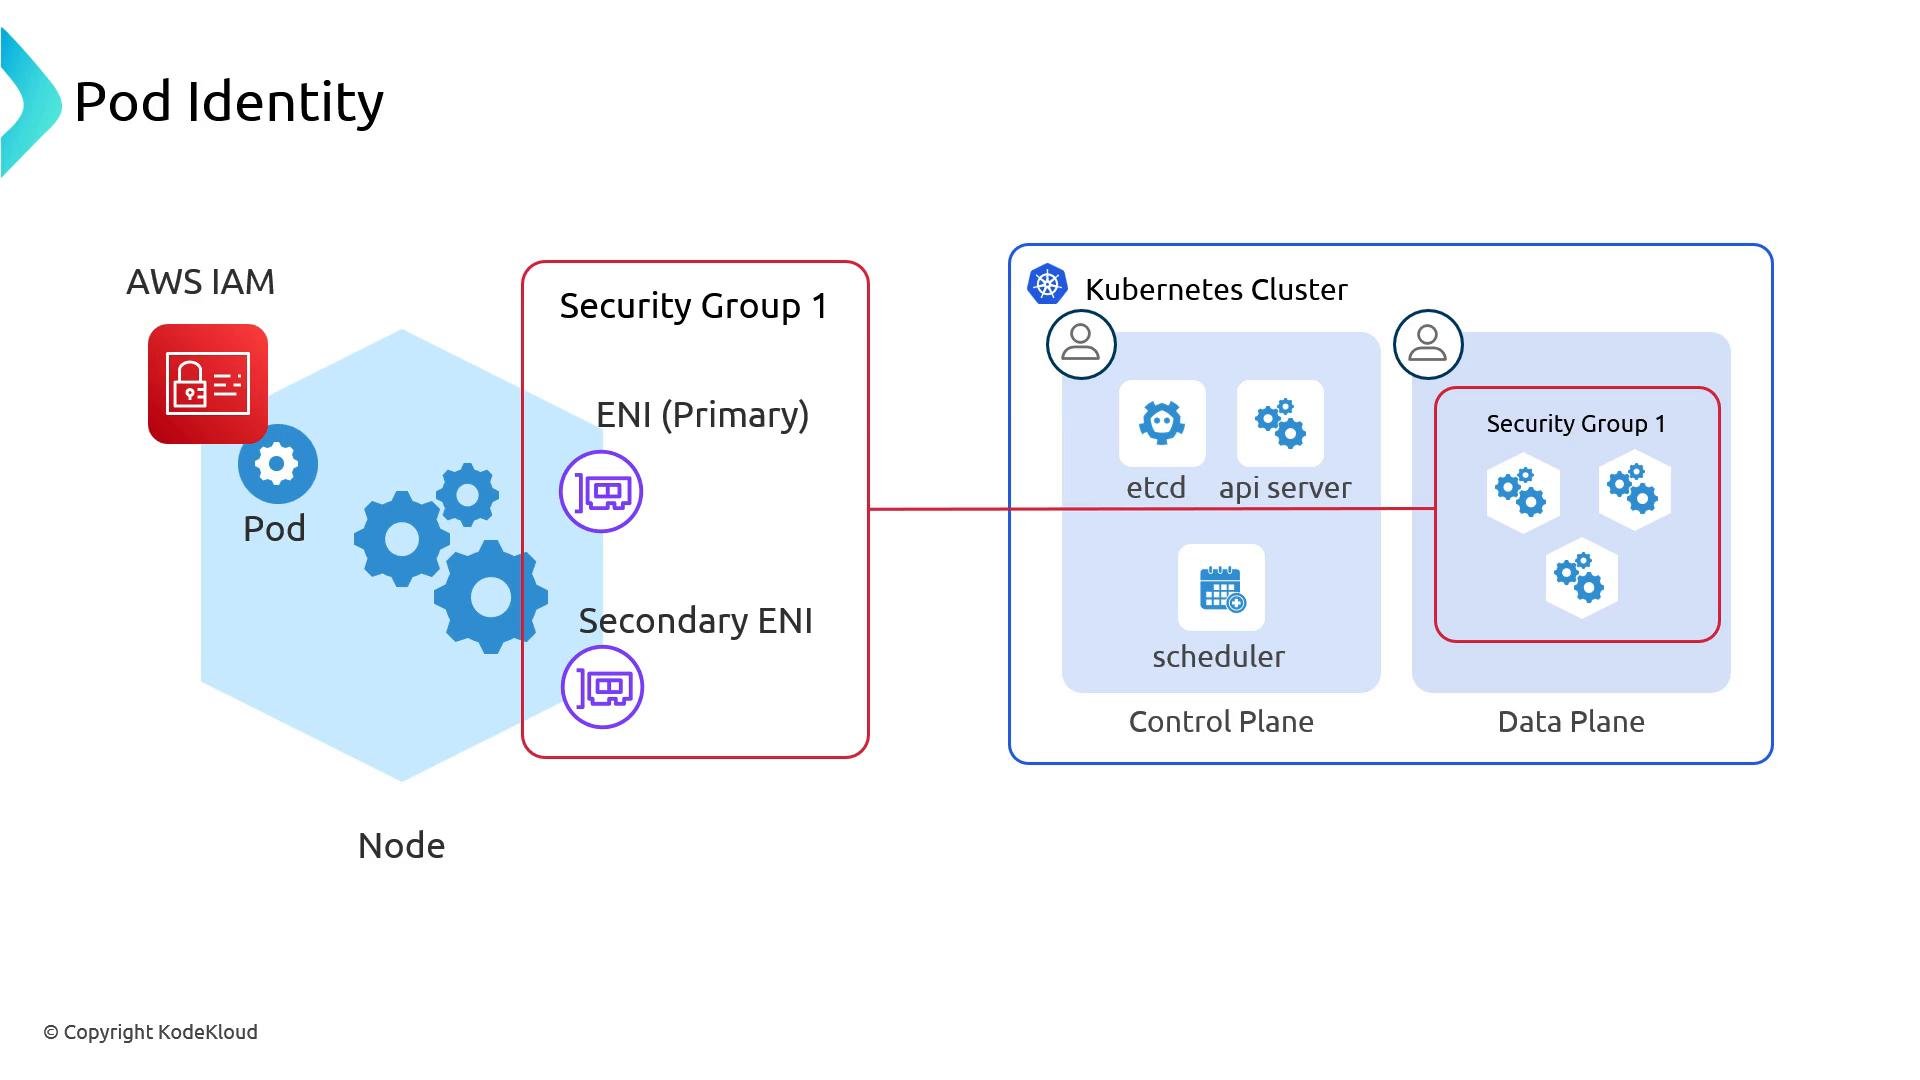
Security groups for pods add network-layer controls specific to individual workloads, but they increase operational surface area. Prefer pod-level IAM (IRSA) and Kubernetes NetworkPolicies for most use cases unless you require per-pod SGs.
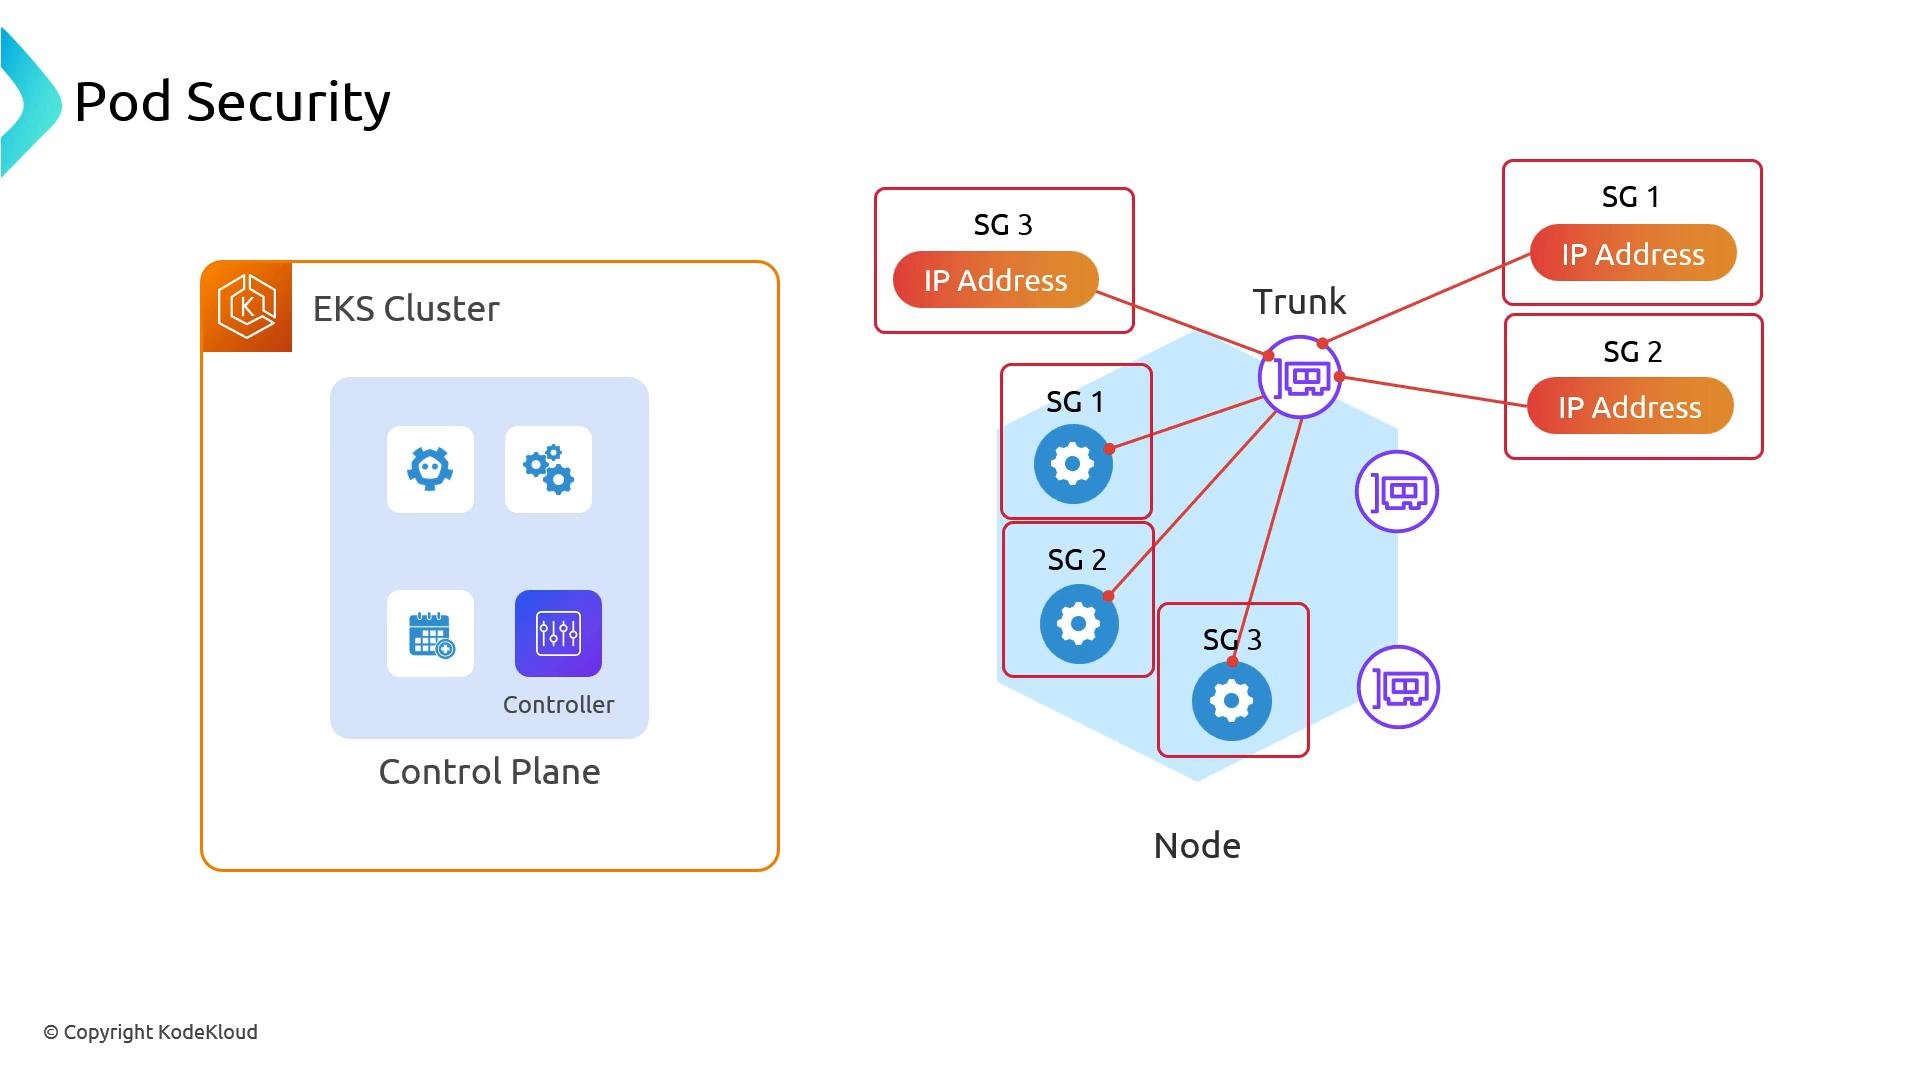
- You must enable the AWS VPC CNI feature that supports security groups for pods and install the cluster-side controller (vpc-resource-controller). The controller coordinates with EC2 trunking APIs.
- AWS creates a trunk ENI on the node. Branch ENIs are attached to that trunk via trunking; branch ENIs can have independent security groups applied.
- Pods assigned IPs from branch ENIs effectively inherit the branch ENI’s security groups, enabling per‑pod network ACLs.
- This trunk/branch model makes per-pod security groups possible, but it changes how IPs are allocated and introduces additional operational considerations (ENI lifecycle, IP accounting, instance type compatibility).
- Instance type support
- Not every EC2 instance type supports ENI trunking. Many Nitro-based instances do, but support is not universal.
- Check the VPC CNI docs and the maintained instance maps for trunking support:
- AWS VPC CNI: https://github.com/aws/amazon-vpc-cni-k8s
- Trunking docs & instance maps in the repo’s
docsfolder
- IP and pod accounting (
maxPods)
maxPodsdetermines how many pod IPs the VPC CNI expects to manage per node.- Pods that receive IPs via branch ENIs for security groups may not follow the same allocation heuristics as standard ENIs, causing unexpected IP exhaustion if
maxPodsand node capacity are not planned accordingly. - In managed node groups,
maxPodsis typically set per node group. To varymaxPodsand ENI behavior you’ll need separate node groups, custom AMIs/kubelet config, or a scheduler/provisioner such as Karpenter to supply different node classes.
- Replacing VPC CNI with other CNIs
- Using alternative CNIs (for example, Calico or Cilium) complicates pod security groups further. Those CNIs manage IPs and networking differently, so integrating ENI trunking/branch ENI behavior on top can be difficult to maintain and troubleshoot.
Trunking and branch ENI behavior depend on AWS-managed APIs and specific instance capabilities. Debugging network issues can be difficult—only adopt pod-level security groups if your team has tooling and experience to manage ENI lifecycle, IP accounting, and AWS trunking behavior.
- Use pod security groups if you require strict per‑pod network isolation that cannot be achieved with NetworkPolicies or IAM.
- Avoid pod security groups for teams without automated SG lifecycle management or visibility into ENI behavior.
- Confirm instance types in your node pools support ENI trunking.
- Update cluster VPC CNI and install
vpc-resource-controllerper the release notes. - Plan
maxPodsand node capacity to avoid IP address exhaustion. - Automate security group lifecycle management (creation, tagging, cleanup) and monitoring.
- Test in a staging environment that mirrors production ENI/instance types.
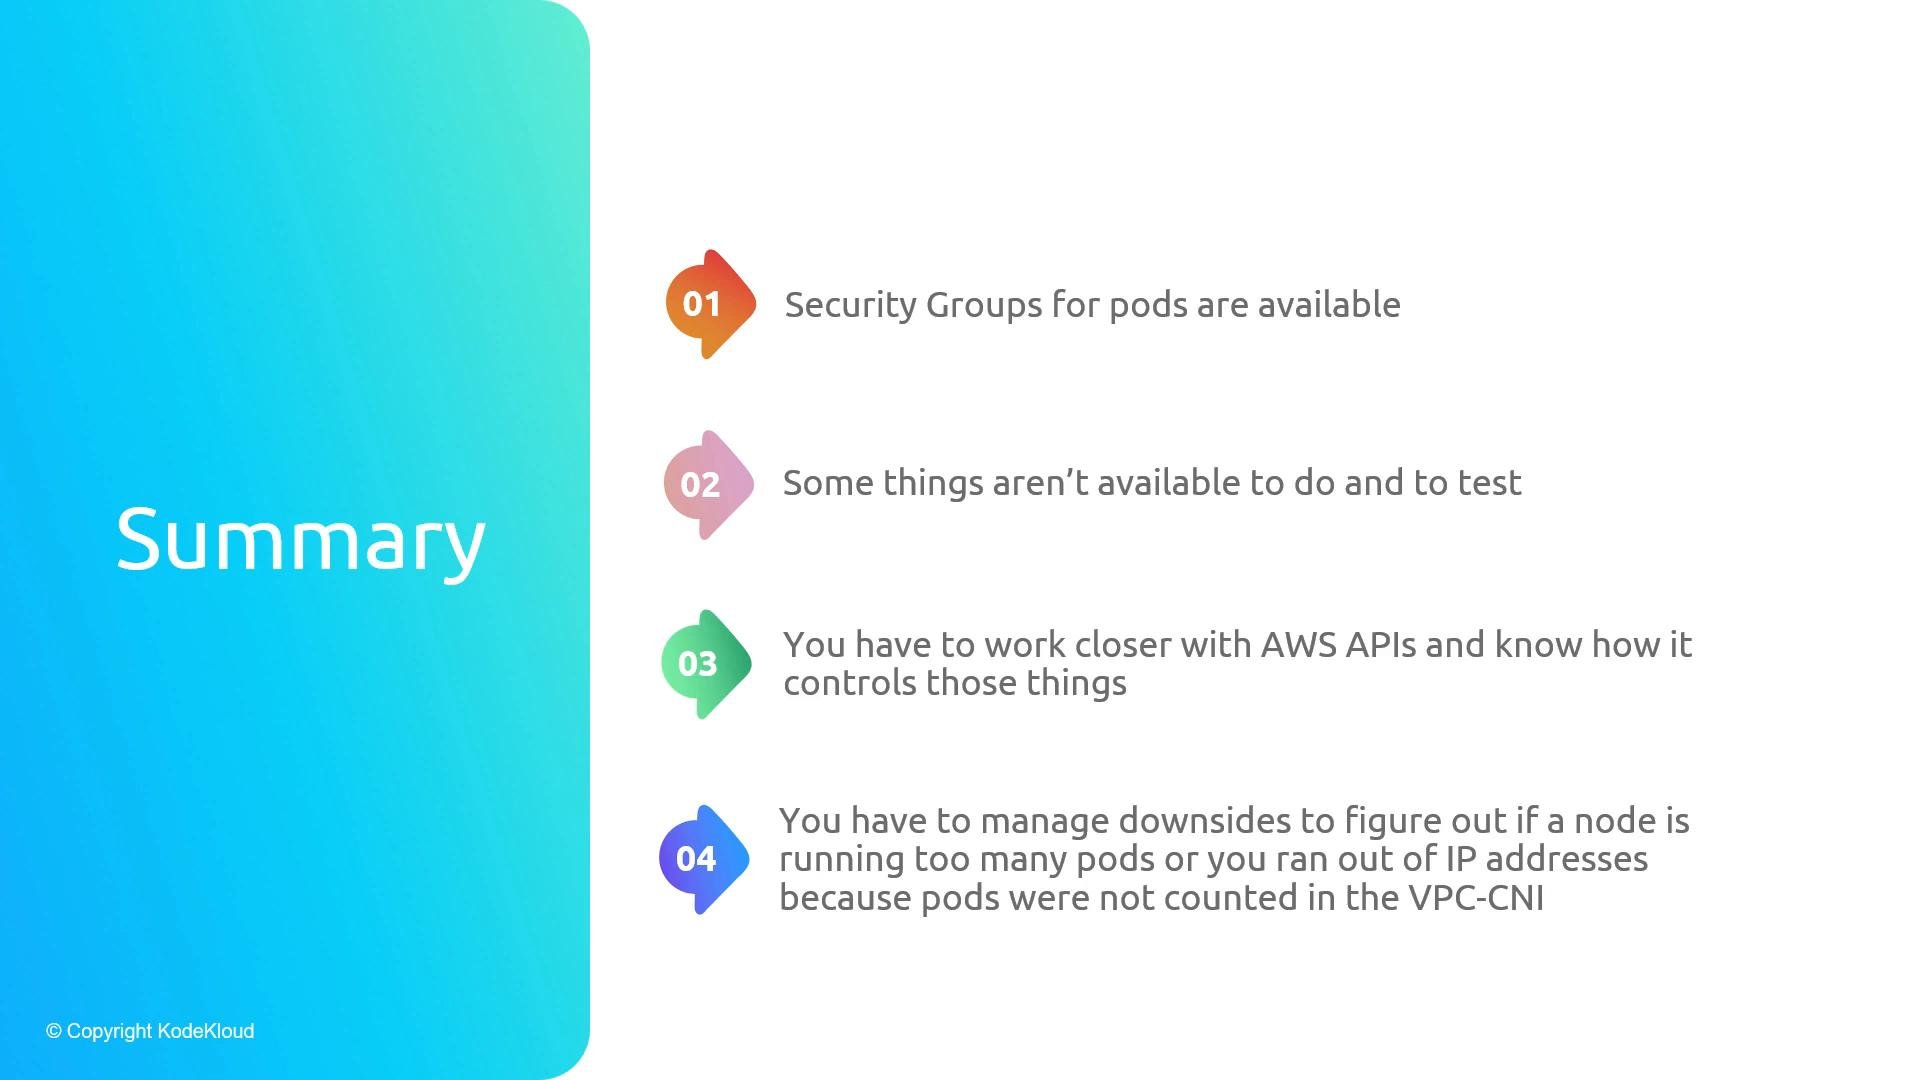
- Pod security groups enable per-pod network controls by using ENI trunking (trunk + branch ENIs), but they add operational complexity and require instance support.
- You must work closely with the VPC CNI and the EC2 trunking model and plan for IP accounting (
maxPods) and node group design. - Prefer IRSA (pod IAM), Kubernetes NetworkPolicies, separate node groups, or cluster isolation for most use cases unless you have automation and expertise to operate pod-level security groups.
- AWS VPC CNI (amazon-vpc-cni-k8s): https://github.com/aws/amazon-vpc-cni-k8s
- EKS IRSA (IAM Roles for Service Accounts): https://docs.aws.amazon.com/eks/latest/userguide/iam-roles-for-service-accounts.html
- Karpenter: https://karpenter.sh/
- Calico: https://docs.projectcalico.org/
- Cilium: https://cilium.io/