

- Clone the template to create one controller (AnsibleController) and two targets (target1, target2).
- Start the VMs and determine their IP addresses.
- Configure hostnames and SSH host keys.
- Install
ansible-coreon the controller and verify connectivity using thepingmodule.
- Clone the controller and target VMs
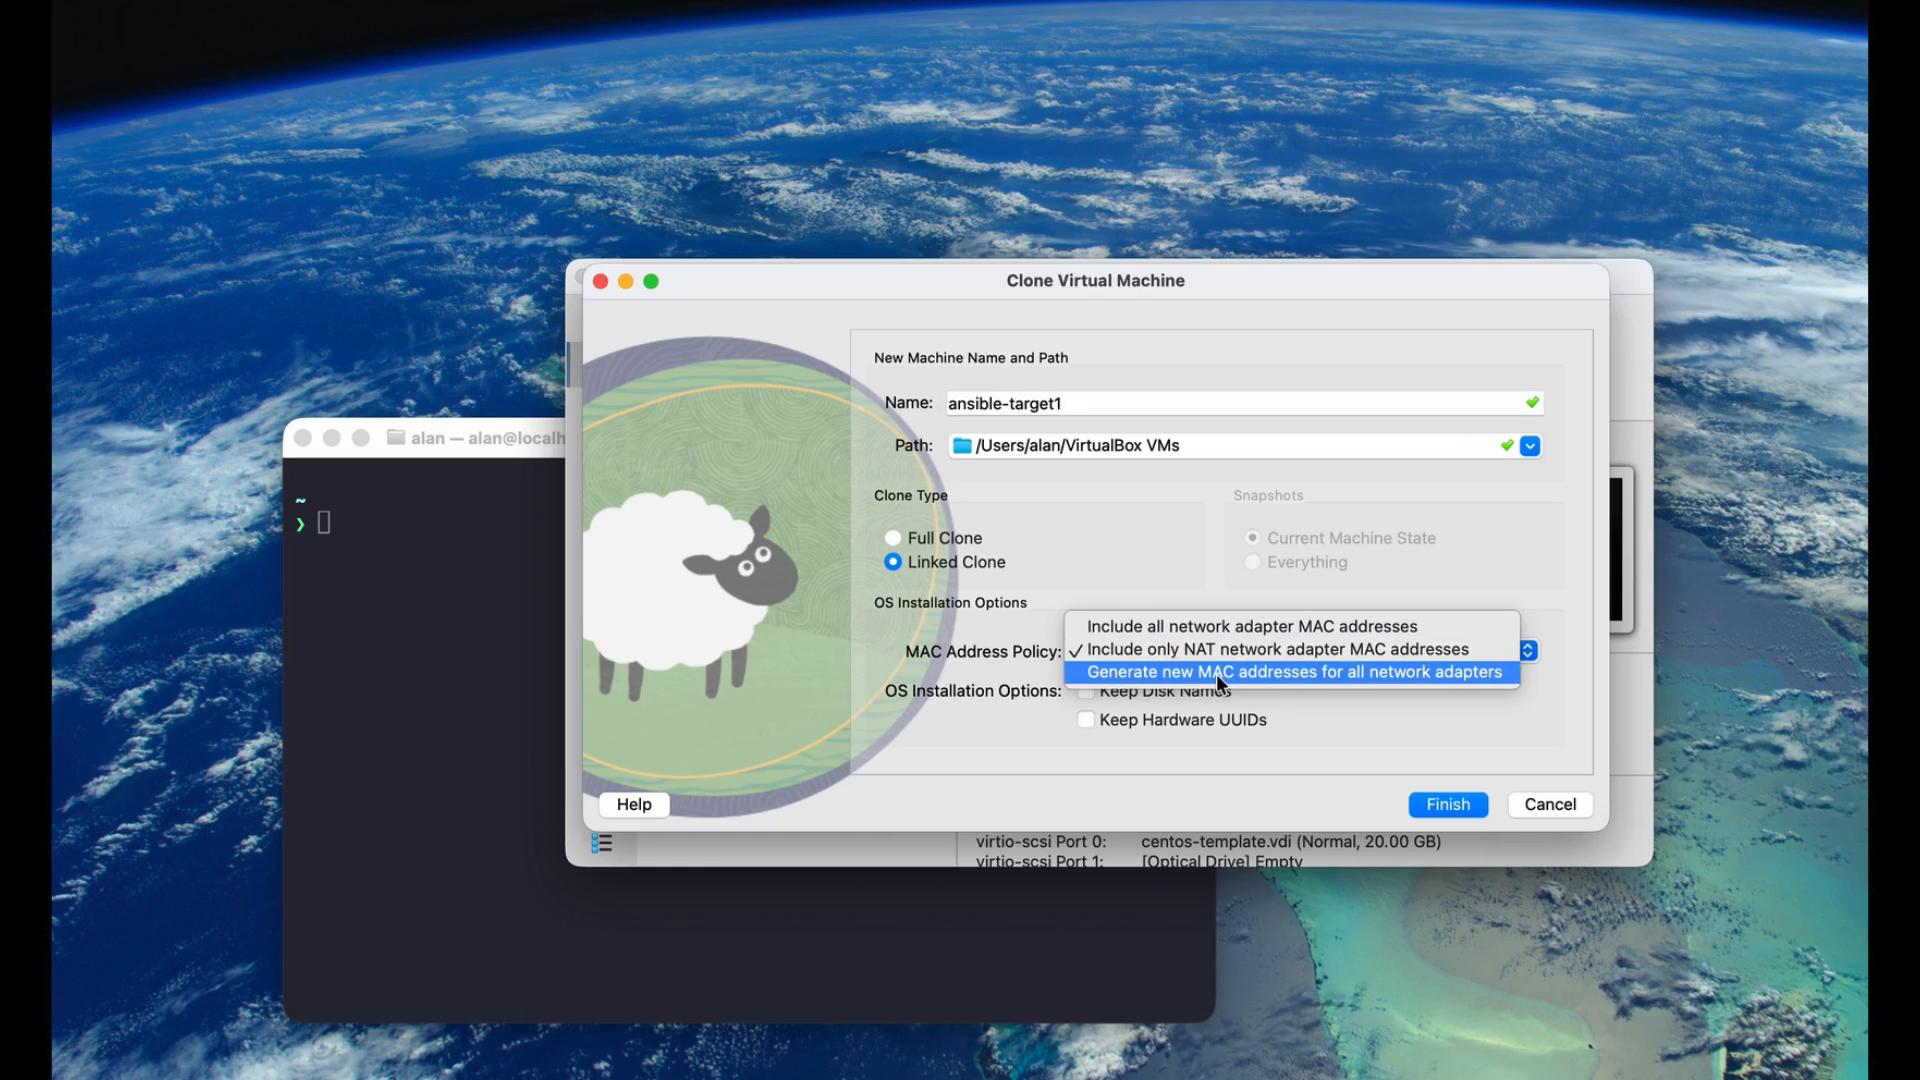
- In VirtualBox, right‑click the template VM → Clone. If the Clone option is not visible, enable Expert Mode in VirtualBox Preferences.
- Create a clone for the controller (e.g.,
AnsibleController) and a clone for the first target (ansible-target1). Use Linked Clone to save disk space and choose “Generate new MAC addresses”.
- Start the controller and target VMs
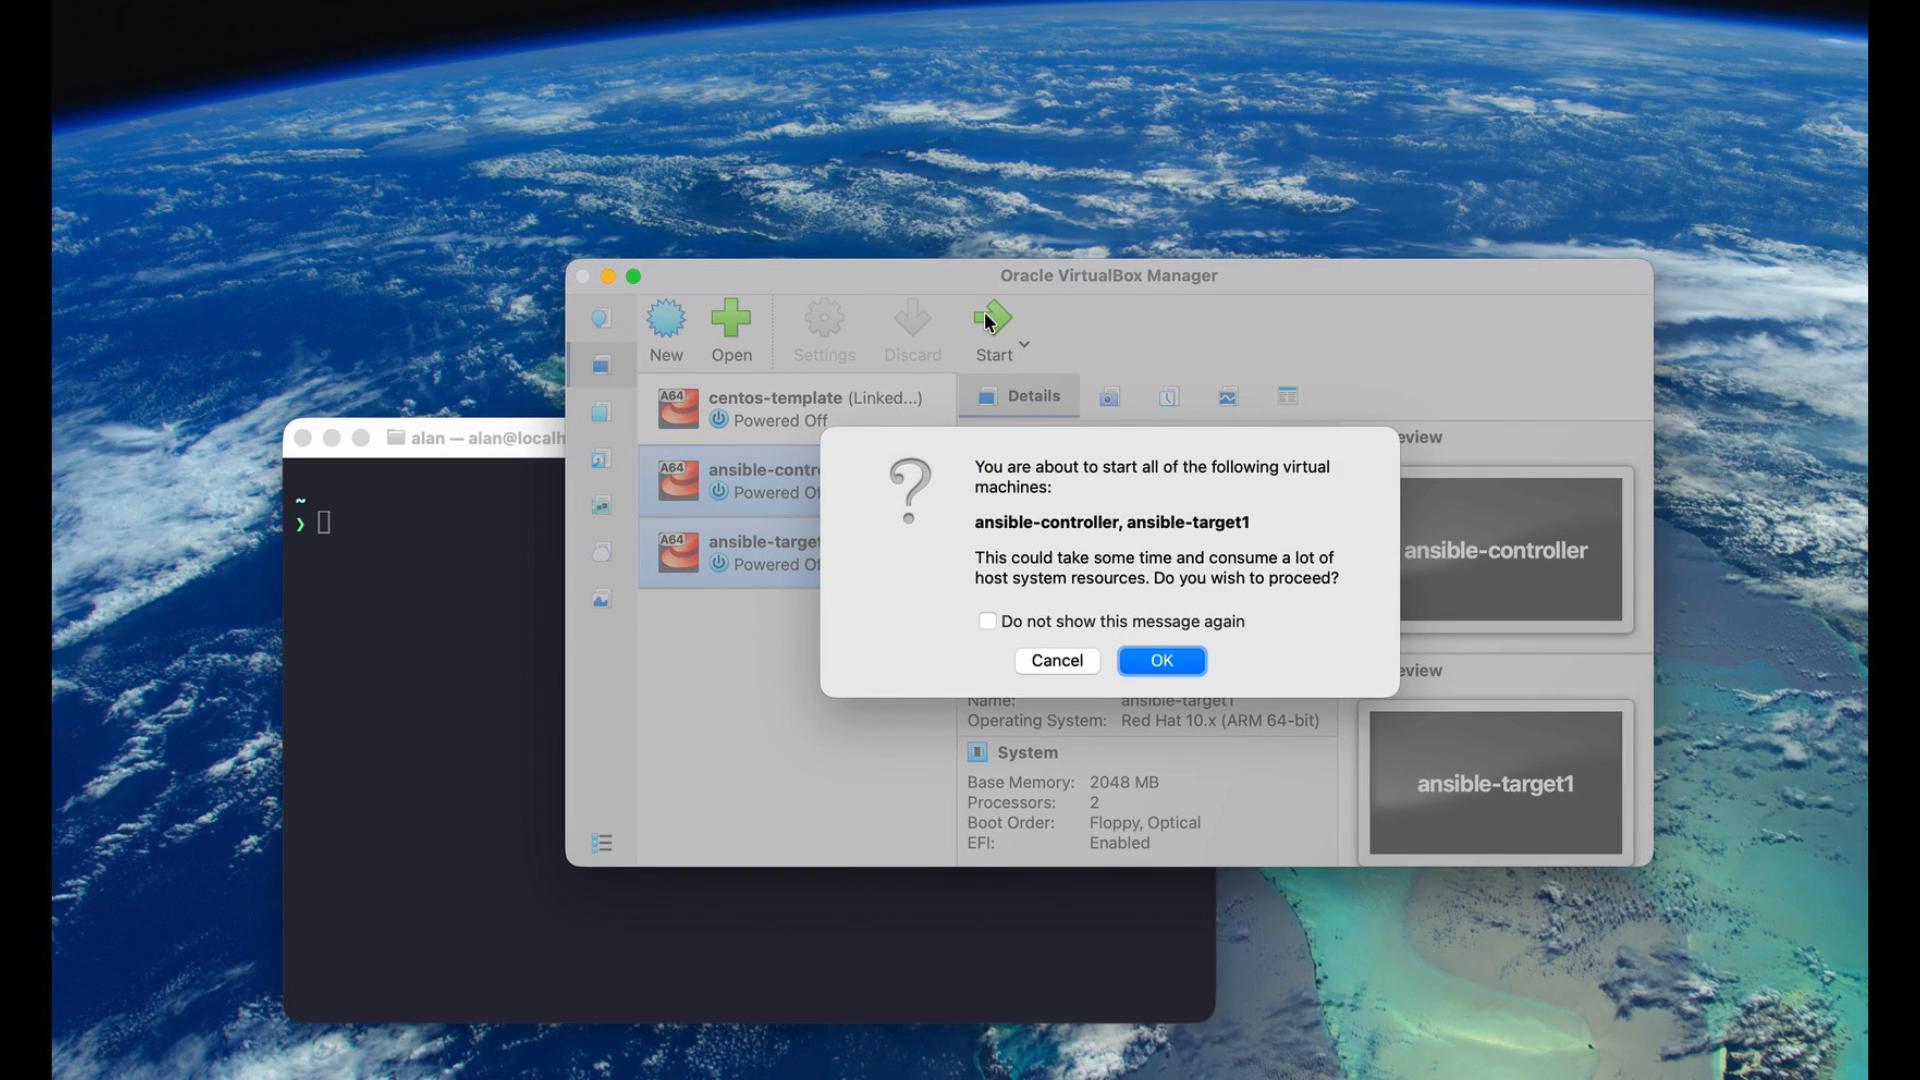
- Start the controller and target VMs from the VirtualBox UI (right-click → Start or use the toolbar).
- Find each VM’s IP address and SSH in from your host
- On each VM, open a terminal and run
ip a. Note theinetaddress for the VM’s network interface (for example,enp0s8):
- From your host machine, SSH into each VM to add SSH host keys to your
known_hostsand perform initial configuration:
- Set meaningful hostnames on each VM
- To reduce confusion, set a readable hostname on each VM. Edit
/etc/hostnameand/etc/hosts.
- Apply the change by rebooting:
- Repeat for
target1andtarget2(set/etc/hostnameaccordingly and update/etc/hosts).
- Install Ansible on the controller
- Check the Ansible installation guide for distribution-specific instructions: https://docs.ansible.com/ansible/latest/installation_guide/intro_installation.html
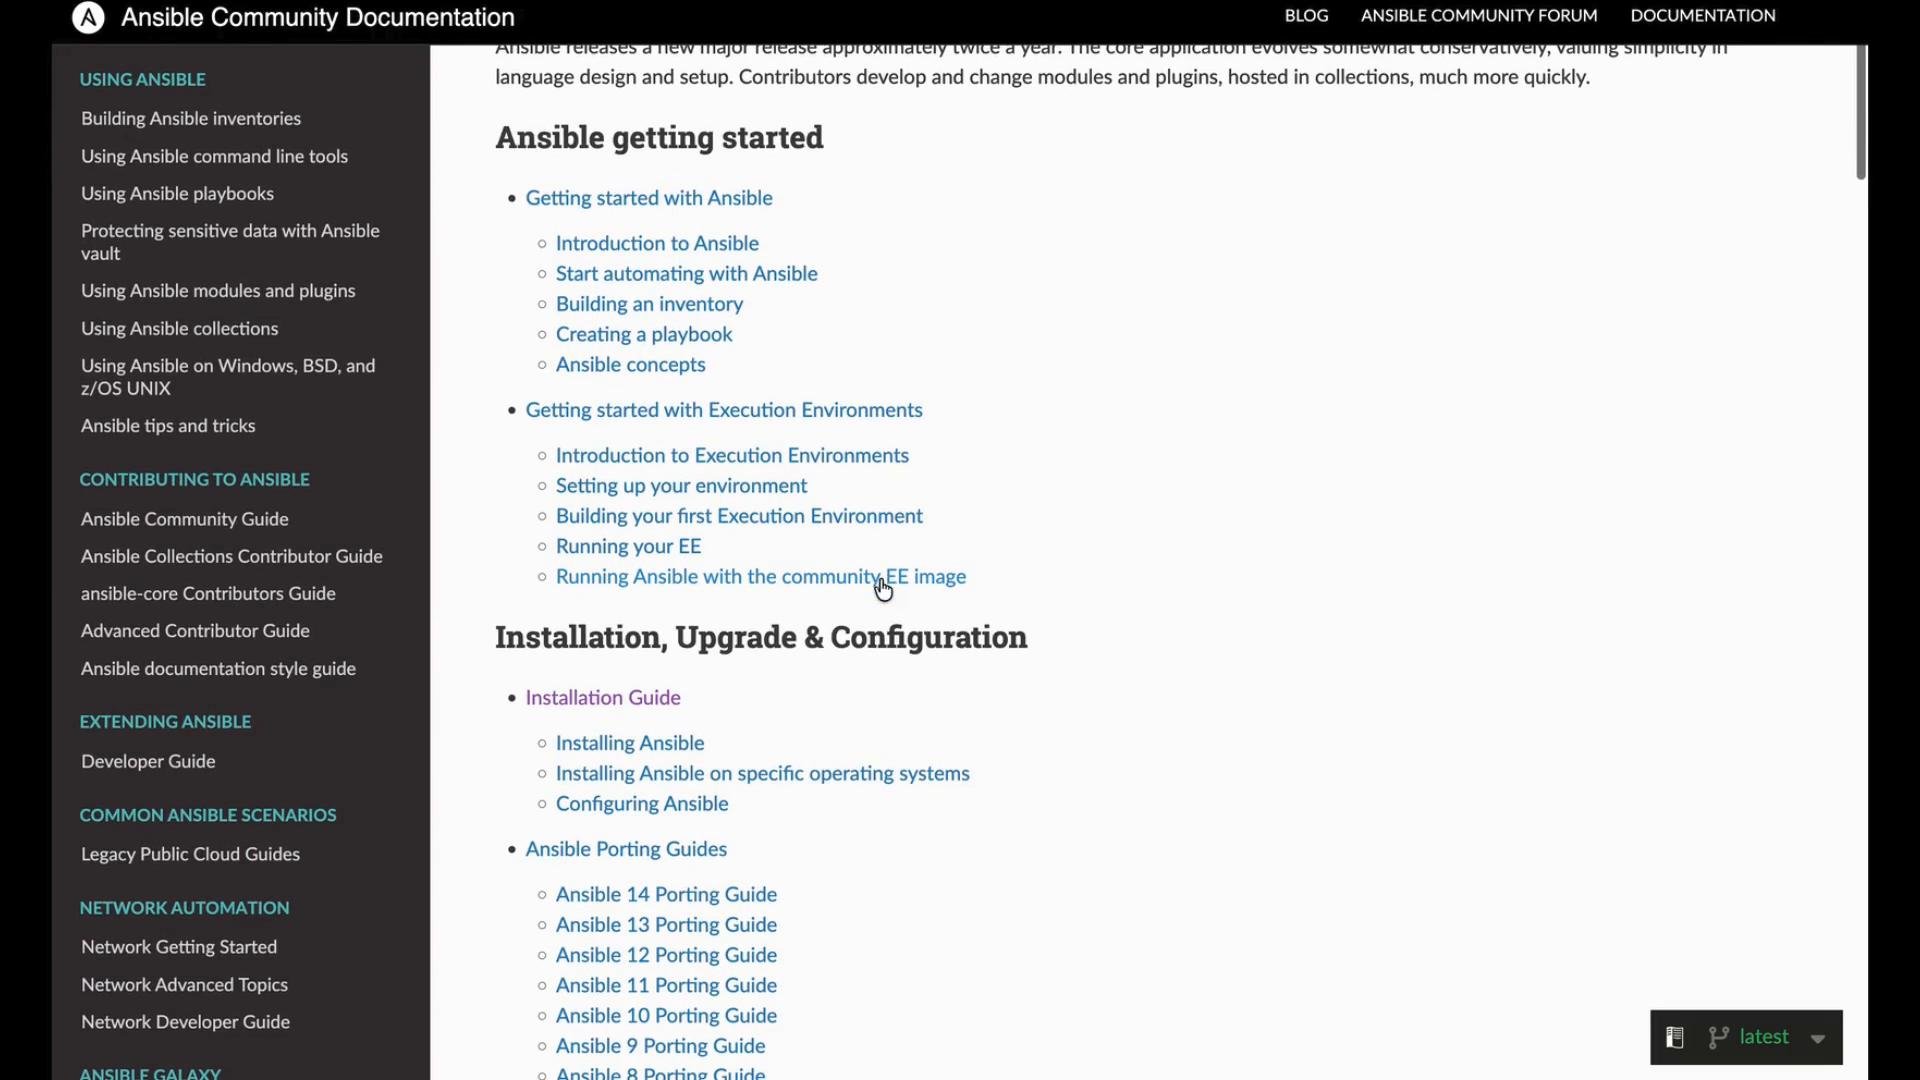
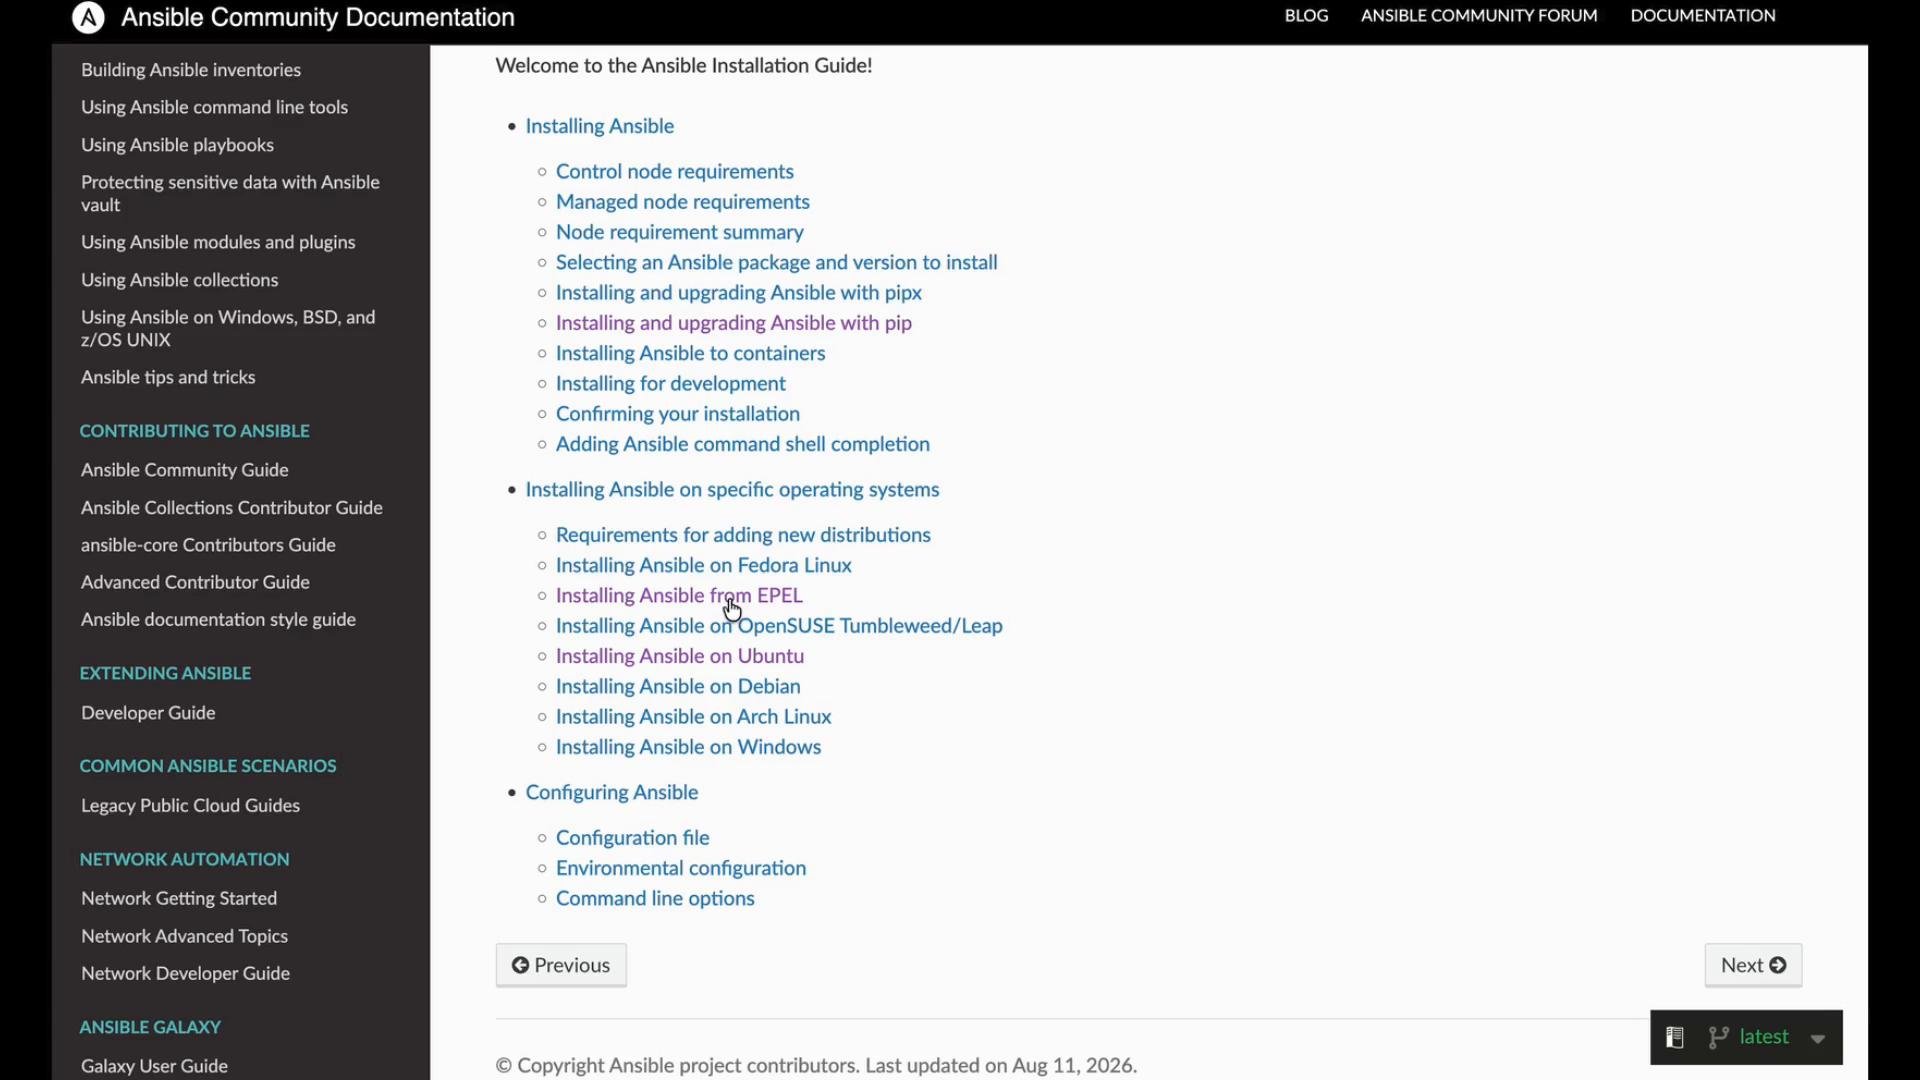
- For CentOS Stream 10 / RHEL-like systems, enable necessary repos and install
ansible-core:
- Verify installation:
- Prepare a simple inventory and verify connectivity
- Create a working directory and an inventory that defines your hosts. For demo convenience this example includes plaintext passwords — do not use this in production.
Storing plaintext passwords in an inventory is convenient for demos but insecure for production. Use SSH keys or Ansible Vault to protect credentials in real environments.
- Test connectivity with the Ansible
pingmodule:
- If Ansible reports an
sshpasserror, installsshpass(used for password-based SSH in this demo):
- Re-run the ping:
- Create the second target (target2) and add it to inventory
- Clone the template again to create
ansible-target2(Linked Clone). Start it and determine its IP (for example,192.168.0.59). From the controller, SSH once to accept the host key:
- Update
inventory.txtto includetarget2:
- Run the ping against
target2:
- Summary and quick reference
Key points
- You cloned a controller and two targets, gave them meaningful hostnames, and recorded each VM’s SSH host key in
known_hosts. - You installed
ansible-coreon the controller andsshpassfor demo password authentication. - You created a basic inventory and validated connectivity with Ansible’s
pingmodule.
- Replace password authentication with SSH key-based authentication from the controller to targets.
- Use inventory groups and host variables to scale your environment.
- Learn Ansible Playbooks to automate configuration and tasks across your targets.
- Ansible Installation Guide — https://docs.ansible.com/ansible/latest/installation_guide/intro_installation.html
- Ansible documentation — https://docs.ansible.com/
- Never store plaintext passwords in production inventory files.
- Add SSH host keys manually (or manage them centrally) before automating with password-based tools like
sshpass.