

billing_accounts keyed by the same customer ID the agent uses. And yes — you will not grant write access to the agent.
MCP toolbox: one binary, many backends
This Snowflake integration is the third platform plugged into the MCP (Model Connector Platform) server. Each platform needs slightly different MCP setup:- BigQuery: the toolbox ran locally as a binary (a subprocess).
- Databricks: the platform was already hosted; you provided a URL and token.
- Snowflake: no extra machinery is required — the toolbox already includes Snowflake support.
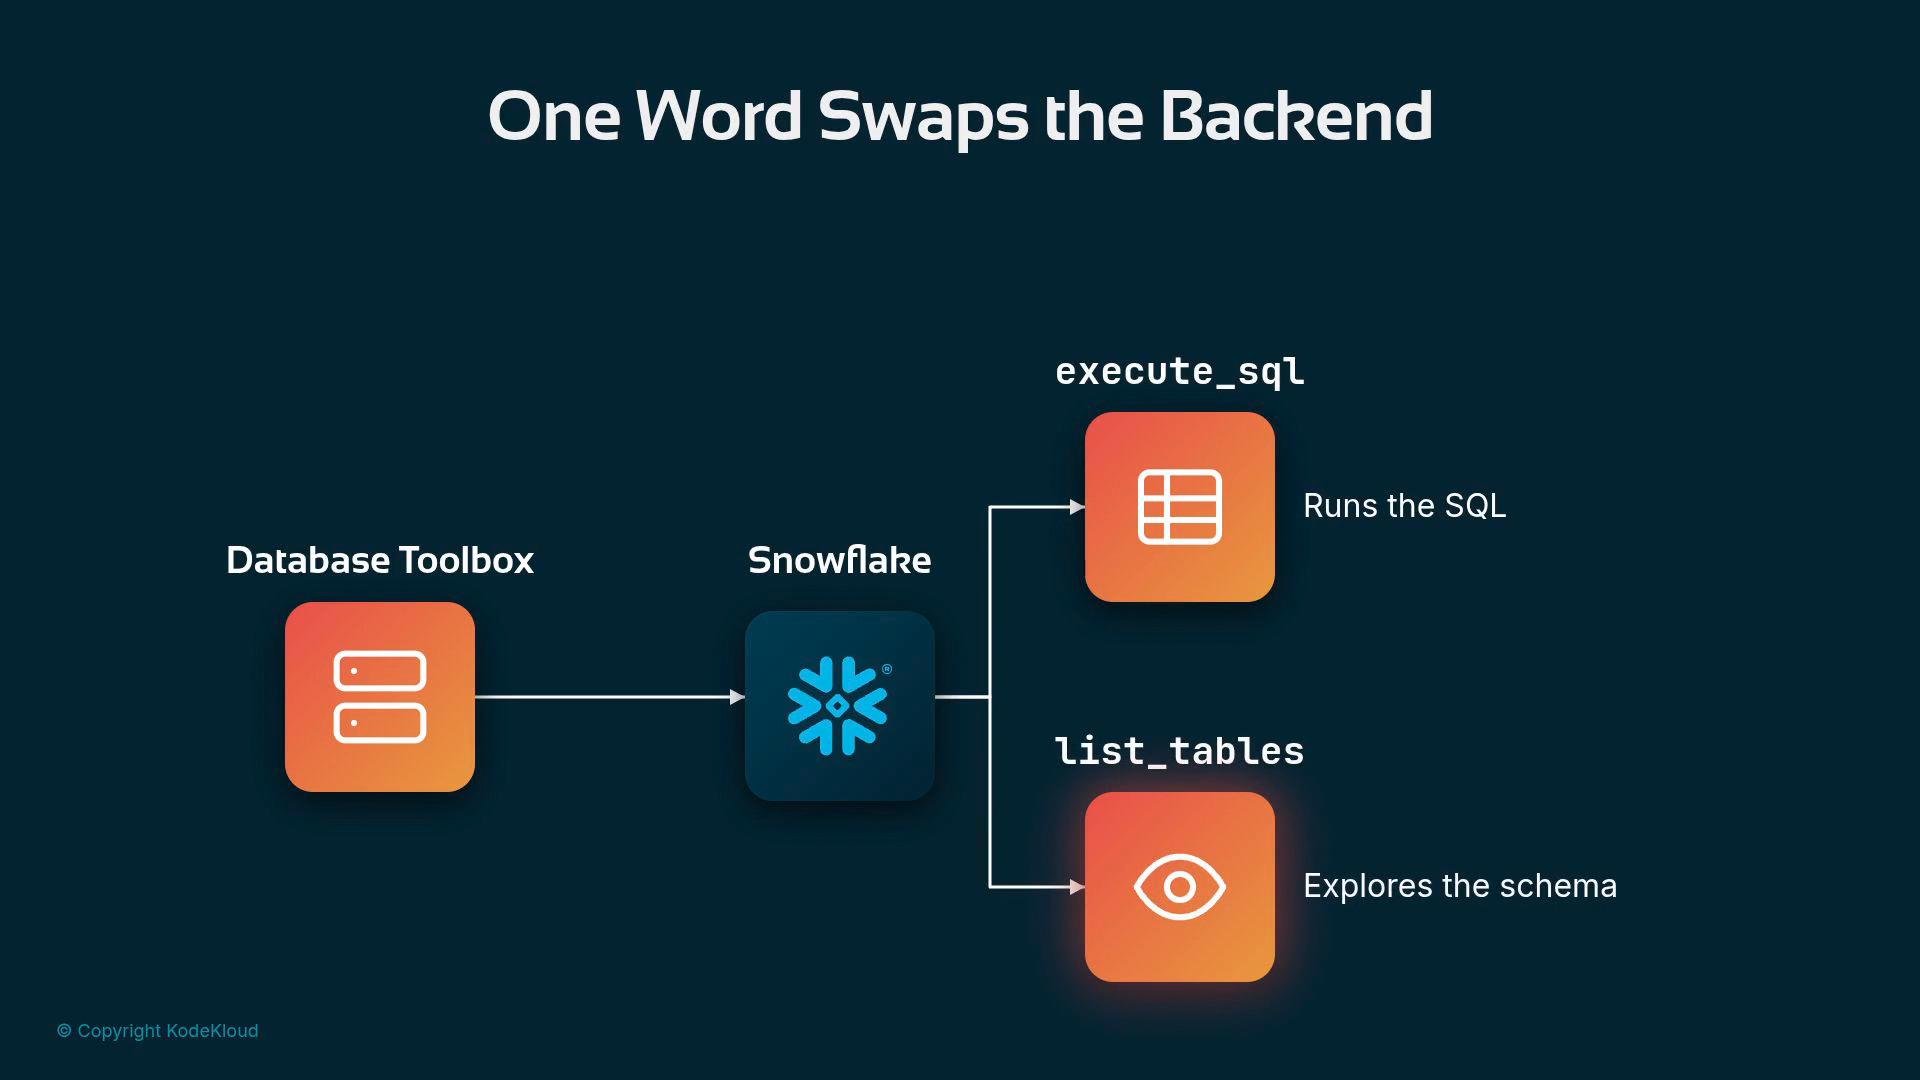
The toolbox swaps backend behavior by a single
--prebuilt <platform> flag. One binary can host connectors for many databases — just change the platform name.- execute_sql — runs SQL generated by the model.
- list_tables — inspects available tables so the agent can explore the schema.
How the toolbox authenticates to Snowflake
The Snowflake prebuilt connector reads its connection configuration from environment variables. The connector expects these variables (useexport or a .env file):
A typical
.env file for local testing:
Enforcing least privilege with a read-only role
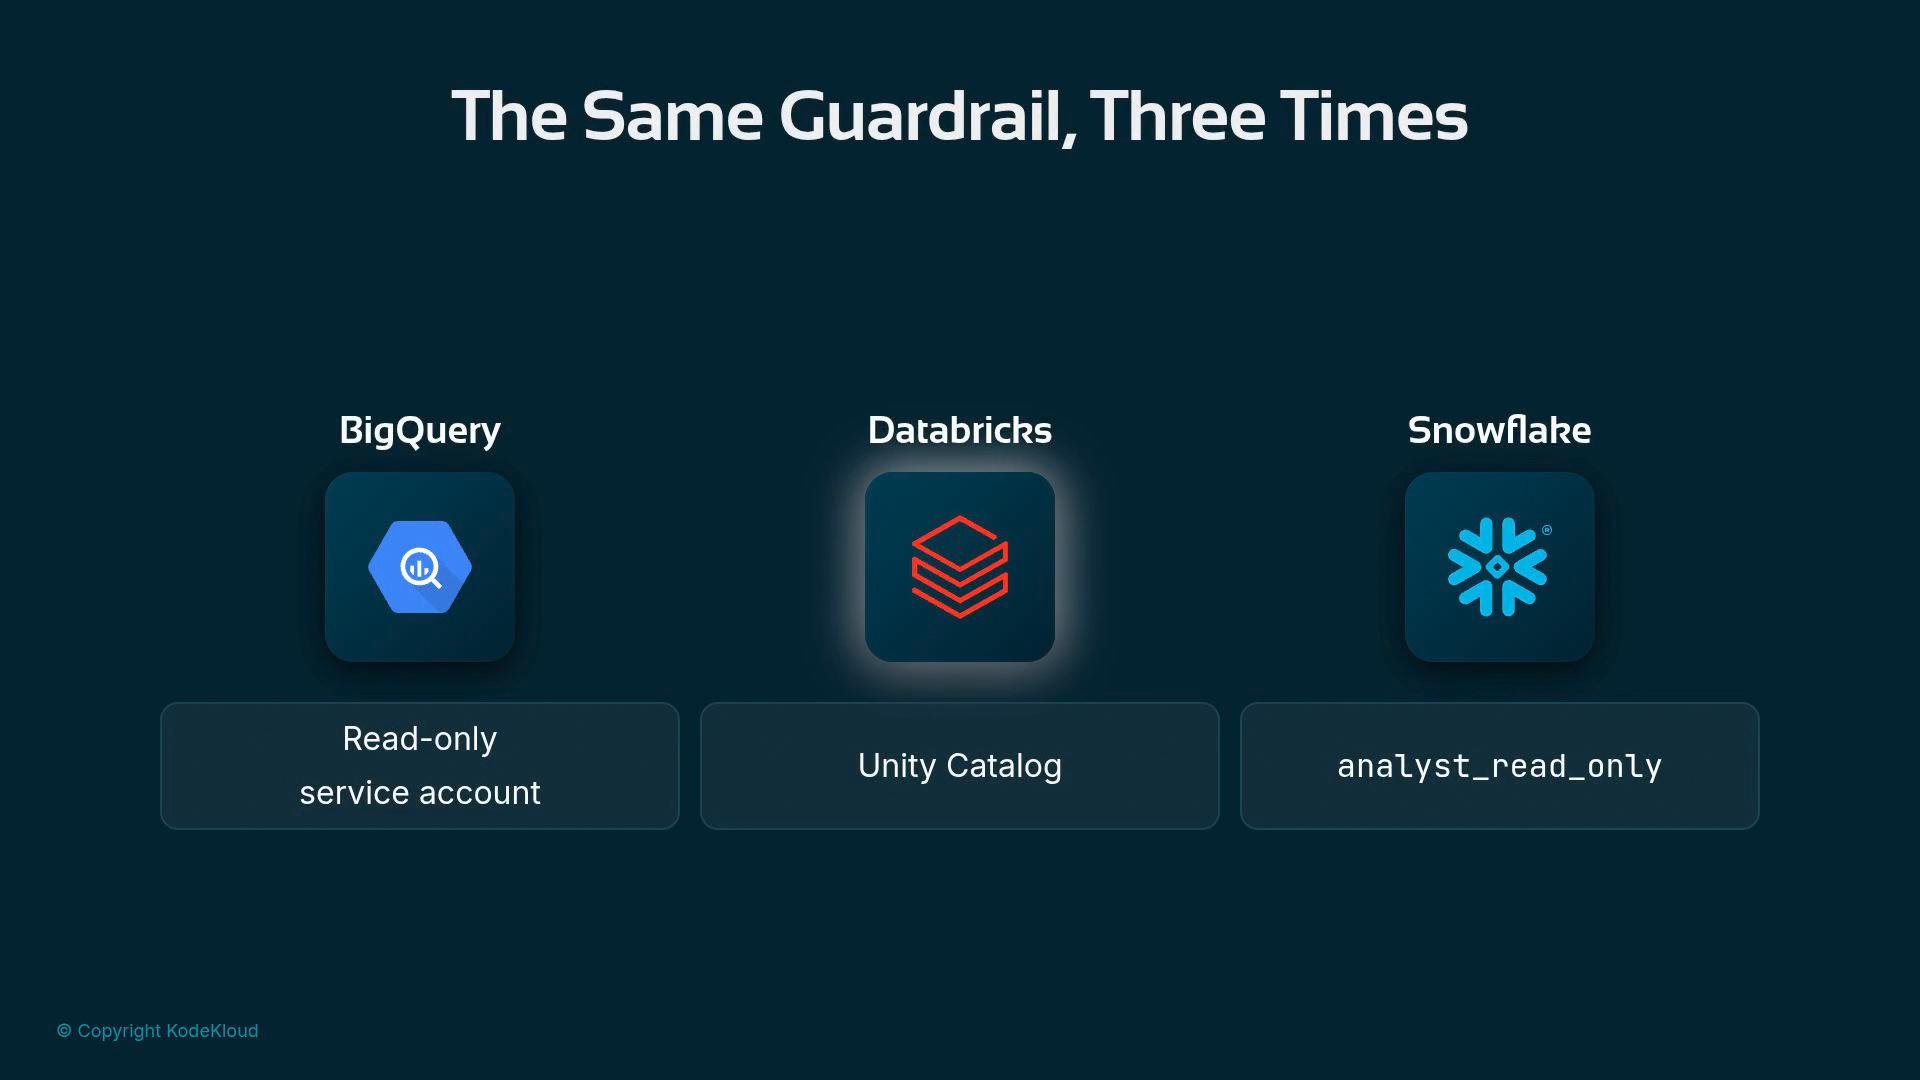
Follow the principle of least privilege: create a role that allows only the operations the agent needs (usuallyUSAGE and SELECT). Dana creates ANALYST_READ_ONLY and grants only the minimum privileges required to read billing tables.
SQL to create the role and grant minimal permissions:
Never grant broad write permissions to the agent’s role. Use a read-only role and grant only the specific tables and usage privileges required.
ANALYST_READ_ONLY in Snowflake.
Quick comparison: guardrail implementations
Links and references
- Snowflake: https://docs.snowflake.com/
- Databricks Unity Catalog: https://docs.databricks.com/data-governance/unity-catalog/index.html
- BigQuery IAM: https://cloud.google.com/bigquery/docs/access-control
- Tooling / MCP: (link to your internal MCP docs or repo)
--prebuilt flag to safely give your agent read-only access to billing data so it can answer money questions without risking writes or privilege escalation.