

Starting point: granting access
The demo begins in an empty project folder for a simple React app. Claude Code asks permission to read and execute files in the working directory before proceeding:The single, focused prompt
A concise, well-scoped prompt helps constrain assumptions and produce more reliable output. In this demo the prompt is:The plan (to-do list)
Claude Code creates and tracks a to-do list covering analysis, backend and frontend setup, authentication flows, security, and testing:What Claude Code can do (high-level)
Claude Code is capable of:- Initializing both backend and frontend directories and package metadata.
- Running CLI commands (e.g.,
npm install,npx create-react-app) when allowed. - Creating server scaffolding, routes, models, email utilities, and frontend components.
- Installing and wiring security libraries (helmet, rate limiting, bcryptjs, jsonwebtoken, express-validator, nodemailer).
- Generating a React TypeScript frontend with authentication context and protected routes.
- Providing a concise summary and startup instructions.
Project initialization and scaffolding
Claude Code sets upbackend and frontend directories, initializes package files, installs dependencies, and scaffolds the frontend using the TypeScript template. Example commands executed in the project root:
create-react-app may print deprecation messages and suggestions for alternative starters; adjust your toolchain if desired.
Example generated environment configuration
A typicalbackend/.env.example generated by Claude Code:
Backend: models, utils, and routes
Claude Code generates a standard Express backend with:- MongoDB connection via
mongoose. Usermodel including email index, password hashing (bcryptjs), verification and reset tokens.- Auth routes: register, login (JWT generation), email verification, password reset endpoints.
- Utilities: nodemailer-based email sender with templates for verification and reset.
- Middleware: authentication checks, rate limiting, and input validation via
express-validator. - Security: helmet, rate limiting, and CORS configuration.
routes/auth.js.
Frontend: React + TypeScript
The generated frontend includes:- An
AuthContext(React context) for global authentication state. - Components:
Login,Register,ForgotPassword,ResetPassword,EmailVerification, and a protectedDashboard. - A
ProtectedRoutewrapper to guard private routes. - Services to call backend APIs and manage JWT tokens (storage, expiry handling, automatic refresh where applicable).
- Basic styling and a header/navigation component.
package.json scripts section for the backend:
Summary output
When the process finishes, Claude Code summarizes the generated stack:-
Backend (Express + MongoDB)
- User model with secure hashing, email verification, account lockout options
- JWT authentication with token generation and validation
- Email service for verification and password reset
- Security: rate limiting, Helmet headers, input validation
-
Frontend (React + TypeScript)
- Authentication context and protected routes
- UI components for registration, login, and recovery flows
- Dashboard with profile and account actions
- Strong password hashing and optional complexity checks
- Account lockout after repeated failed attempts
- JWT expiration and refresh strategies
- Email verification before enabling accounts
- Rate limiting for sensitive endpoints
- Secure headers via Helmet and input validation/sanitization
- Start MongoDB (locally or use a managed service such as MongoDB Atlas).
- Configure email (Gmail app password is commonly used — see Google’s App Passwords).
- Run backend:
cd backend && npm run dev. - Run frontend:
cd frontend && npm start. - Open the app at
http://localhost:3000.
Generated projects accelerate prototyping, but always audit and harden any generated code before using it in production.
Running the services locally (examples)
Run backend and frontend in separate terminals. Backend:Generated project map (representative)
(Adjust paths to match the exact output if you inspect the generated repository.)
Visual: registration form with network error
Here is a captured screenshot of the frontend registration form showing a “Network error” (this happened because an email service was not configured):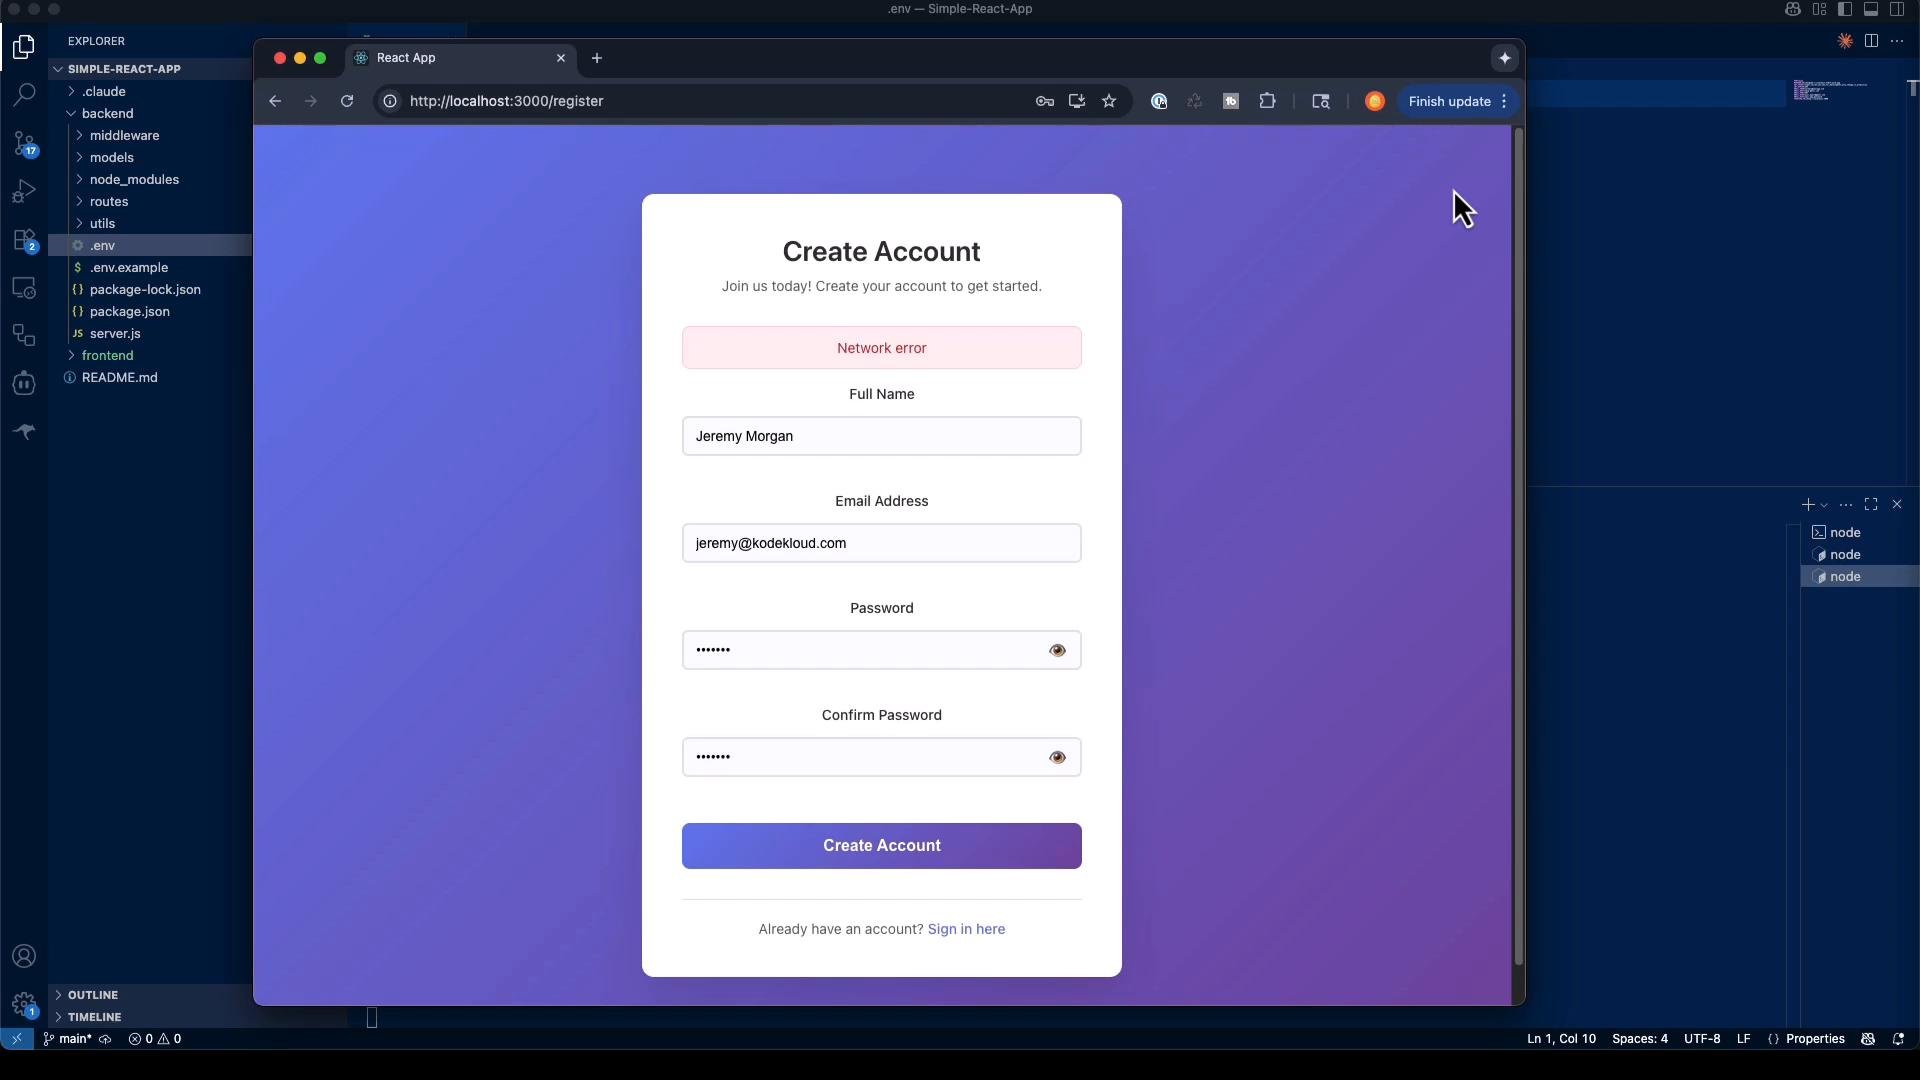
.env (for example: EMAIL_USER, EMAIL_PASS, EMAIL_HOST, EMAIL_PORT).
Caveats and practical notes
- Generated defaults (TypeScript, dashboard, error handling) are reasonable starting points but may not match your product constraints — review and customize.
- Do not treat generated code as production-ready. Always perform security reviews, dependency audits, and add tests.
- CLI tools and templates evolve (e.g.,
create-react-appdeprecations). Update commands and dependencies to match the latest ecosystem. - Generation can take time because many files are written; this is expected for full-stack scaffolds.
Security warning: never deploy scaffolded code to production without reviewing secrets, hardening authentication flows, rotating keys, and adding proper rate limits, logging, monitoring, and tests.
What autonomous task completion teaches us
Key takeaways about autonomous code generation:- Independent problem solving: Claude Code can make and explain architectural decisions, ask clarifying questions, and autonomously execute steps when permitted.
- Multi-component orchestration: It can create backend, frontend, utilities, and wire them together.
- Rapid prototyping: You can obtain a working prototype (authentication flows, verification, password reset, protected routes) far faster than hand-coding boilerplate.
Next steps and further reading
- Learn about prompt patterns and how to control assumptions to get more reliable generation results.
- Explore stepwise refinement techniques to guide Claude Code through complex tasks incrementally.
- References: