Date: 2025-08-21
Auditor: Claude Code Security Analysis
Version: 1.0.0
This executive summary prioritizes remediation and recommends tools and processes. It is not a replacement for line-by-line code audits, automated/static scans, or penetration testing. Use this to guide immediate actions and to create detailed remediation tickets for engineering teams.
Executive Summary
The Express Login Demo application contains multiple security issues across configuration, authentication, session, logging, and transport layers. The audit found 12 issues with a combined Overall Security Posture of: CRITICAL (9.2/10 Risk Score). Key metrics at a glance:
Immediate actions required:
- Replace weak or hard-coded JWT secret with a cryptographically strong secret and store it in a secrets manager.
- Implement rate limiting for authentication endpoints.
- Sanitize logs and reduce error-response detail to avoid leaking sensitive data.
- Enforce HTTPS and add appropriate security headers (Helmet).
npm audit for dependency checks:
Critical items below require immediate attention. Create high-priority tickets and coordinate credential rotations, deployment windows, and stakeholder communication before applying fixes that rotate secrets or revoke tokens.
Critical Vulnerabilities (Fix Immediately)
1. Weak or Hard-coded JWT Secret Key
- Severity: Critical
- CVE: N/A (configuration issue)
- CWE: CWE-798 (Use of Hard-coded Credentials)
- Location:
.env(example:.env:2)
- Generate a cryptographically secure secret (256-bit / 32 bytes recommended).
- Do not commit secrets to source control. Use environment variables or a secrets manager (AWS Secrets Manager, Azure Key Vault, HashiCorp Vault).
- Rotate any exposed secrets immediately and update dependent deployments.
.env (never commit):
2. Database Credentials or Secrets Exposed
- Severity: Critical
- CWE: CWE-200 (Information Exposure)
- Location:
.envor other committed configuration files
- Rotate exposed credentials immediately.
- Move secrets to a dedicated secrets manager and restrict access via IAM roles or RBAC.
- Add
.env, secrets, and config files to.gitignore. Consider scanning history for leaked credentials.
3. Sensitive Error Information Disclosure
- Severity: Critical
- CWE: CWE-209 (Information Exposure Through Error Messages)
- Location:
routes/auth.jsand global error handlers
- Return generic client-facing error messages (e.g., “Invalid credentials” or “Internal server error”).
- Log detailed errors securely on the server side with structured logging and appropriate retention controls.
- Sanitize logs to ensure no secrets or PII are stored in plaintext.
High Priority Issues (Fix within 1 week)
4. Missing Rate Limiting on Auth Endpoints
- Location:
routes/auth.js:9(login route) - Risk: Allows unlimited authentication attempts → credential stuffing / brute force.
- Add rate limiting middleware (e.g.,
express-rate-limit) and consider account lockouts or progressive delays after repeated failures.
5. Insufficient Security Event Logging
- Severity: High
- CWE: CWE-778 (Insufficient Logging)
- Location:
routes/auth.js:32-46
- Log authentication events (success/failure, source IP, user-agent) using structured logging (JSON).
- Avoid logging sensitive fields (passwords, tokens). Route logs to centralized aggregators (ELK, Splunk, Cloud Logging).
6. Missing HTTPS Enforcement and Security Headers
- Severity: High
- CWE: CWE-319 (Cleartext Transmission of Sensitive Information)
- Location:
server.js
- Enforce TLS with valid certificates and redirect HTTP to HTTPS.
- Use Helmet to set security headers: HSTS, X-Frame-Options, X-Content-Type-Options, and define CSP where applicable.
7. No Input Sanitization for Logging (Log Injection)
- Severity: High
- CWE: CWE-117 (Improper Output Neutralization for Logs)
- Normalize and sanitize untrusted input before logging. Prefer structured logs rather than free-form text.
- Validate and escape user-supplied data that will be stored in logs or displayed in dashboards.
Medium Priority Issues (Fix within 1 month)
8. Missing Security Headers (CSP, HSTS, X-Frame-Options)
- Severity: Medium
- CWE: CWE-693 (Protection Mechanism Failure)
- Location:
server.js
- Configure Helmet and define a Content Security Policy to mitigate XSS and resource injection.
9. No Session Invalidation or Token Blacklisting
- Severity: Medium
- CWE: CWE-613 (Insufficient Session Expiration)
- Location:
routes/auth.js
- Implement short-lived access tokens and refresh tokens.
- Store refresh tokens securely (HttpOnly cookies) and maintain a server-side blacklist or token store (e.g., Redis) to revoke tokens on logout or compromise.
- Issue short-lived access token (15 min)
- Issue refresh token stored in a secure HttpOnly cookie
- On logout, mark refresh token as revoked in the server-side store
10. Inadequate Error Handling Exposing Implementation Details
- Severity: Medium
- CWE: CWE-209
- Location:
routes/auth.js:72-94
- Standardize error handling middleware and ensure stack traces are not returned to clients. Log internal details only to secure logs.
11. Missing Input Length Validation
- Severity: Medium
- CWE: CWE-770
- Location:
routes/auth.js:10-16
- Enforce reasonable maximum lengths for email, username, and other inputs. Use
express-validatoror similar libraries.
Low Priority Issues (Fix in next release)
12. No Monitoring and Health-check Endpoints
- Severity: Low
- CWE: CWE-778 (Insufficient Logging / Observability)
- Location: Application-wide
- Add health endpoints and metrics (Prometheus compatible), instrument performance metrics and errors, and integrate alerts to improve detection and response time.
Security Recommendations and Implementation Roadmap
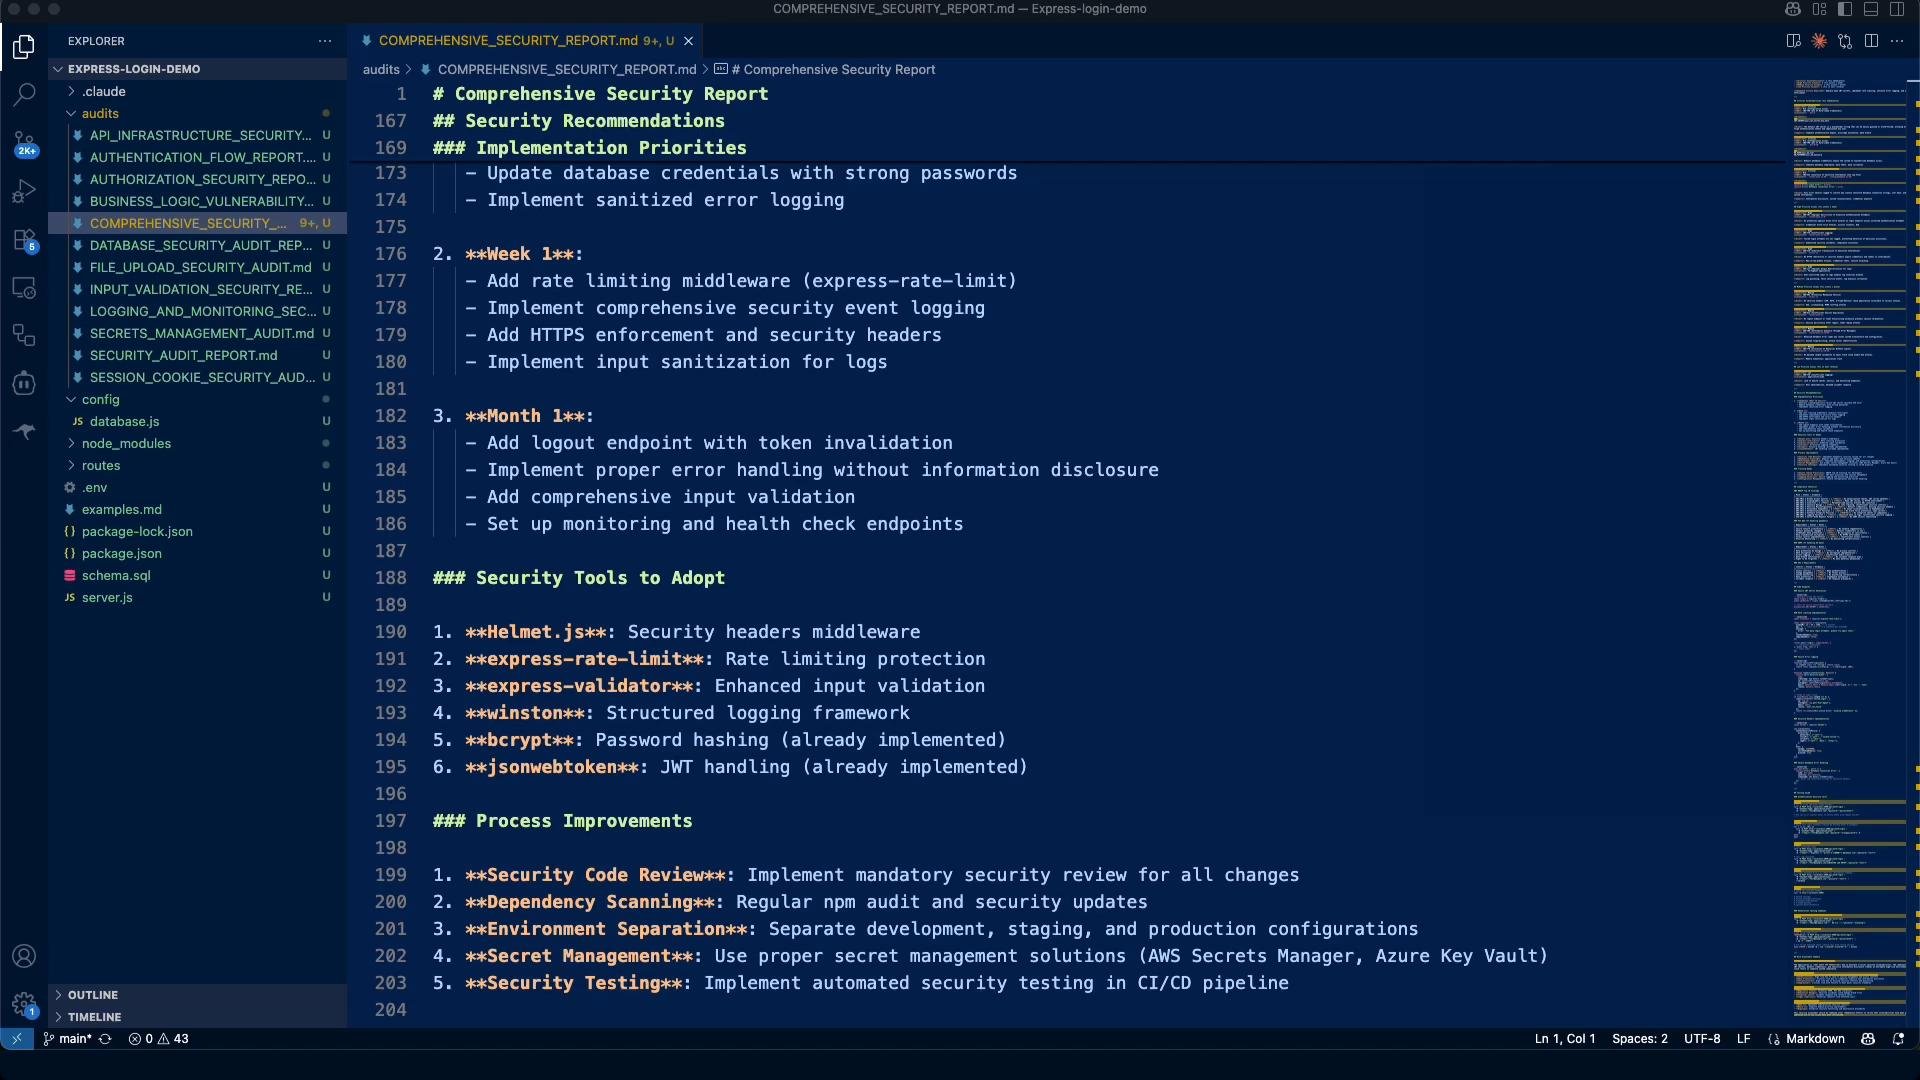
Prioritized implementation plan:
Recommended tools:
- Helmet.js — security headers (helmetjs.github.io)
- express-rate-limit — rate limiting (npmjs.com/package/express-rate-limit)
- express-validator — input validation (express-validator.github.io/docs/)
- winston / pino — structured logging
- bcrypt — secure password hashing
- jsonwebtoken — JWT handling
- Secrets manager — AWS Secrets Manager, Azure Key Vault, or HashiCorp Vault
- SAST/DAST/Dependency scanning — integrate into CI pipelines
- Require security-focused code reviews for auth and cryptography changes.
- Automate dependency and vulnerability scanning in CI.
- Separate environment configurations (dev/staging/prod) and enforce least privilege.
- Prohibit storing secrets in repositories and provide secure secrets onboarding.
- Provide secure-coding training focused on OWASP Top 10 for developers.
Compliance Checklist
- OWASP Top 10: Authentication and injection protections addressed via rate limiting, input validation, CSP recommendations.
- PCI DSS: If handling payments, ensure encryption in transit, strict logging, and segmentation.
- GDPR: Minimize PII, apply retention policies, and secure storage/access controls.
- SOC 2: Ensure proper logging, monitoring, and access controls for SOC 2 readiness.
Secure Code Examples (Selected)
- Generate secure JWT secret (Node.js):
- Express: Helmet + HTTPS redirect + rate limiting:
- Safe error handling:
- Logout / token revocation concept:
Testing Guide (Verification commands & checks)
- Rate limiting: use a script or
curlto exceed allowed requests to/loginand verify a429response. - HTTPS redirect:
curl -I http://your-hostshould return a301/302redirect tohttps://. - Security headers:
curl -I https://your-hostshould showStrict-Transport-Security,X-Frame-Options,X-Content-Type-Options, etc. - Logging: attempt failed and successful logins and confirm events exist in centralized logs without sensitive data.
- Dependency scan: run
npm auditand triage high/critical results in CI.
Notes on Scope and Next Steps
This report is an executive-level summary intended to prioritize remediation work. It is not a replacement for detailed, line-by-line secure-code fixes, automated scans, or pentesting. For each identified issue produce an actionable ticket that includes:- Code references and proposed changes
- Test cases to verify remediation
- Rollback plan and deployment windows if secrets or tokens must be rotated