Modern platform networking challenges
Platform networking is more complex today because workloads span clusters, environments, and traffic patterns (mostly east–west with north–south ingress). Observability at the network layer is critical for debugging, capacity planning, and security posture.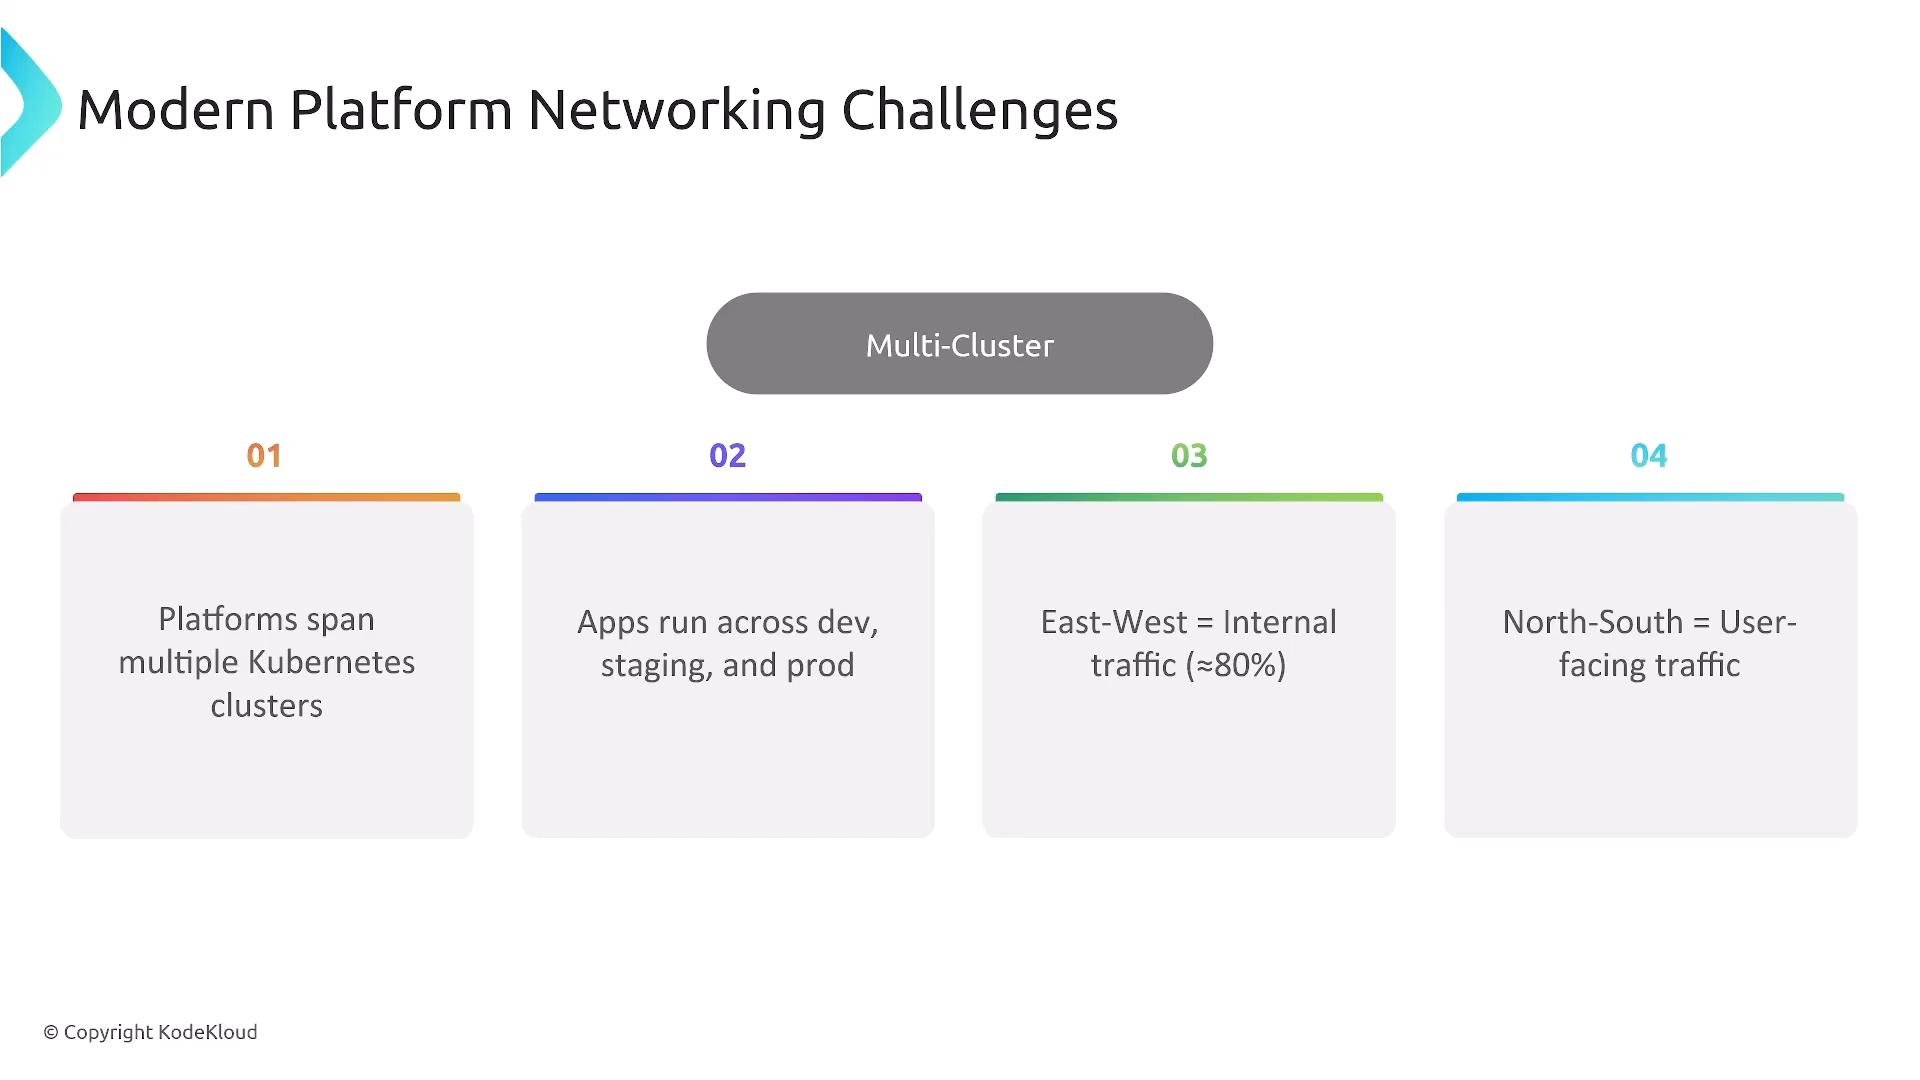
Traffic observability and optimization
To optimize traffic (east–west and north–south) you must capture network-level logs, metrics, and traces across your routing topology. Extend existing monitoring tools to include network telemetry and distributed tracing to reason about routing complexity and performance bottlenecks.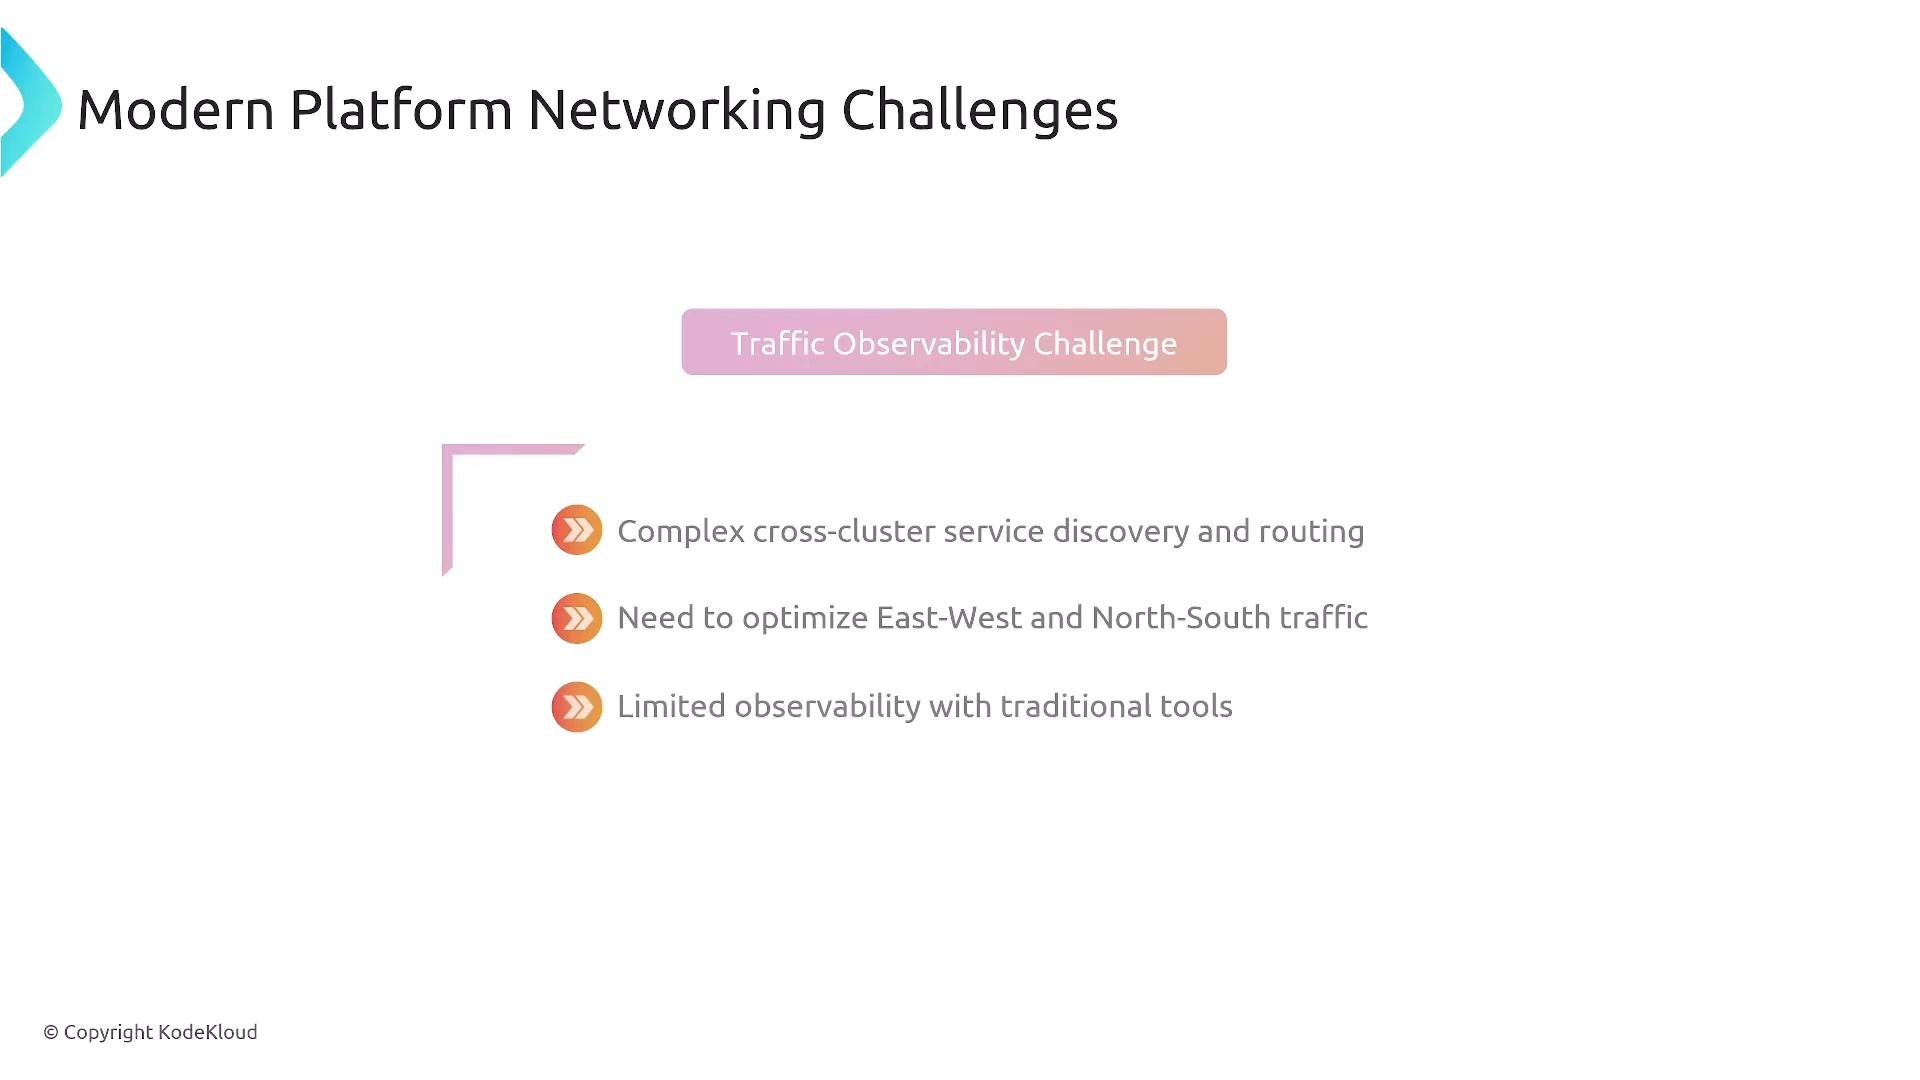
Platform personas and requirements
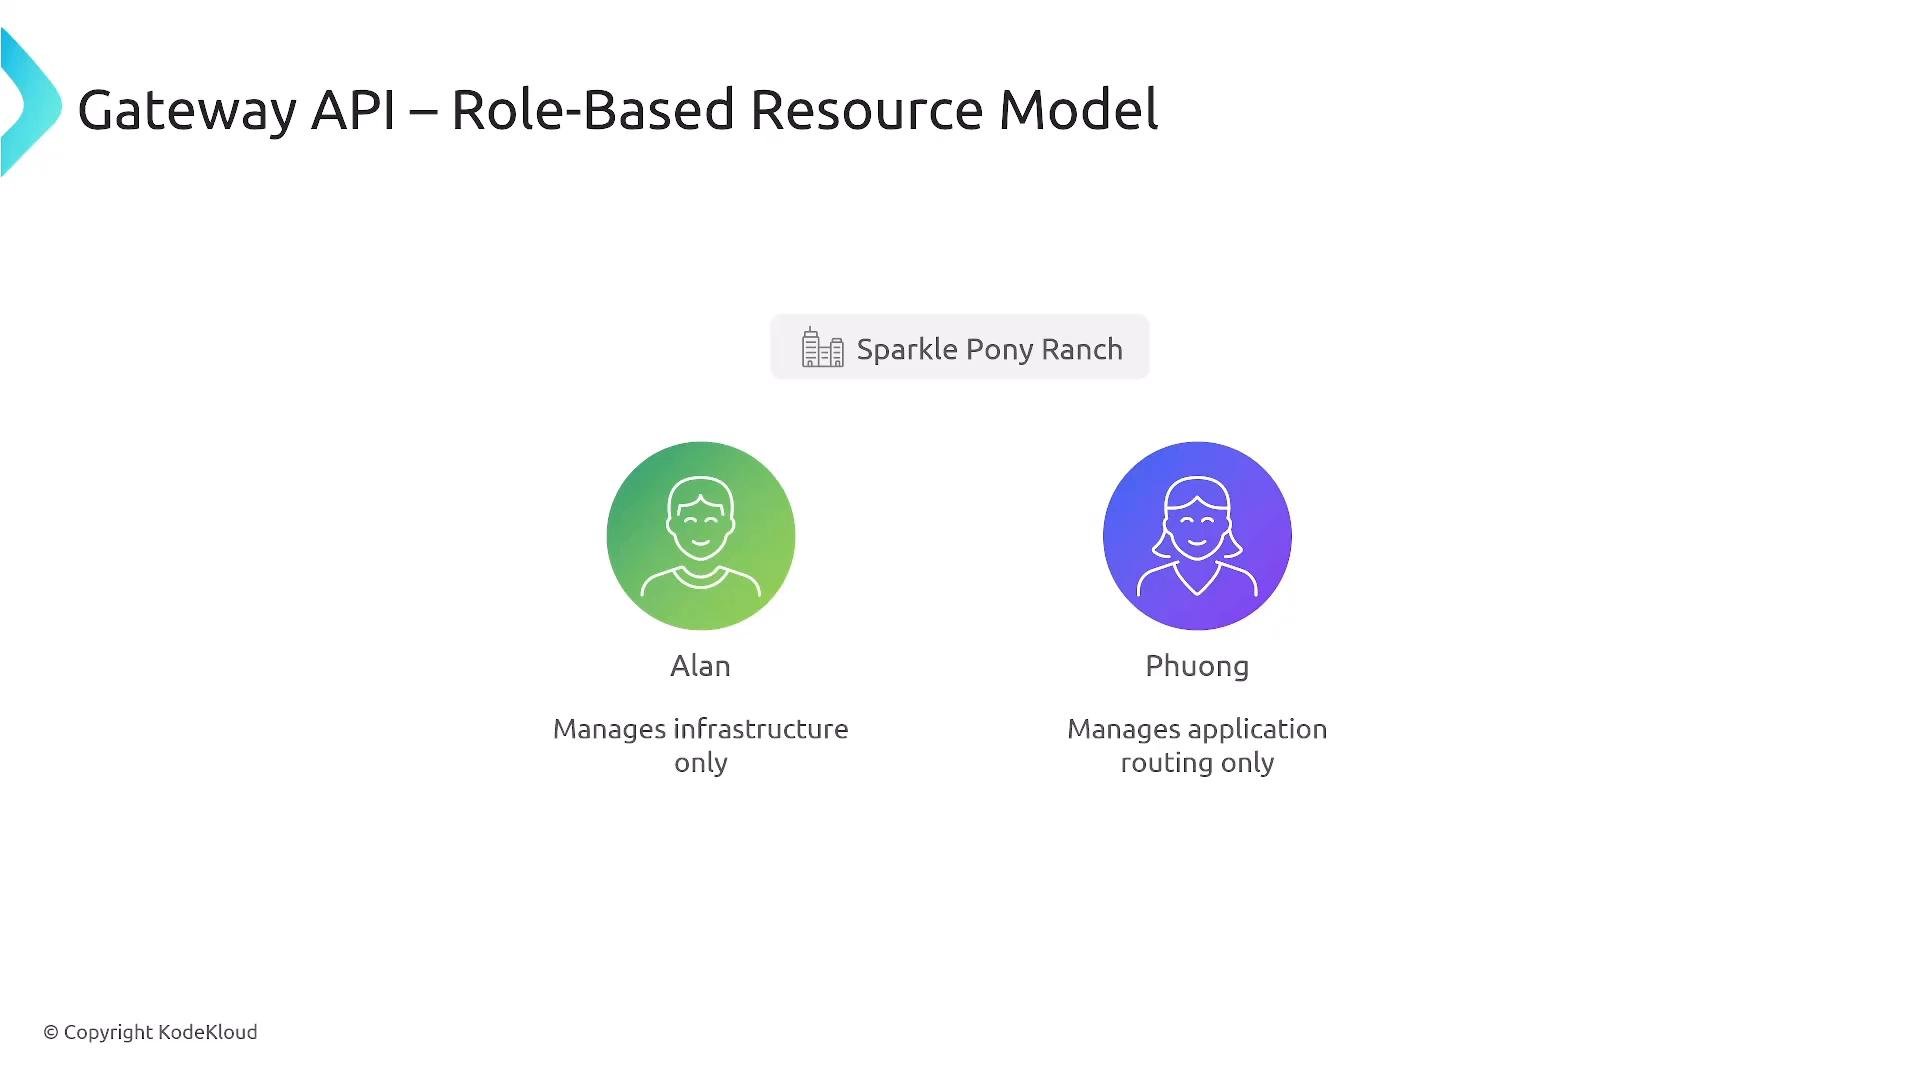
In our example organization (Sparkle Pony Ranch) different personas require different platform responsibilities:- Swati — focuses on SLAs, observability, and operational readiness.
- Alan — focuses on infrastructure efficiency and compliance.
- Phuong — wants self-service networking with sensible defaults and built-in security.
Kubernetes service types and exposure options
Understand the trade-offs of each Kubernetes service type when exposing workloads:
Useful references:
- Kubernetes Services: https://kubernetes.io/docs/concepts/services-networking/service/
- Ingress: https://kubernetes.io/docs/concepts/services-networking/ingress/
Service discovery in Kubernetes
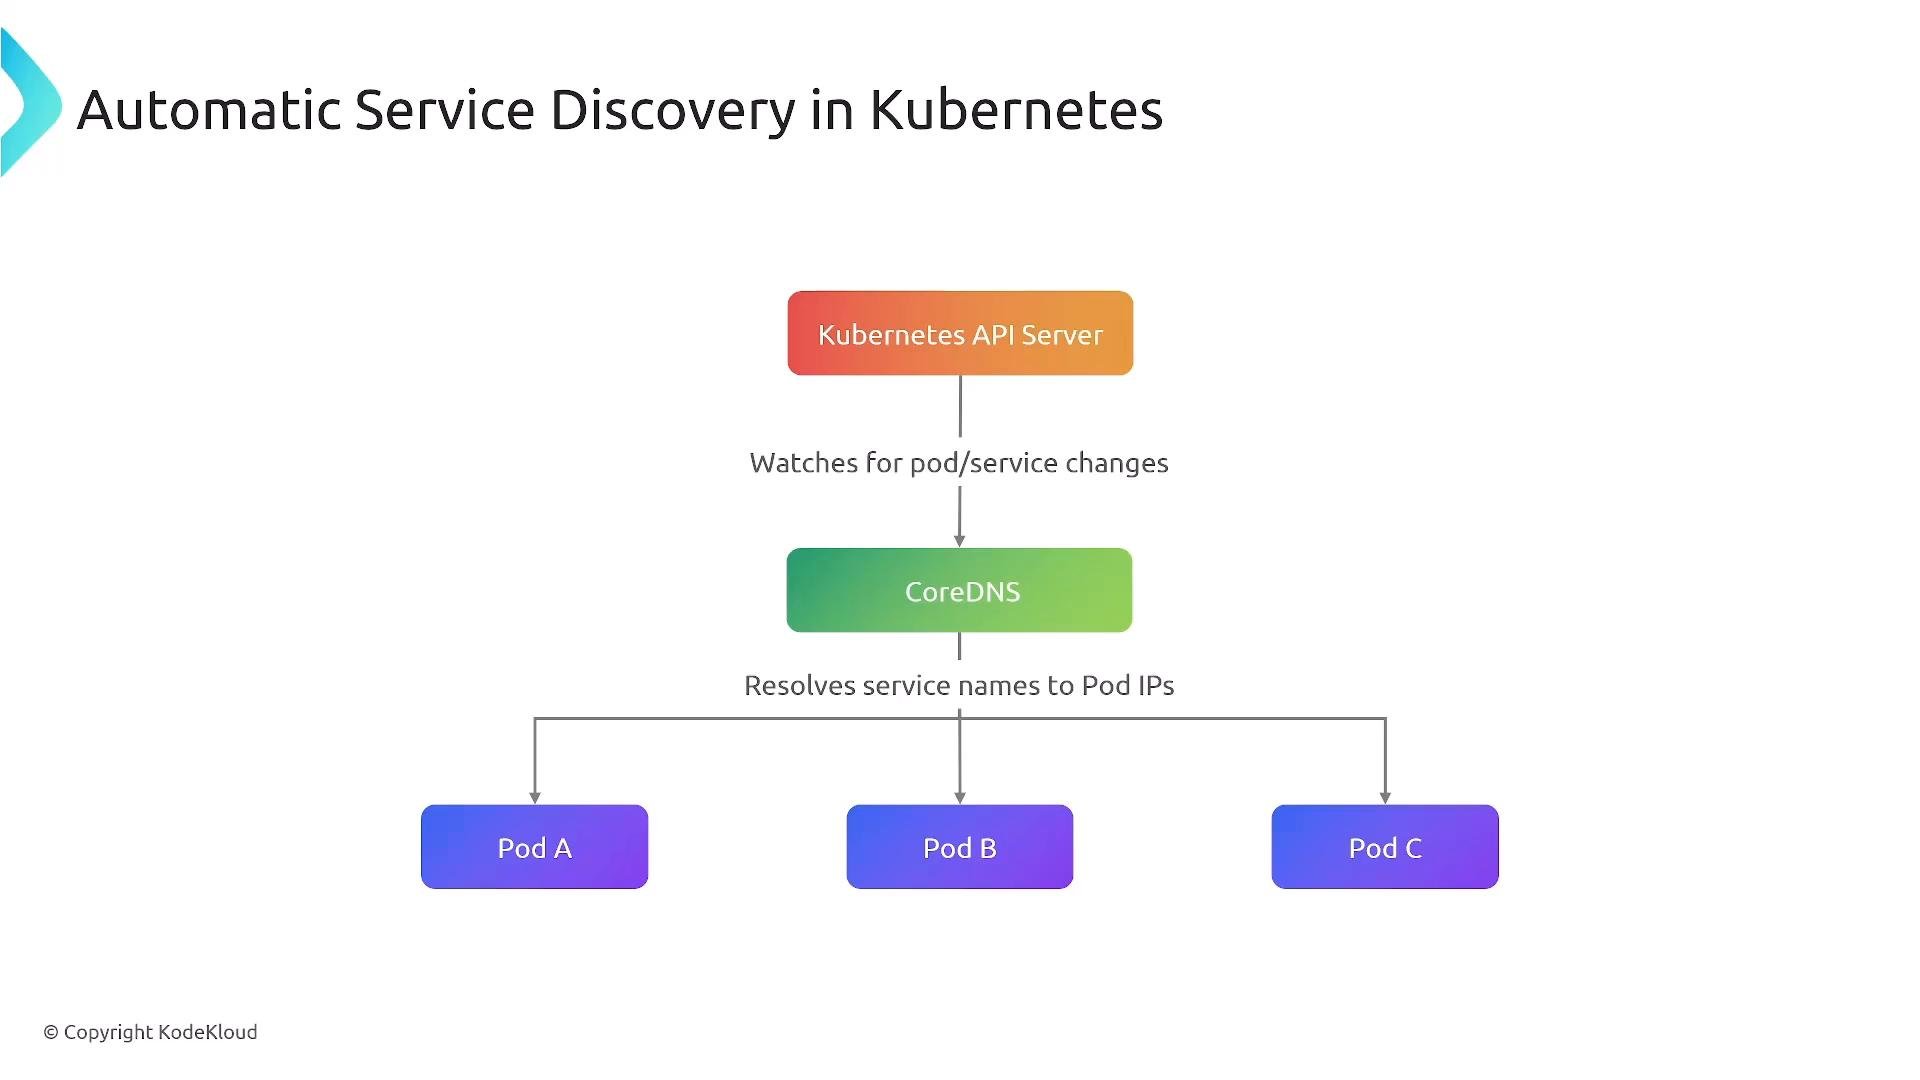
Kubernetes provides automated service discovery via DNS. CoreDNS watches the API server and serves DNS records for services so new services are reachable without manual configuration.- Service FQDN pattern:
service.namespace.svc.cluster.local - CoreDNS resolves service names to the Service cluster IP and endpoints.
pony-spawner.magical-creatures.svc.cluster.local
Understand conceptually how DNS and CoreDNS enable service discovery in Kubernetes (service FQDNs and how services resolve to endpoints). You don’t need to memorize every internal detail, but know the role CoreDNS plays.
Layer 7 ingress controllers and their limitations
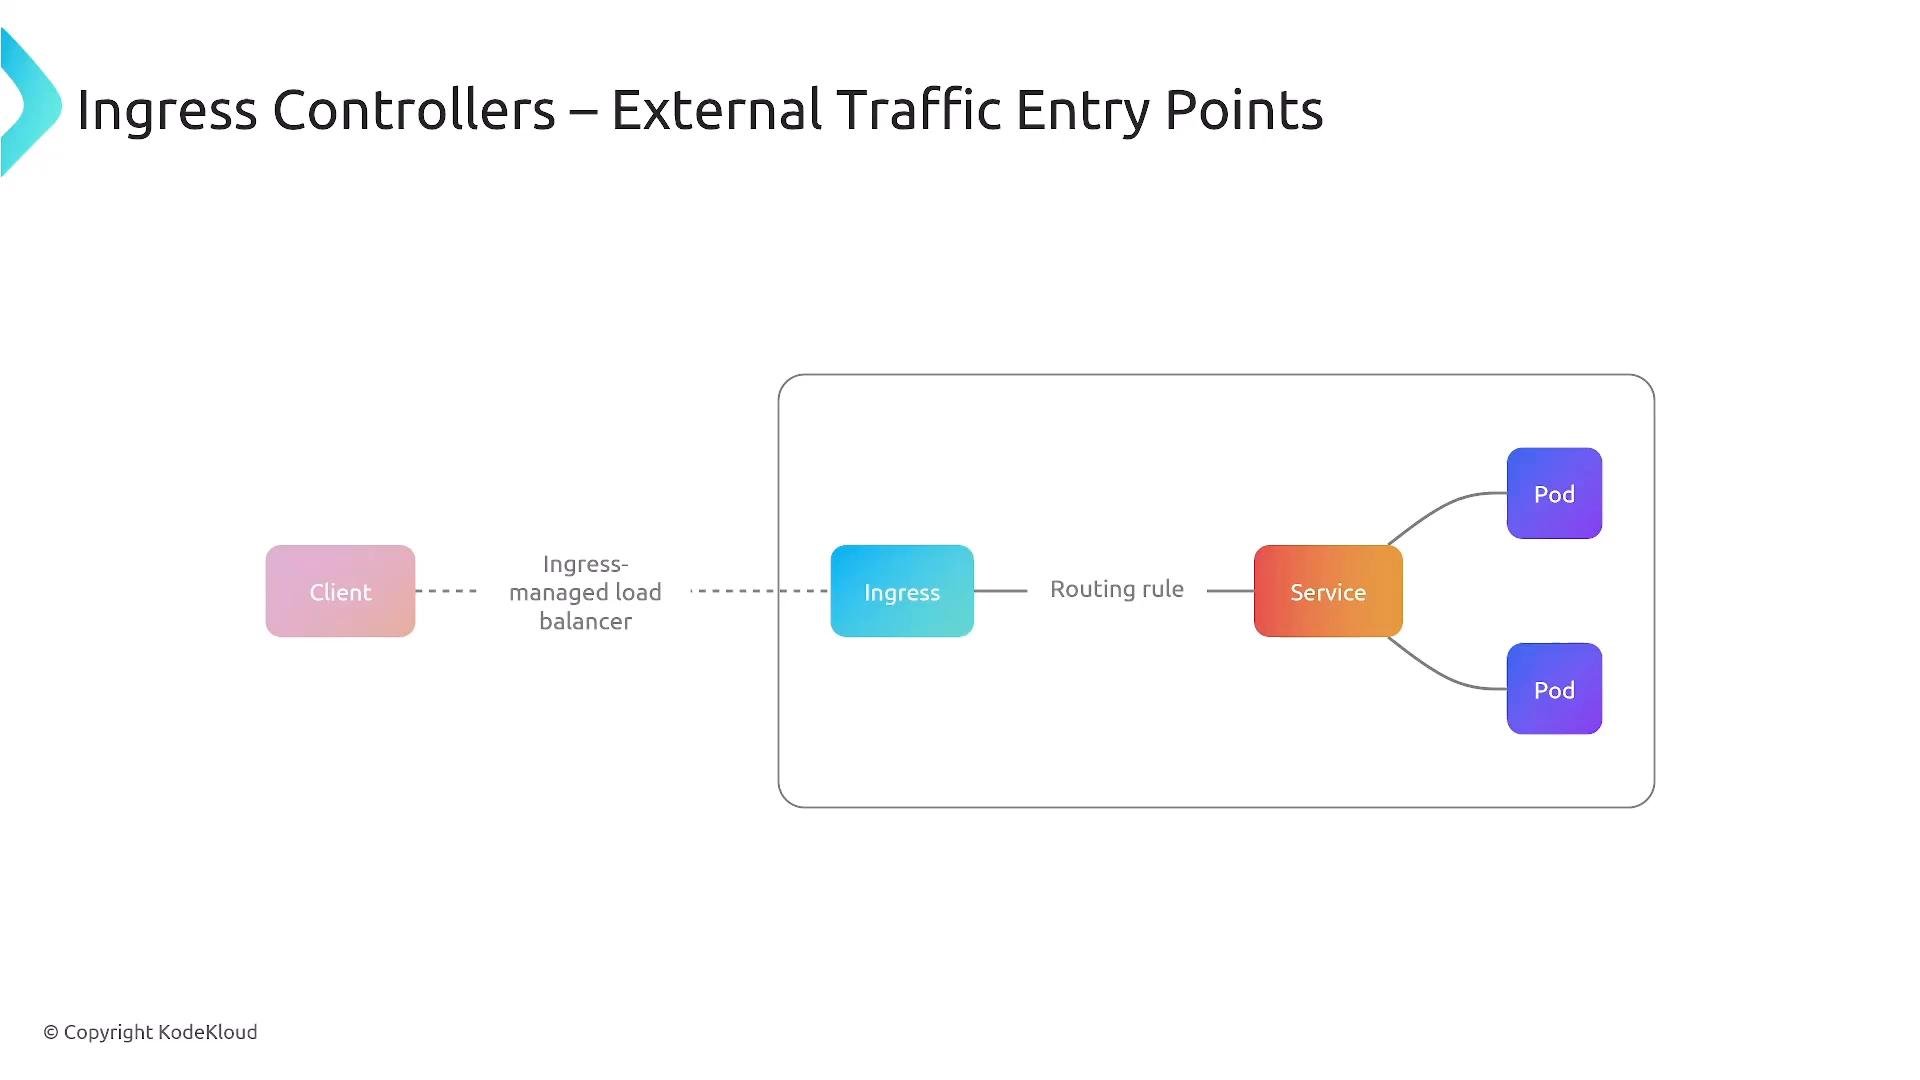
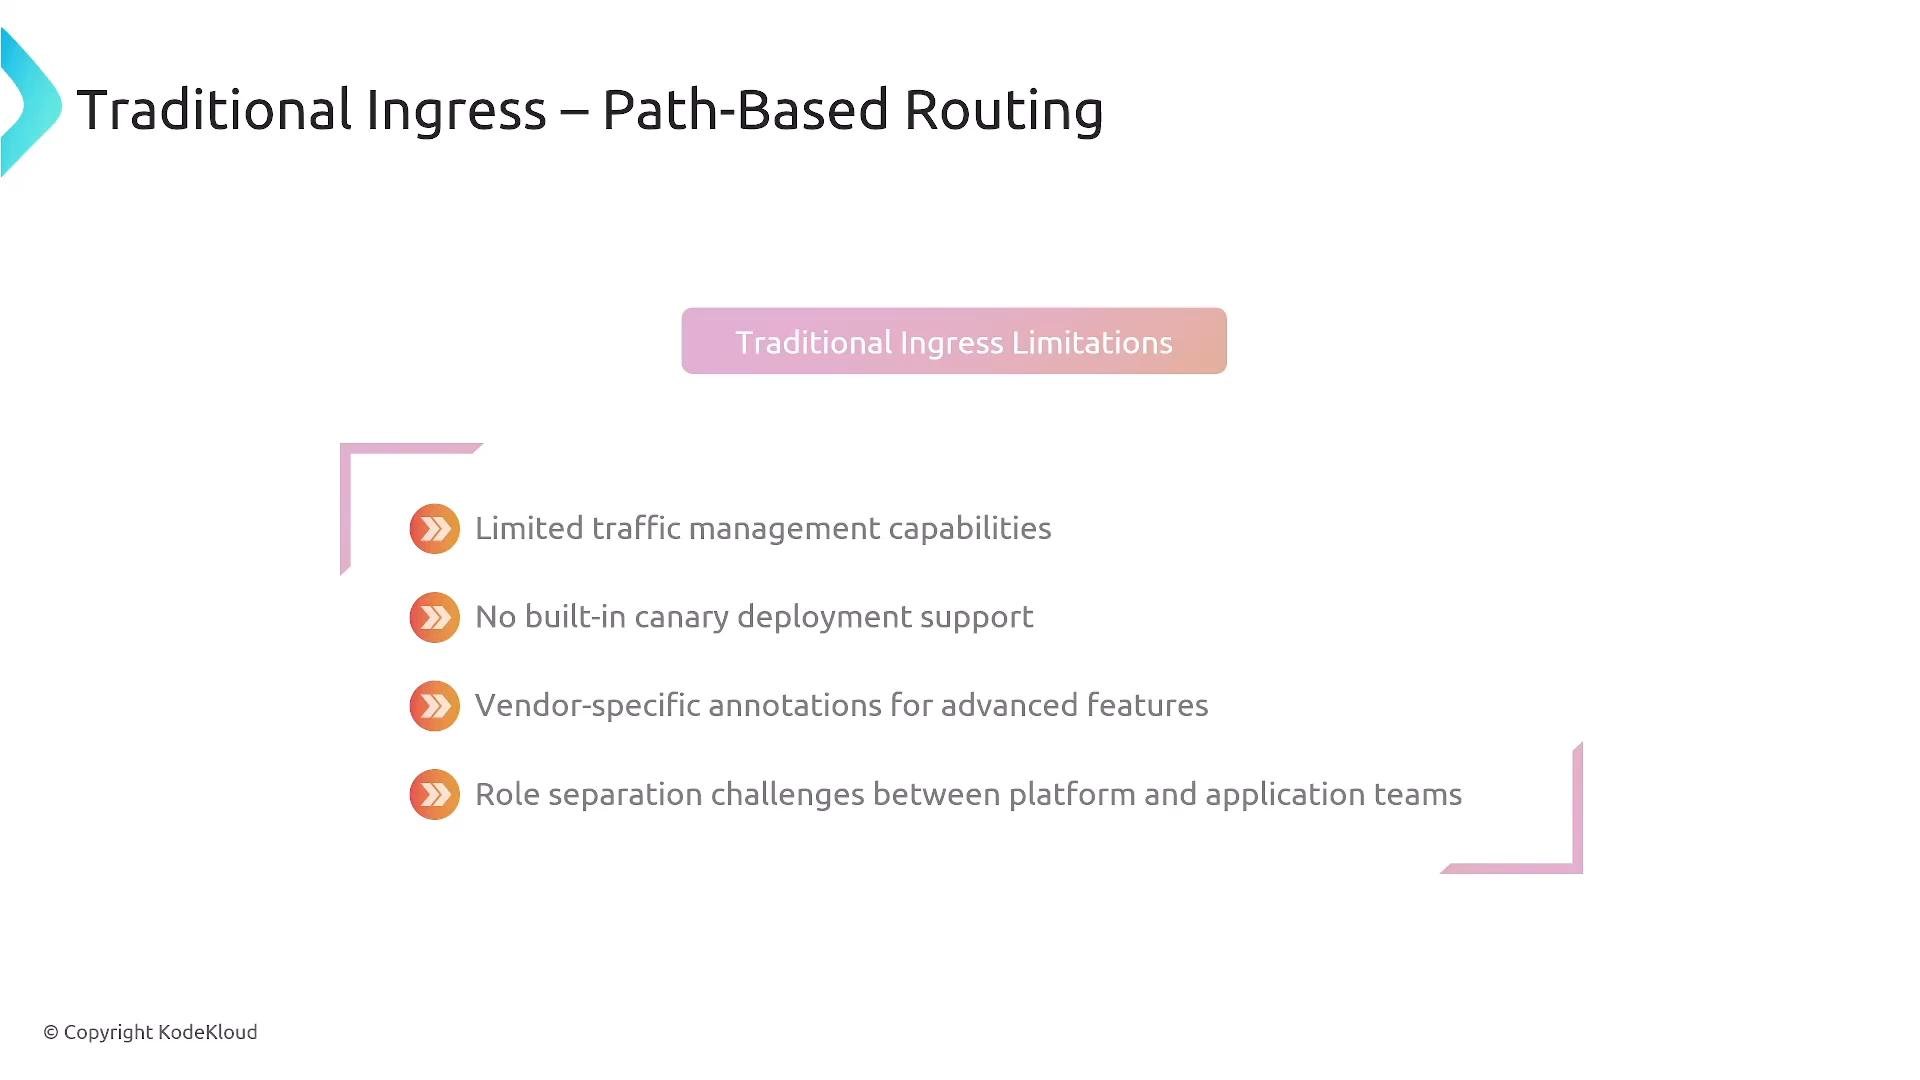
Ingress controllers provide L7 routing (HTTP/S) and commonly sit behind cloud or external load balancers. Typical flow: client → external load balancer → Ingress controller → Service → Pod Common limitations:- Limited or inconsistent traffic management (no native canary support).
- Advanced features often require vendor-specific annotations (reduces portability).
- Role separation between platform and application teams can be challenging.
Gateway API — richer, role-based routing
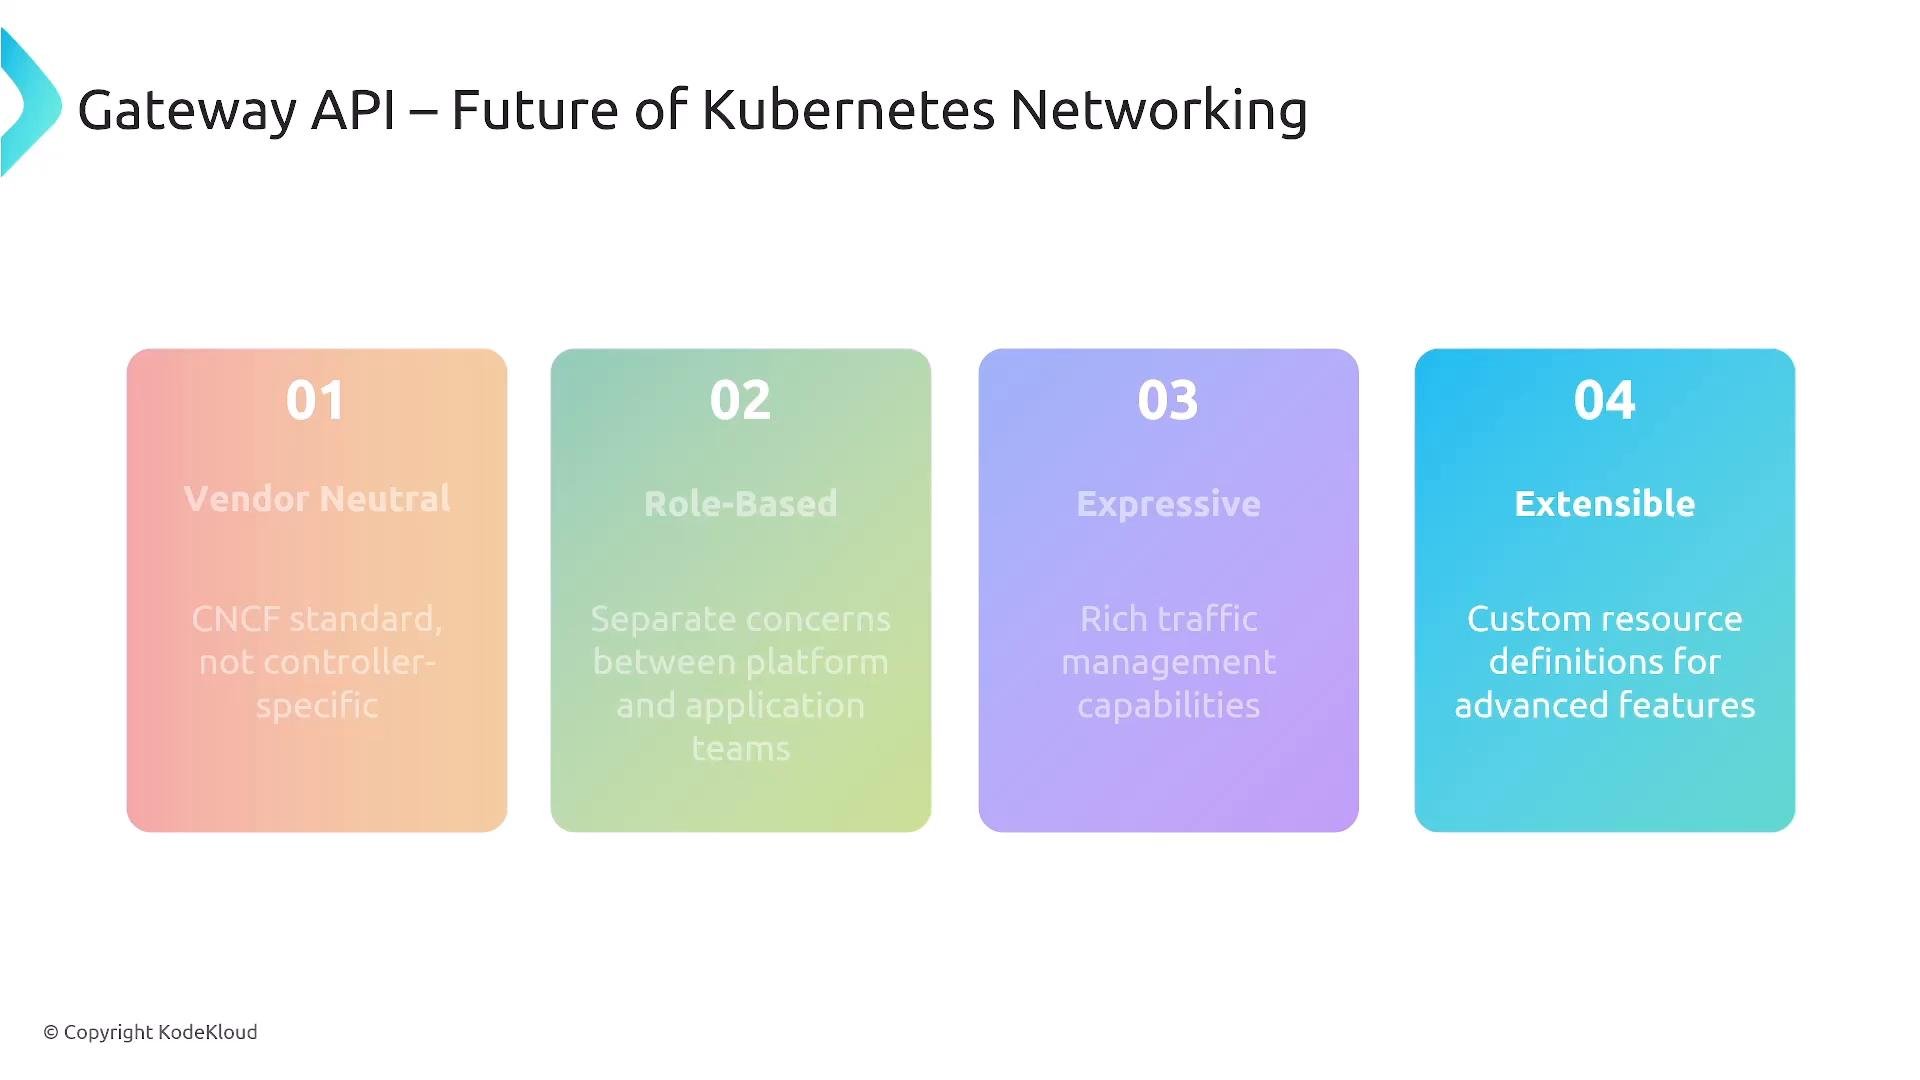
Gateway API is a newer, vendor-neutral Kubernetes API for expressive, role-based L4/L7 routing. It solves many of the limitations of traditional Ingress by separating responsibilities and providing richer traffic controls. Benefits:- Role separation: platform defines GatewayClass and Gateways; apps define HTTPRoute or equivalent.
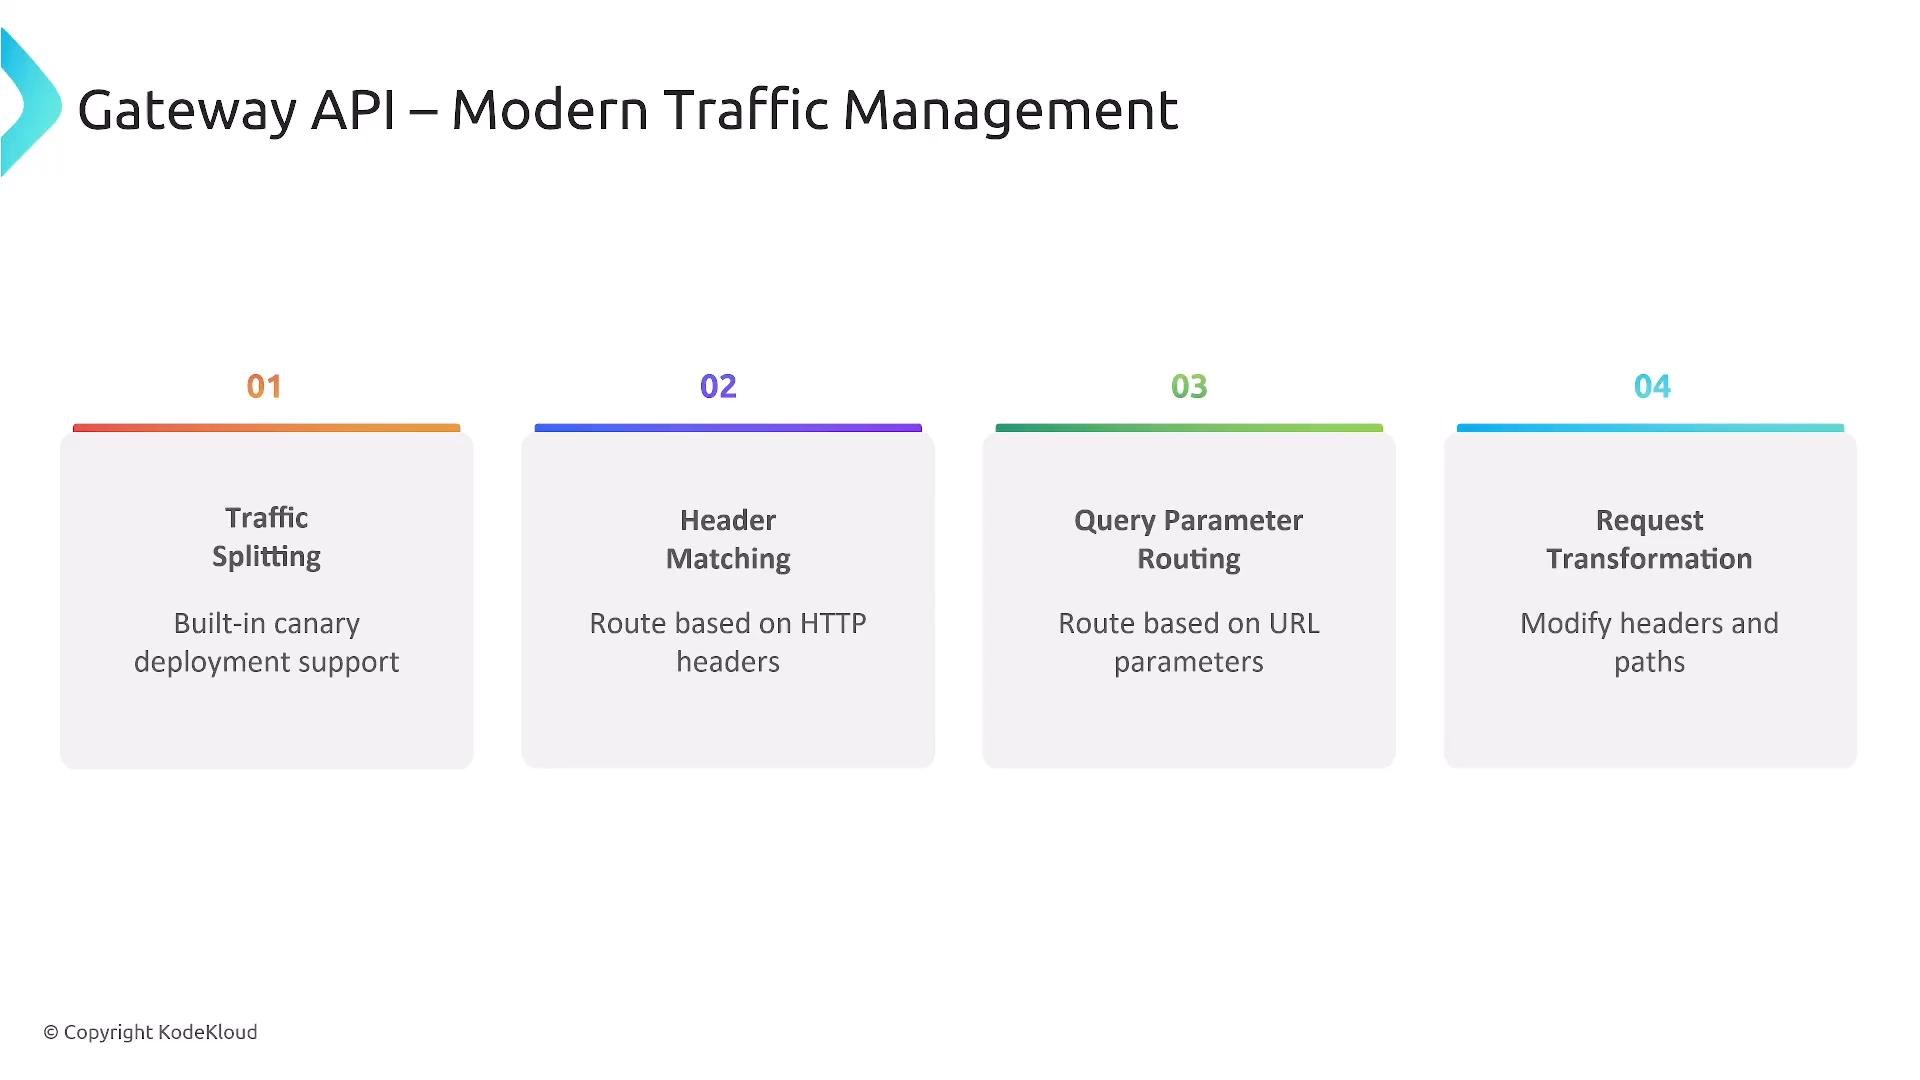
- Rich traffic management: header-based routing, traffic splitting, request transforms, TLS policies.
- Extensibility: vendor-specific features via attachments while preserving portability.
Role-based model in Gateway API
The Gateway API encourages platform-infrastructure separation:- Platform teams: create GatewayClass and provision Gateways with listeners, protocols, TLS settings.
- Application teams: create HTTPRoute (or TCPRoute, TLSRoute) and attach/claim these routes to a Gateway to express application-level routing.
- Infrastructure can enforce backend TLS policies, routing constraints, and security guardrails while developers control application-specific routes.
Advanced traffic management with Gateway API
Gateway API supports built-in capabilities needed for modern release strategies:- Traffic splitting for canaries and progressive rollouts.
- Header-based routing (A/B testing, multi-tenancy headers).
- Query-parameter routing and request/response transformations.
- Fine-grained TLS configuration per listener and backend.
Service mesh and integration
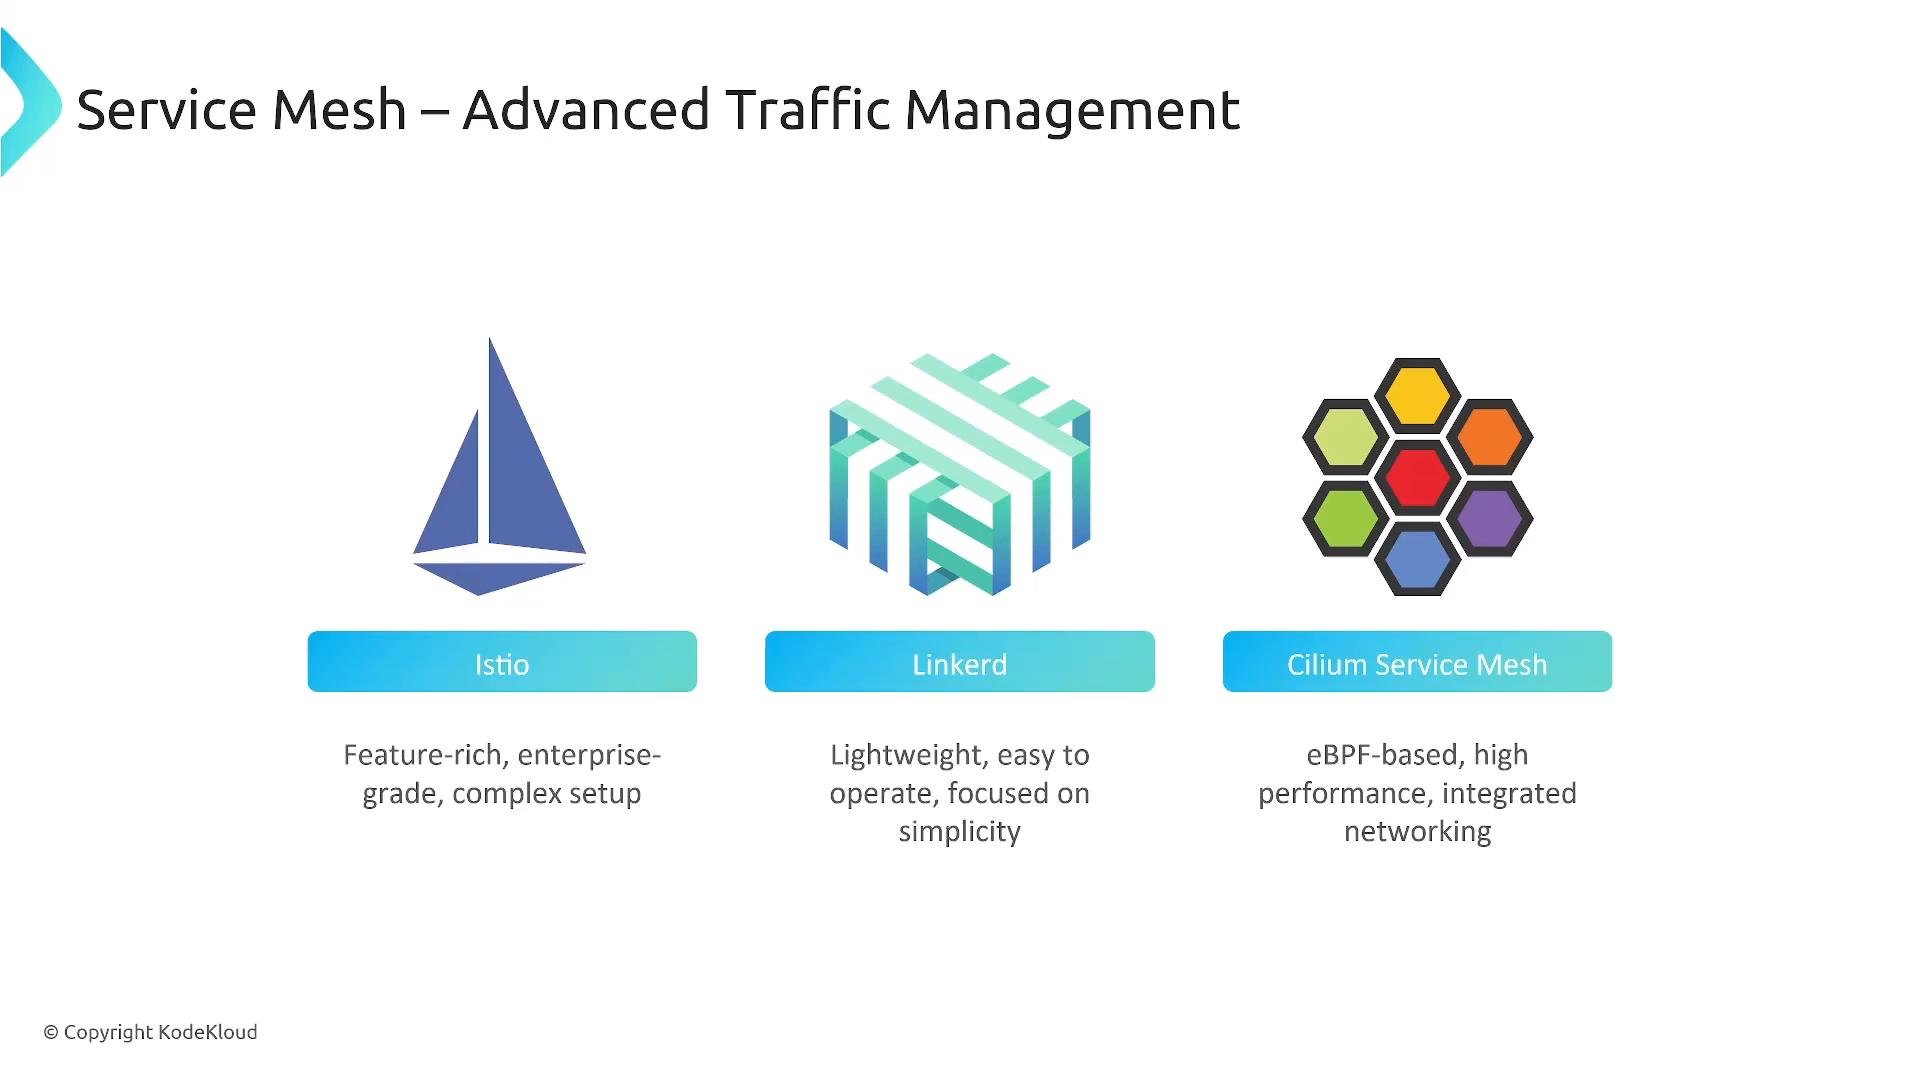
Gateway API can complement or integrate with service meshes (Istio, Linkerd, Envoy, Cilium) depending on needs. Choose a mesh when you require:- mTLS identity and workload identity features
- Advanced telemetry and tracing
- Circuit breaking, retries, and rich L7 policies
- Complex cross-cluster routing and telemetry correlation
- Istio: https://istio.io/
- Linkerd: https://linkerd.io/
- Cilium: https://cilium.io/
Network segmentation and Zero Trust
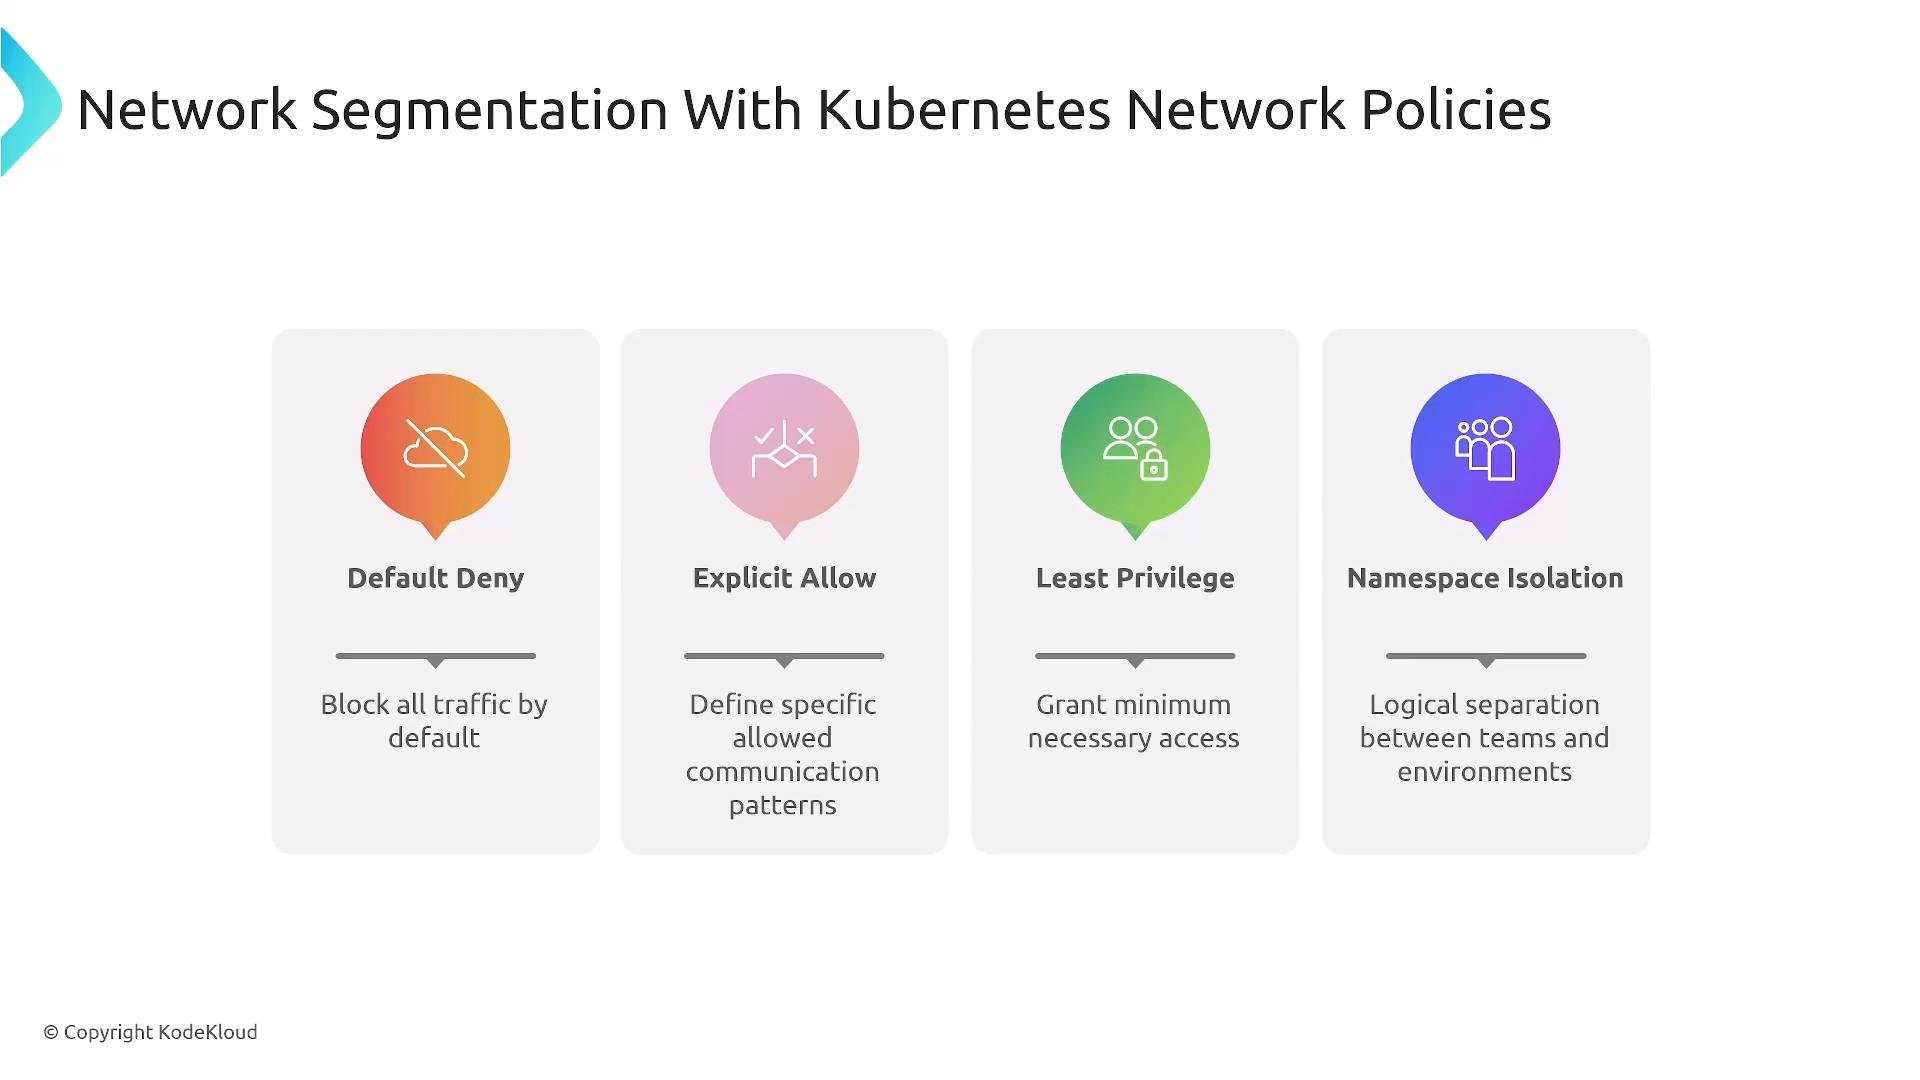
Adopt Zero Trust networking principles in Kubernetes:- Default-deny by default and explicitly allow required flows.
- Least privilege: grant minimal access between namespaces and services.
- Micro-segmentation: use NetworkPolicies, service mesh policies, or CNI capabilities to isolate workloads.
Cross-cluster communication concerns
Multi-cluster and geo-distributed workloads introduce additional challenges:- Network latency and throughput between clusters
- Certificate and identity management across clusters
- Multi-cluster service discovery and failover strategies
- Cost considerations for cross-region data transfer
Advanced load balancing and resiliency
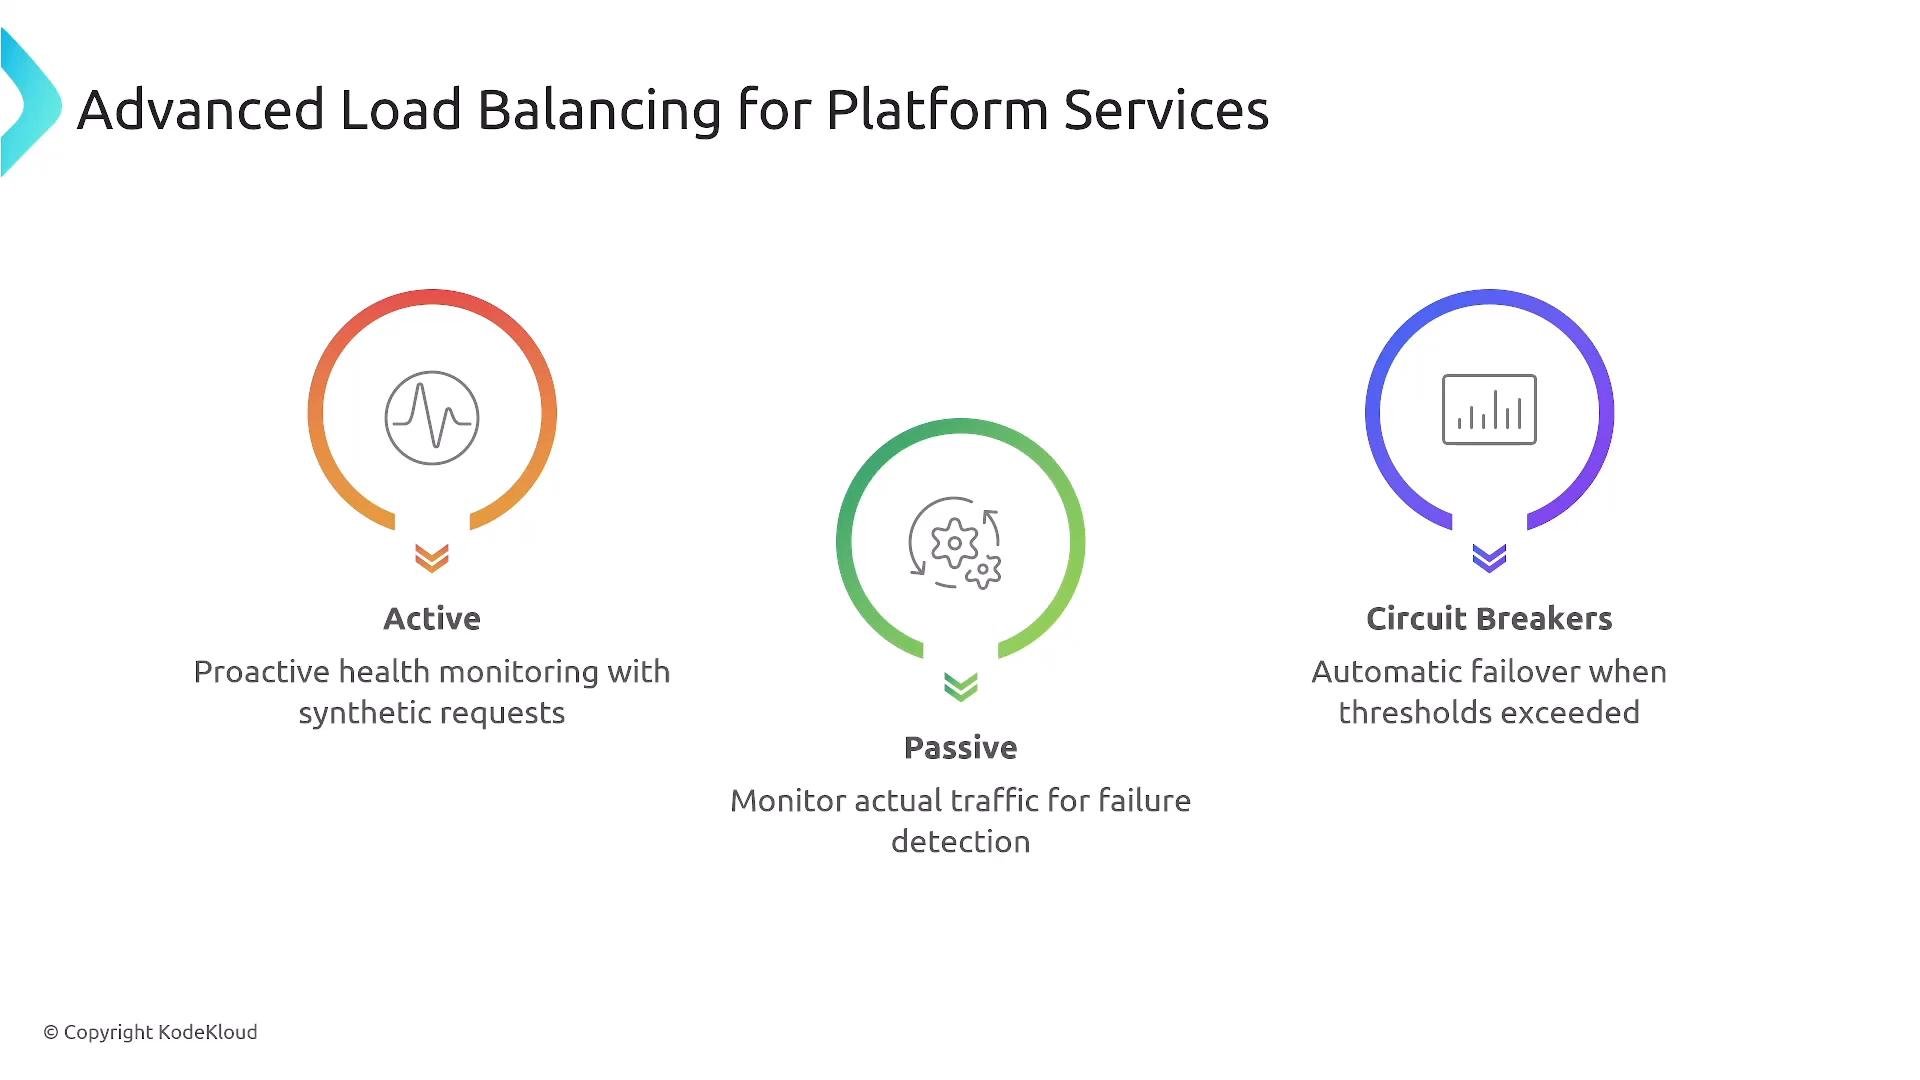
Design resilient traffic handling with a mix of active and passive checks, circuit breakers, and retry policies.- Active health checks: periodic probes to endpoints.
- Passive health checks: observe failed requests and mark endpoints unhealthy.
- Circuit breakers and retry budgets: prevent cascading failures.
Deployment patterns that affect networking
Traffic management patterns influence how you design routing and observability.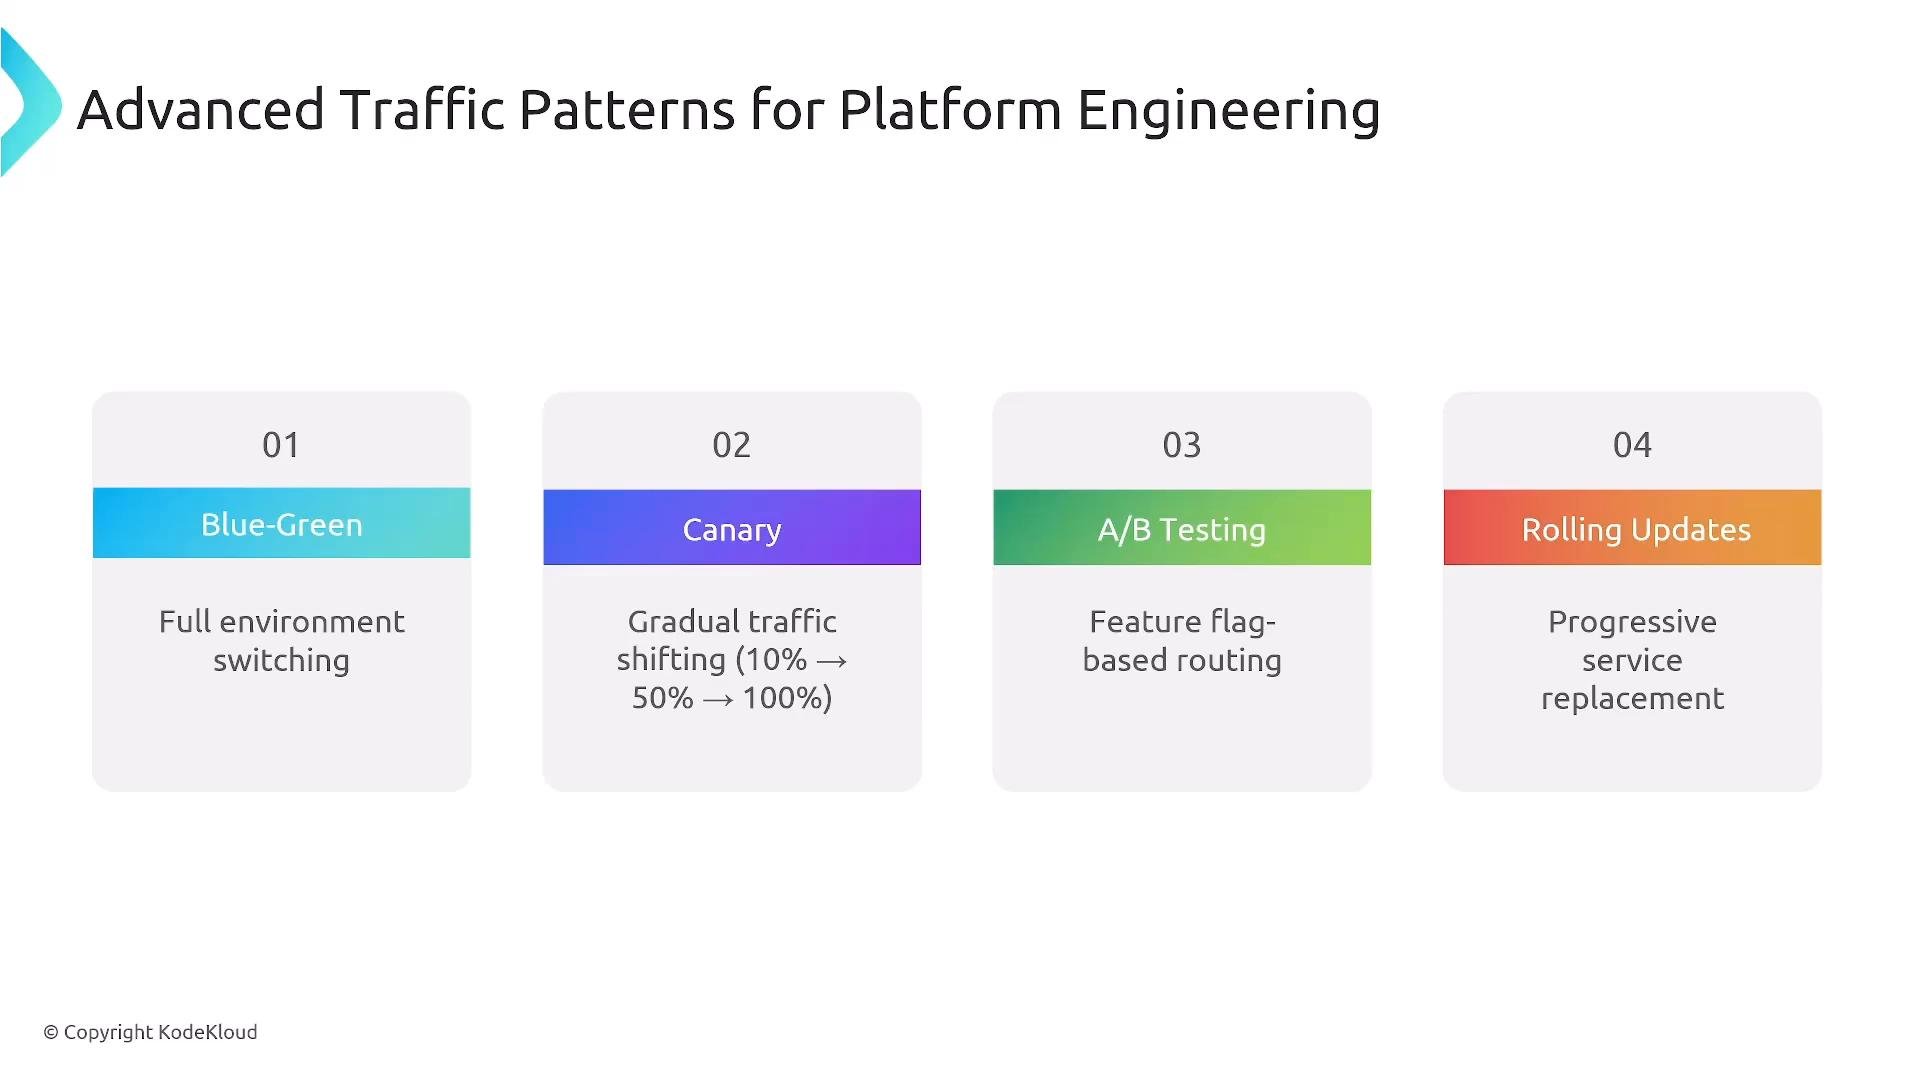
Key takeaways for platform engineers
- Service discovery is fundamental: Kubernetes + CoreDNS provides FQDN-based service resolution.
- Gateway API provides role-based, portable L4/L7 routing and richer traffic management than traditional Ingress.
- Enforce Zero Trust: default-deny policies, explicit allows, and least privilege segmentation.
- Use canary, blue-green, A/B testing, and rolling updates for safer deployments; Gateway API and service meshes simplify implementation.
- Plan for multi-cluster and cross-region challenges (latency, identity federation, discovery, cost).
- Observability is essential: ensure network-level telemetry (logs, metrics, traces) for troubleshooting and capacity planning.
- Balance cost vs. complexity when choosing between Ingress, Gateway API, and a full service mesh.