

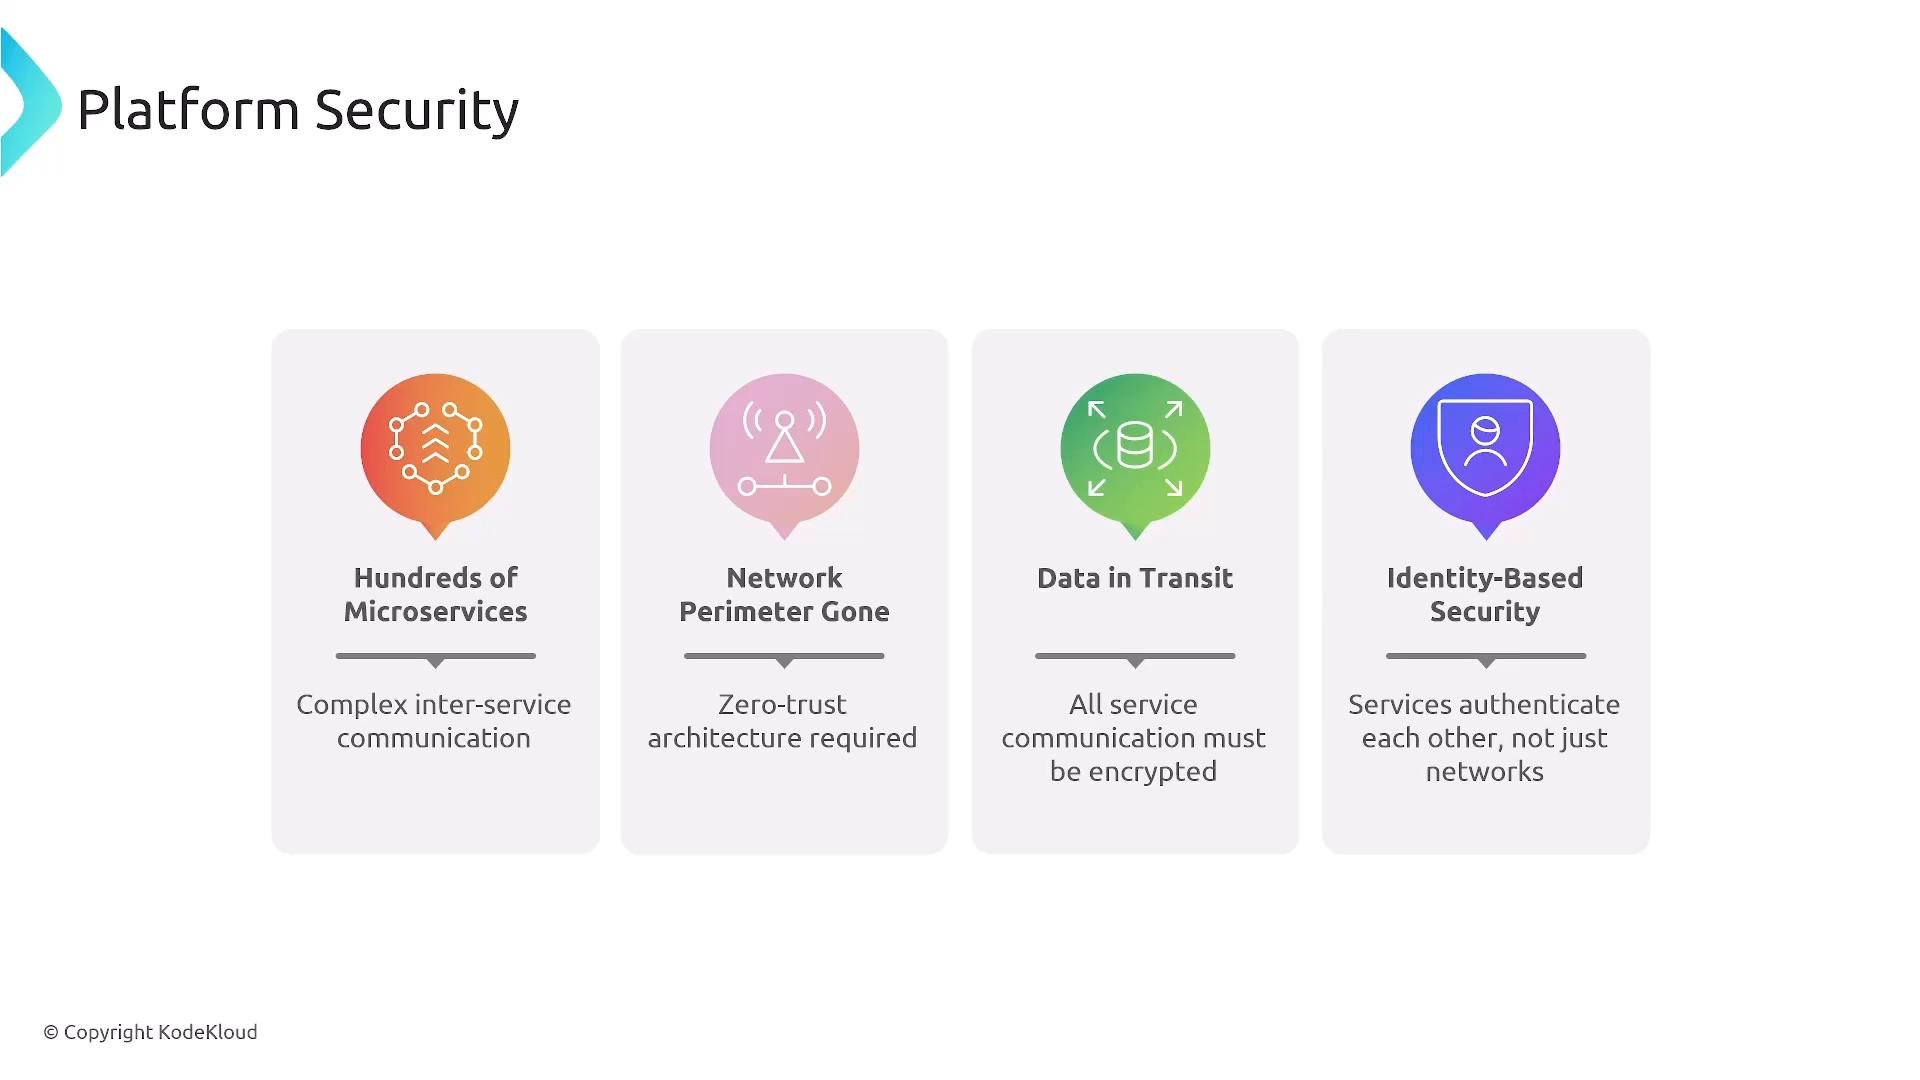
- Scales to hundreds of microservices with consistent security and traffic controls.
- Enables zero‑trust service identities and explicit allow policies.
- Encrypts data in transit and provides service-to-service identity verification, including across clusters.
- Implements policy-as-code for service communication, reducing brittle network-level controls.
From perimeter security to service identity
Modern cloud-native platforms move away from perimeter/IP-based controls toward cryptographic service identities, automatic encryption-in-transit, and centralized policy enforcement. In this zero‑trust model, every service interaction must be explicitly authenticated and authorized.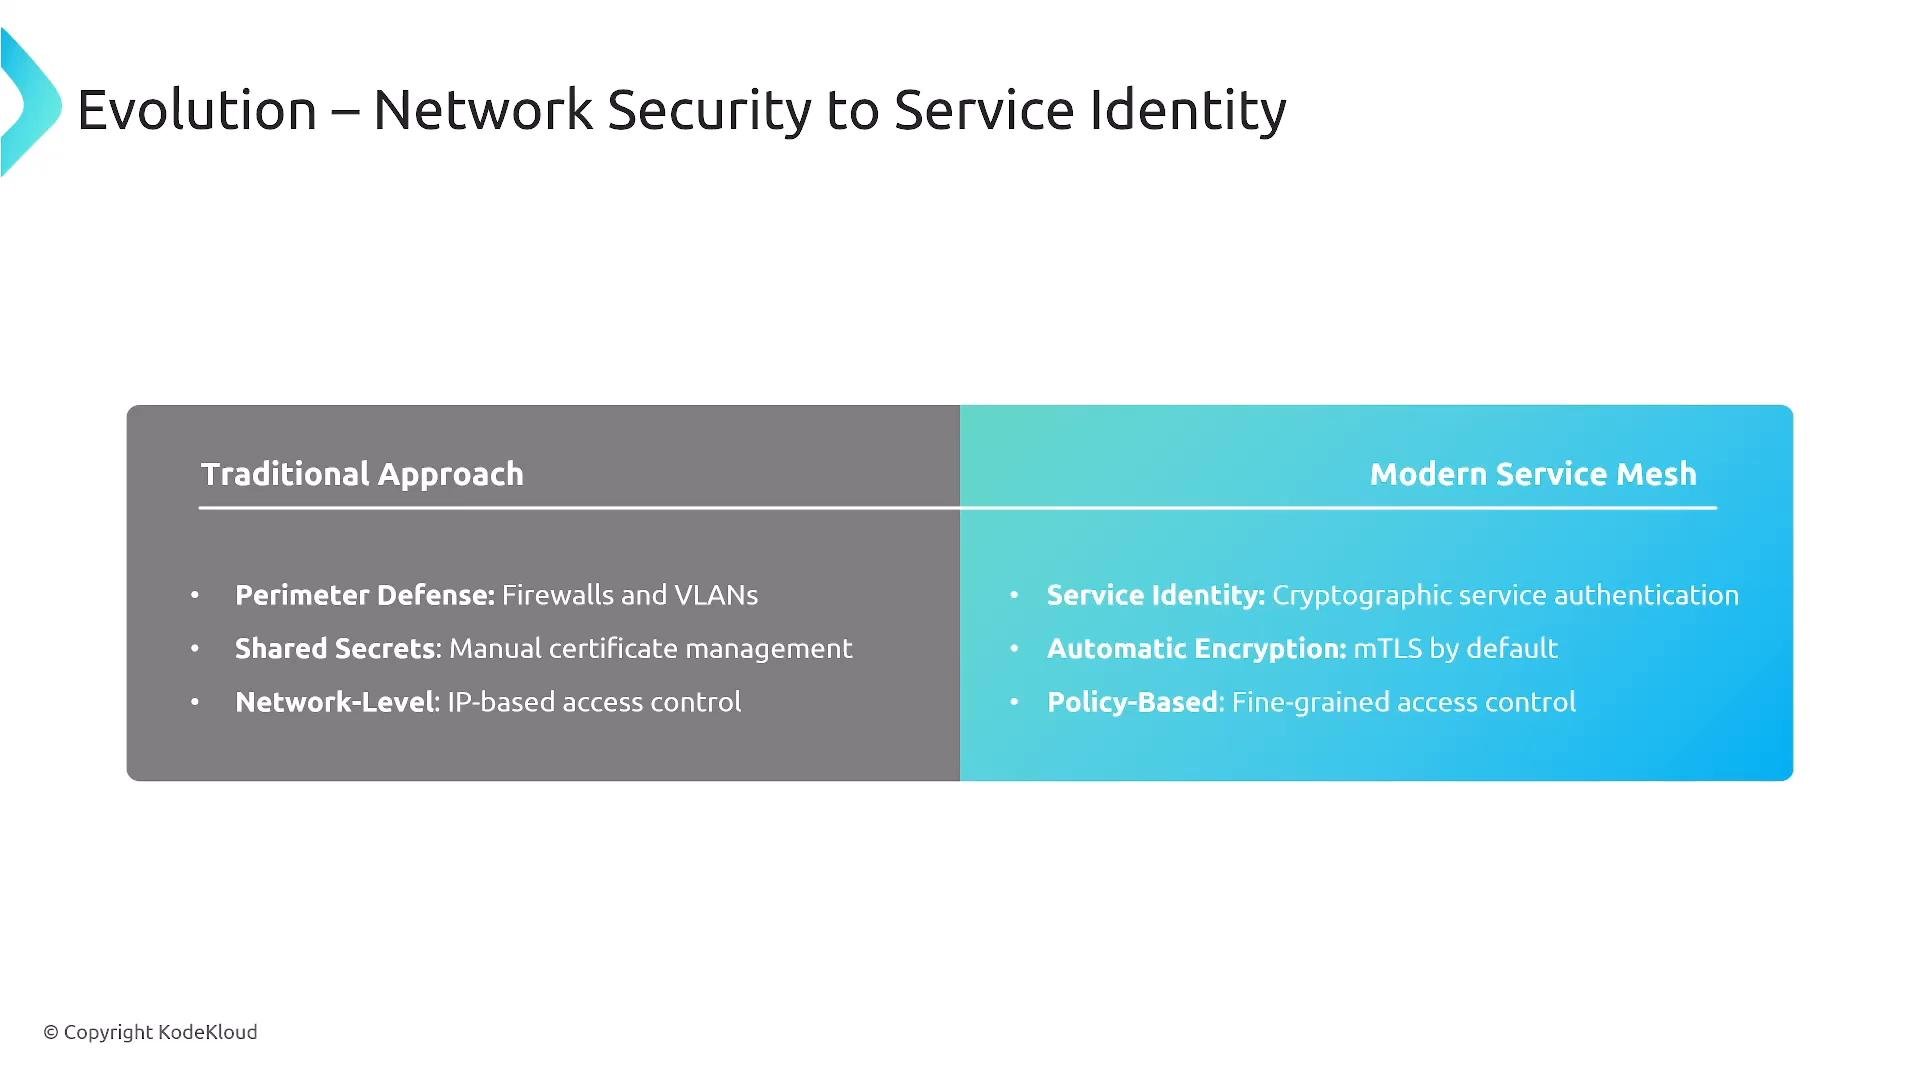
- Platform engineers can provide centralized networking, identity, and security guarantees.
- Developers focus on business logic without embedding certificate handling into app code.
- The infrastructure transparently handles mTLS, certificate rotation, and policy enforcement.
What is a service mesh?
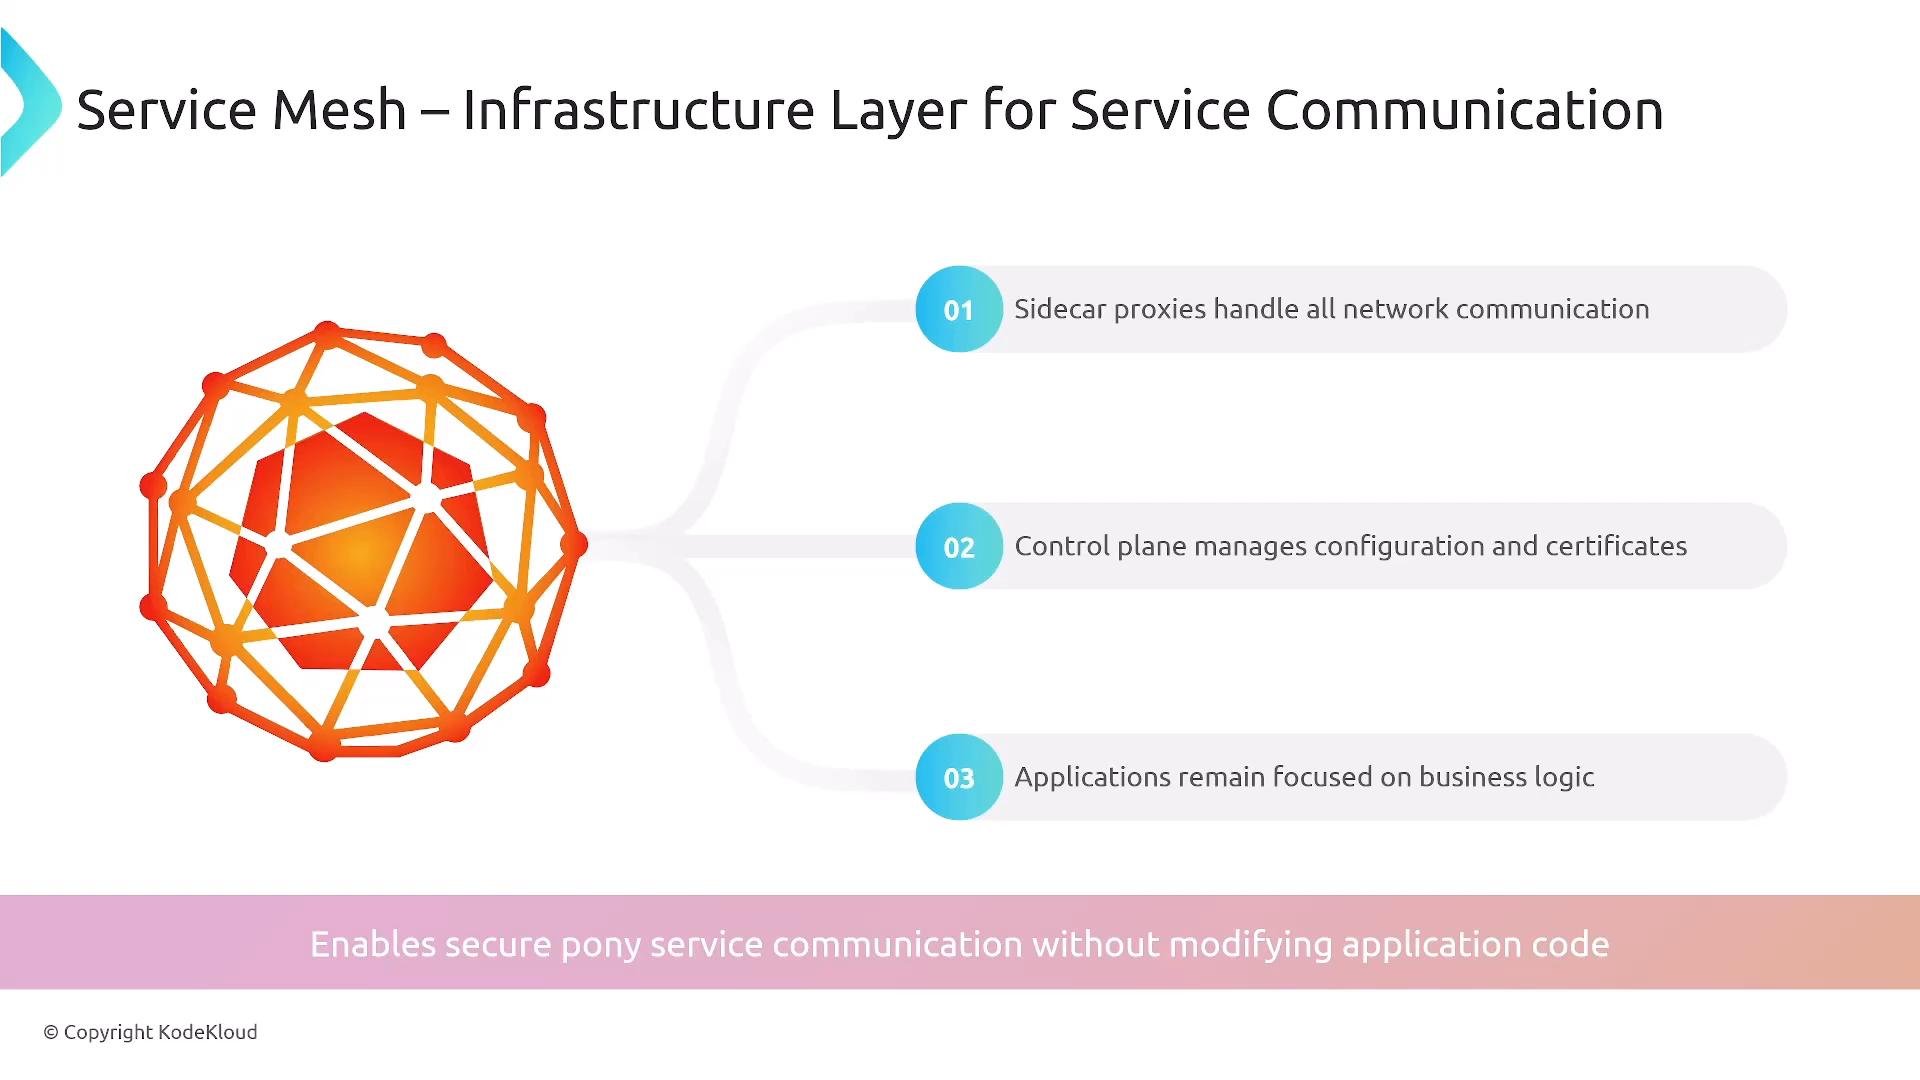
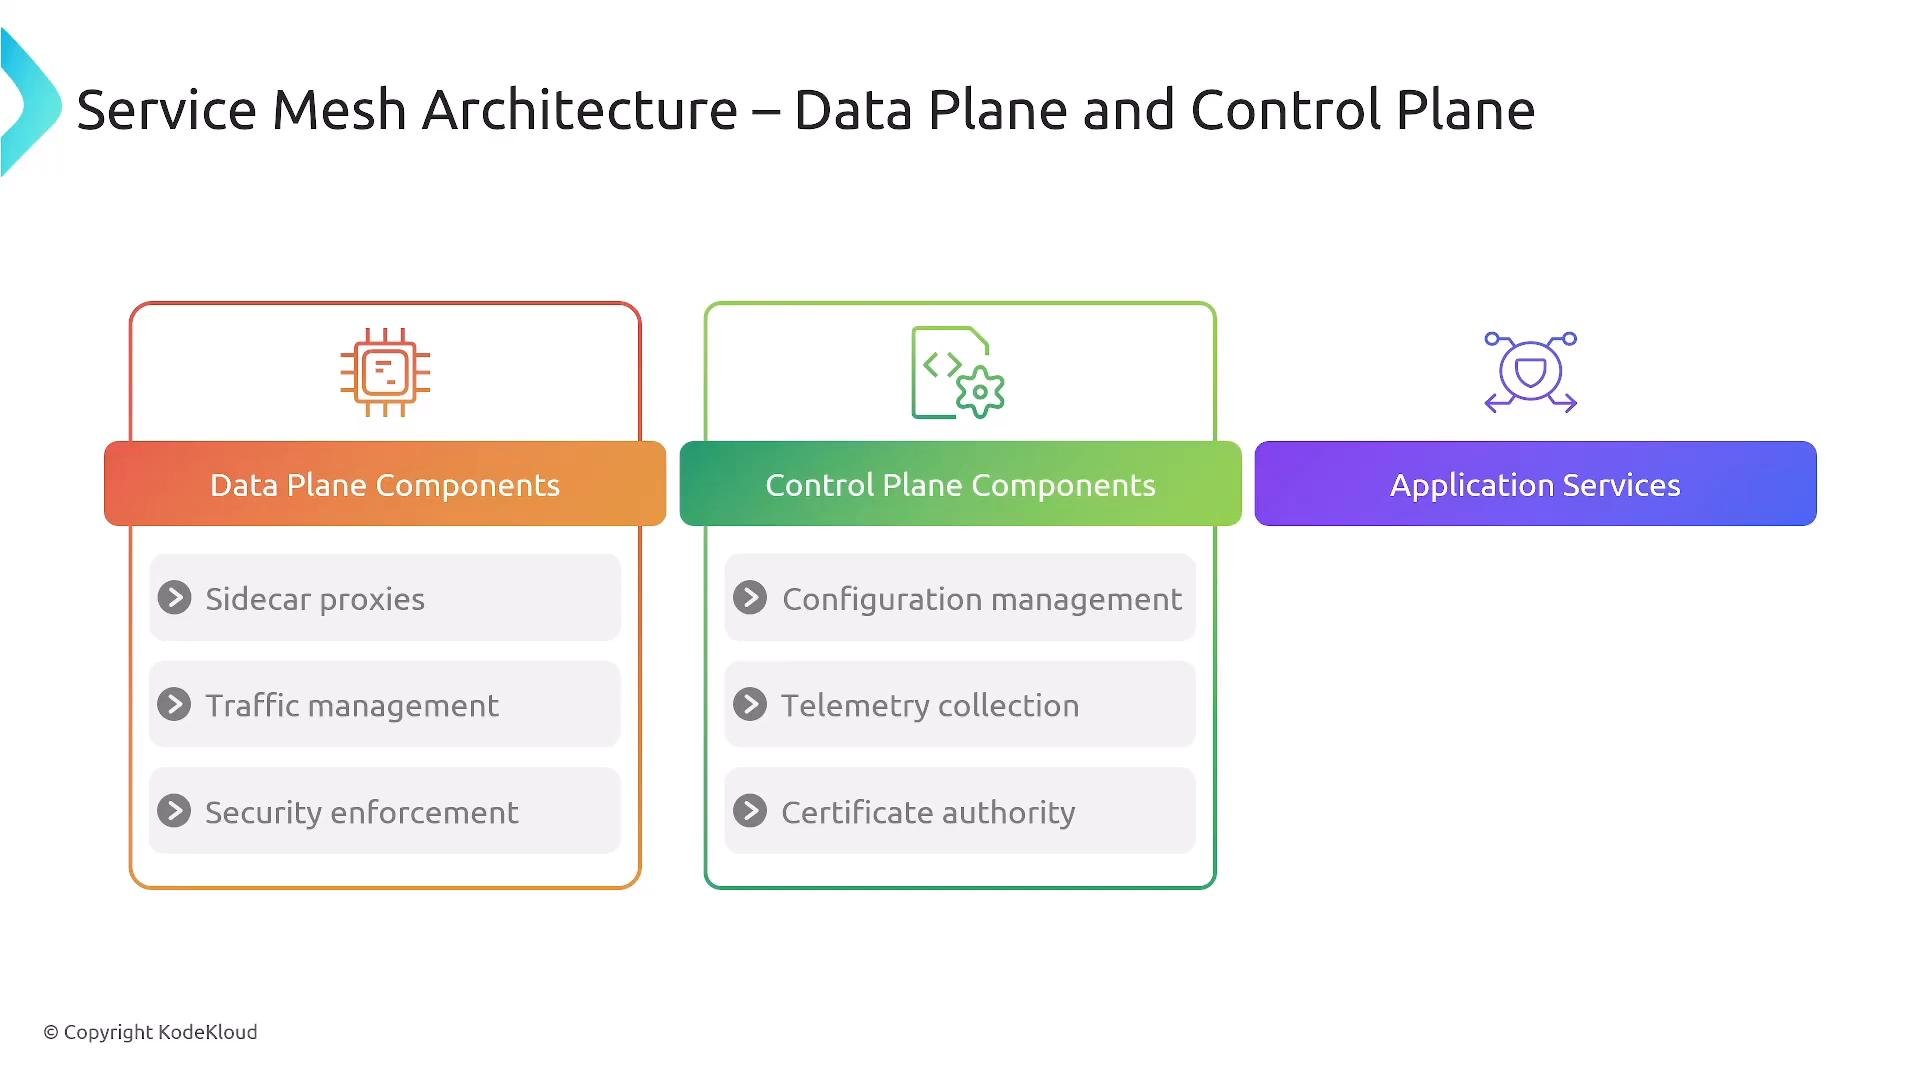
A service mesh is an infrastructure layer that provides secure, observable, and controllable service-to-service communication. It is commonly implemented using sidecar proxies injected into application pods, or via ambient/injectionless modes. Typical mesh components:- Data plane: sidecar proxies that handle traffic, encryption, and enforcement.
- Control plane: manages configuration, issues certificates, and collects telemetry.
- Applications: run unmodified and rely on the mesh for communication features.
Mutual TLS (mTLS) — cryptographic service authentication
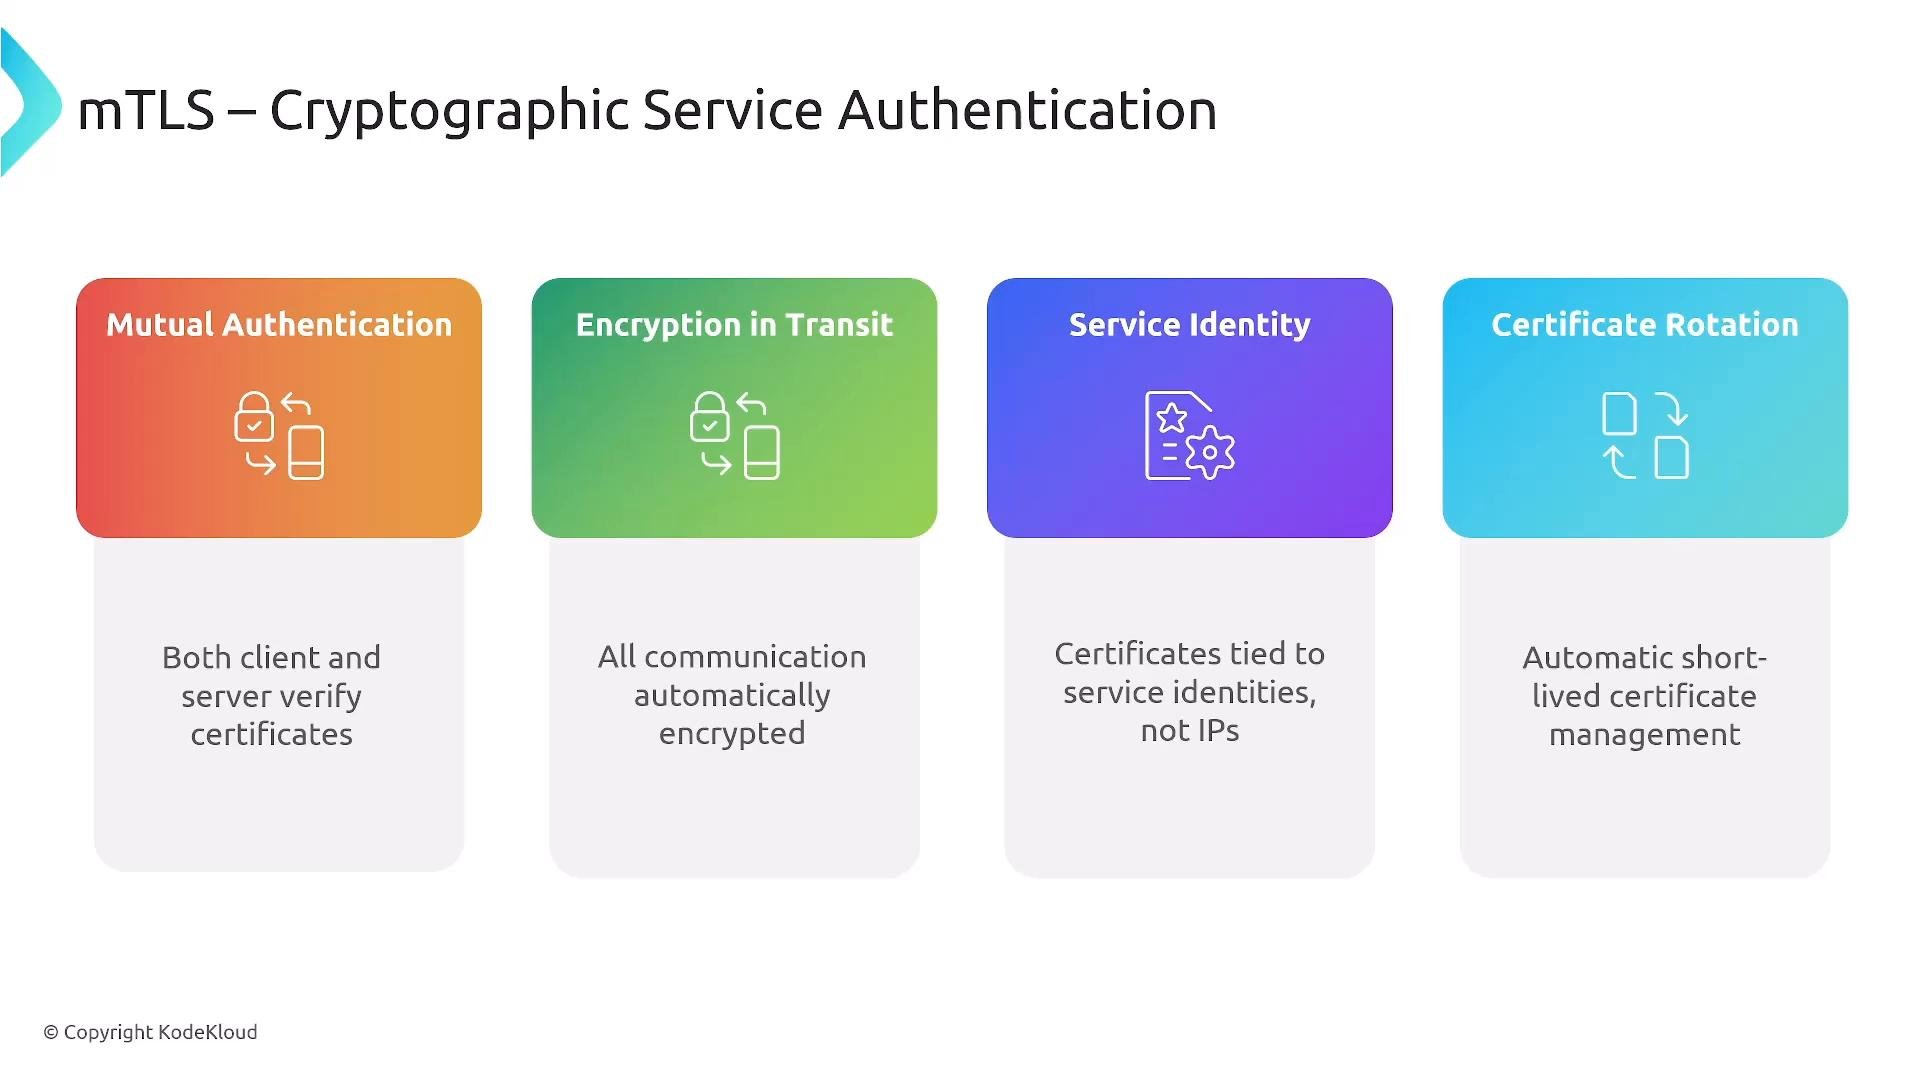
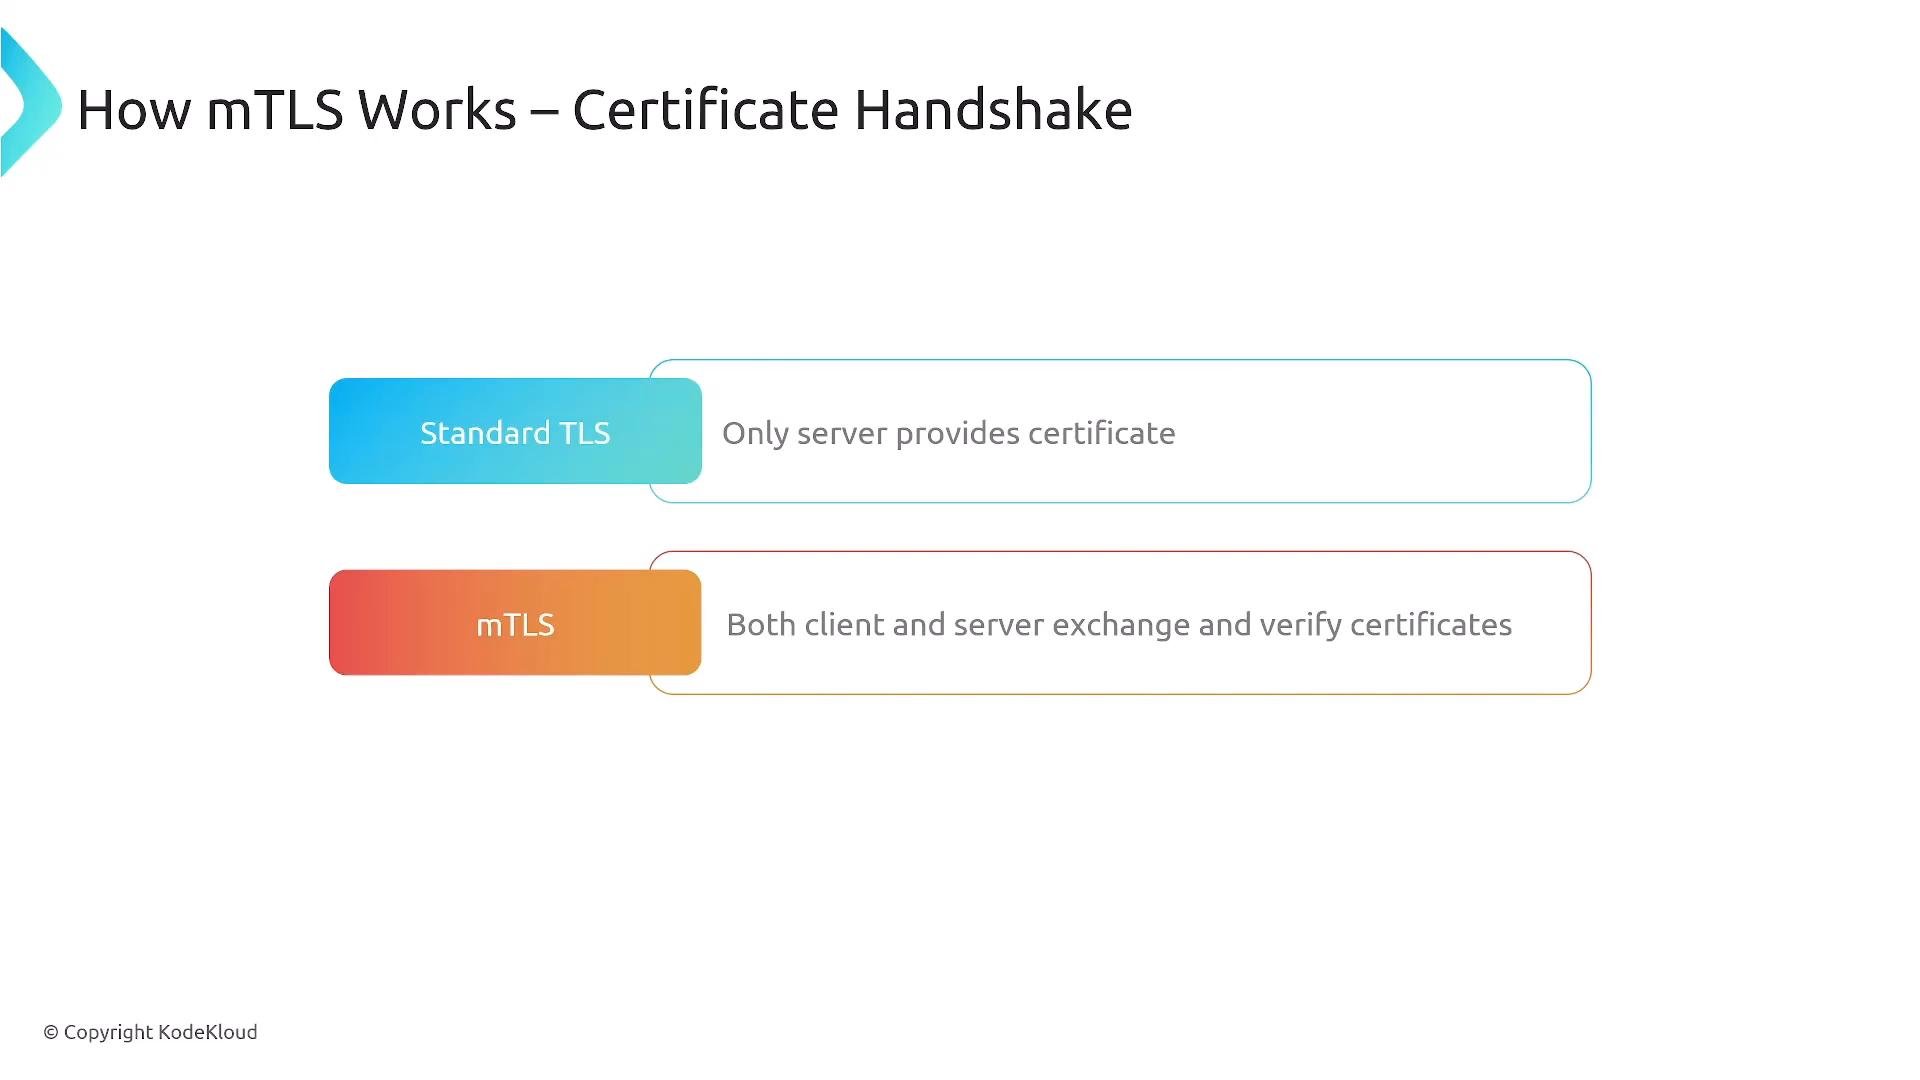
One of the most important security primitives provided by service meshes is mutual TLS (mTLS). mTLS provides:- Mutual authentication (both client and server validate certificates).
- Encryption for data in transit.
- Service identity (certificates bind to service identities, not IPs).
- Automated short‑lived certificate issuance and rotation.
Popular meshes and proxies
Understand the common projects and their trade-offs:
Each choice involves trade-offs: choose Istio for advanced features, Linkerd for operational simplicity and performance, or Envoy if you need a flexible high-performance proxy.
Network layer: L4 vs L7
Service meshes and related controls can operate at different OSI layers. Choose the layer that matches your needs for performance and application awareness.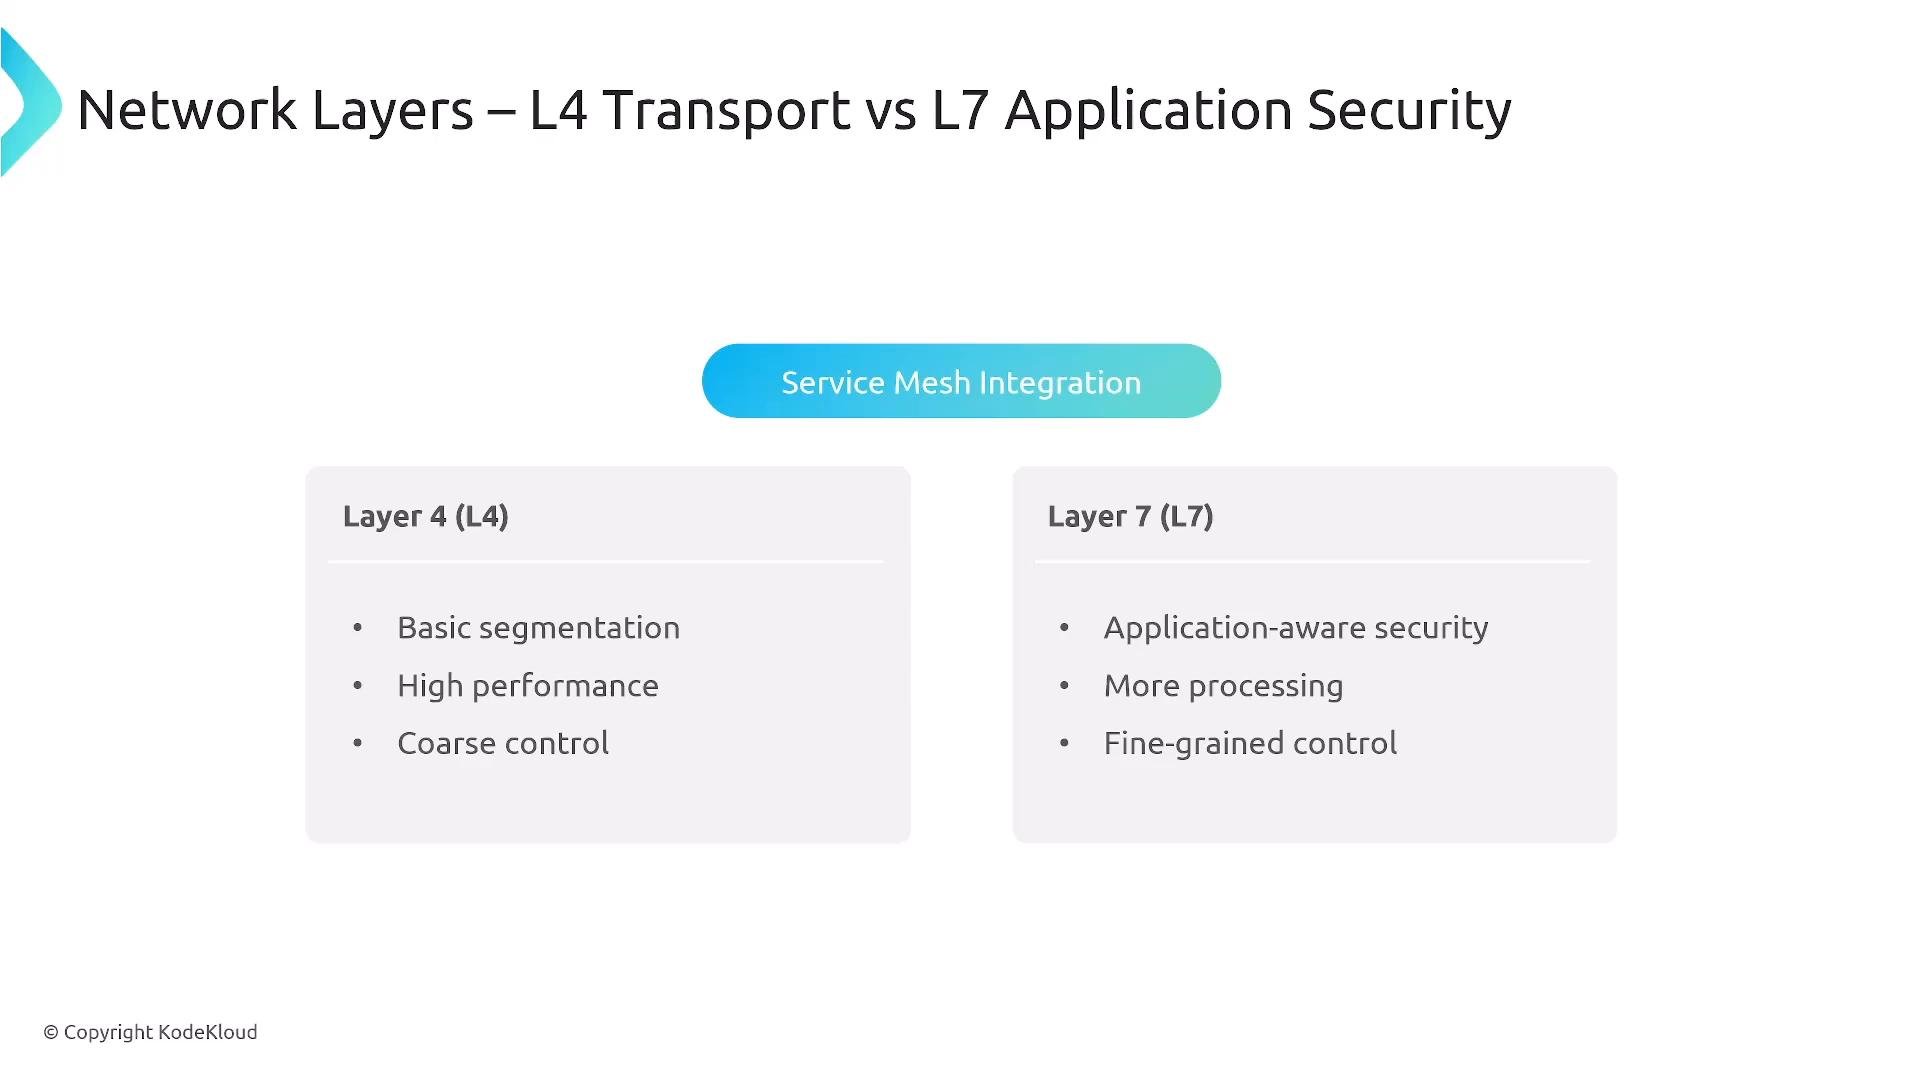
- Many meshes favor deny-by-default for east-west traffic; you should write explicit allow policies.
- Identity-based access control replaces brittle IP rules.
- The mesh control plane automates certificate issuance, rotation, and revocation; this is not an eBPF responsibility.
eBPF — kernel-level observability and enforcement
eBPF extends the kernel with safe, efficient programs allowing deep visibility and high-performance enforcement. eBPF complements service meshes by accelerating the data plane and providing visibility at the packet/process level. Common eBPF-based projects: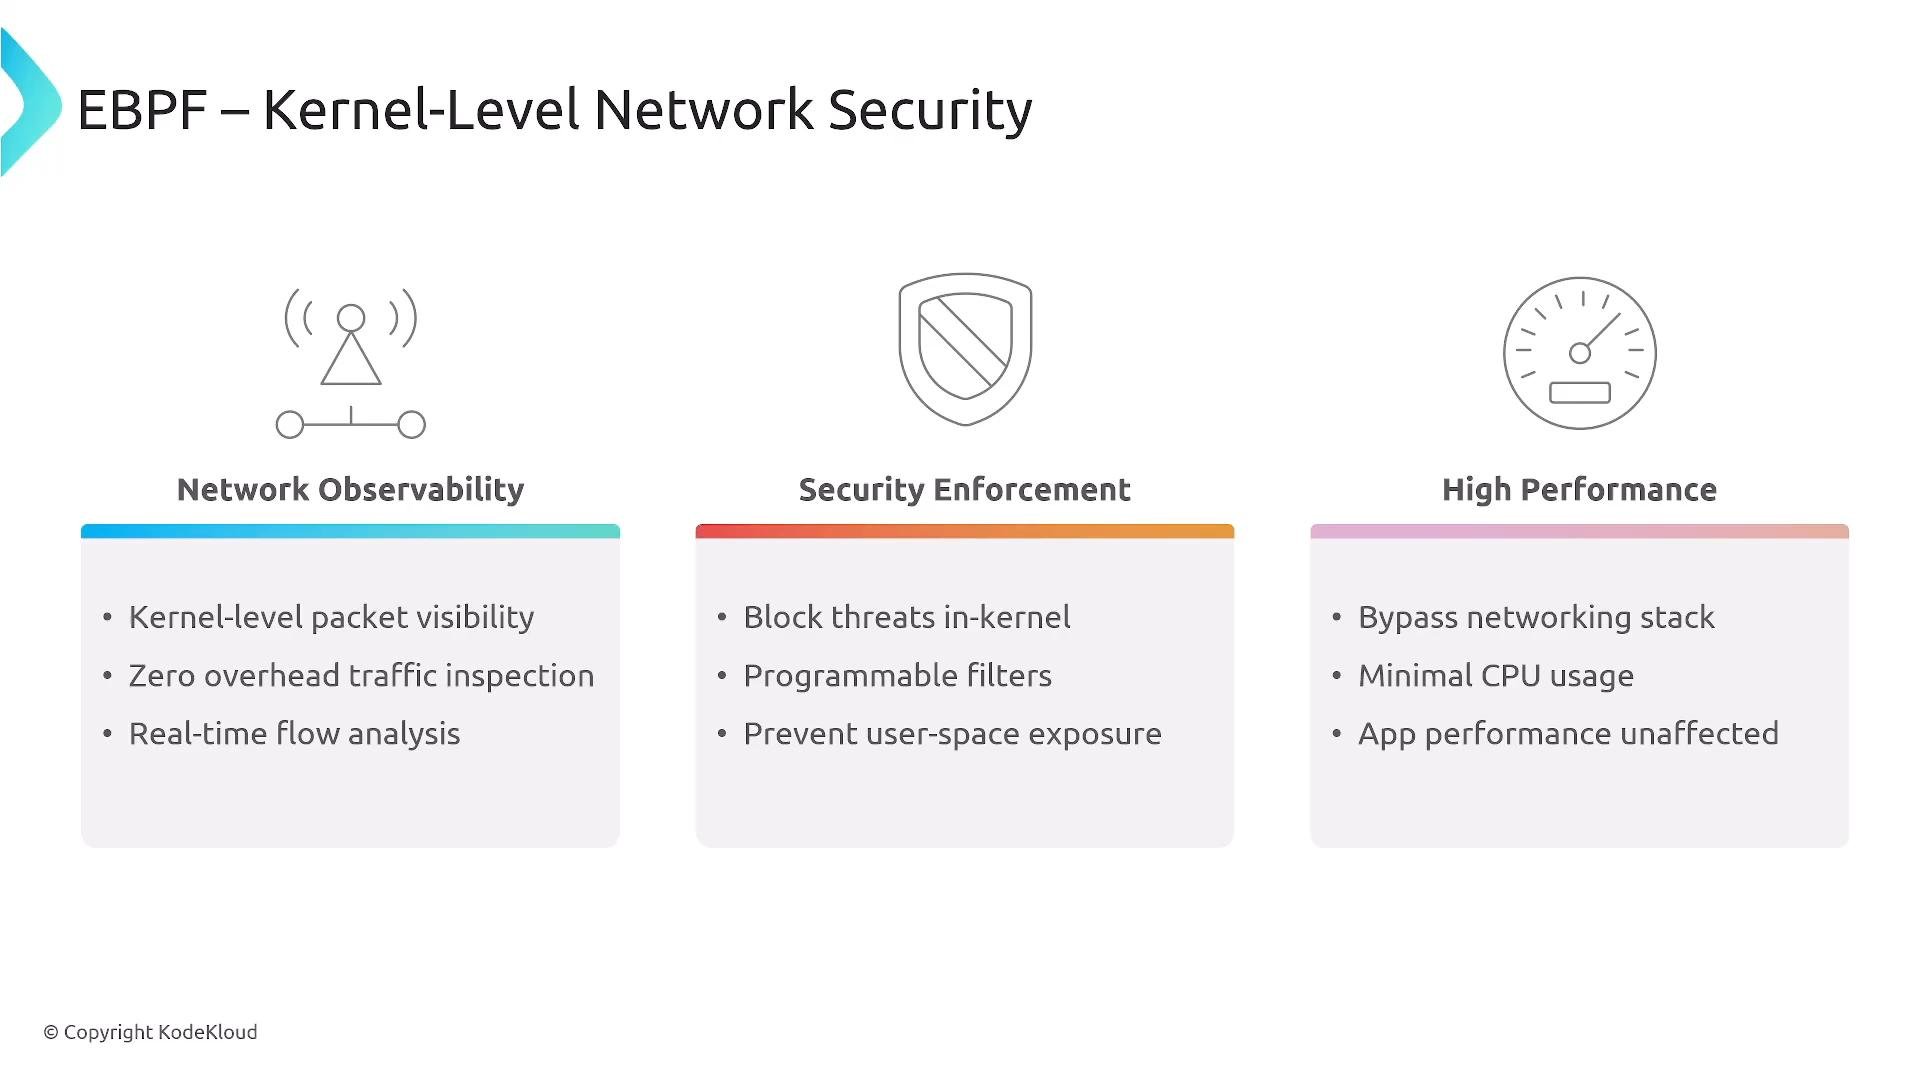
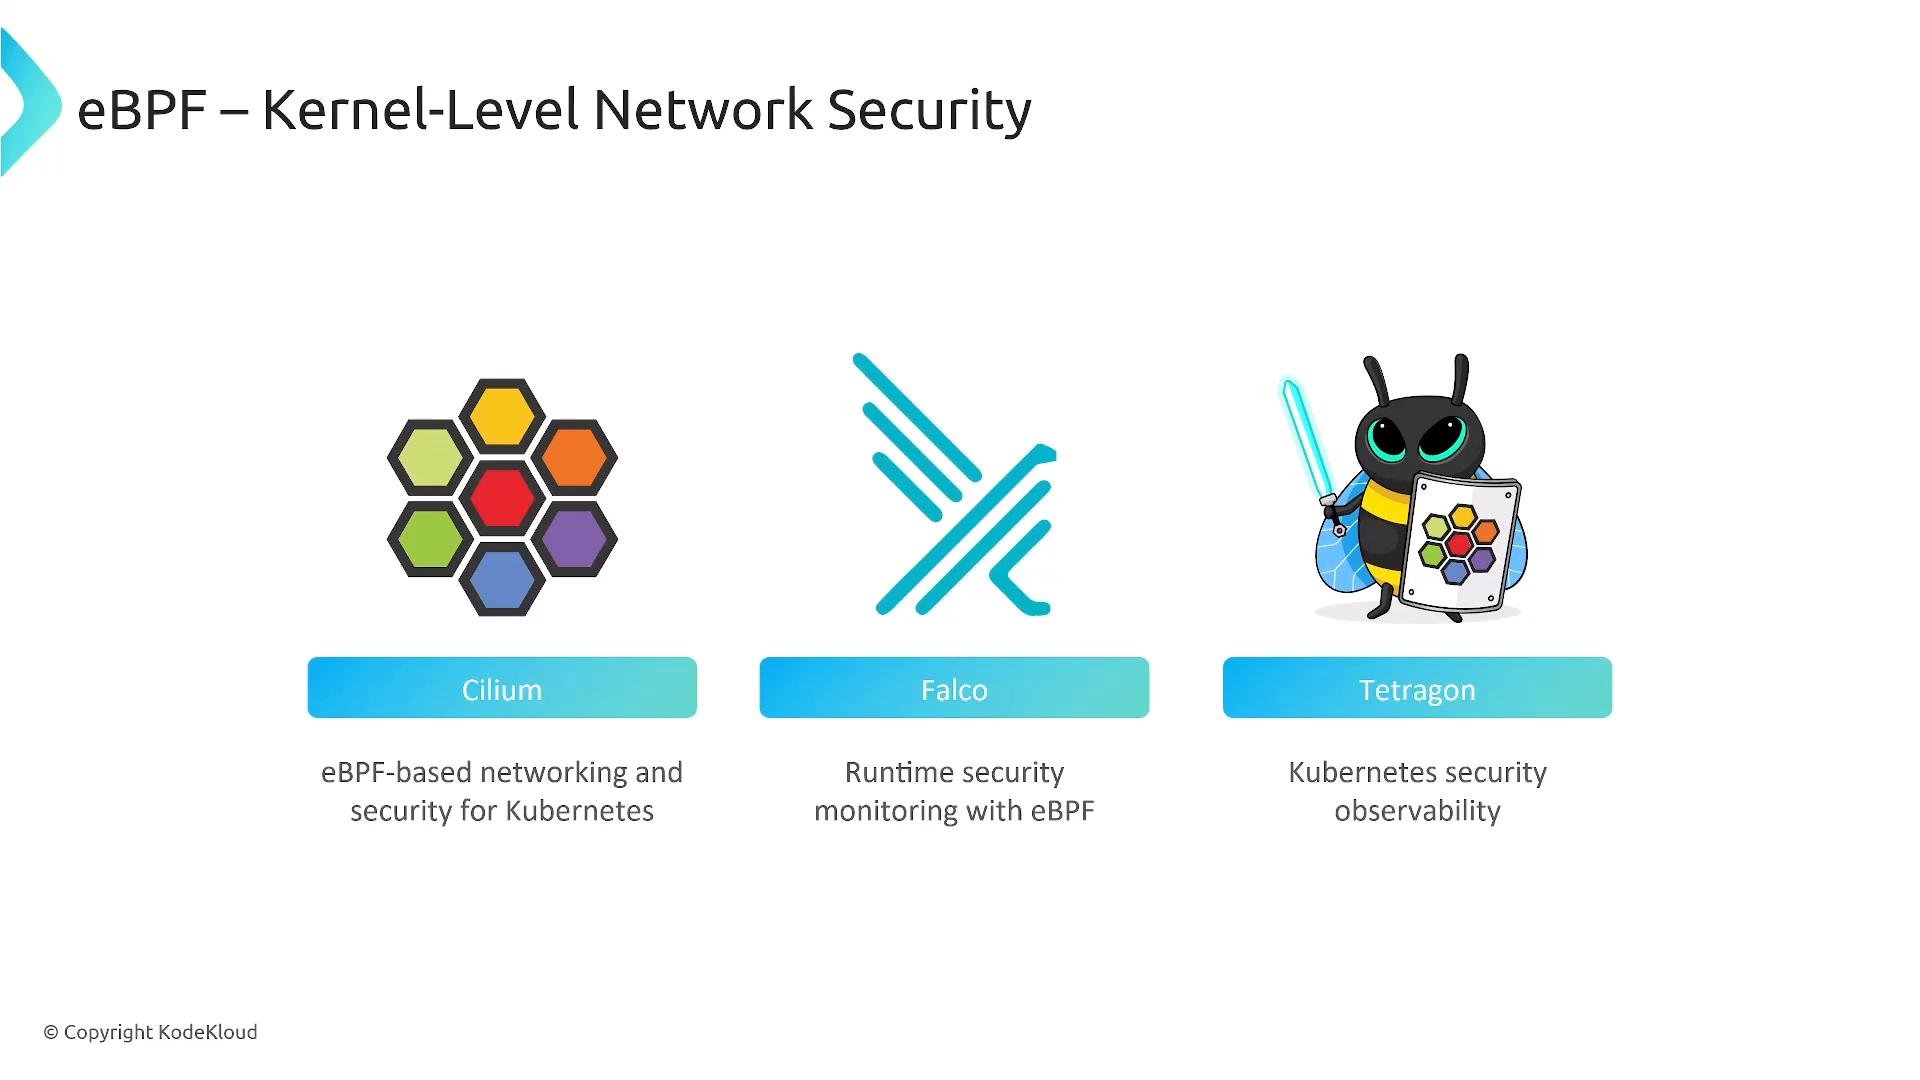
- Accelerates the data plane and provides deep packet/process visibility.
- Enables high-performance, kernel-level network policies that integrate with meshes.
- Does not manage certificate lifecycles — certificate management remains the mesh/control plane’s responsibility.
Case study: Sparkle Pony Ranch (SPR)
SPR’s plan is to deploy a mesh to provide mTLS, centralized policy-as-code, and to offload certificate management from application teams. Expected benefits include fewer incidents, better audit trails, and higher developer productivity.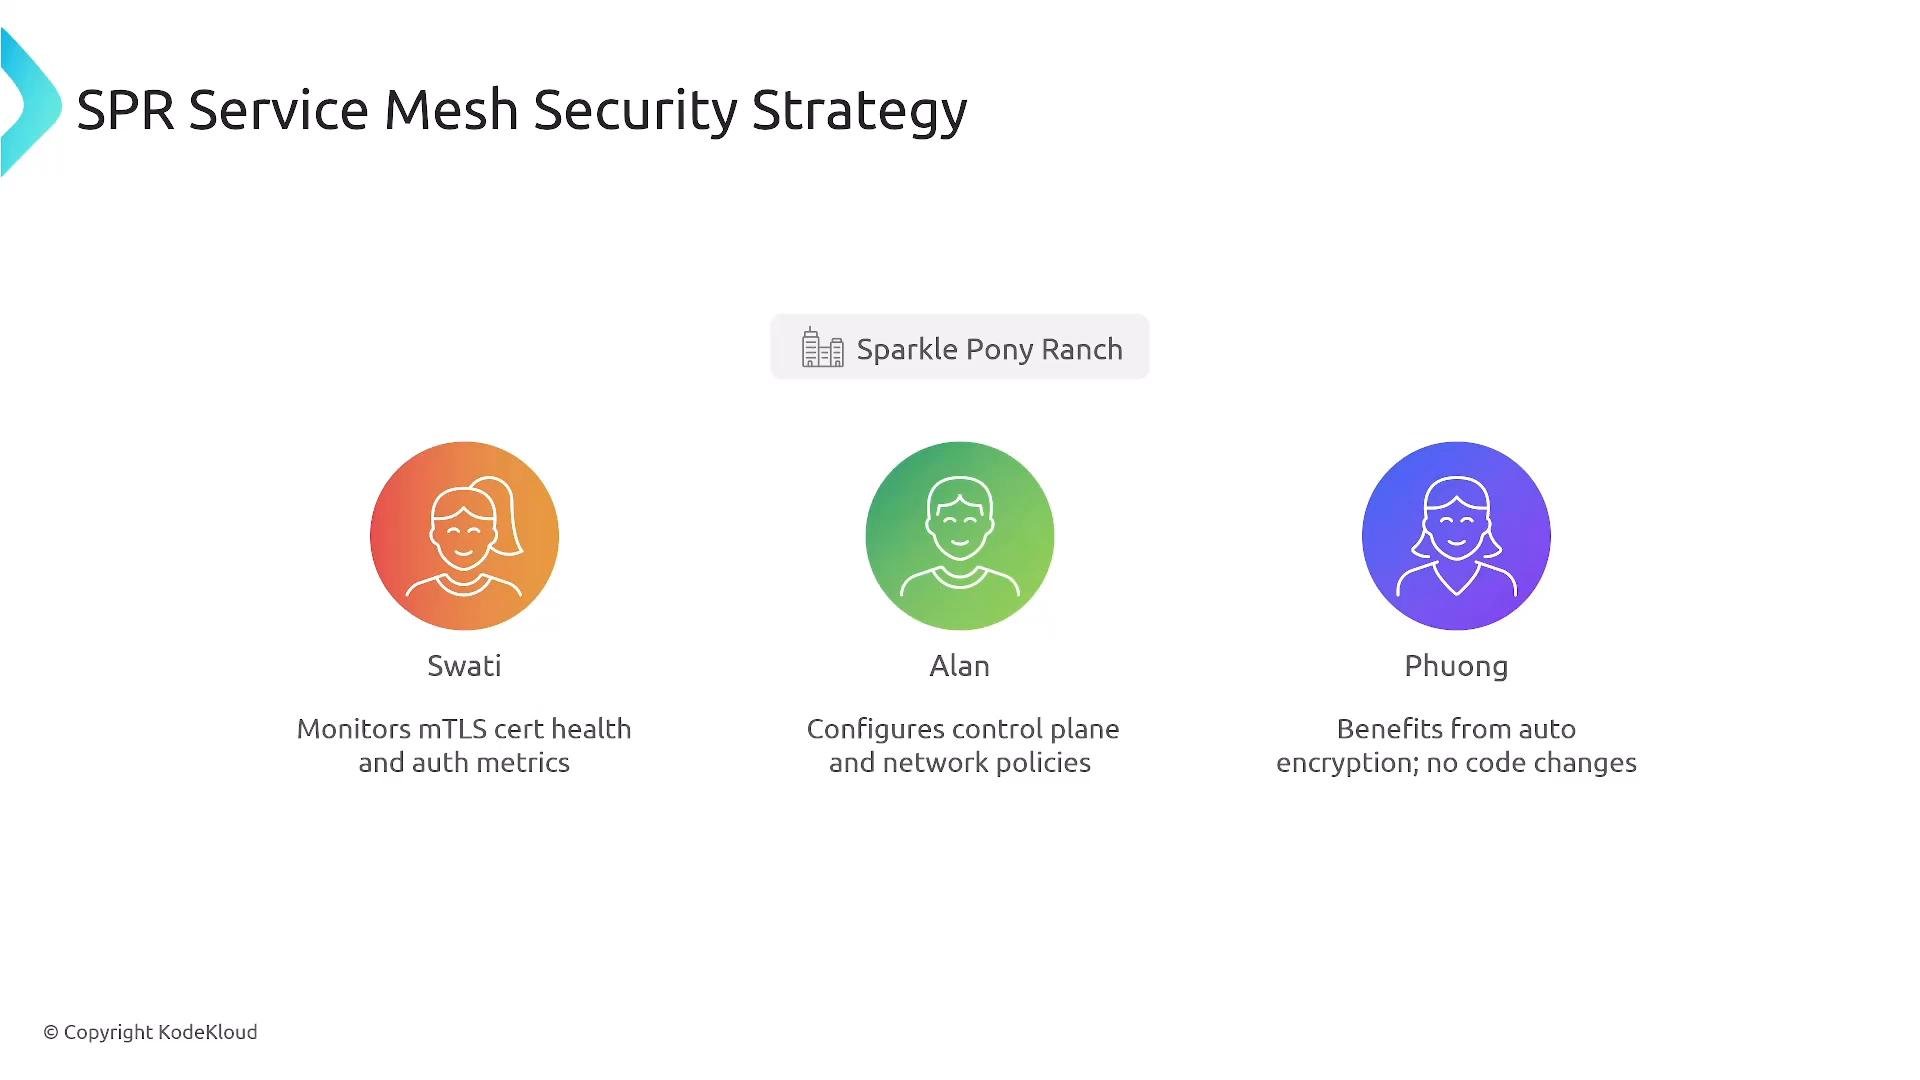
Summary — what to study for the exam
- Understand service mesh architecture (data plane vs control plane) and the value of sidecars or ambient modes.
- Know mTLS benefits: mutual authentication, encryption-in-transit, short-lived certs, and automated rotation.
- Be able to compare service mesh projects (Istio, Linkerd, Envoy) and eBPF tools (Cilium, Falco, Tetragon).
- Know L4 vs L7 trade-offs: performance vs application-aware control.
- Understand zero‑trust networking patterns: encrypt all traffic, authenticate services cryptographically, and use explicit allow policies.
The exam emphasizes conceptual understanding and trade-offs (service mesh vs eBPF, mTLS benefits, L4 vs L7) rather than deep implementation details. Focus on the purpose, capabilities, and typical use cases of each technology.