

- Tell Terraform which cloud or platform to talk to (provider block).
- Define the resources you want to create (resource blocks).
- Provide details about each resource (arguments inside resource blocks).
- The provider block tells Terraform how to communicate with Azure.
- The resource block describes the resource group and its required arguments (name and location).
For the AzureRM provider the
features {} block is required. It enables provider-default capabilities even when left empty.
Other helpful commands:
terraform validate to check syntax and terraform fmt to format files. The code describes desired infrastructure; Terraform commands perform the actual changes.
Provider block explained
The provider tells Terraform how to communicate with an external system (here, Azure Resource Manager).
provider "azurerm"selects the AzureRM provider plugin.features {}is required by the AzureRM provider even when left empty.- You can set
subscription_iddirectly, or supply it via environment variables (for example,ARM_SUBSCRIPTION_ID) or variables for cleaner separation of secrets and configuration.
<PROVIDER_RESOURCE_TYPE>— provider-specific resource type (e.g.,azurerm_storage_account).<LOCAL_NAME>— logical name used inside Terraform for referencing this resource (not seen by Azure).- Inside the block: key-value arguments describe how to create or configure the resource.
- Resource group:
nameandlocationare required. - Storage account:
name,resource_group_name,location,account_tier, andaccount_replication_typeare required. Many other settings (network rules, tags, etc.) are optional.
- Ensure Terraform is installed and available:
terraform -version. - Ensure you are logged into Azure CLI and pointing at a subscription:
az account show. - Consider installing the HashiCorp Terraform extension for VS Code for syntax highlighting and IntelliSense: https://marketplace.visualstudio.com/items?itemName=HashiCorp.terraform
az account show output (truncated)
- Create a folder for your code, e.g.,
first-code. - Start with a
main.tffile. For larger projects split code into multiple.tffiles and modules.
main.tf file with the following:
terraform init output (truncated)
terraform initdownloads provider binaries into the local.terraformdirectory.- The provider binary downloaded depends on your OS/architecture (e.g.,
darwin_arm64,windows_amd64).
terraform plan converts your HCL into an execution plan and shows what will be added, changed, or destroyed — without making changes.
Apply the changes
terraform apply output (truncated)
terraform.tfstate in the working directory). This file is how Terraform tracks resources it manages.
The state file may contain sensitive information (IDs, attributes, secrets). Do not commit
terraform.tfstate to version control. For teams, use a remote backend (for example, Azure Storage, S3, or Terraform Cloud) to store state securely and enable state locking.terraform plan or terraform apply. If the portal change is not reflected in your HCL, Terraform will attempt to reconcile the real state to match your code — which may overwrite or remove the manual change.
Example: adding a tag via Azure Portal
You can add a tag to the resource group in the portal. The Portal shows the edit UI:
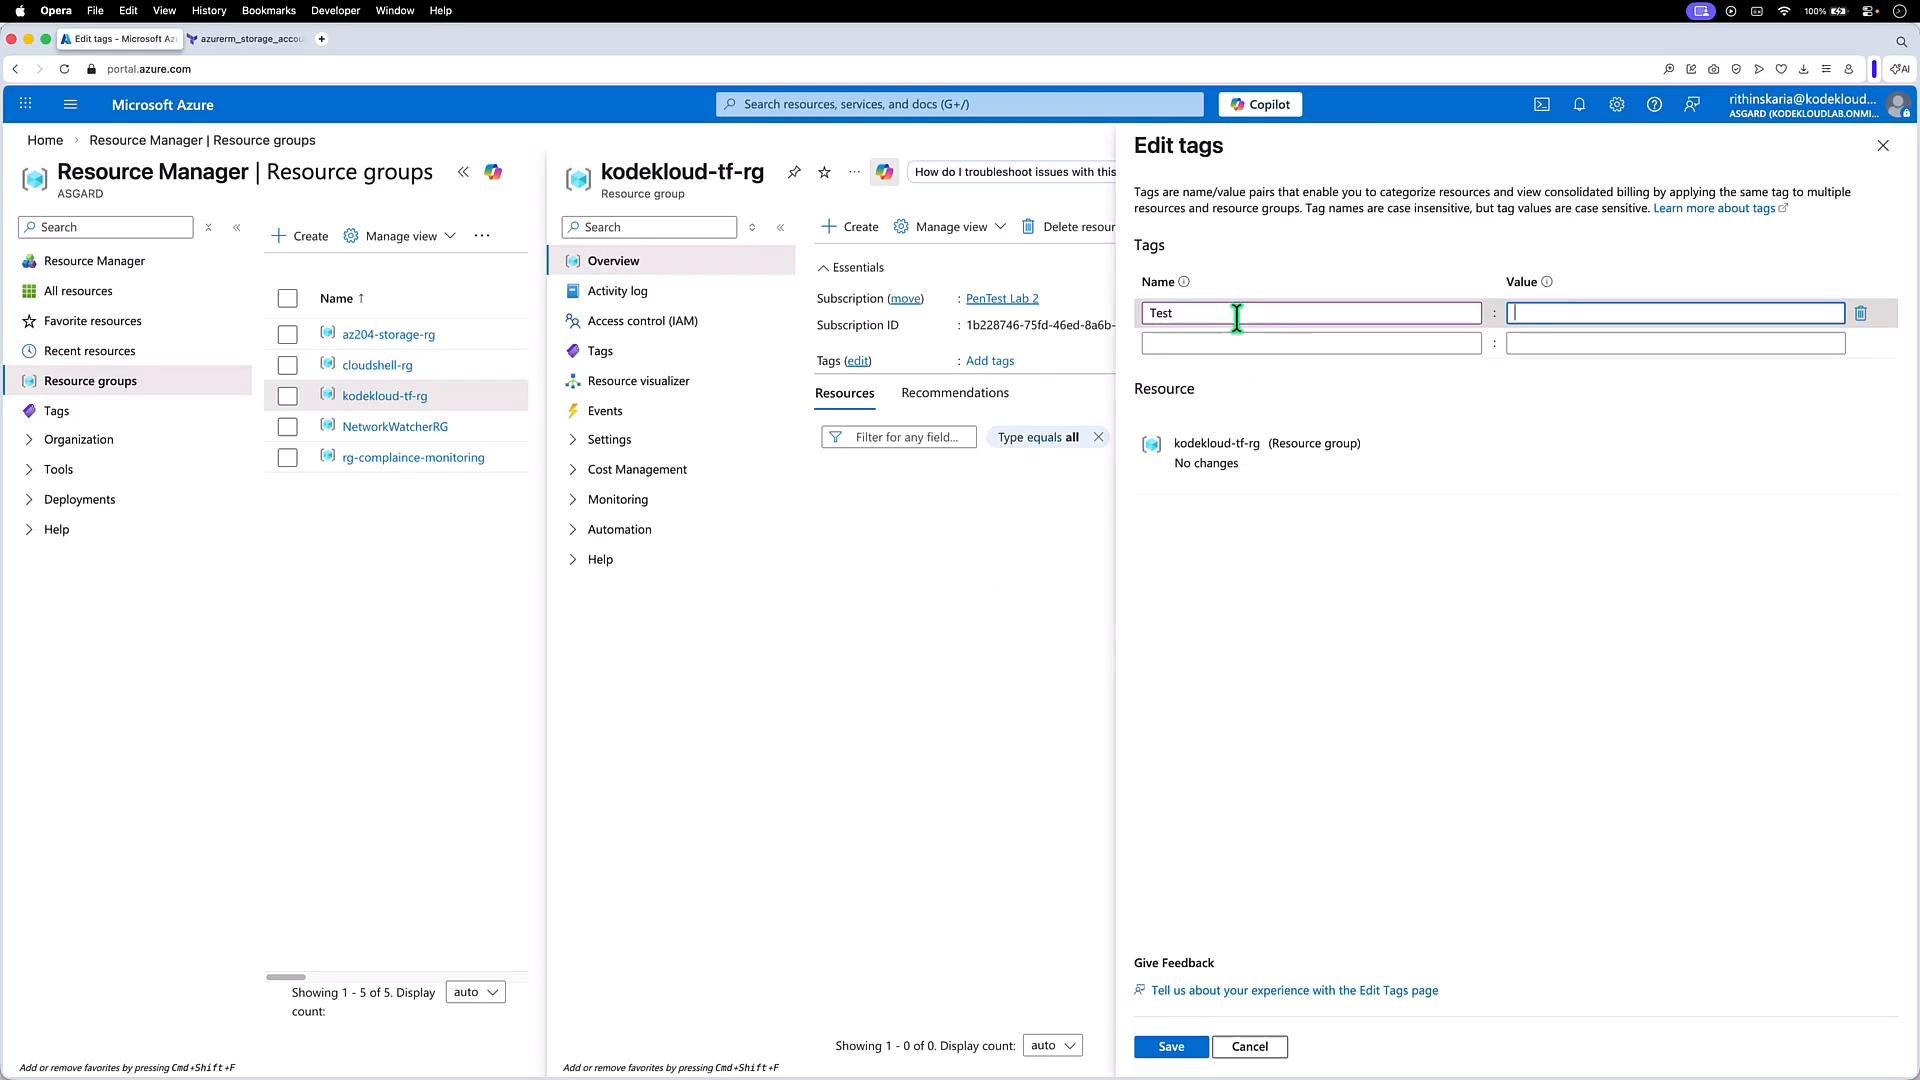
terraform plan, Terraform will show changes required to make the resource match the configuration in your HCL (for example, it may propose to remove or change that tag). This behavior demonstrates Terraform’s desired-state model: Terraform will always aim to make the real infrastructure match the declared code.
Wrap-up
You now know the basic HCL pattern (provider → resource → arguments) and the essential Terraform workflow (init, plan, apply). Next topics to continue learning:
- Variables and outputs (parameterize your configurations)
- State backends and locking (secure, shareable state)
- Modules (reusable infrastructure components)
- Best practices for project structure and secrets management
- Terraform Registry — Azure Provider: https://registry.terraform.io/providers/hashicorp/azurerm/latest
- HashiCorp Terraform extension for VS Code: https://marketplace.visualstudio.com/items?itemName=HashiCorp.terraform
- Azure CLI documentation: https://docs.microsoft.com/cli/azure/overview