

lifecycle meta-argument — specifically ignore_changes — and how it lets you allow out-of-band updates (for example, manual tag edits in the AWS Console) without Terraform attempting to revert them. You’ll learn the minimal Terraform configuration used for the demo, how Terraform detects drift, and how adding ignore_changes changes Terraform’s behavior.
This demo uses AWS S3 resources. You should have the AWS provider configured and credentials available (for example via
AWS_ACCESS_KEY_ID / AWS_SECRET_ACCESS_KEY or an AWS profile). See the Terraform docs for provider setup: https://developer.hashicorp.com/terraform/providers/awsResources in main.tf
The examplemain.tf below creates an S3 bucket plus ownership controls and an ACL. This is intentionally minimal so you can focus on lifecycle behavior.
yes. The apply will create the resources and produce output similar to:
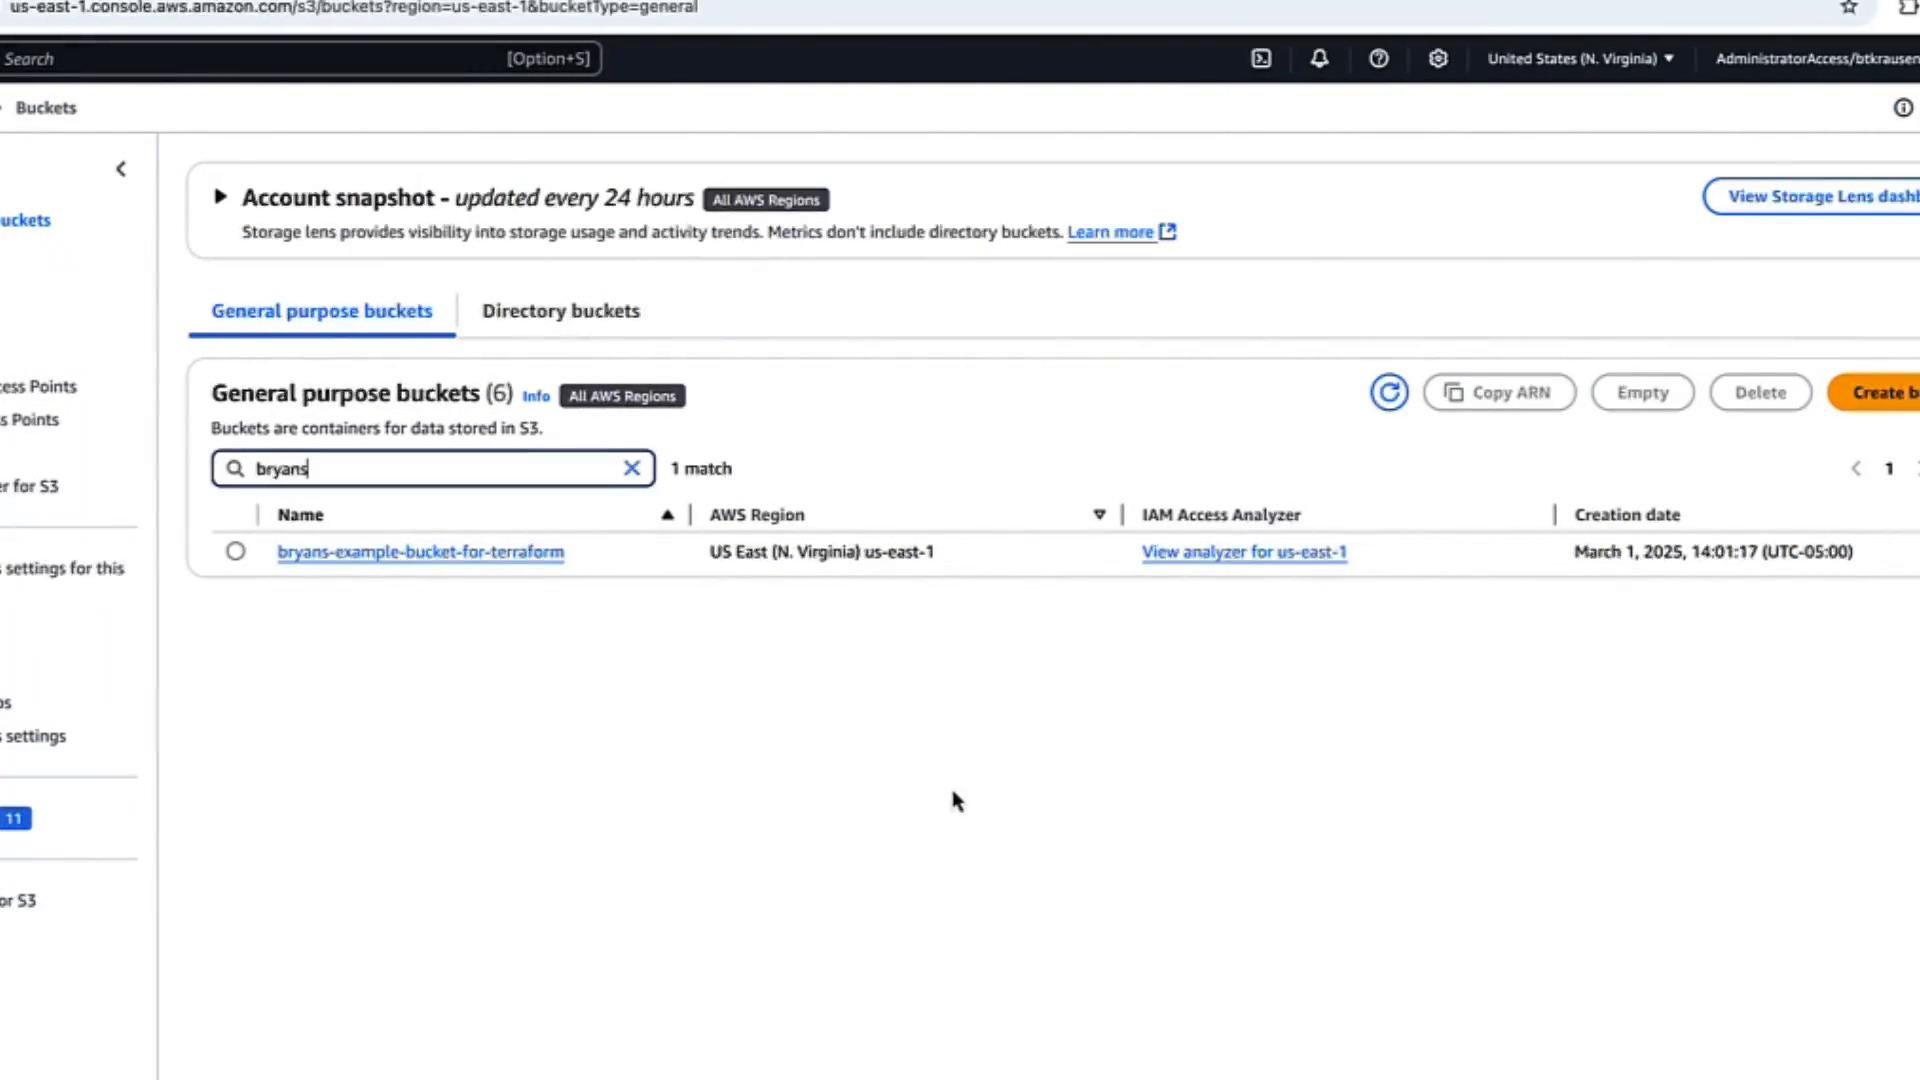
Scenario: Out-of-band tag change
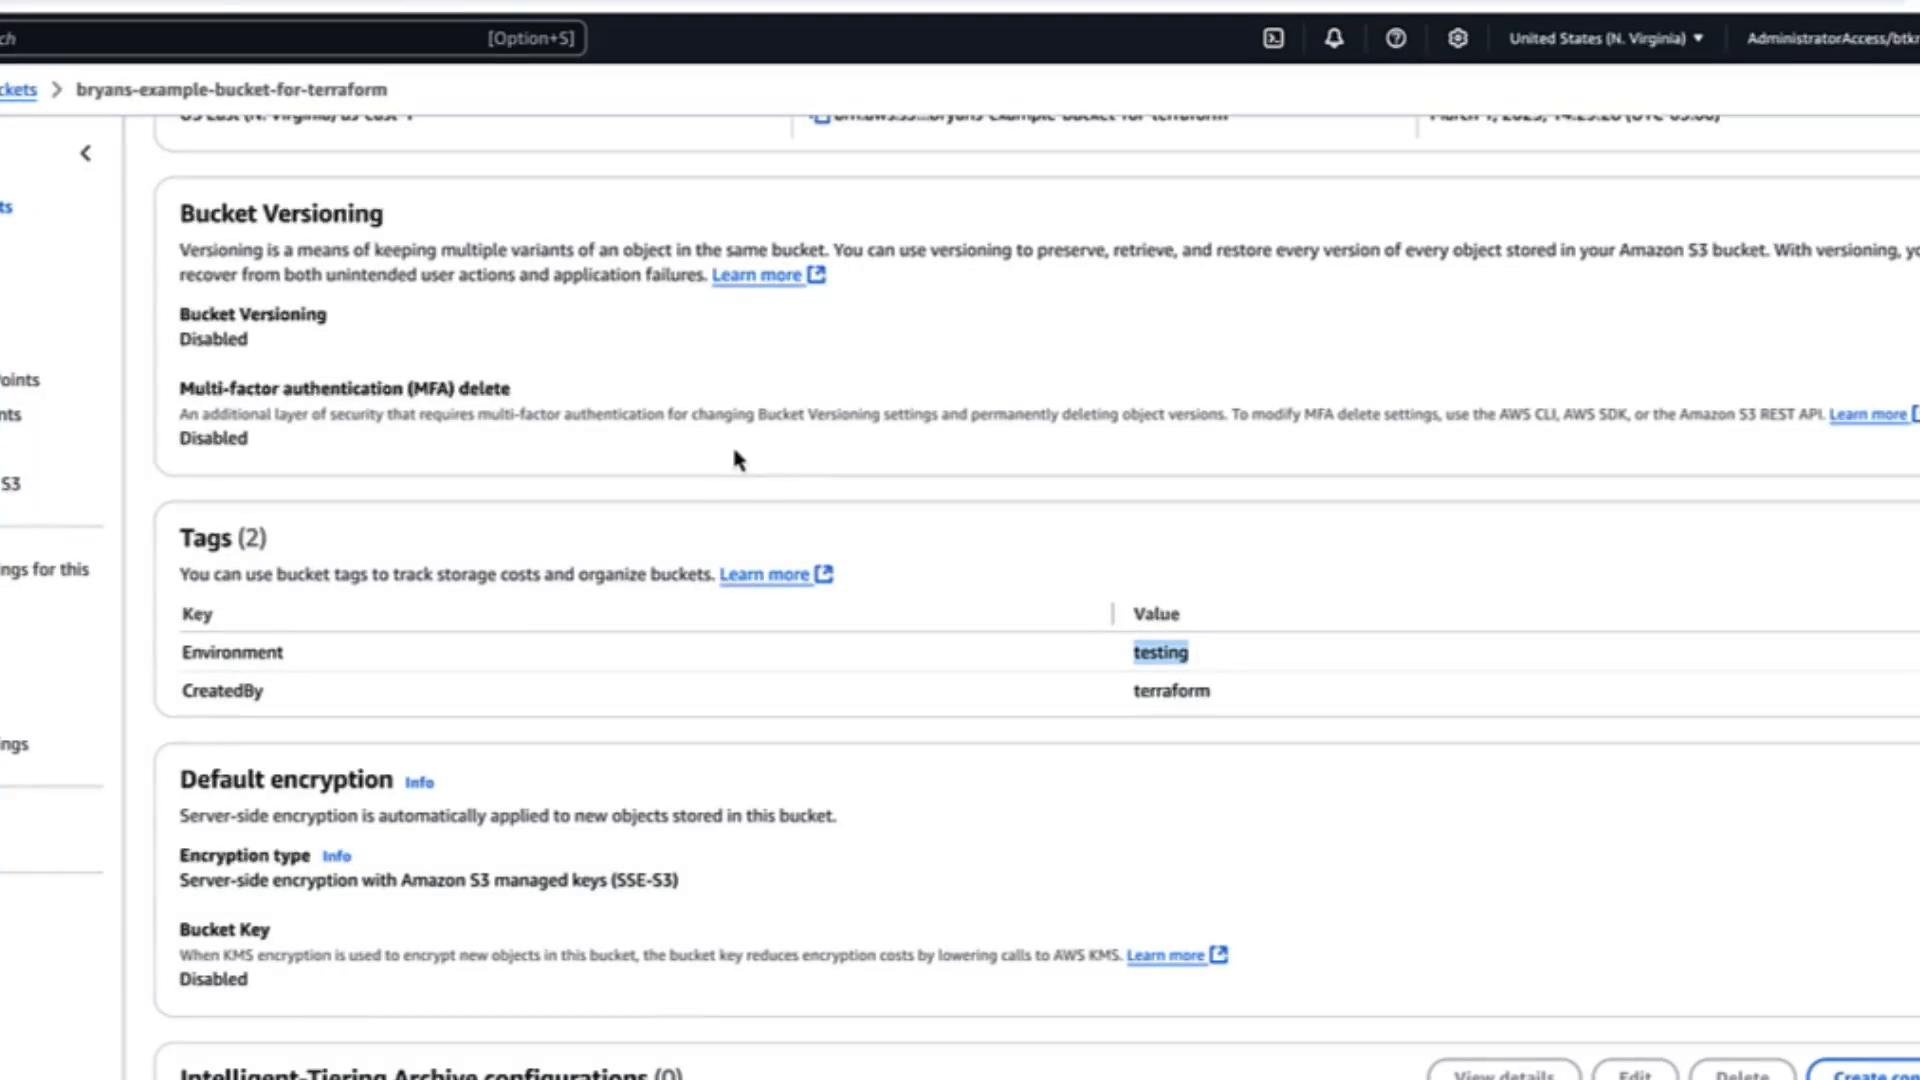
If you open the bucket in the AWS Console under Properties, you’ll see the tags created by Terraform:Environment = productionCreatedBy = terraform
Environment from production to testing. This is an out-of-band change (i.e., not made through Terraform).
To see how Terraform reacts, run a refresh/plan:
Environment = production, Terraform plans to revert the manual change back to production.
Allowing out-of-band edits with lifecycle.ignore_changes
If you want to permit manual updates to specific attributes (for example, user-modified tags in the console) and prevent Terraform from reverting them, add alifecycle block with ignore_changes to the resource. Update the aws_s3_bucket resource like this:
tags attribute when refreshing state and planning changes.
Run terraform plan again:
Environment: testing, Terraform will not attempt to revert it because ignore_changes tells Terraform to stop reconciling the tags attribute:
Use
ignore_changes sparingly. Ignoring changes causes Terraform to stop reconciling that attribute, which can lead to drift between your configuration and real infrastructure. Prefer allowing Terraform to manage attributes unless you have a clear operational need for out-of-band edits.When to use ignore_changes
Summary
- By default, Terraform detects drift between configuration and real infrastructure and will plan to reconcile differences.
- The
lifecyclemeta-argument withignore_changesallows you to instruct Terraform to ignore specific attribute changes (for example,tags) so out-of-band updates are not reverted. - Use
ignore_changesintentionally, document why certain attributes are ignored, and minimize its scope to avoid unexpected drift.
- Terraform lifecycle meta-arguments: https://developer.hashicorp.com/terraform/language/meta-arguments/lifecycle
- Terraform CLI
plan: https://developer.hashicorp.com/terraform/cli/commands/plan - AWS S3 documentation: https://docs.aws.amazon.com/s3/
lifecycle meta-argument to manage resource behavior.