

- Prerequisites: Docker (optional, for building images) and an AWS account with permissions to create ECS, IAM, VPC, and security group resources.
- Public images used in this demo (available on Docker Hub):
KodeKloud/ECS-Project1KodeKloud/ECS-Project2
Application (Project 1)
Project 1 is a minimal Node.js + Express app that serves a static HTML page at the root path. Example view fileindex.ejs:
index.js:
Important: this app listens on container port
3000. When creating the container definition in ECS/Fargate, expose container port 3000. With Fargate (awsvpc network mode) ECS manages the host mapping and the container port is used to reach the application.1) Quick start: use the ECS wizard
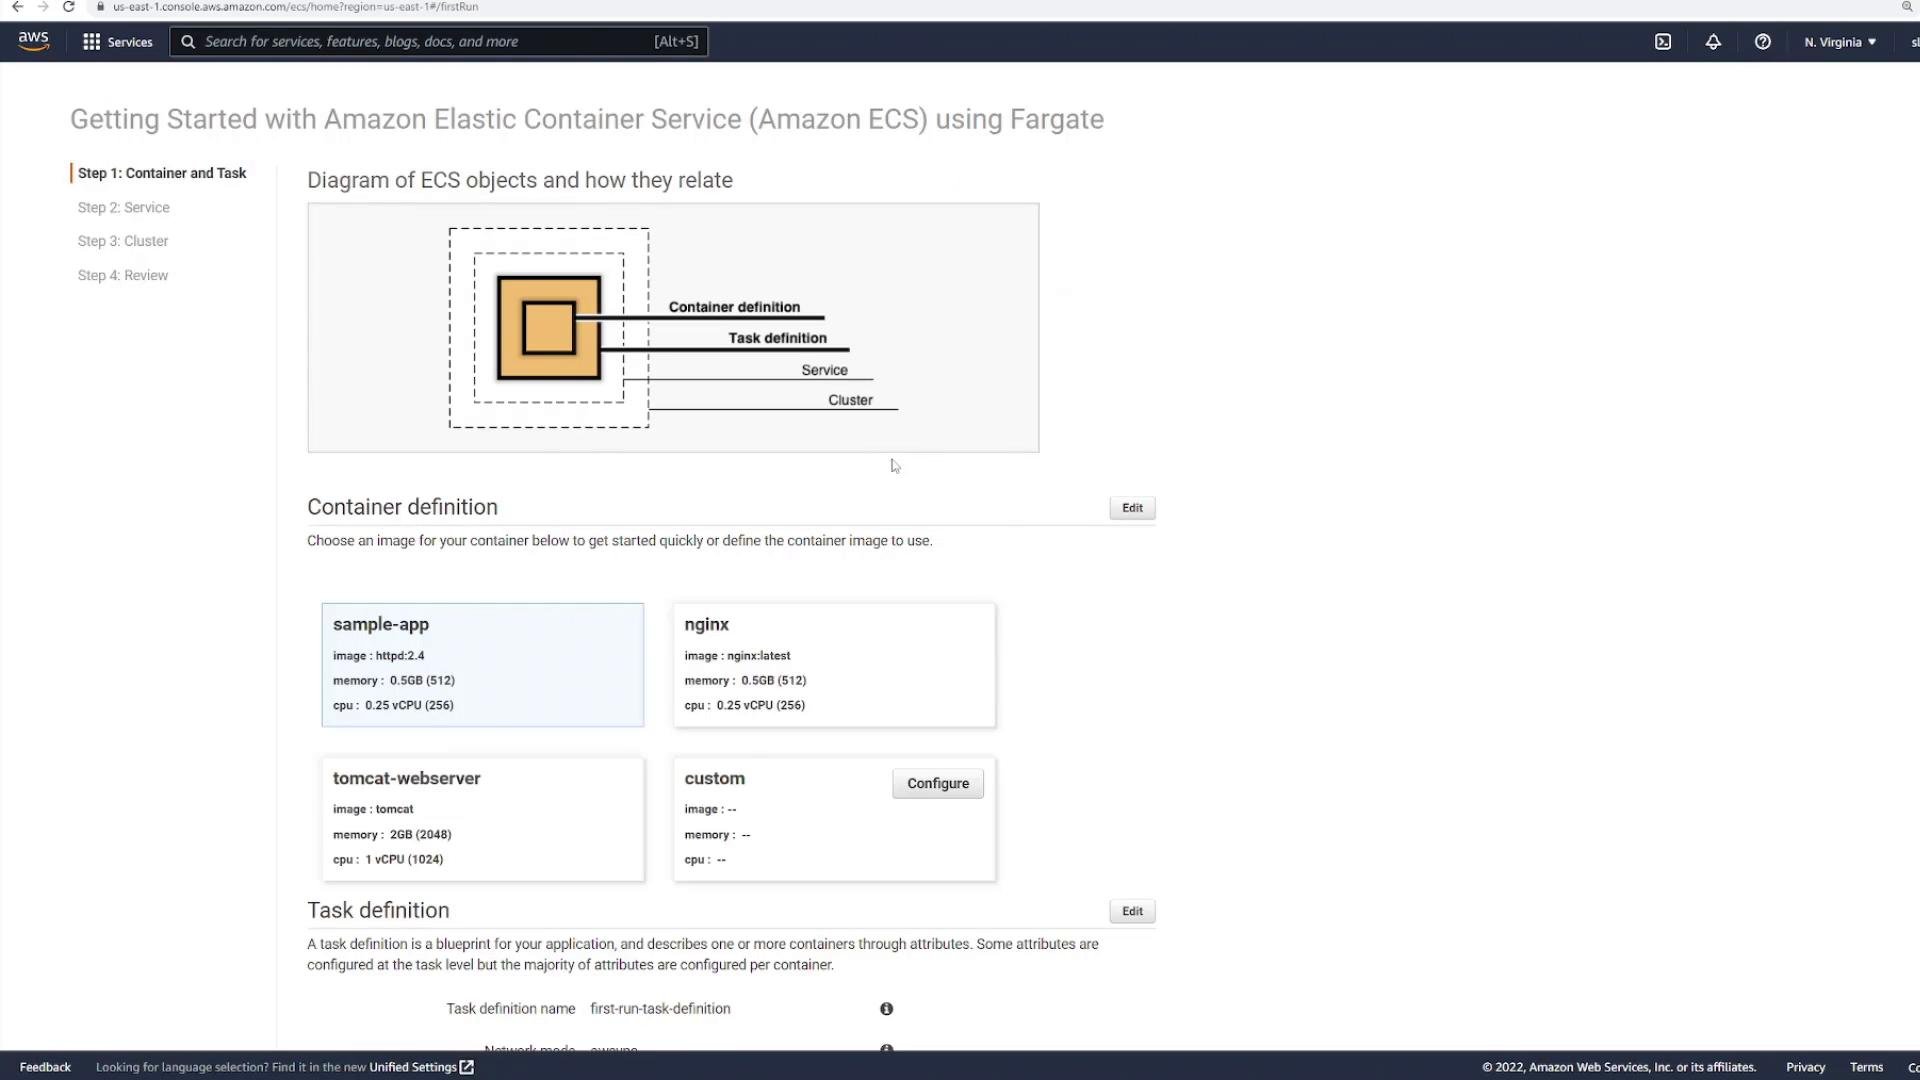
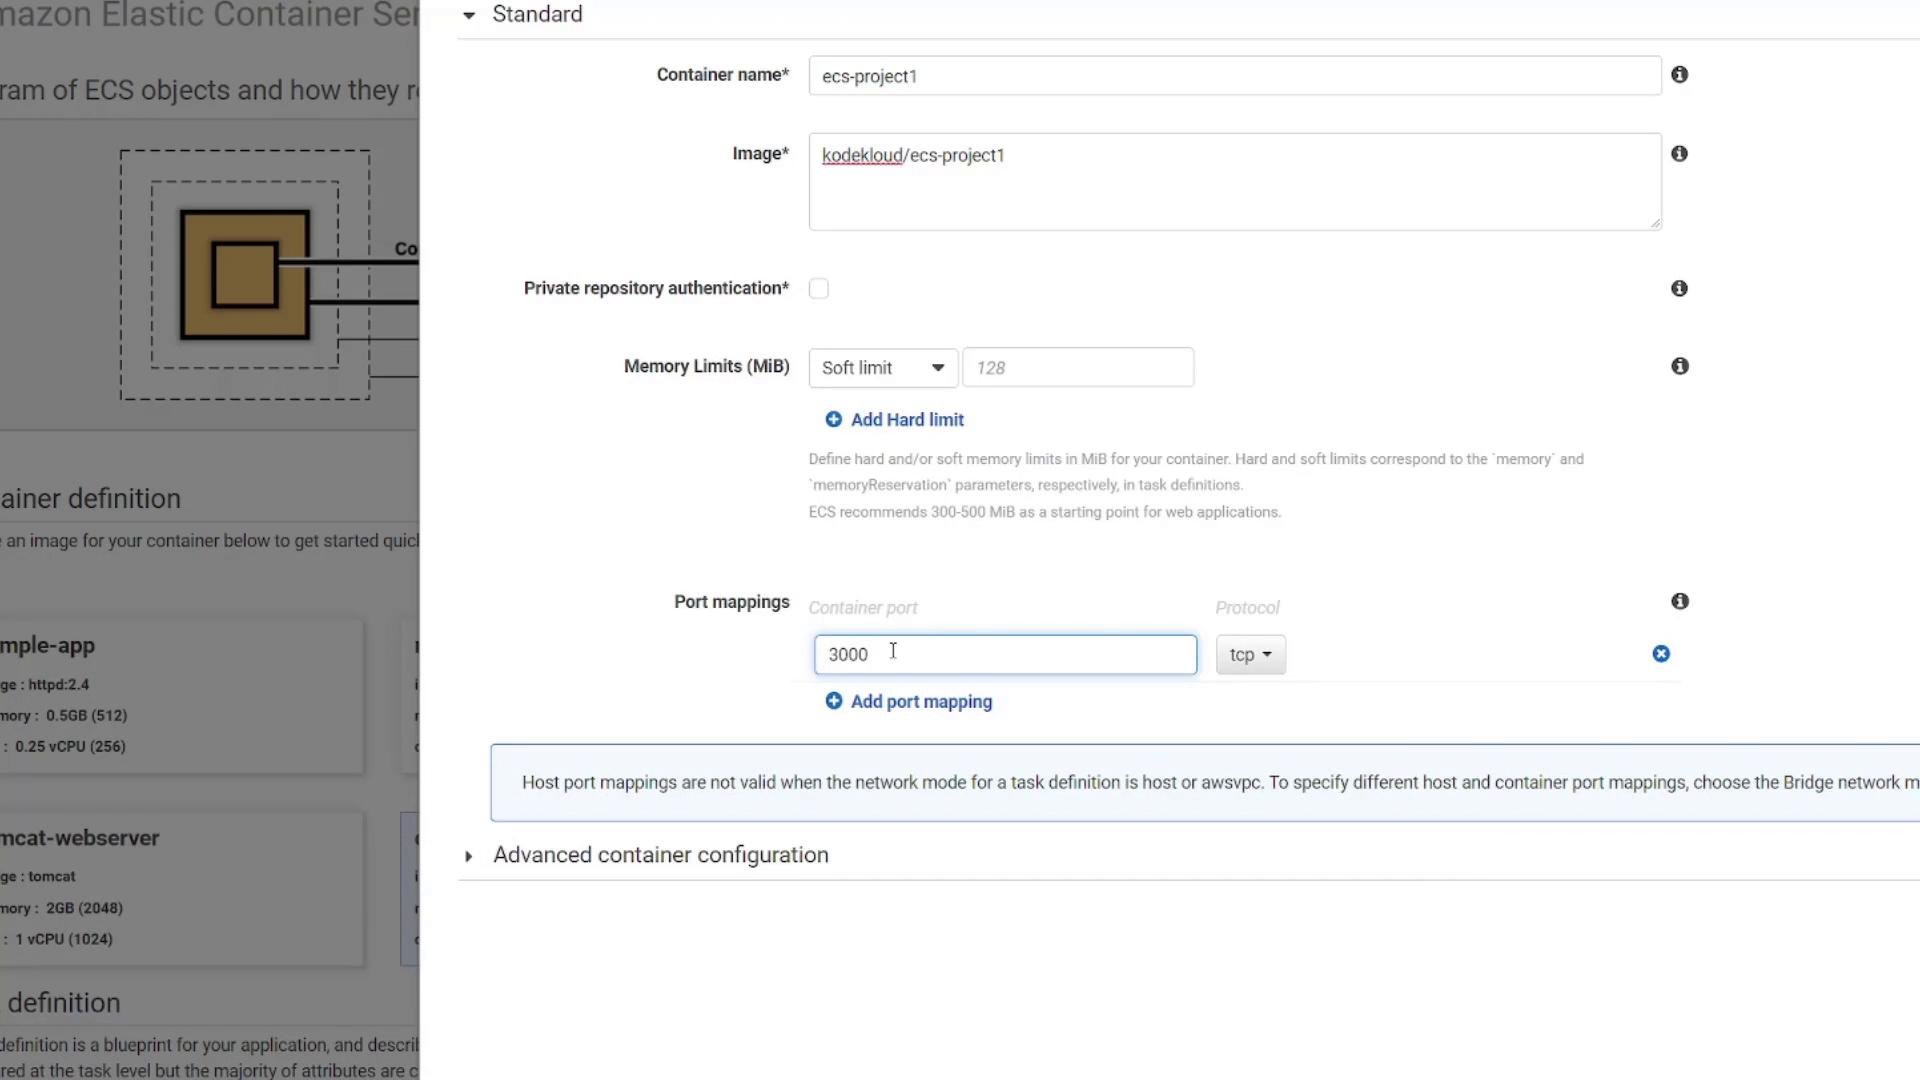
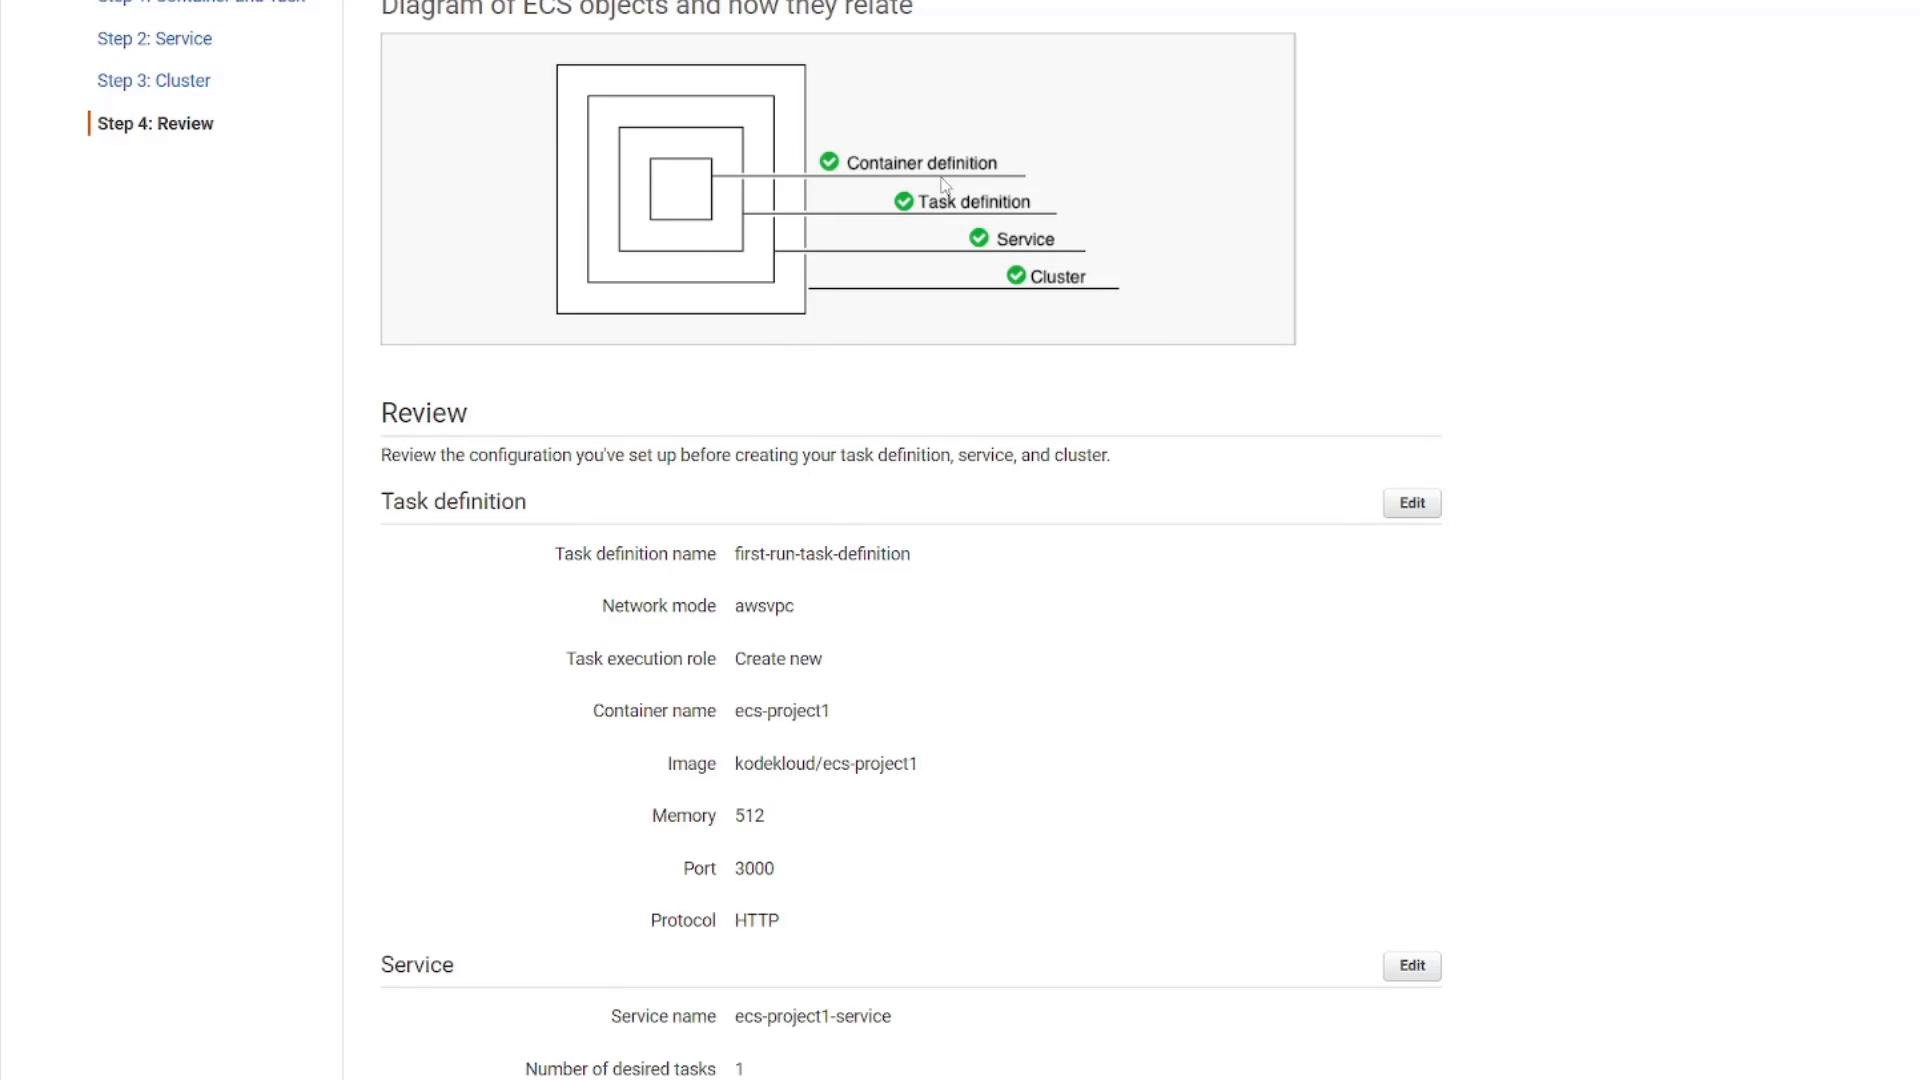
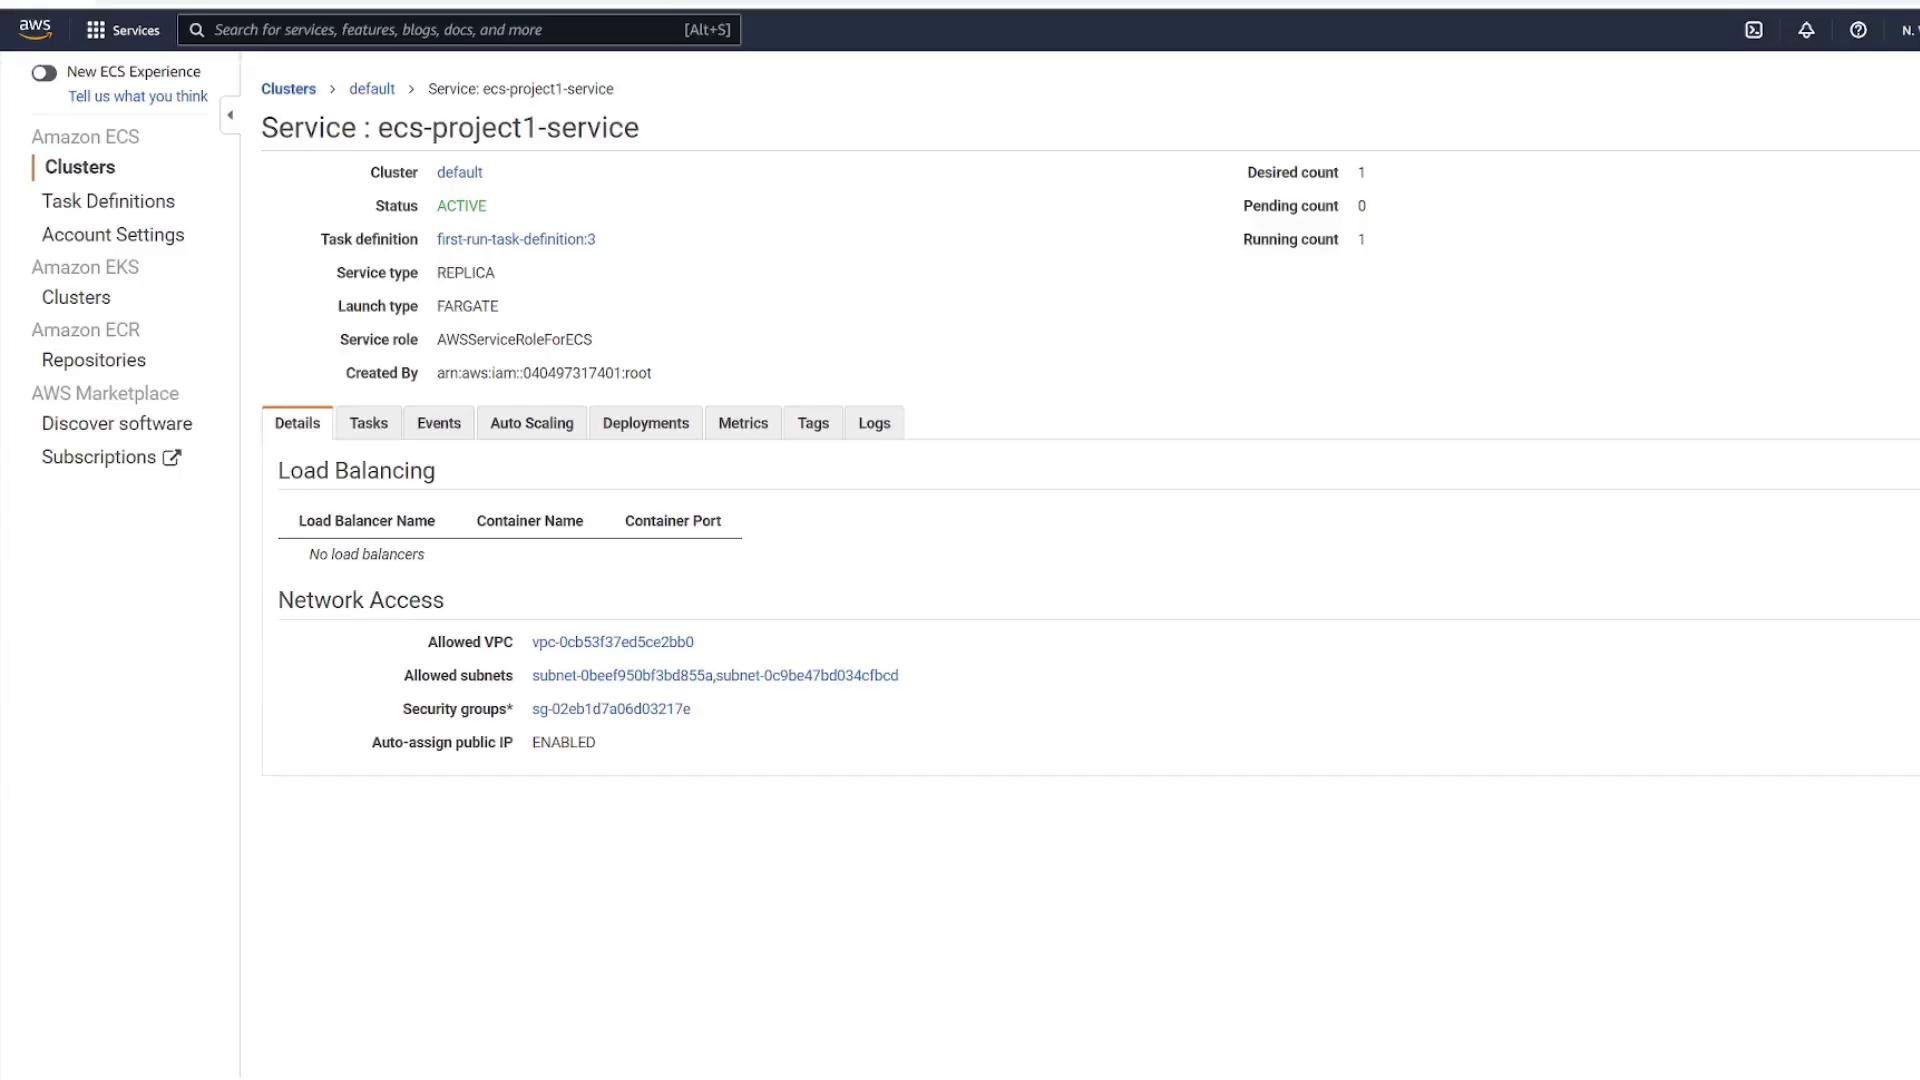
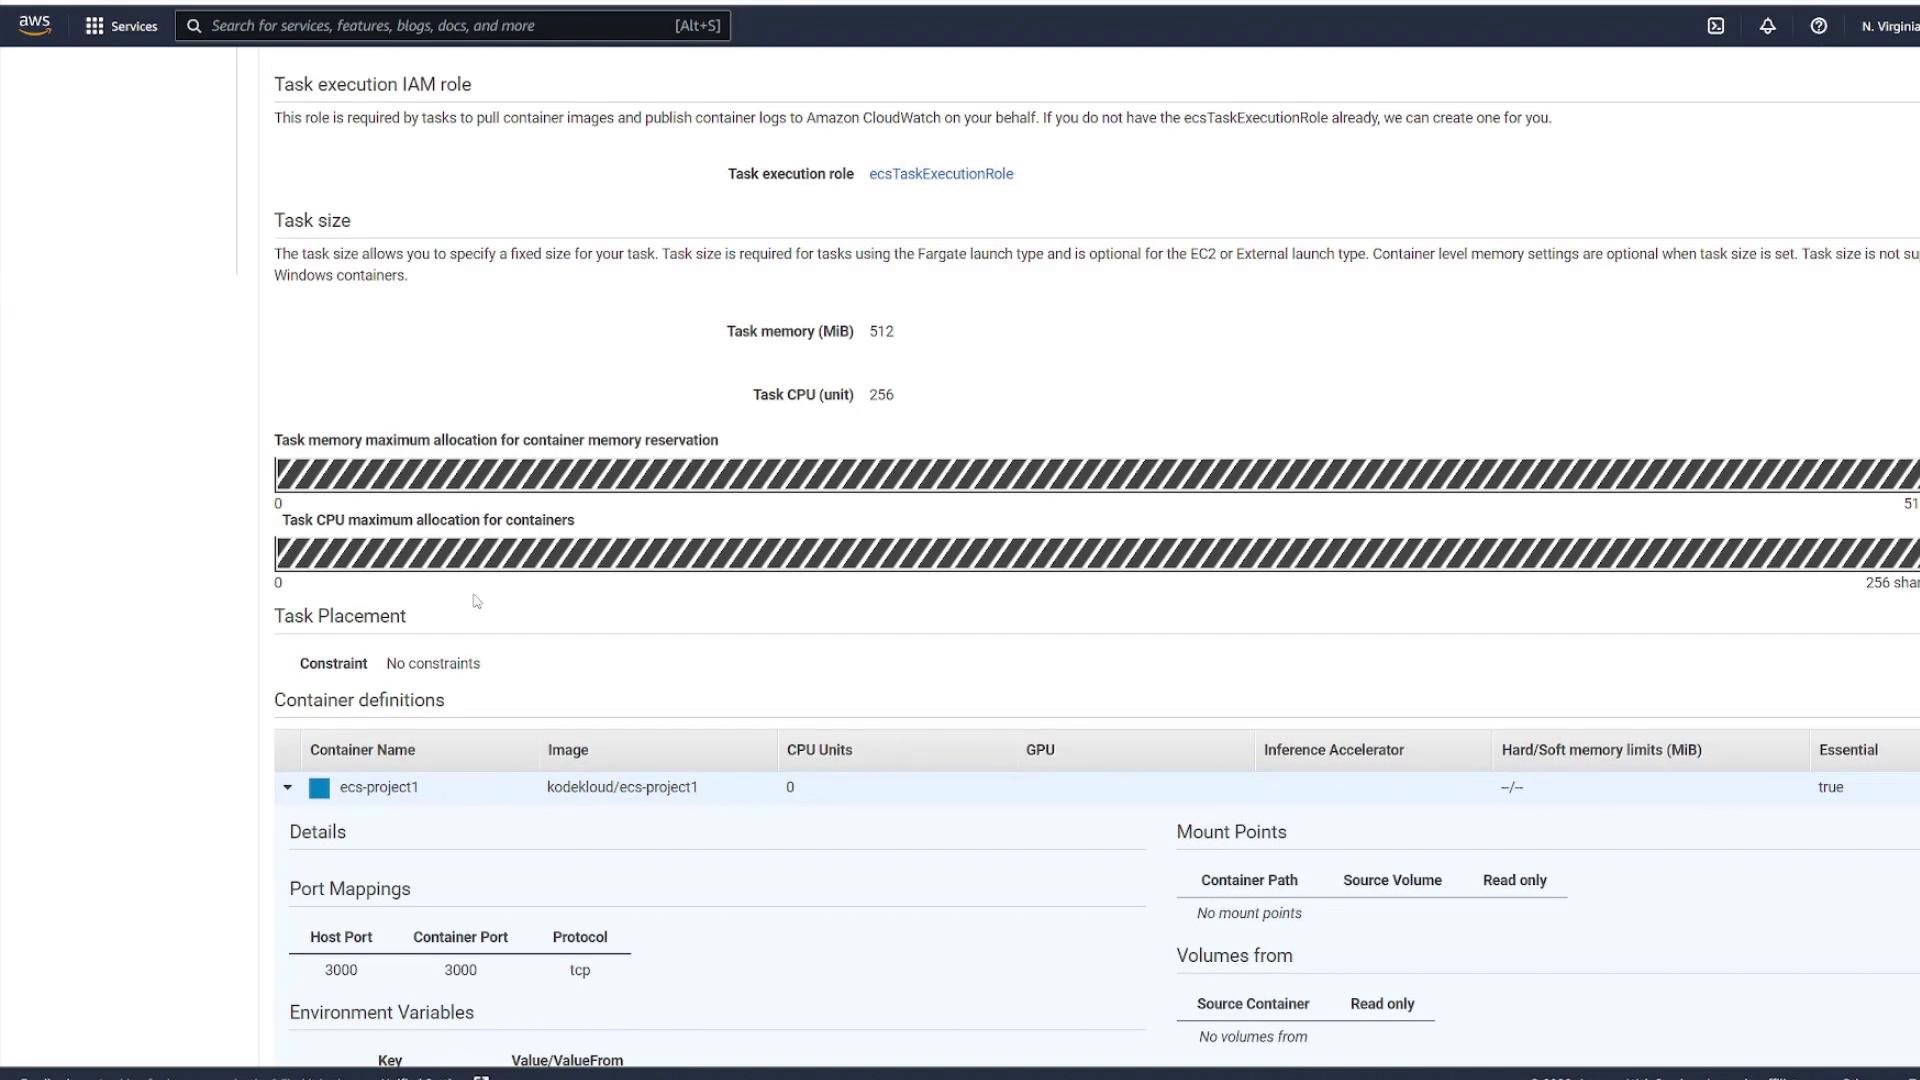
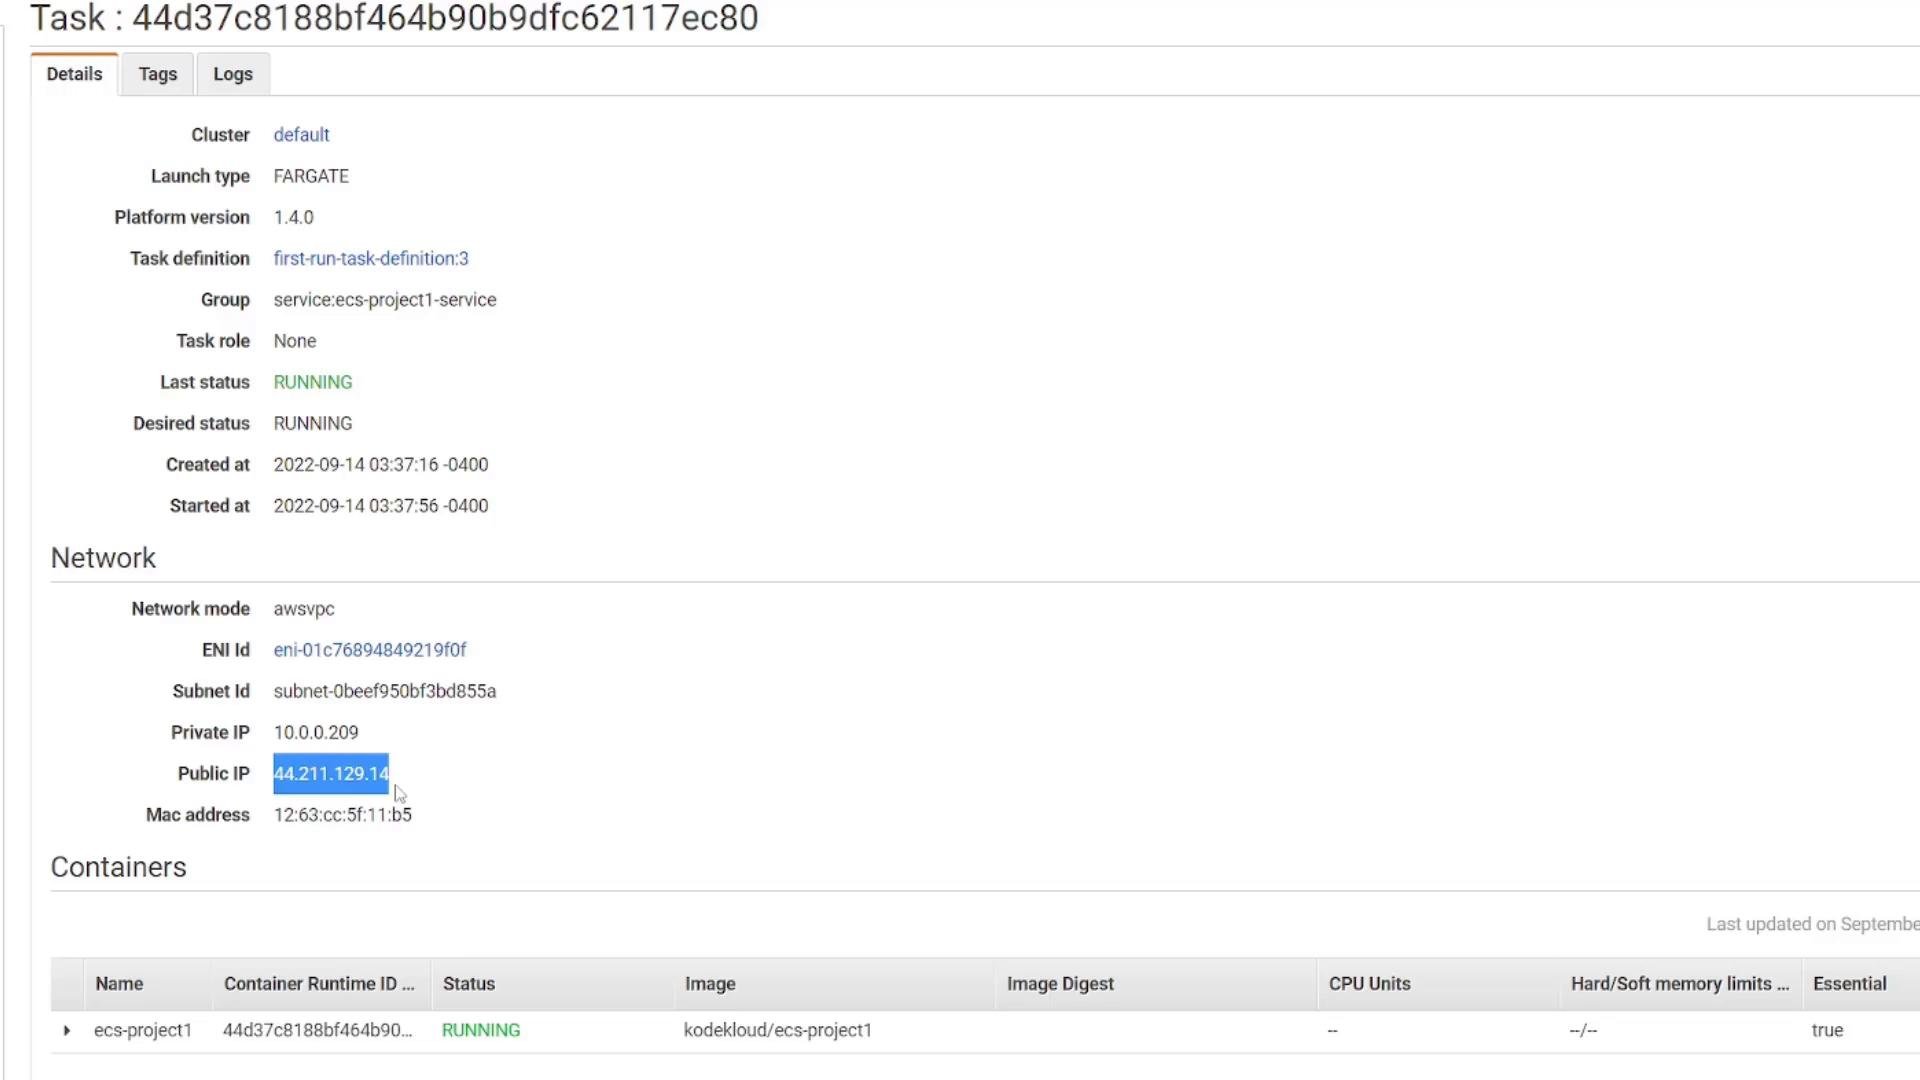
Open the AWS Console and search for “ECS” or go to the Amazon Elastic Container Service page. If this is your first time, the ECS quick start wizard can create a task definition, cluster, VPC, subnets, and a service for you. We’ll run the wizard once to inspect its defaults, then delete the created resources and perform the same steps manually. In the wizard choose a Custom container and provide values similar to:- Container name:
ecs-project1 - Image:
KodeKloud/ECS-Project1 - Memory limits: optional/sensible defaults
- Port mappings: container port
3000(TCP)
- Container port:
3000(TCP) - Image:
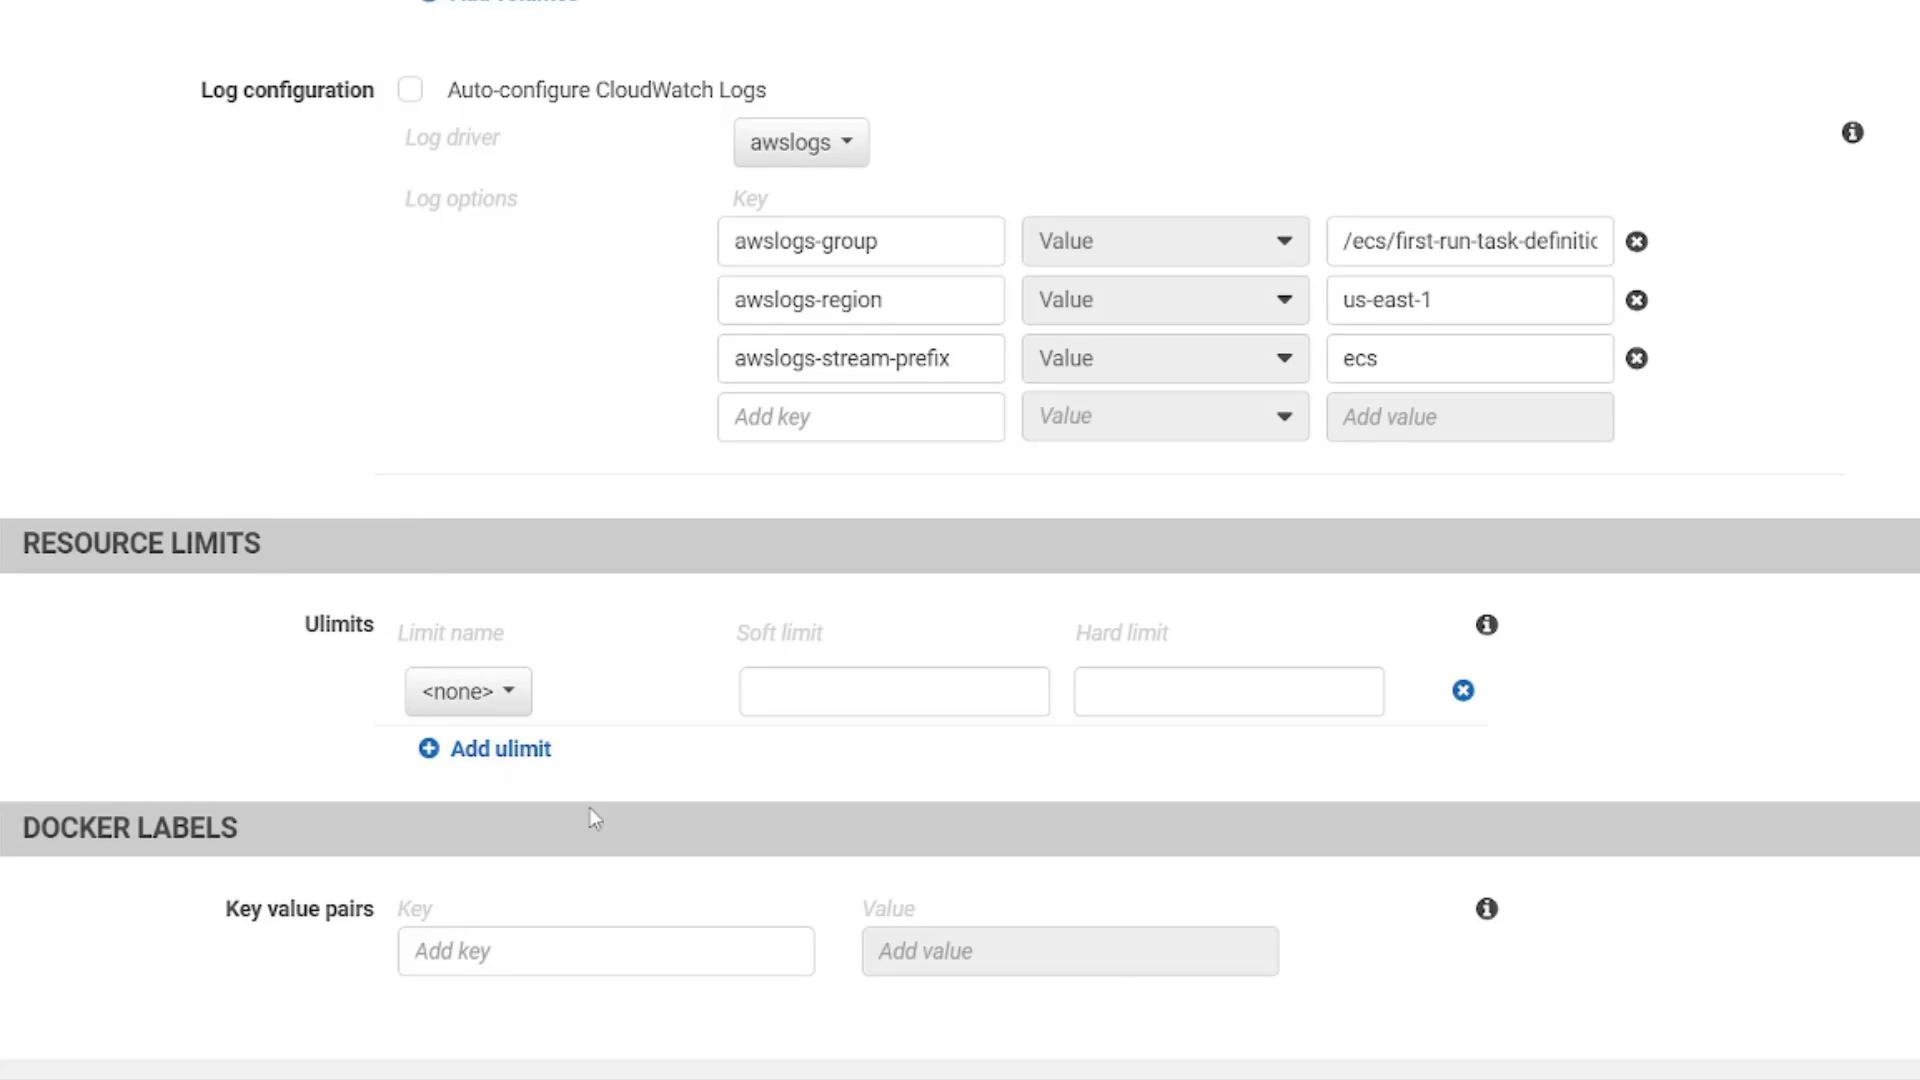
KodeKloud/ECS-Project1 - Optional: memory, CPU, health checks, environment variables, logging
2) Clean up wizard resources (so we can recreate manually)
To learn the underlying steps, delete the resources the wizard created:- Delete the service (stops and removes tasks).
- Delete the cluster (removes cluster and the VPC/subnets the wizard created).
3) Create a cluster and task definition manually
Create a new cluster:- Go to ECS → Clusters → Create Cluster
- Choose “Networking only (Fargate)”
- Name the cluster, e.g.,
cluster1 - Let ECS create a VPC and subnets for you (or choose an existing VPC)
- Create and open the cluster
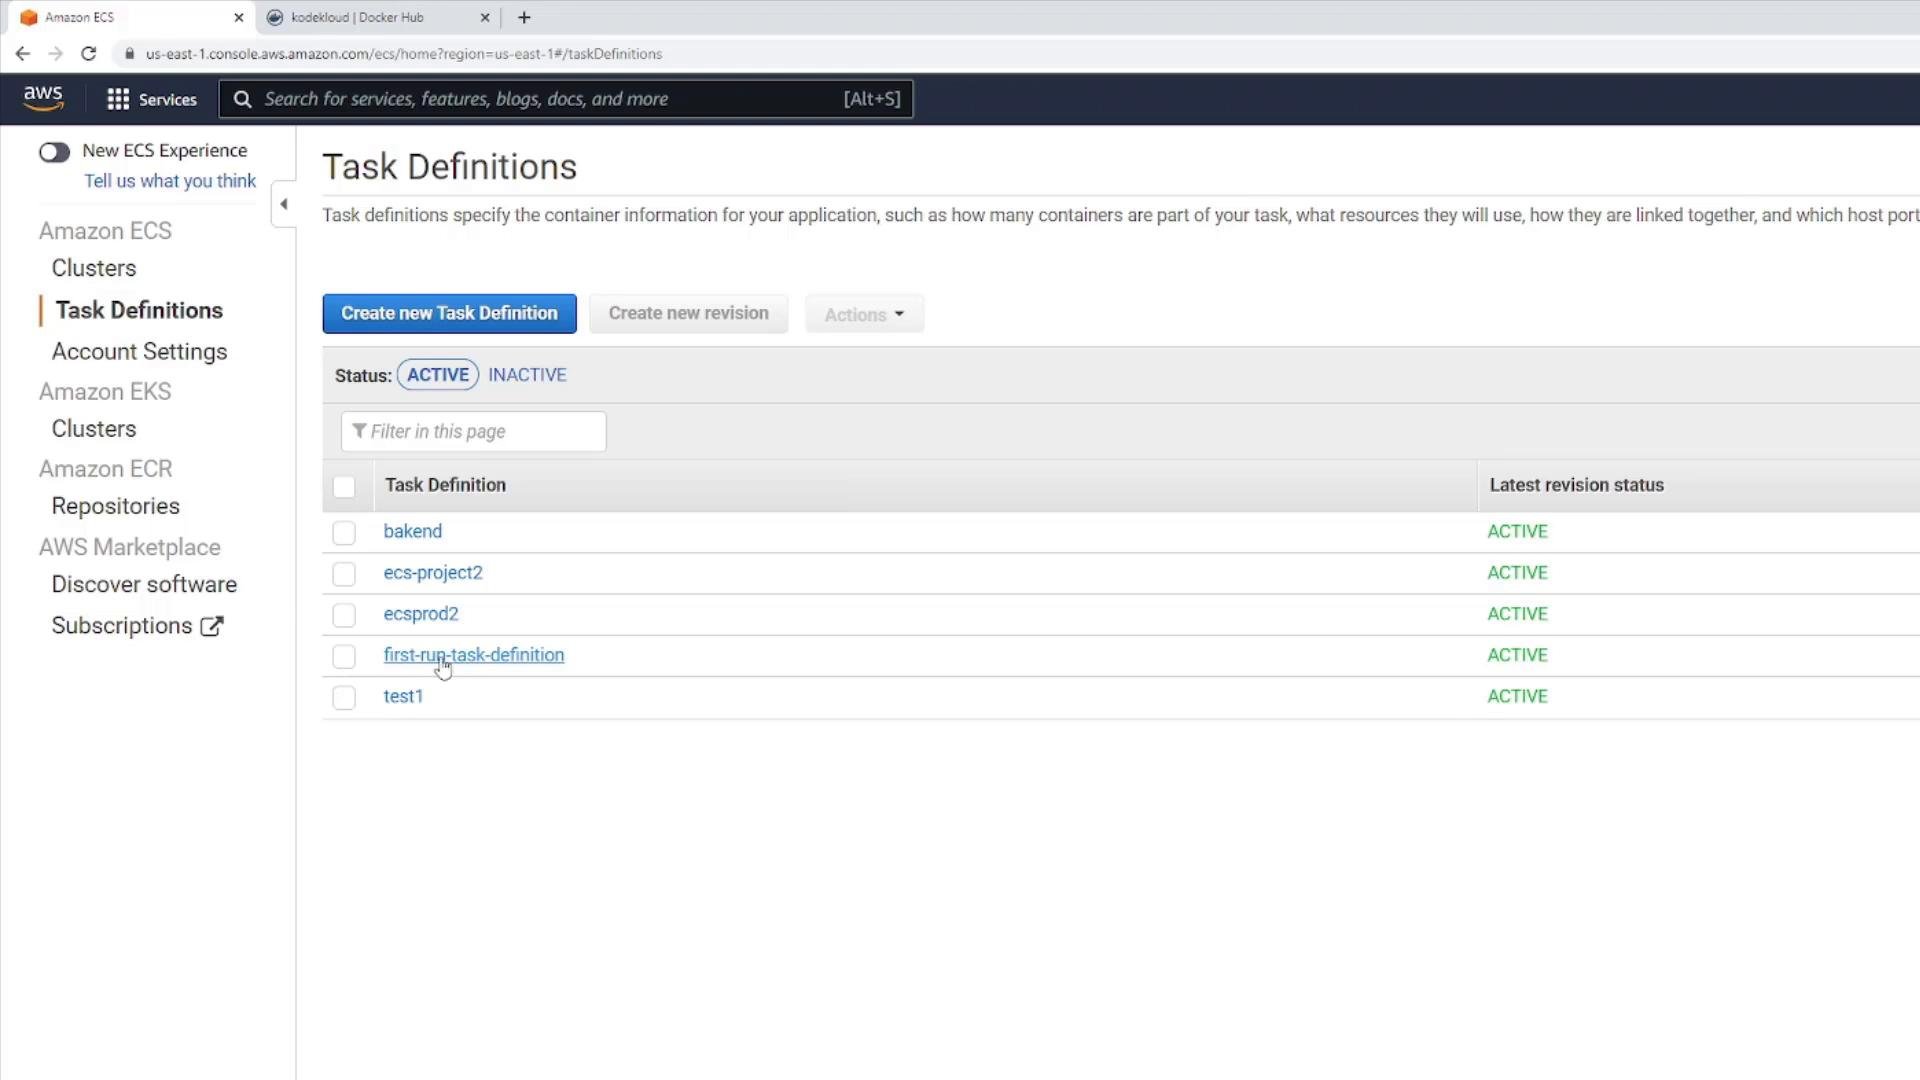
- ECS → Task Definitions → Create task definition → select
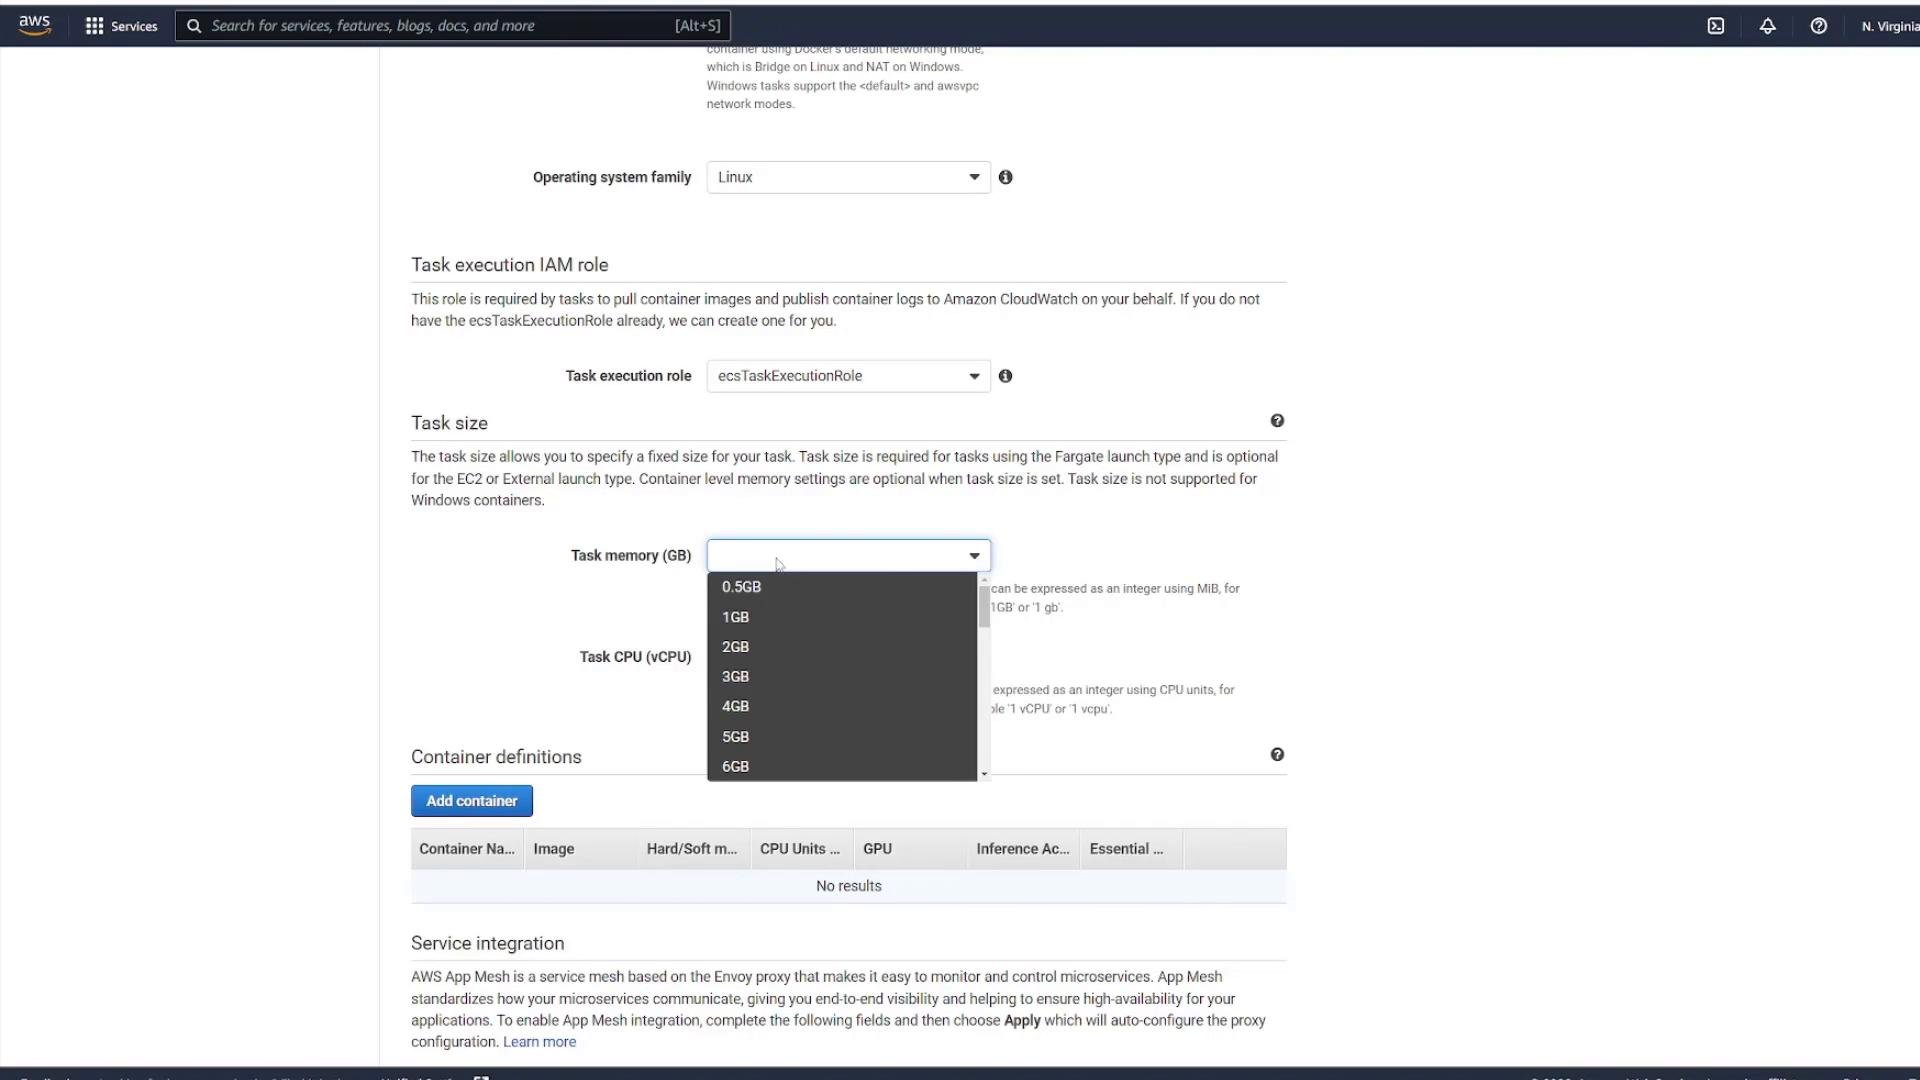
FARGATE - Name the task definition and select the Task execution role (this role lets ECS pull images and write logs)
- OS family:
Linux - Set Task CPU and Memory appropriate to your app
- Add a container definition:
- Container name:
node-app - Image:
KodeKloud/ECS-Project1 - Port mapping: container port
3000, TCP - Optionally: health check, env vars, logging (awslogs)
- Container name:
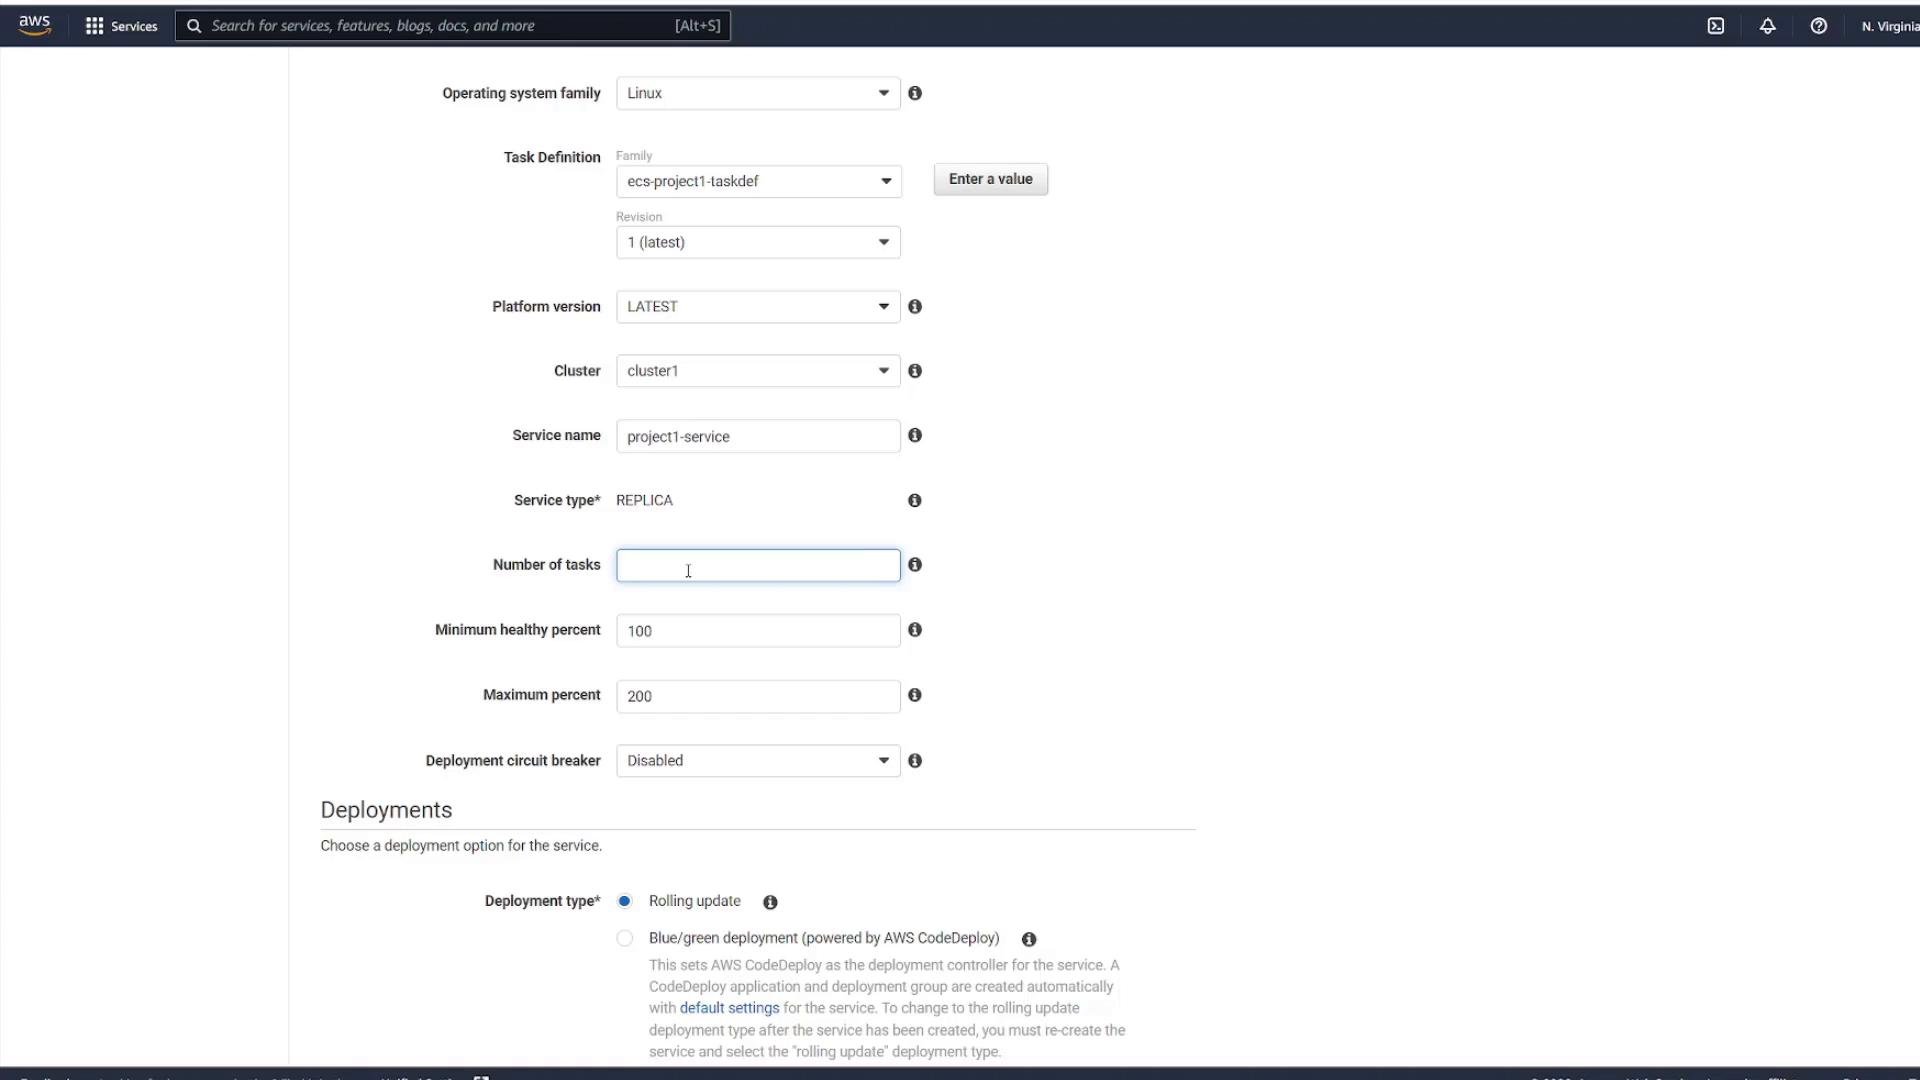
- Cluster → Services → Create
- Launch type:
FARGATE - Task definition: select your newly created task definition (latest revision)
- Cluster:
cluster1 - Service name:
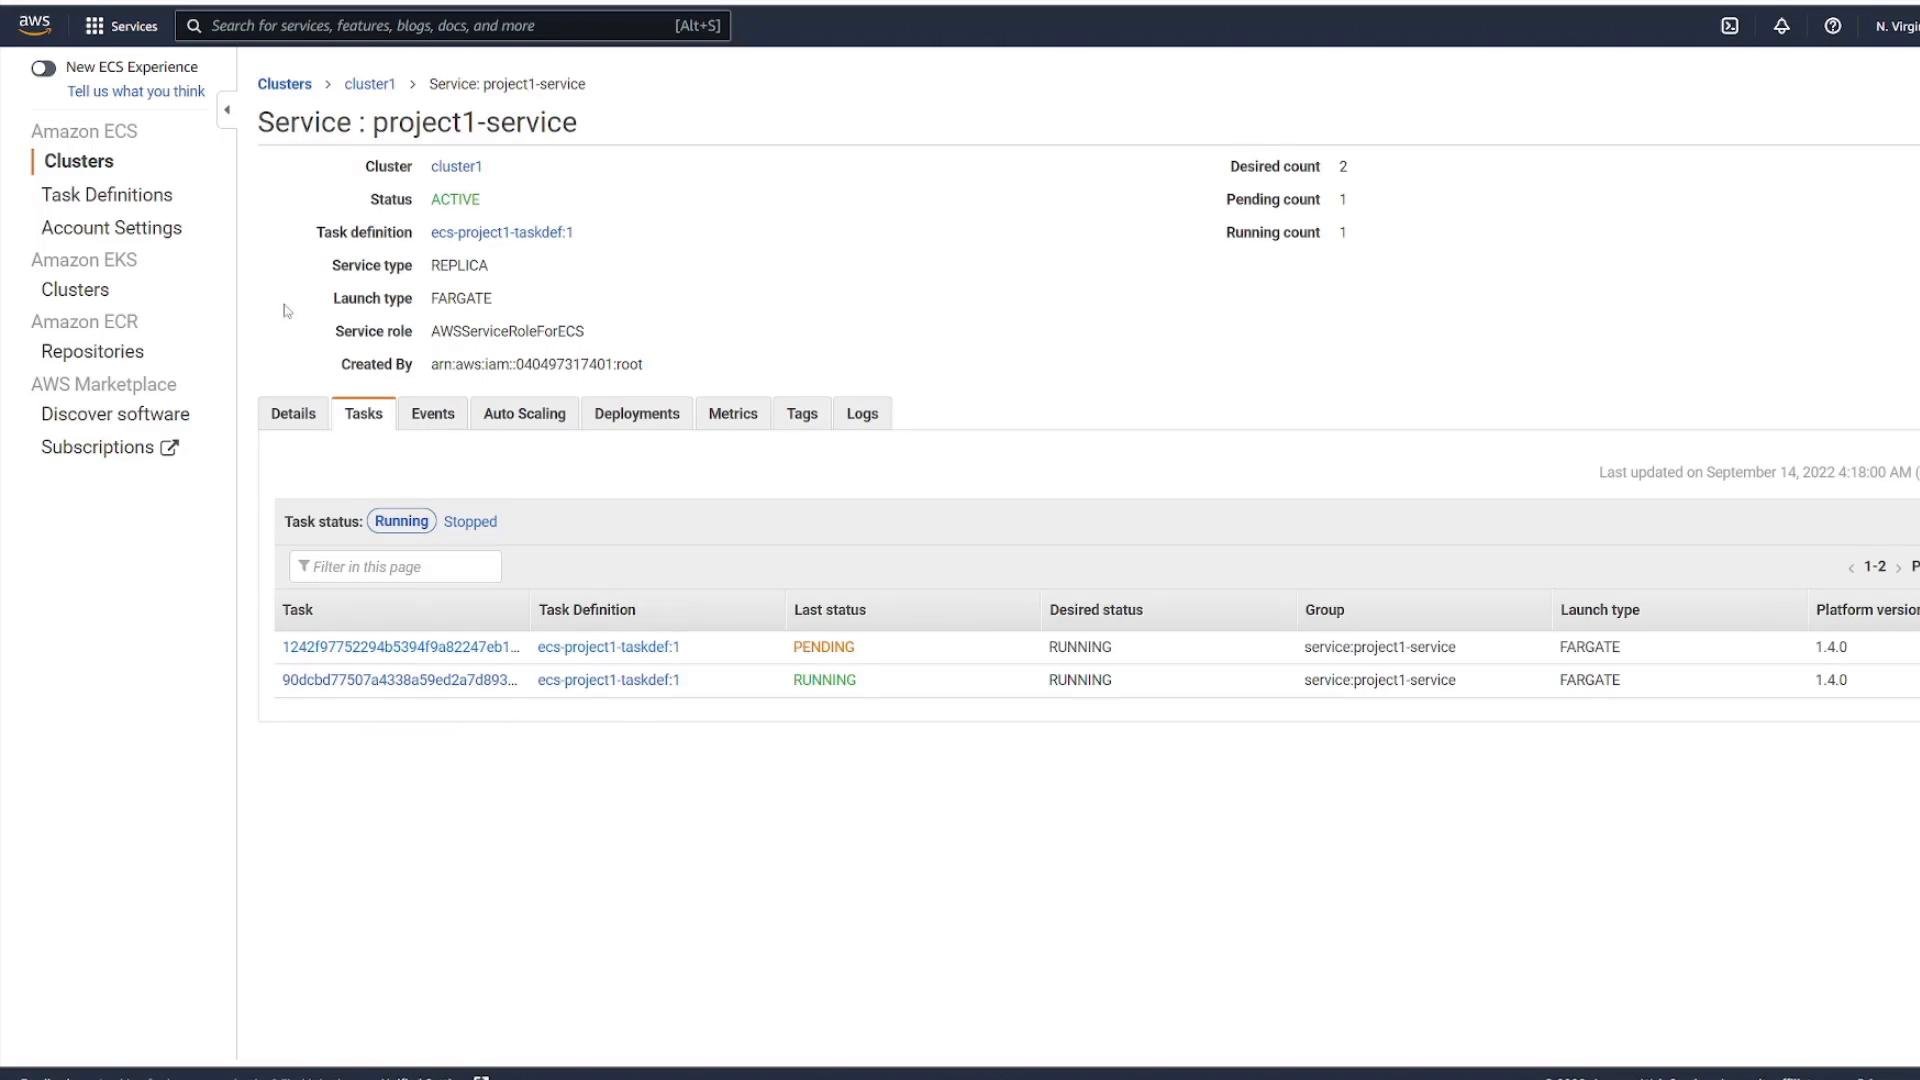
project-one-service - Number of tasks: desired scale (e.g.,
1or2) - Networking:
- VPC and subnets: choose those created for the cluster
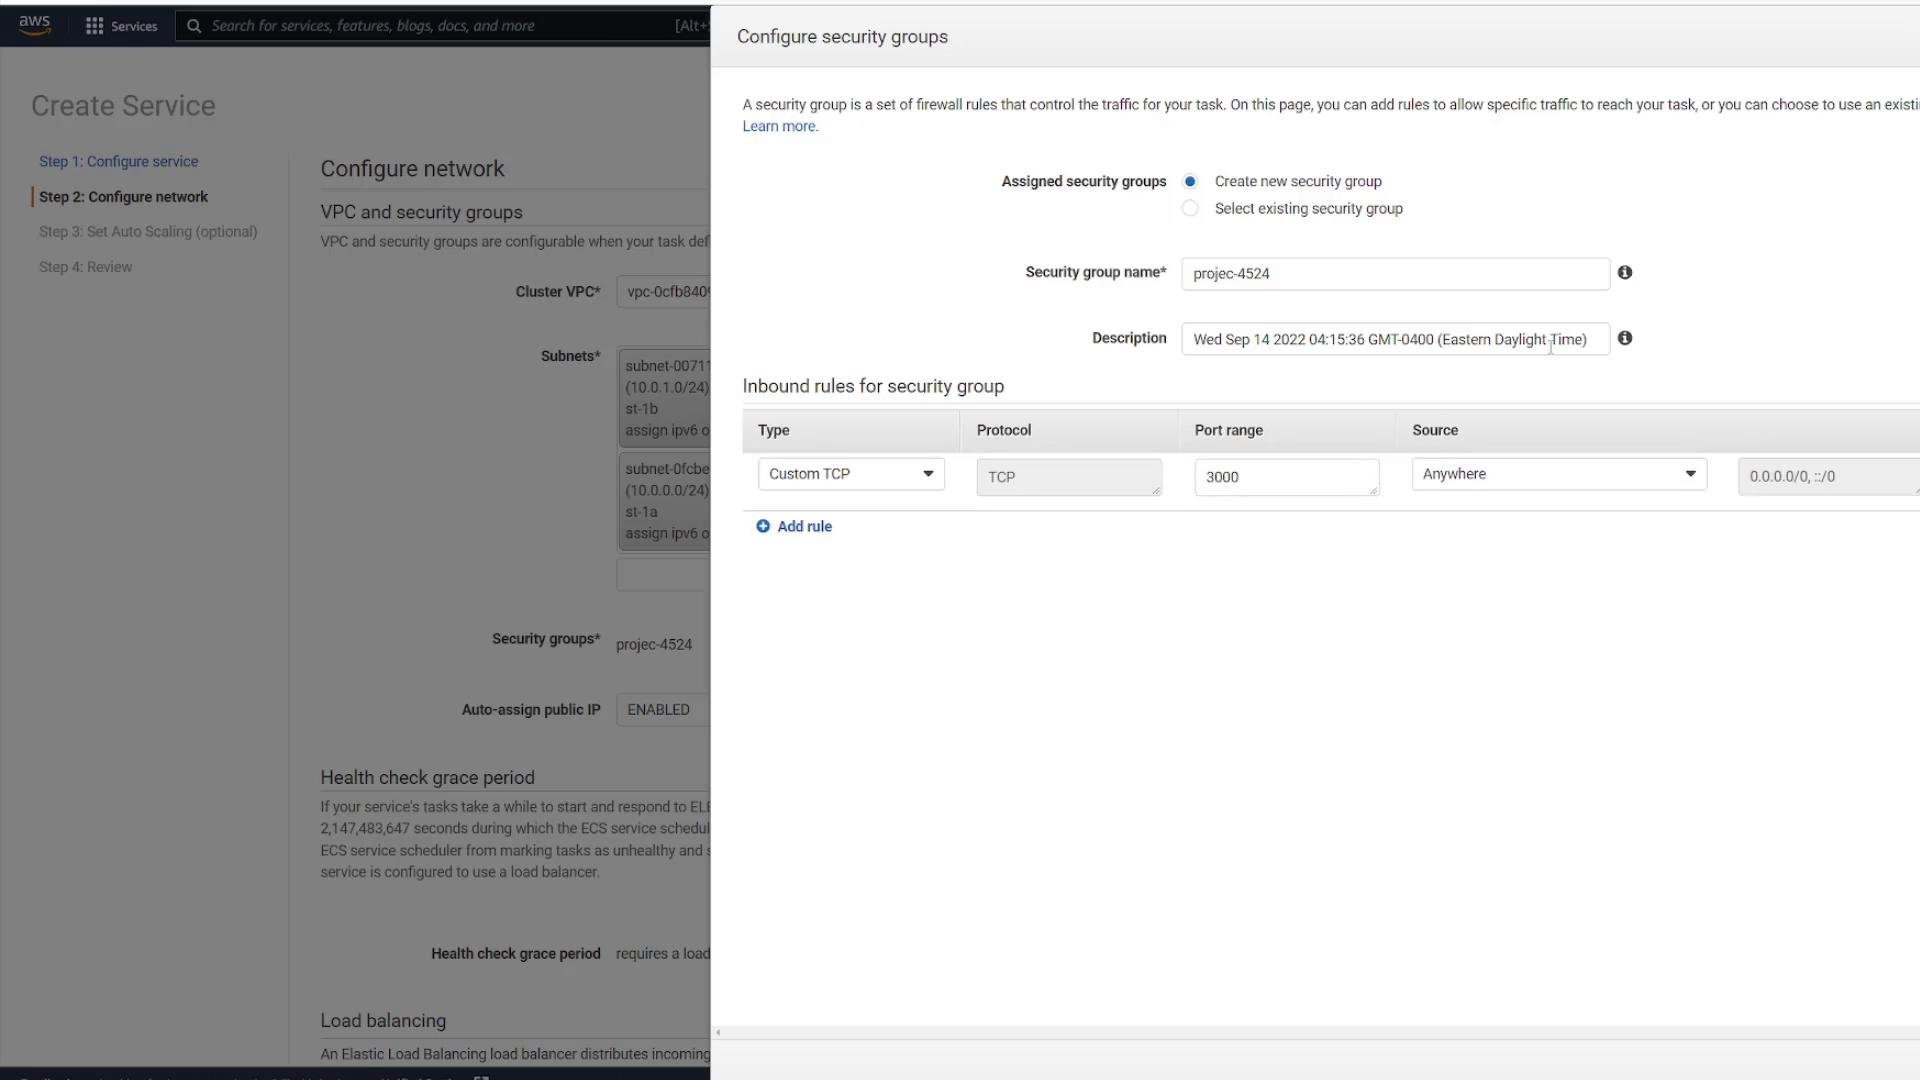
- Security group: ensure it allows inbound traffic to the container port (
3000) from the clients that need access
- Load balancer: optional (skipped in this demo)
- Auto Scaling: optional (skip for the demo)
Be careful when opening security groups to the internet. For demo purposes you may allow
0.0.0.0/0 to port 3000, but for production use least-privilege rules or a load balancer with restrictive access.3000 from the required CIDR range.
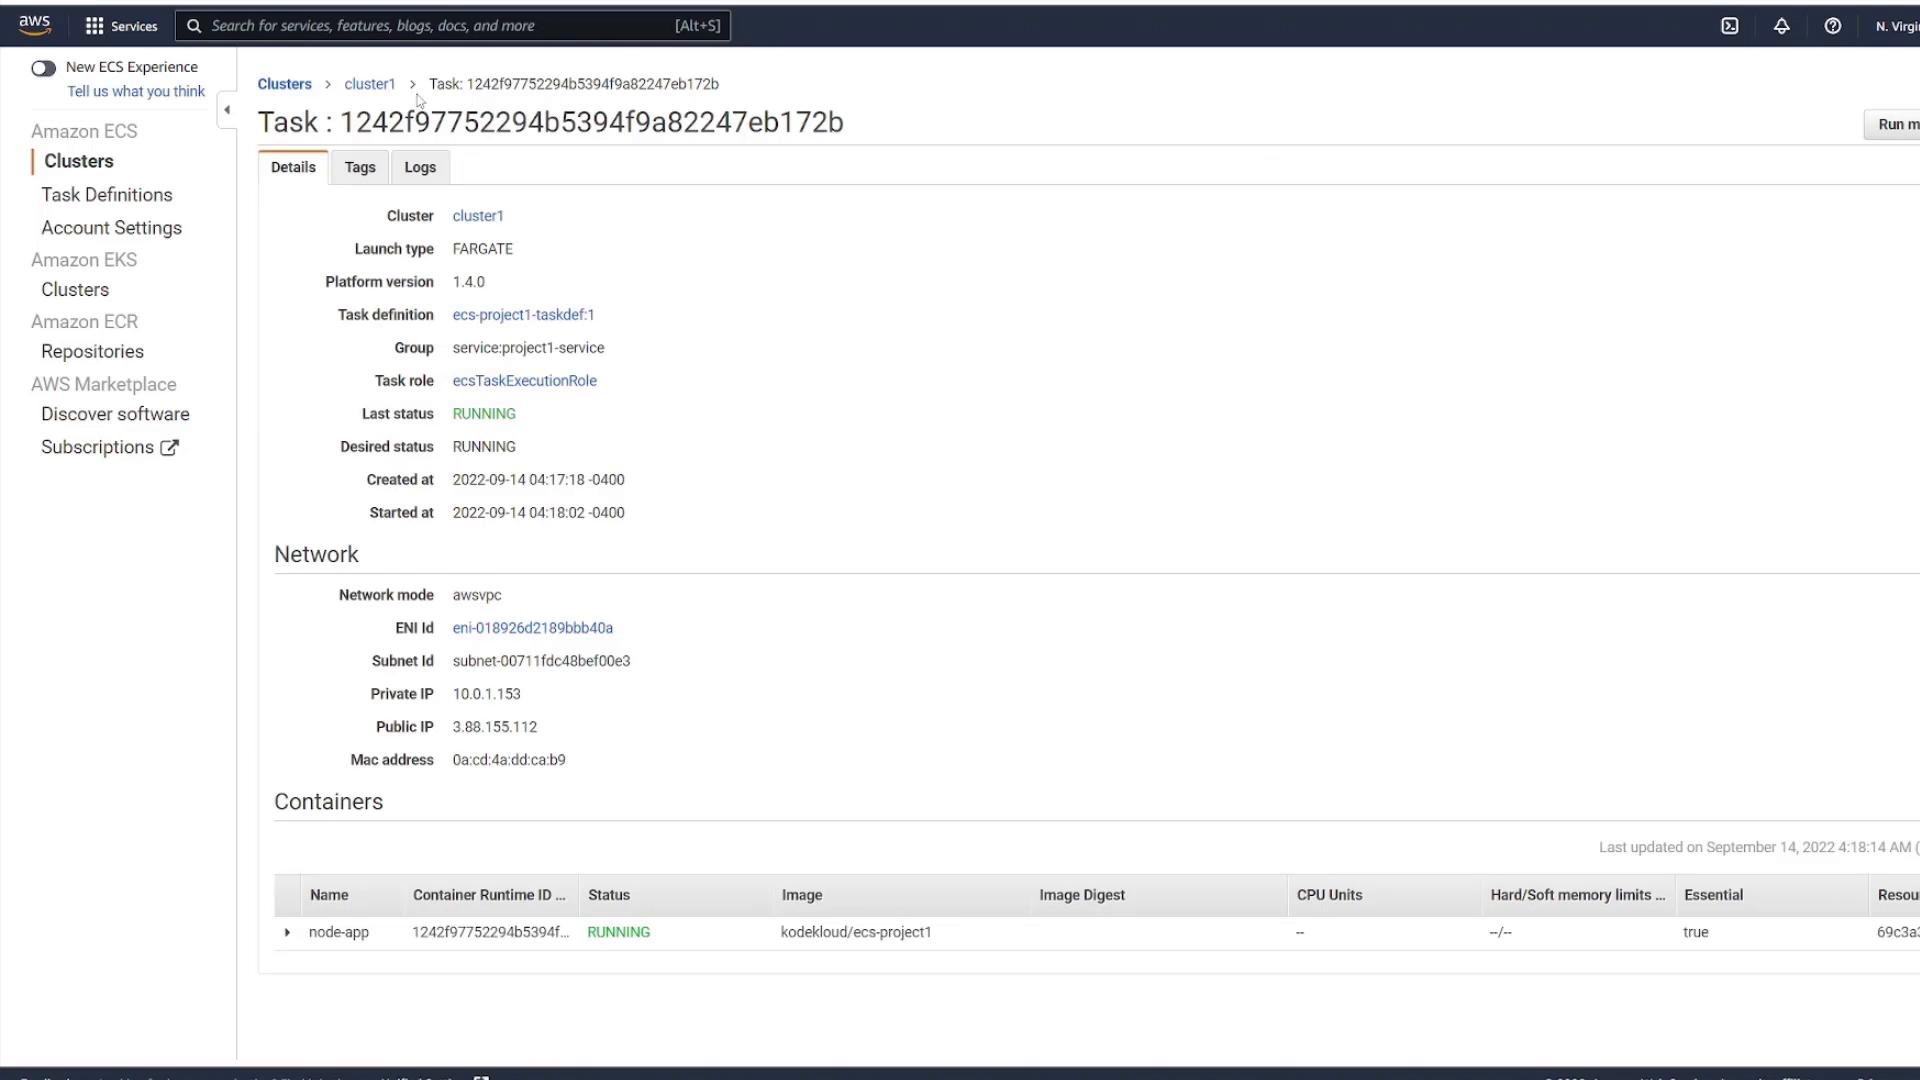
4) Updating the app image and redeploying
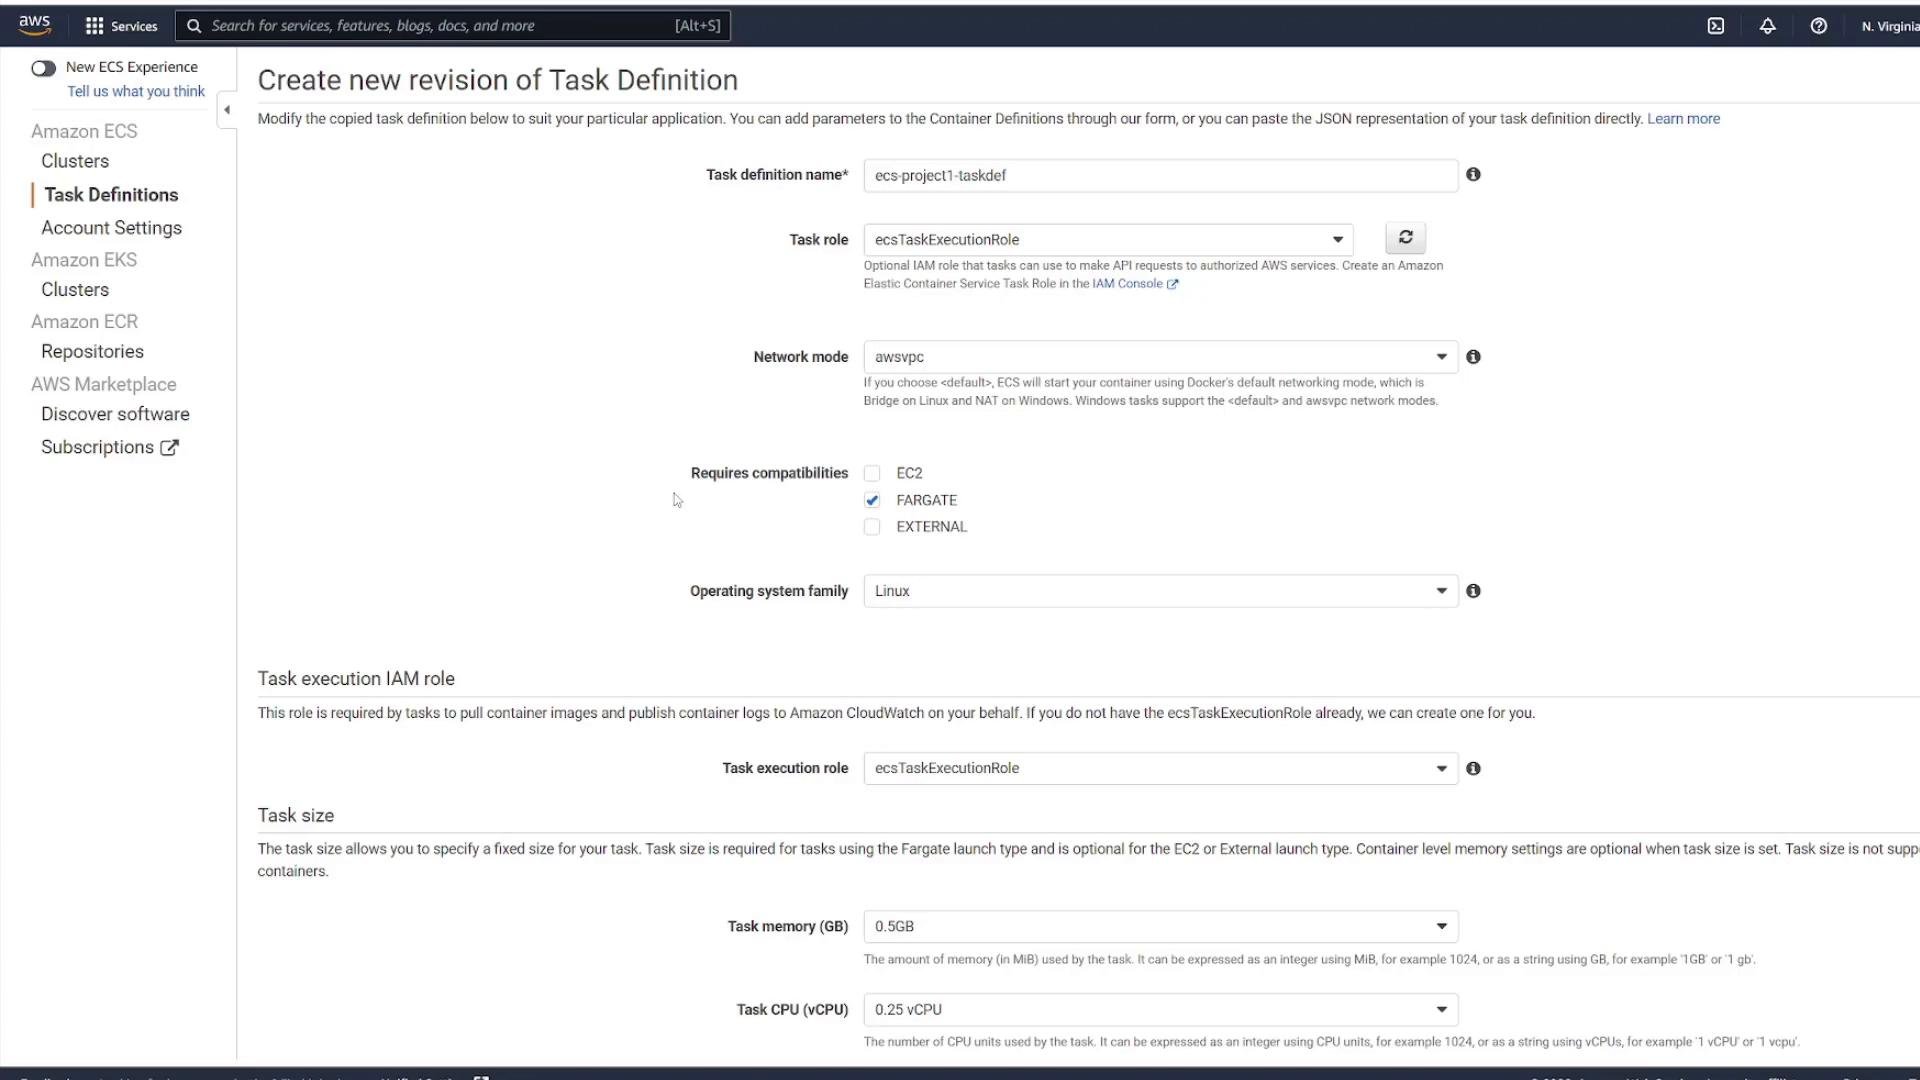
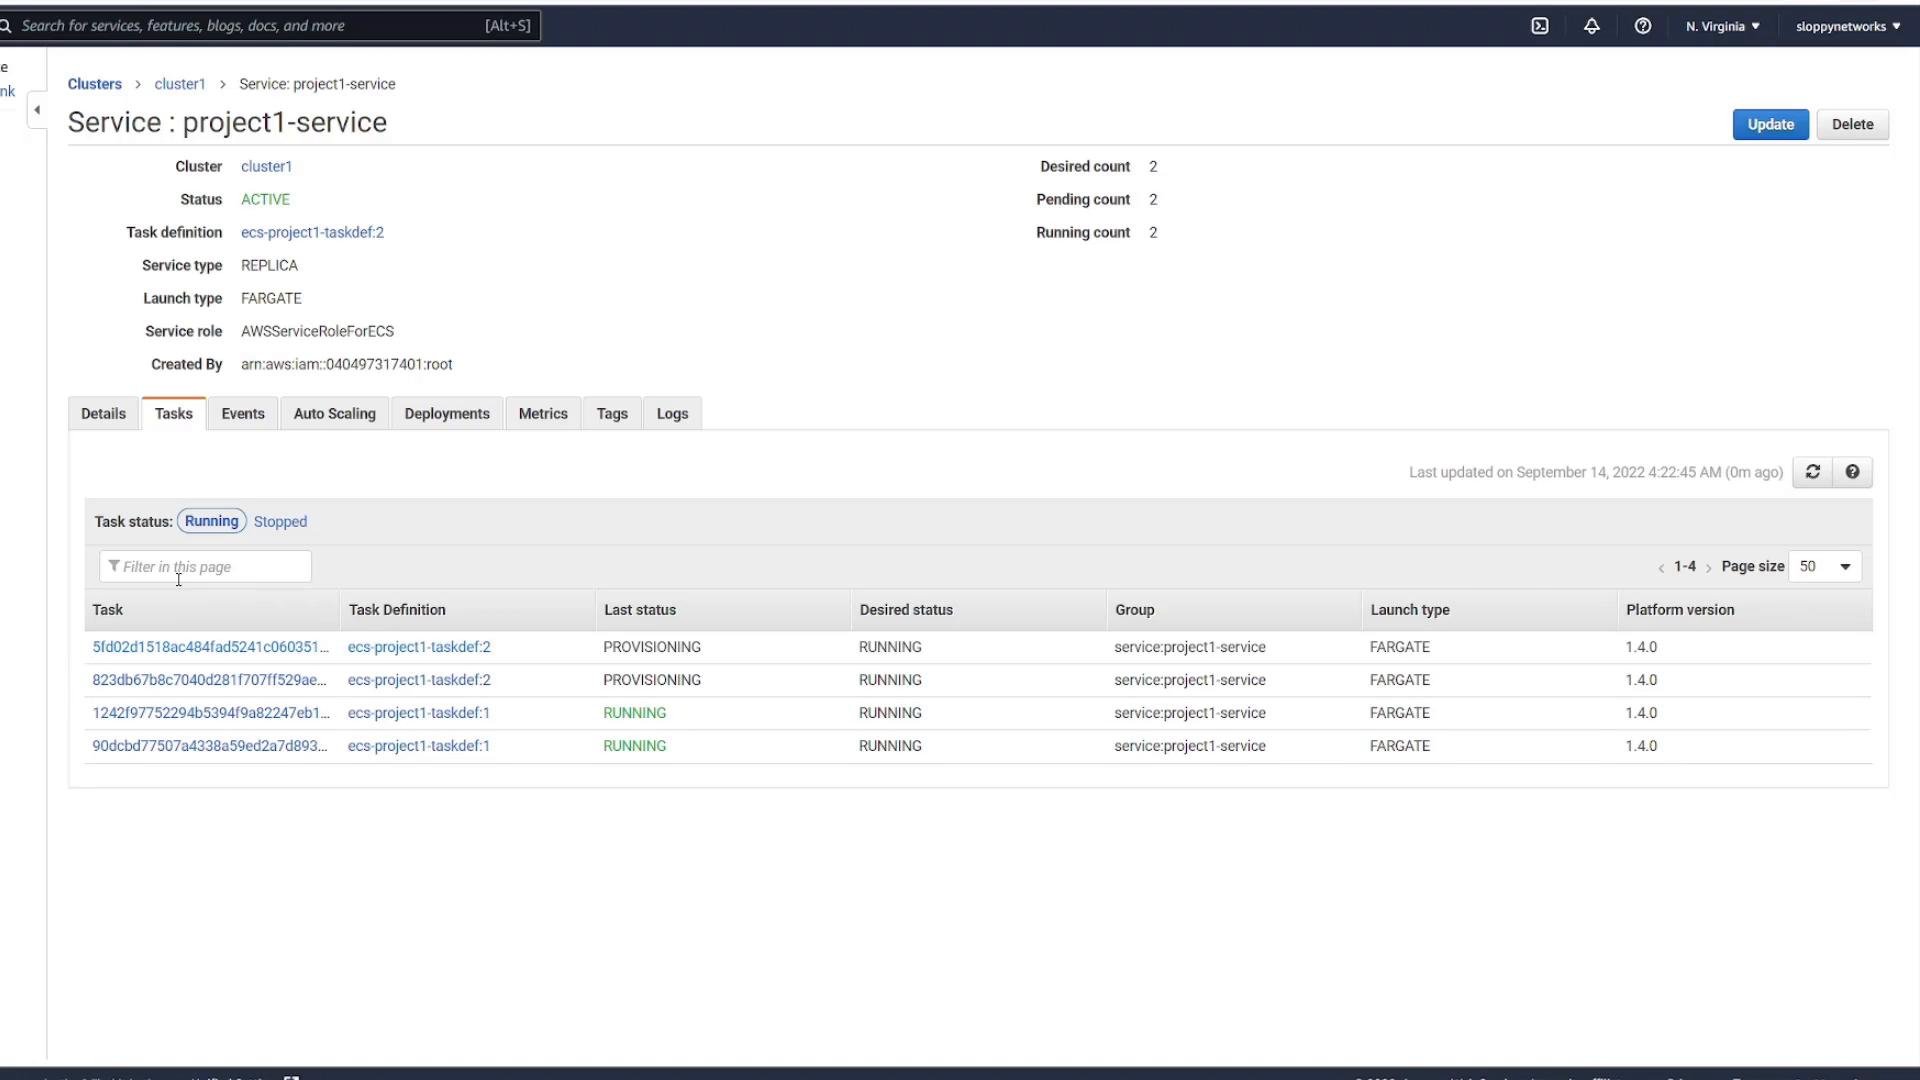
If you change application code (for example, modify the HTML view), rebuild and push a new Docker image to your registry (Docker Hub in this demo). ECS will not automatically pull the new image until you trigger a deployment. Example local steps (build and push):- In the Service view: Choose Update → check “Force new deployment” — this causes ECS to create new tasks that pull the updated image.
- Or: Create a new revision of the Task Definition (if you changed configuration) and update the service to use that revision.
5) Final cleanup and next steps
When finished with the demo resources:- Delete the service (this will stop tasks).
- Delete the cluster (if you don’t plan to reuse it).
- Delete any related security groups, VPCs, or load balancers the demo created (if applicable).
- Amazon ECS docs: https://docs.aws.amazon.com/ecs/
- Amazon EC2 (for EC2-backed ECS): https://learn.kodekloud.com/user/courses/amazon-elastic-compute-cloud-ec2