

What is Verified Permissions?
Amazon Verified Permissions is a purpose-built, managed policy engine that externalizes fine-grained authorization from application code. After you implement authentication, your application still needs to answer authorization questions: What is a user allowed to do? Can they view another user’s content? Can they delete an item? Verified Permissions centralizes that logic so security teams and developers can create, audit, and evaluate policies outside of application code. Key points at a glance:- Centralizes policy management so teams can view, create, and audit authorization rules in one place via the AWS Console, AWS CLI, or AWS SDKs.
- Uses the Cedar policy language for expressive, fine-grained policies. See the Cedar docs: Cedar policy language.
- Evaluates authorization requests at runtime and returns an allow/deny decision to your application.
- Pricing is usage-based: billing depends on the number of authorization requests evaluated each month.
Verified Permissions lets you separate authorization from application code so security teams can audit policies without scanning application logic.
How Verified Permissions works
The service follows a simple, repeatable workflow: define your authorization model, author policies, evaluate requests at runtime, and audit decisions.-
Define a schema (the authorization model)
- Model the domain entities and relationships that matter for access control: principals (subjects), resources, actions, and relationships (for example,
owner,member,viewer). This schema captures the structure your Cedar policies will reference.
- Model the domain entities and relationships that matter for access control: principals (subjects), resources, actions, and relationships (for example,
-
Create policies
- Write policies in Cedar to express who can do what, under which conditions. Policies can reference relationships, attributes on principals/resources, and contextual data (such as request time or IP).
- Example Cedar-style snippet (illustrative):
-
Evaluate requests at runtime
- Your application sends authorization queries (principal, action, resource, and optional context) to Verified Permissions from any compute environment: AWS Lambda, Amazon ECS, AppSync, API Gateway, or on-premises services.
- The service evaluates the request against the stored schema and policies, and returns a definitive allow/deny decision.
- Audit and manage
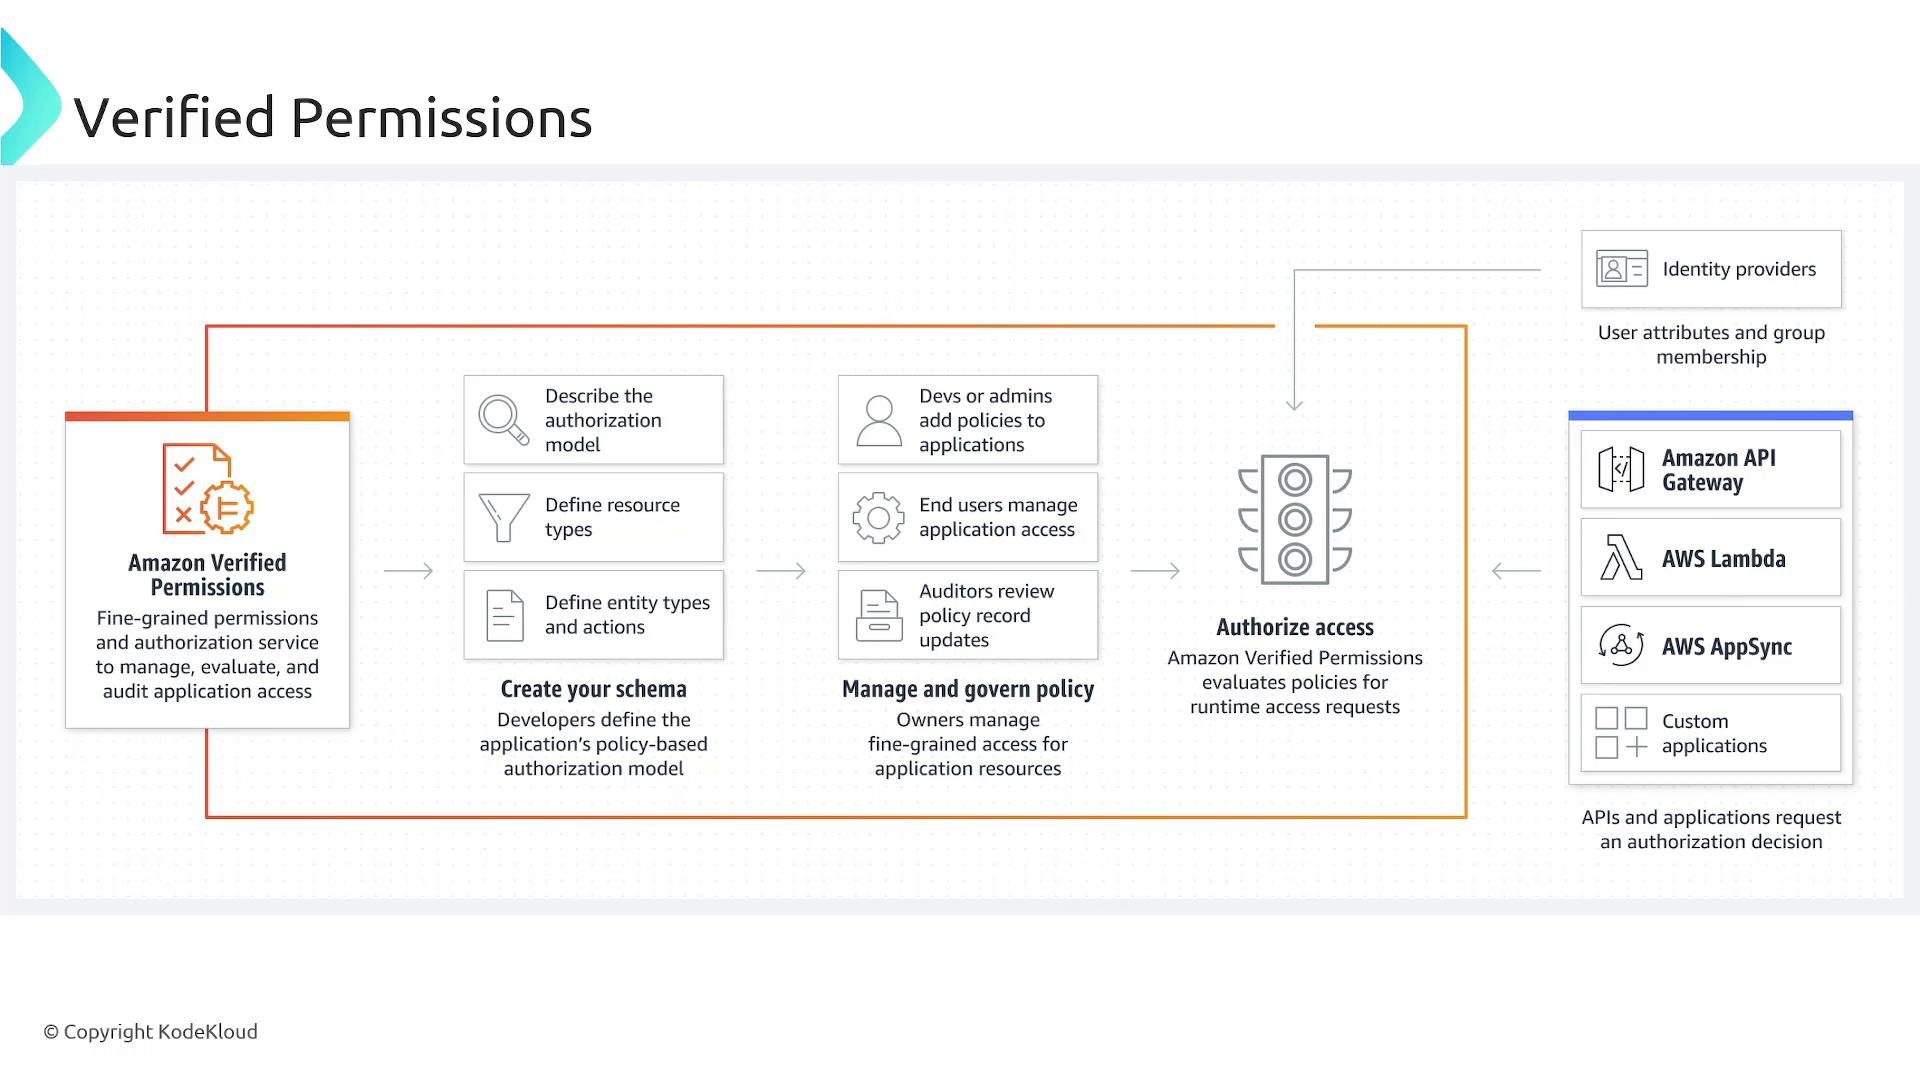
Why use Verified Permissions?
Verified Permissions provides several operational and security benefits when compared to embedding authorization logic in application code:-
Decouples authorization from business logic
Keep permission rules out of application code. This reduces duplication, lowers the risk of subtle bugs, and enables centralized governance. -
Enables real-time, zero-trust authorization
Each access attempt is evaluated at request time — nothing is implicitly trusted based on prior state or cached permissions. -
Improves auditability and governance
Centralized policies, versioning, and evaluation logs make compliance reviews and security audits more straightforward. -
Integrates with identity providers and AWS services
Works with common identity sources and integrates smoothly with AWS compute and API services for low-friction adoption.
When to choose Verified Permissions
Policy creation — who can author policies?
- Developers and security teams typically author and maintain policies during development and operations.
- In some application designs, end users may express policy-like rules (for example, sharing preferences). Those user-defined rules can be modeled in the schema and evaluated by Verified Permissions alongside centrally managed policies.
Summary
Amazon Verified Permissions is a managed policy evaluation service that centralizes authorization using the Cedar policy language and a clear authorization model. By delegating policy storage and decision-making to the service, you get consistent runtime authorization, improved auditability, and a clean separation between business logic and access control.Links and References
- Amazon Verified Permissions product page
- Cedar policy language docs
- AWS Console | AWS CLI | AWS SDKs and tools
- AWS Lambda | Amazon ECS | AppSync | API Gateway