

- Full name
- Date of birth
- Email address
- Phone number
- Home address
- Passport number, Social Security number, or other government-issued identifiers
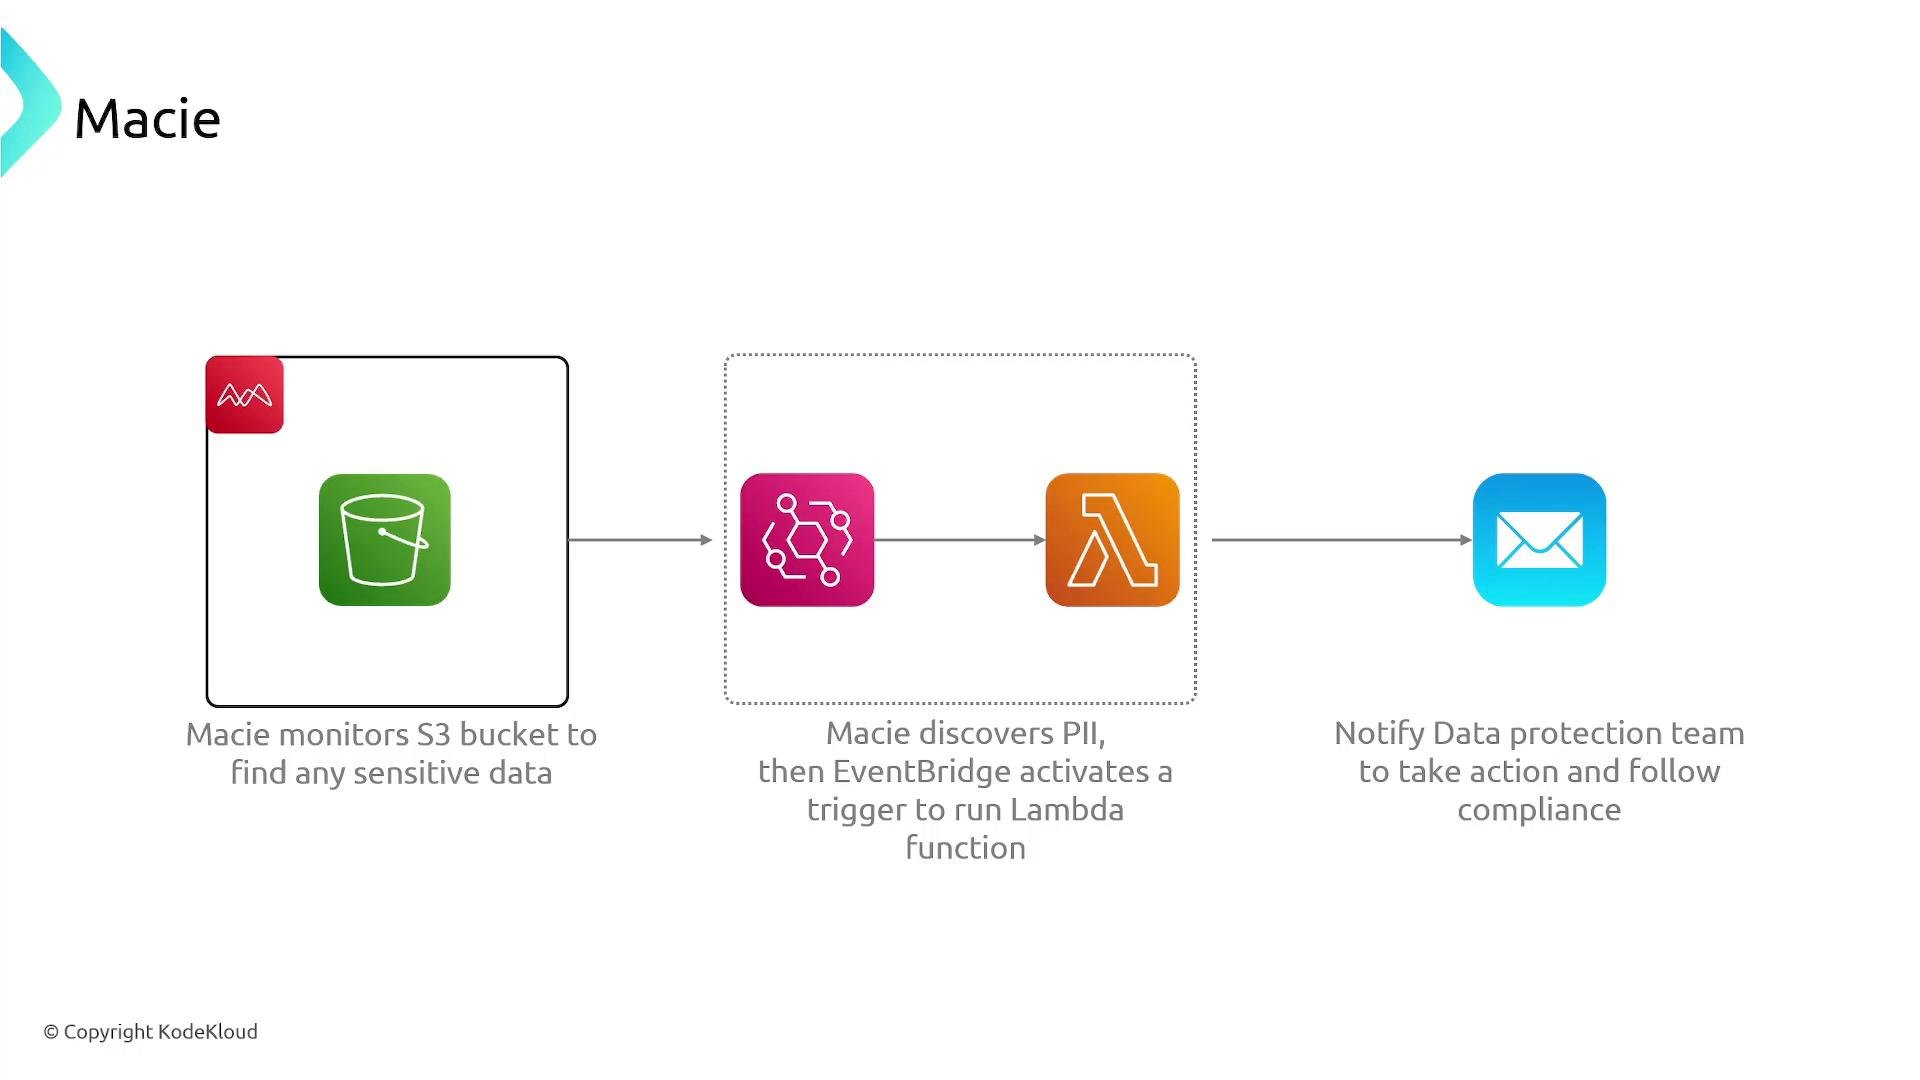
- Macie analyzes both object metadata and object content in S3 to identify sensitive information.
- It uses managed data identifiers (pre-built patterns for common sensitive types such as credit cards and SSNs) plus custom data identifiers you can create for organization-specific patterns.
- When a finding is produced, Macie classifies the severity and provides context so you can prioritize investigations.
- Route the finding to EventBridge to trigger Lambda, Step Functions, or other targets.
- Send notifications via Amazon SNS or integrate with ticketing systems.
- Aggregate and analyze findings using the Macie console dashboards or export them to SIEM/SOAR tools for advanced analysis.
- Discovery: Macie scans configured S3 buckets and indexes objects and metadata.
- Classification: Objects are evaluated against managed and custom identifiers to detect sensitive data.
- Finding generation: When sensitive data is detected, Macie generates findings with severity, sample data, and location.
- Action: Findings are routed to EventBridge, stored, or forwarded to downstream systems for remediation or reporting.
- Discover and inventory locations of PII and sensitive data across S3.
- Continuous monitoring for accidental data exposures in object storage.
- Automated remediation pipelines (e.g., quarantine objects, block access, notify owners).
- Compliance reporting and data governance.
Getting started — quick checklist
- Enable Amazon Macie in the AWS account and choose which S3 buckets to scope.
- Review and tune managed data identifiers for your environment.
- Create custom data identifiers for organization-specific patterns.
- Configure EventBridge rules to catch Macie findings and route to automation targets (Lambda, Step Functions, SNS).
- Build remediation logic in Lambda or Step Functions (notification, quarantine, policy enforcement).
- Monitor and refine using Macie dashboards and exported logs to SIEM/SOAR systems.
Macie focuses on discovering and protecting sensitive data stored in Amazon S3. Review the Macie pricing and the scope of S3 scanning before enabling across many buckets to estimate cost and scan coverage.
- Amazon Macie
- Amazon S3
- Amazon EventBridge
- AWS Lambda
- Macie user guide: https://docs.aws.amazon.com/macie/latest/user/what-is-macie.html
- SIEM and SOAR concepts: https://en.wikipedia.org/wiki/Security_information_and_event_management and https://en.wikipedia.org/wiki/Security_orchestration,_automation,_and_response