

In this lesson we focus on designing reliability for AWS security services: which services expose reliability controls you can manage, and which are fully managed by AWS. You’ll learn practical reliability levers (multi-AZ, cross‑Region replication, clustering), and where to rely on AWS-managed resilience.
Many AWS security services are fully managed and built for high availability. Your primary responsibility is to integrate their telemetry and findings into resilient detection, incident response, and recovery workflows rather than changing the core service resilience.
Identity, authentication, and authorization
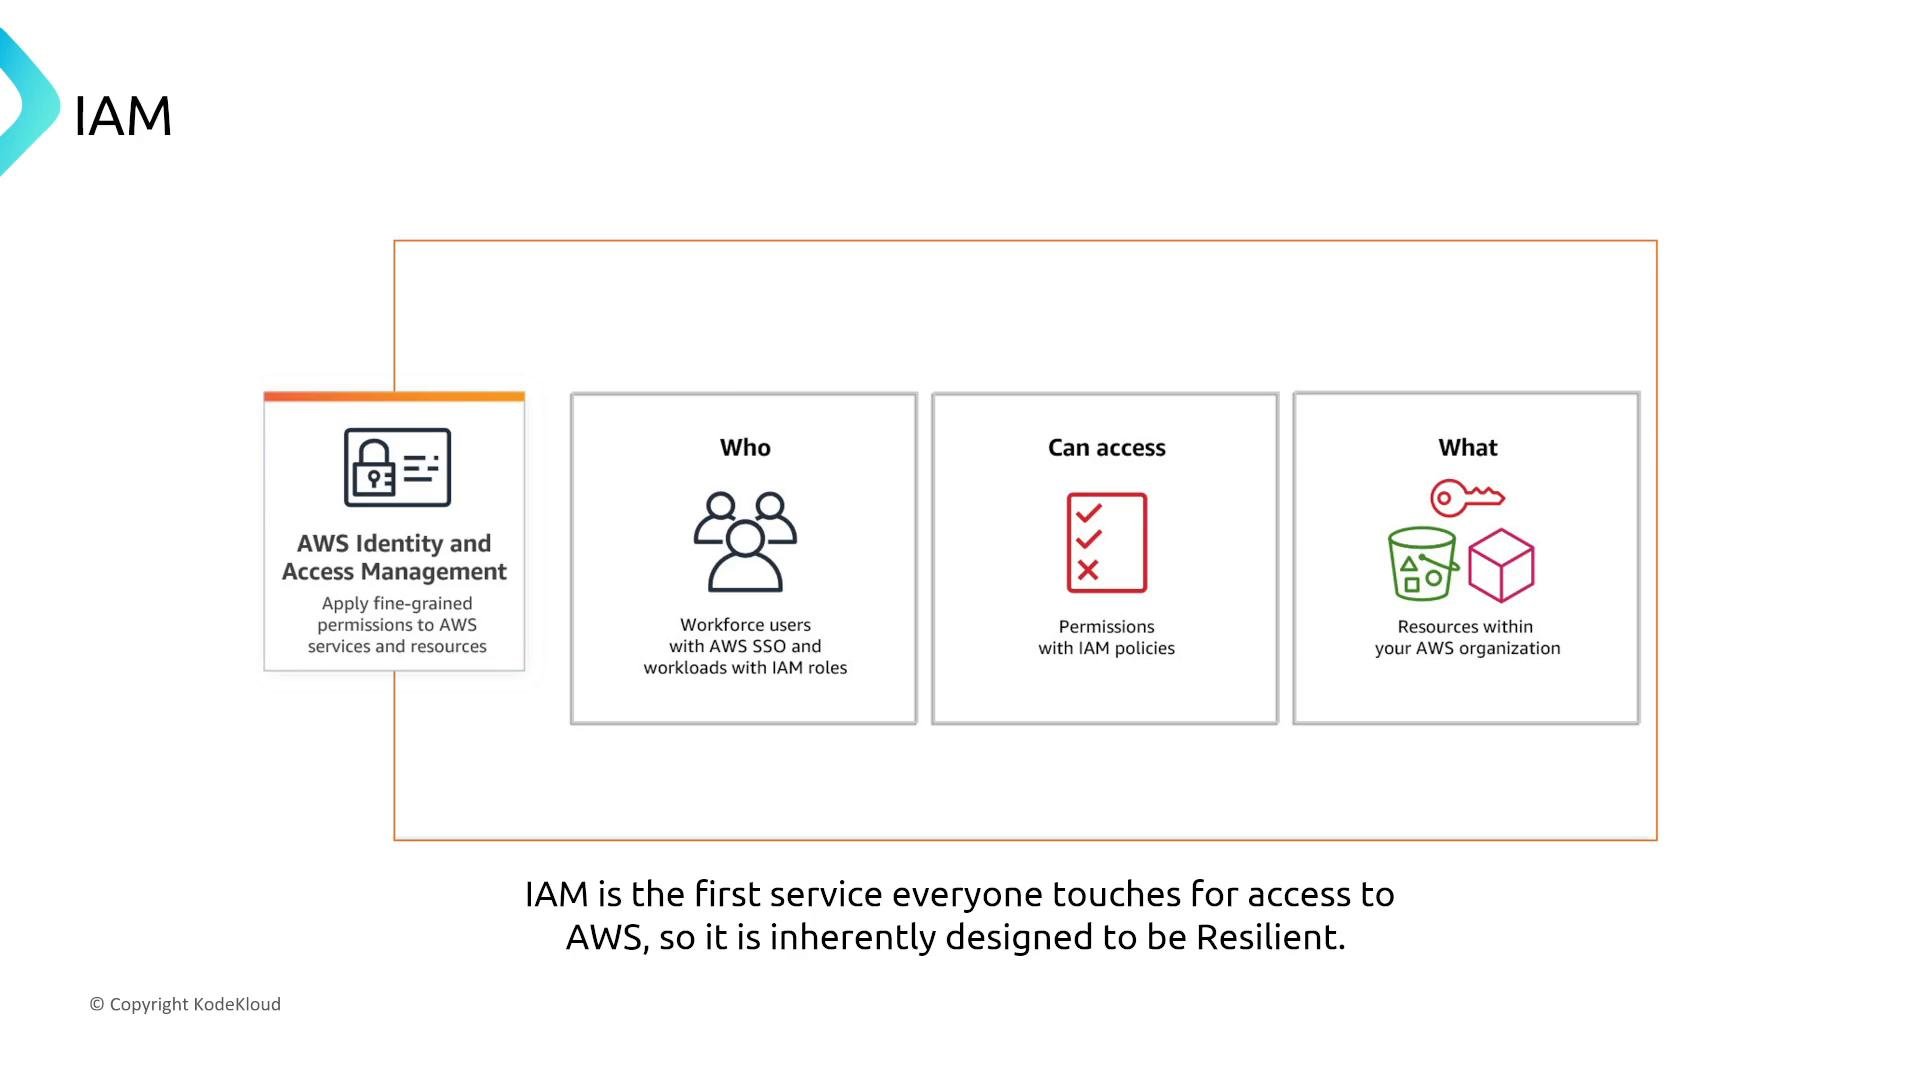
- IAM (AWS Identity and Access Management): AWS manages availability and resilience for IAM. Design decisions you make around permission models (least privilege, role chaining, delegation, policy scoping) impact security posture and operational reliability but are not availability knobs.
- IAM Identity Center (AWS SSO): Integrate with trusted identity providers and configure SSO, but the service’s underlying availability is AWS-managed.
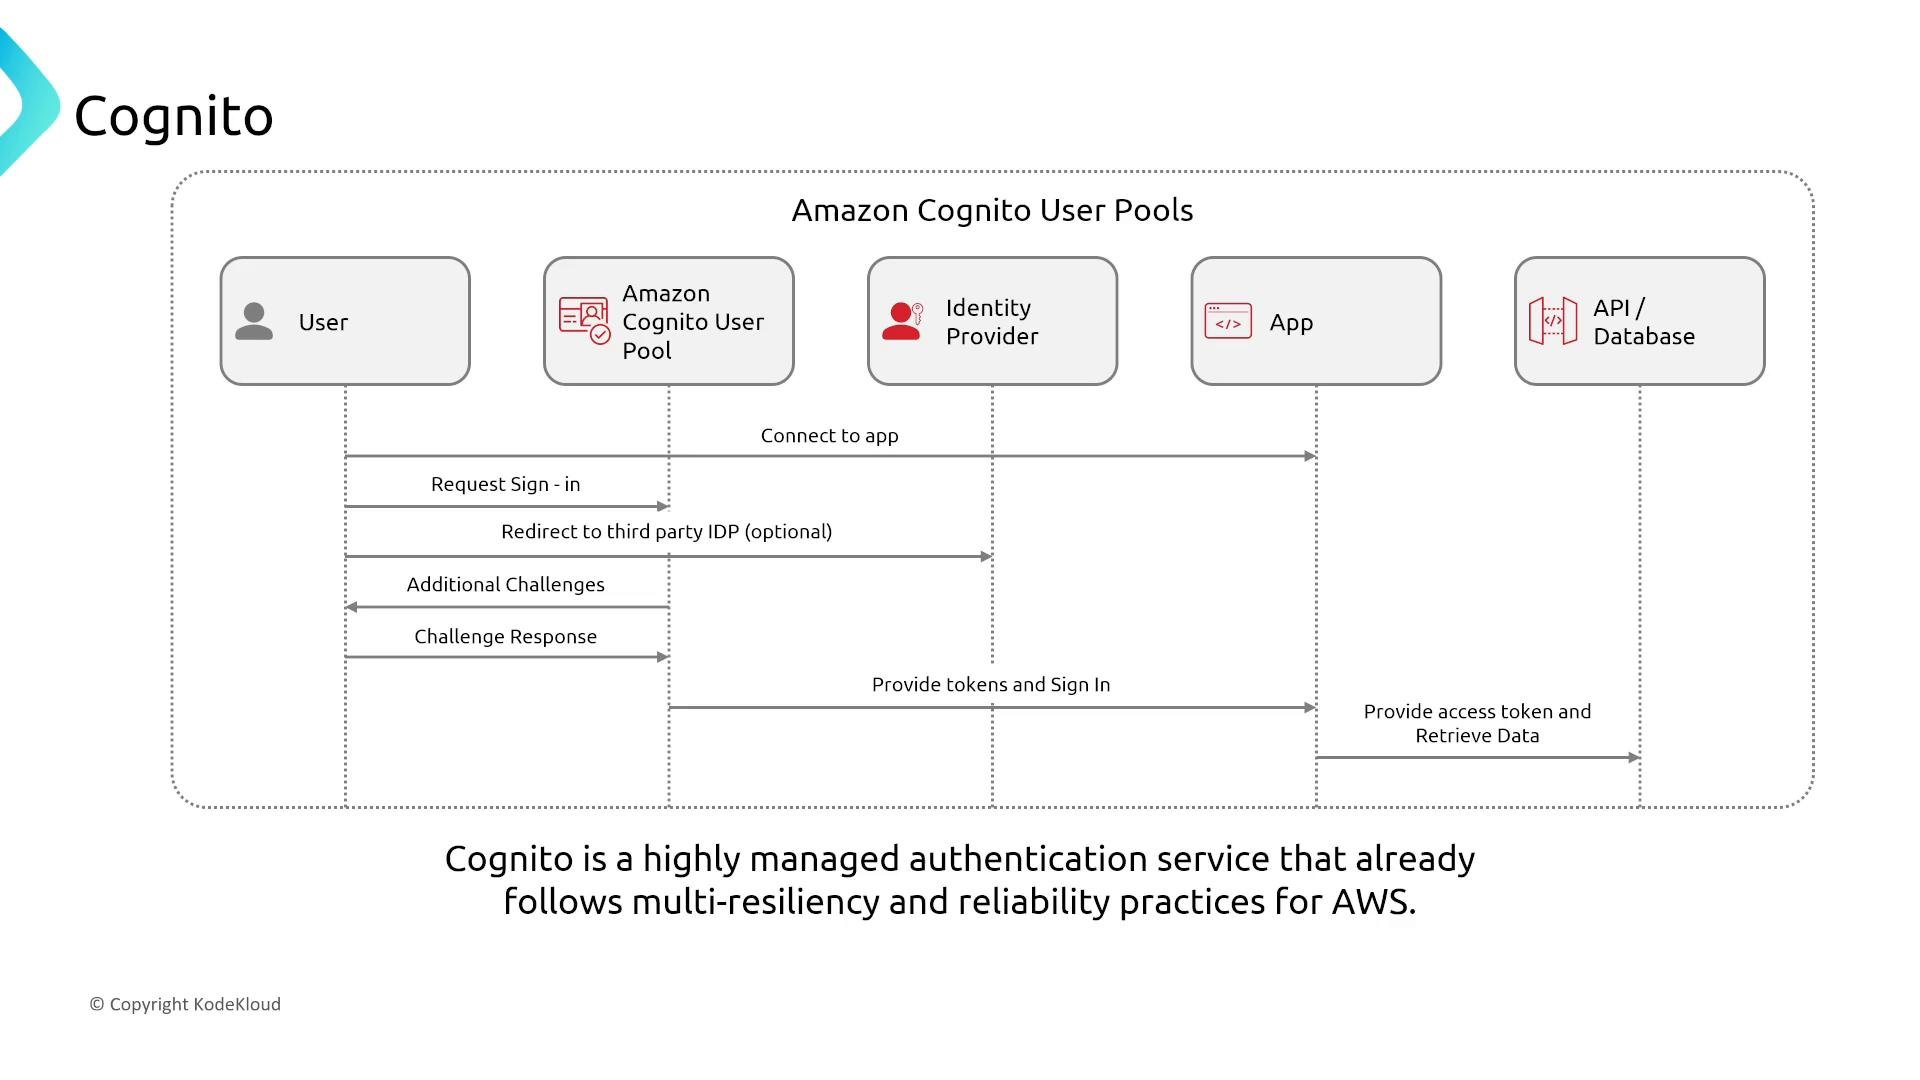
- Amazon Cognito: A highly managed authentication solution (user pools, federated sign-in, tokens). Cognito follows AWS resiliency best practices (multi‑AZ, managed failover).
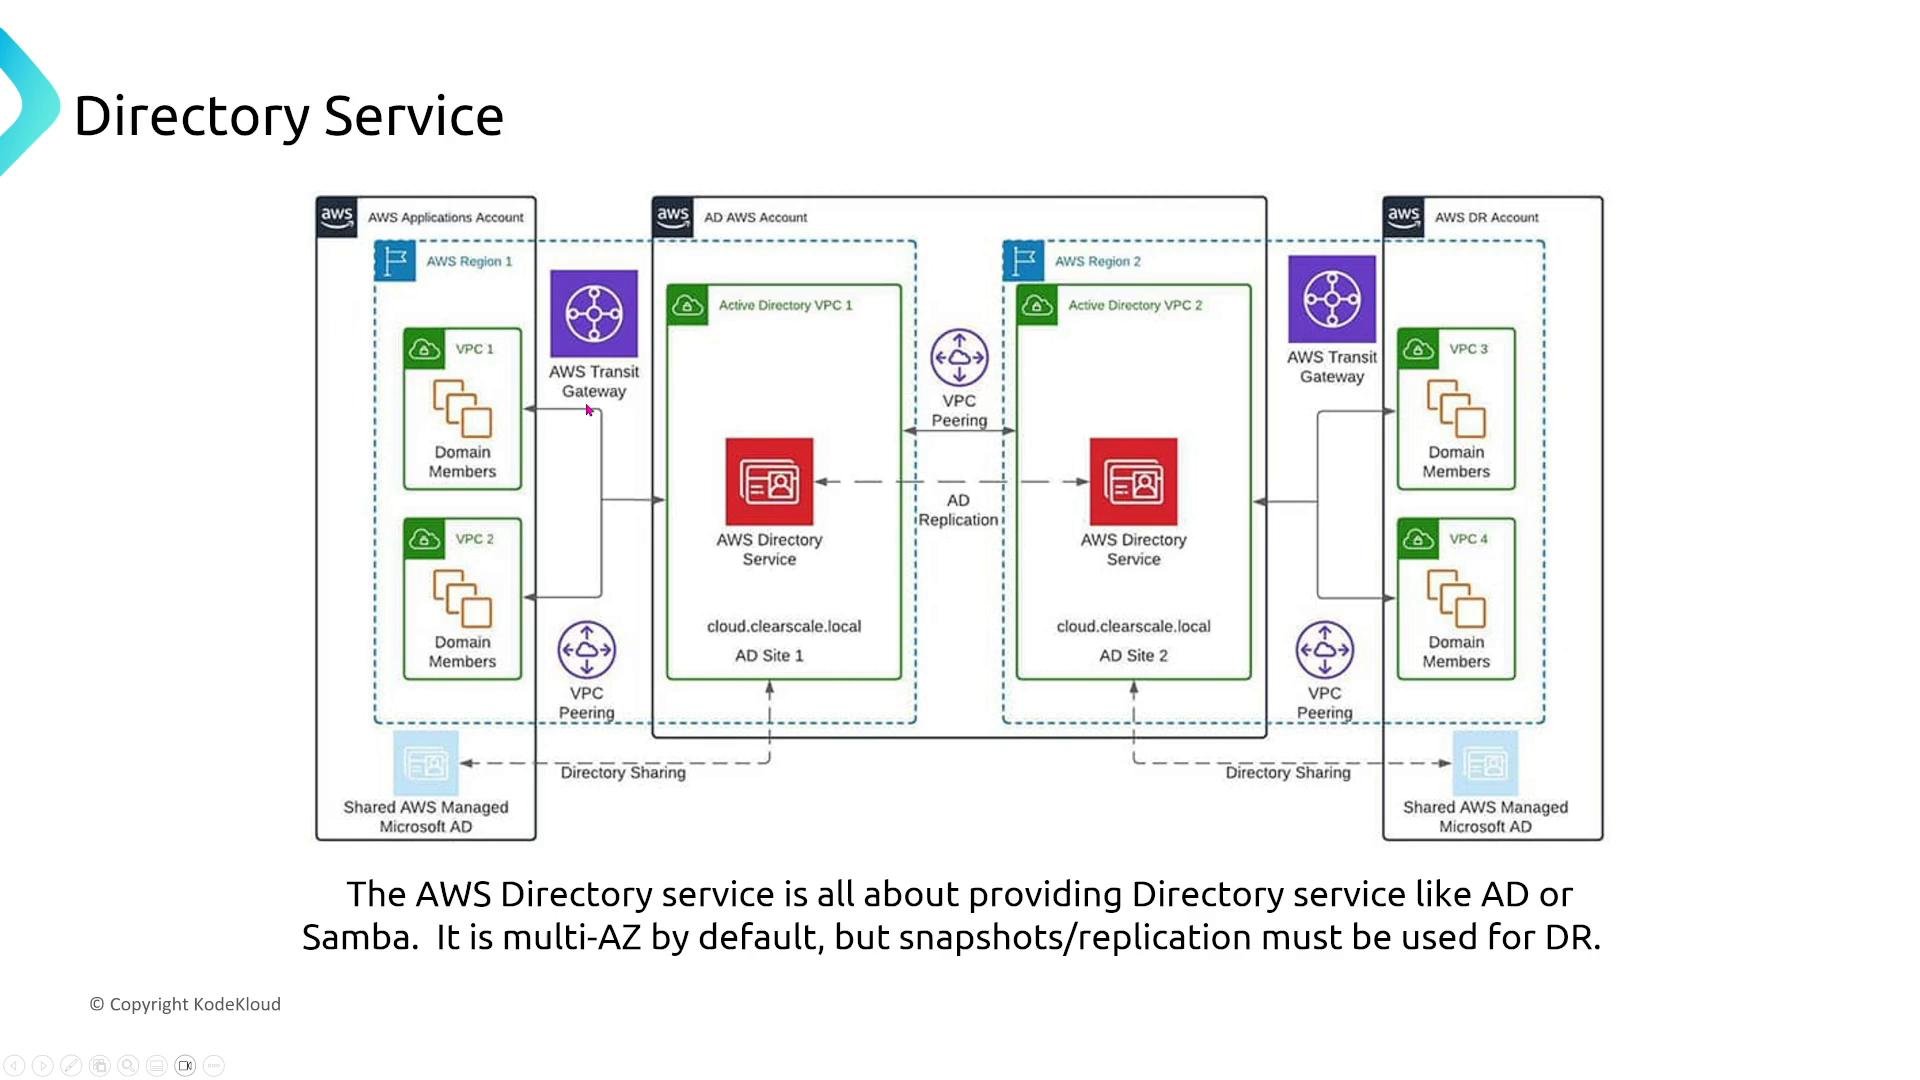
- Directory Service (AWS Managed Microsoft AD): Deployed Multi‑AZ in a Region by default. For cross‑Region disaster recovery, configure AD replication or deploy additional directory instances in other Regions.
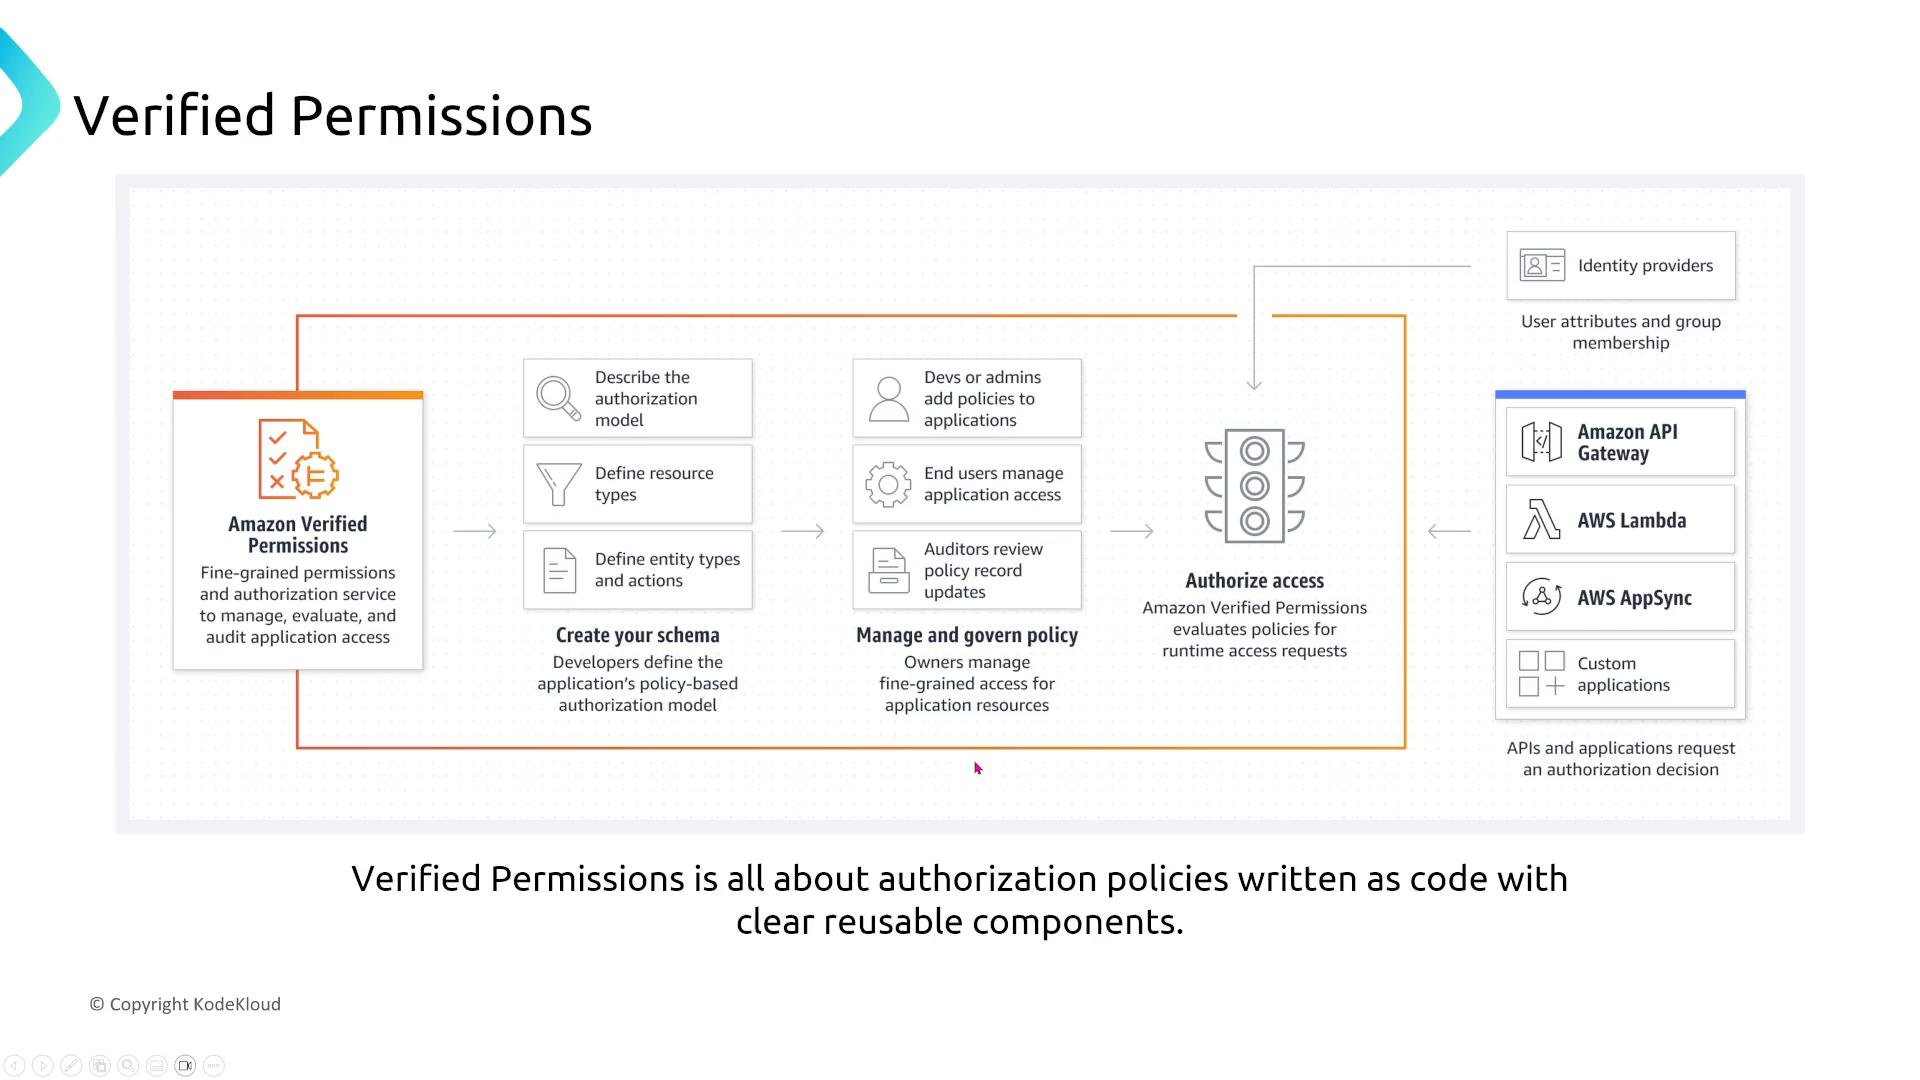
- Verified Permissions (policy-as-code): Focuses on correctness, governance, and runtime authorization integration. Reliability considerations are about ensuring authorization workflows and policy evaluation scale and are observable; the service itself is managed.
Auditing, monitoring, and telemetry
- CloudTrail: Captures API activity. Service resilience is AWS-managed. You should design alerts, EventBridge rules, and CloudWatch alarms to surface important API events and automate responses.
- AWS Config: Managed, redundant service for configuration monitoring and compliance detection — use its outputs to detect drift and automate remediation.
- AWS Artifact: Provides compliance documents — no customer-managed availability knobs.
Threat detection and scanning
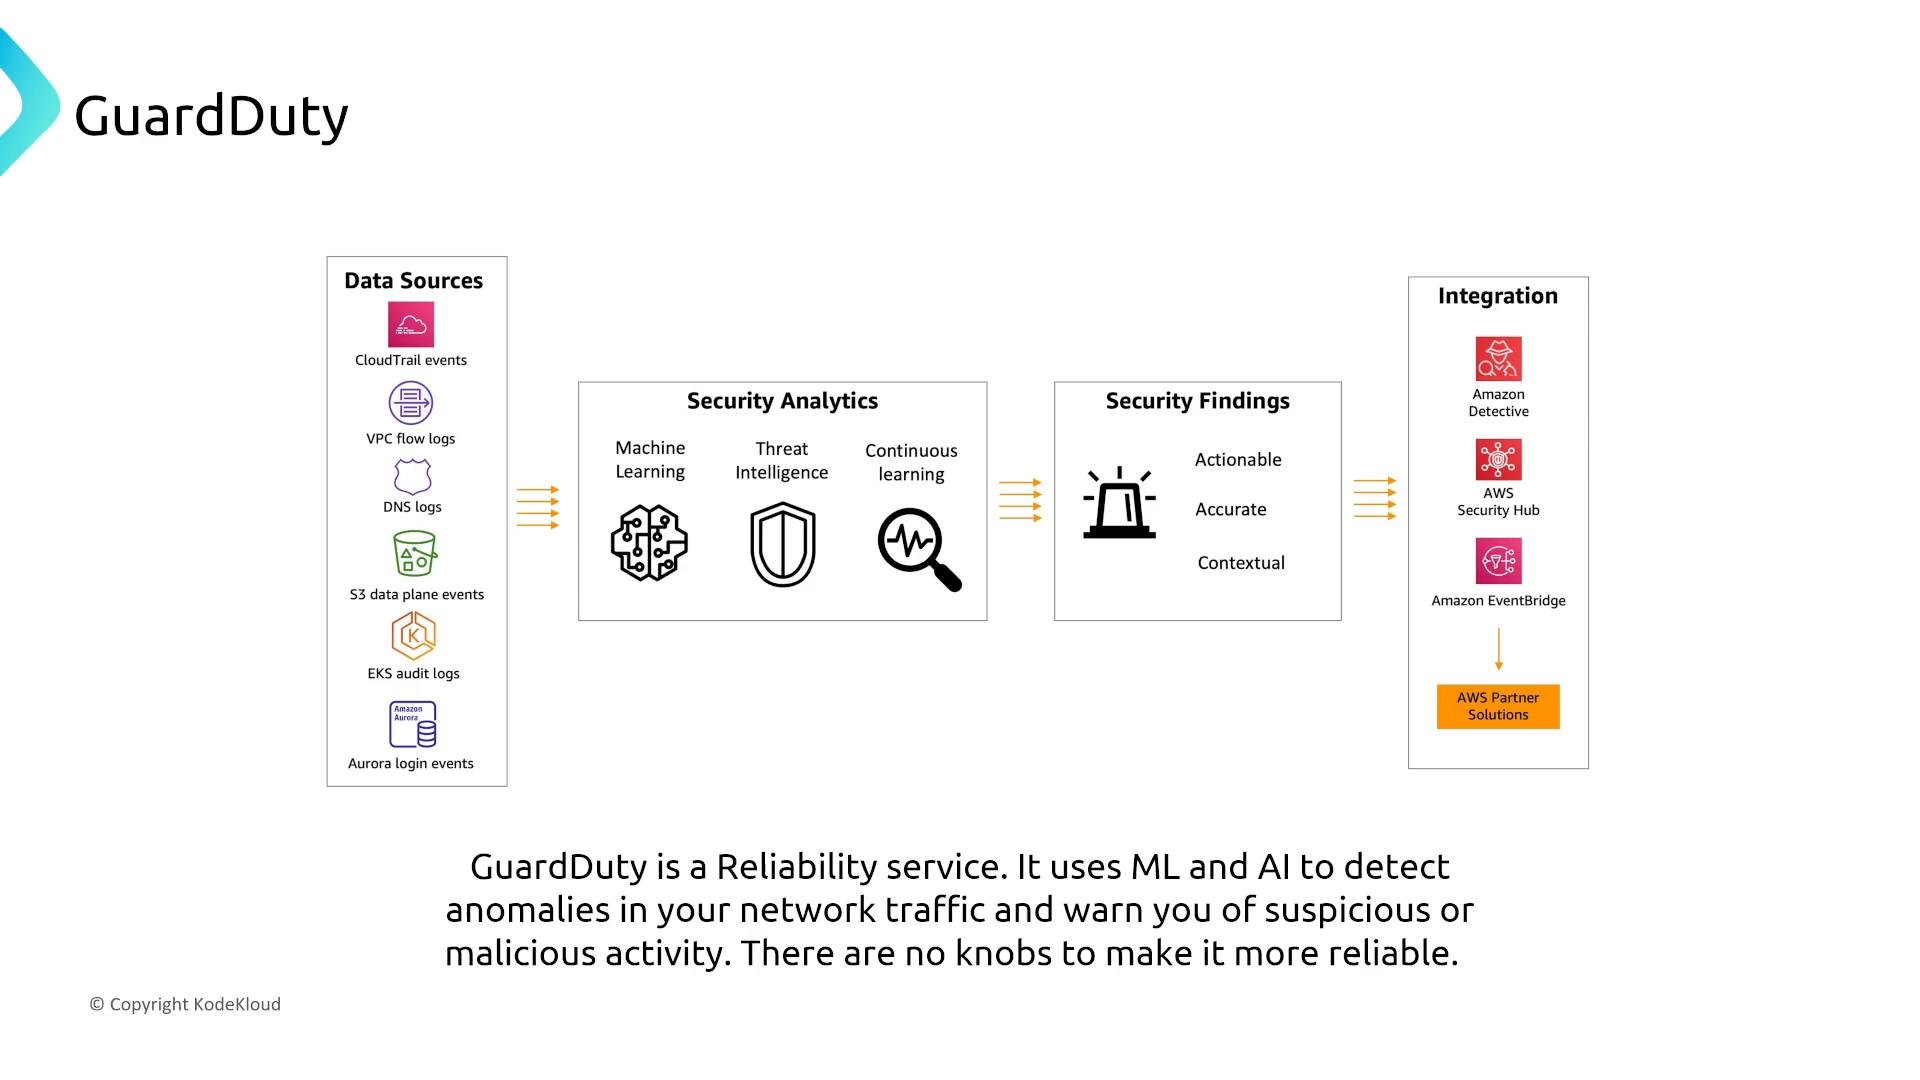
- Amazon GuardDuty: Managed threat detection that ingests CloudTrail, VPC Flow Logs, DNS logs, S3 data events, and more. Highly available and designed for continuous detection.
- Amazon Inspector, Amazon Macie: Managed scanning and data classification services. Focus on integrating findings into automated remediation and incident response playbooks.
- Resilience Hub: Centralizes resiliency posture assessments. It aggregates data to help you improve detection and response but does not expose availability knobs for the underlying security tools.
Encryption and key management
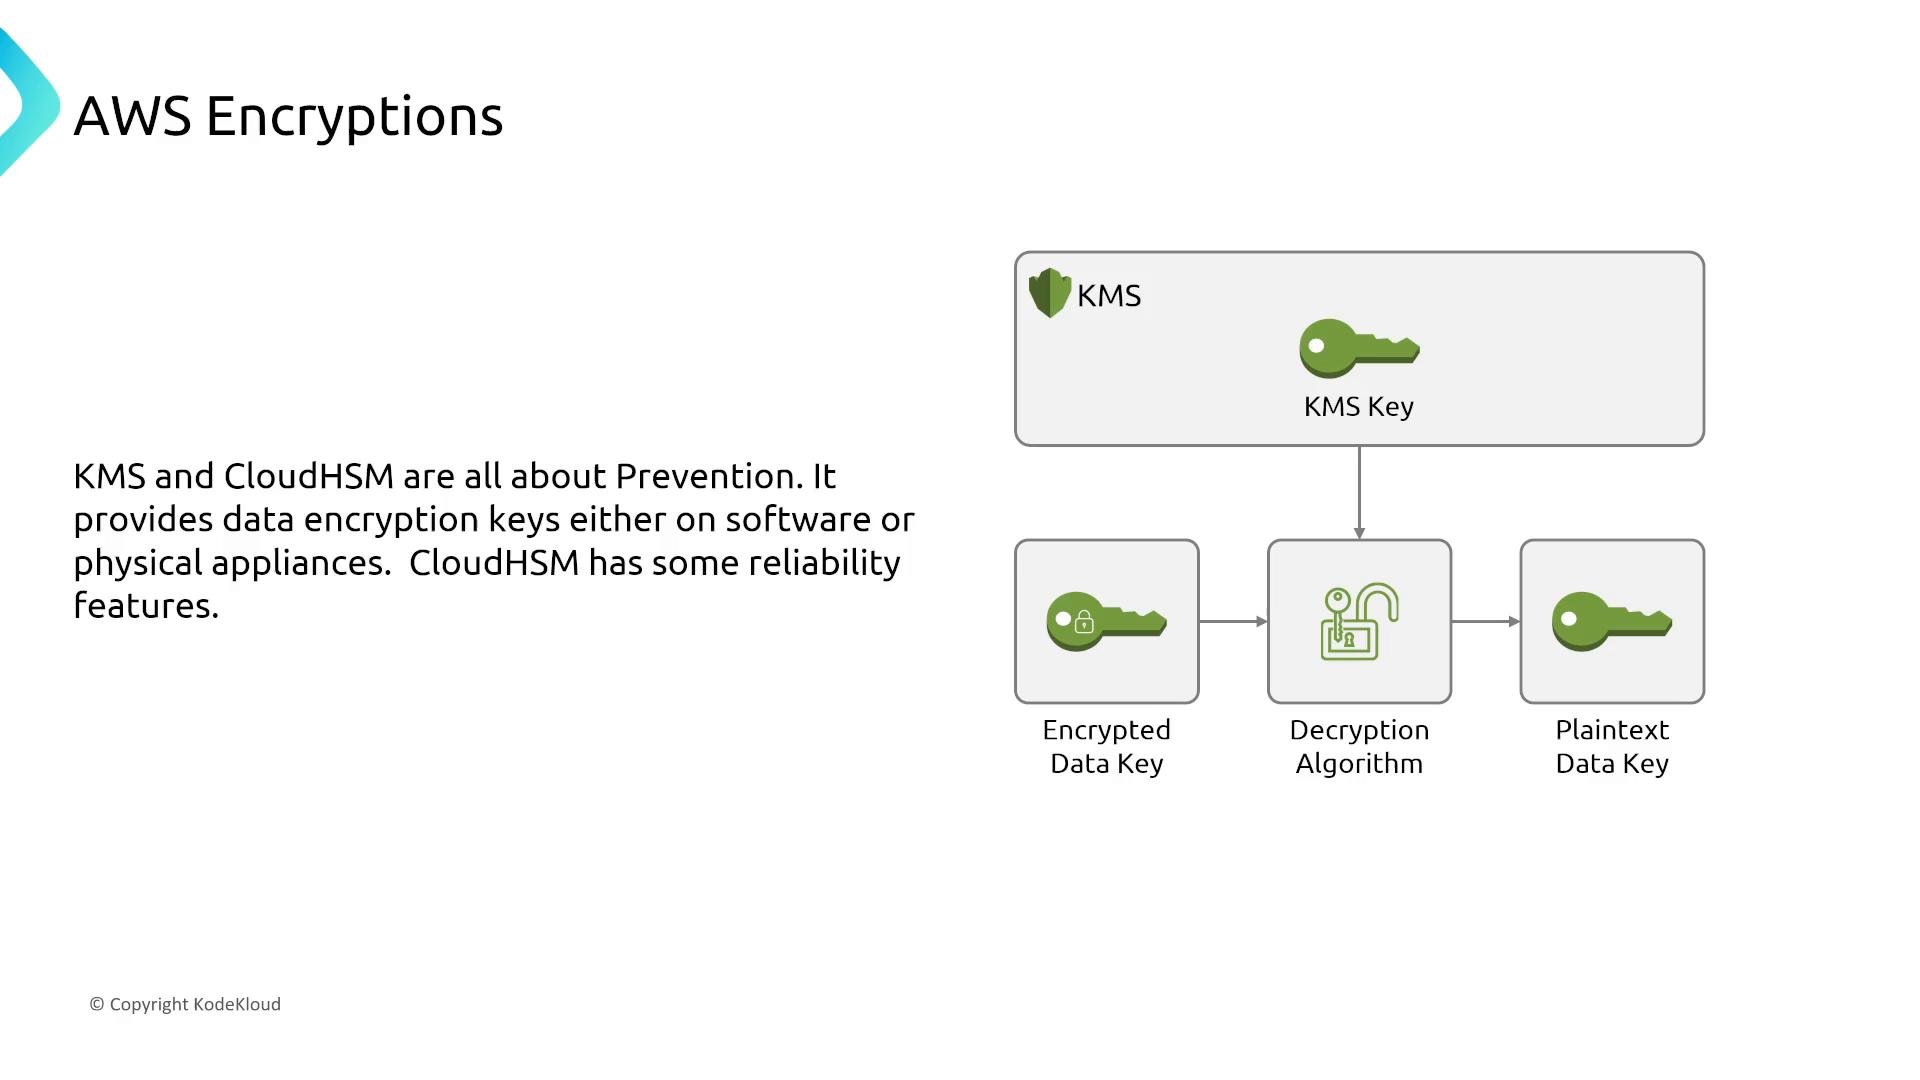
- AWS Key Management Service (KMS): Regional, highly available, AWS‑managed HSM-backed key service. AWS manages availability; design around key usage patterns and cross‑Region replication of encrypted data rather than KMS internals.
- AWS CloudHSM: Customer-controlled HSM cluster. Use multi‑AZ deployment and cluster configurations for redundancy. You manage cluster lifecycle, backups, and recovery operations.
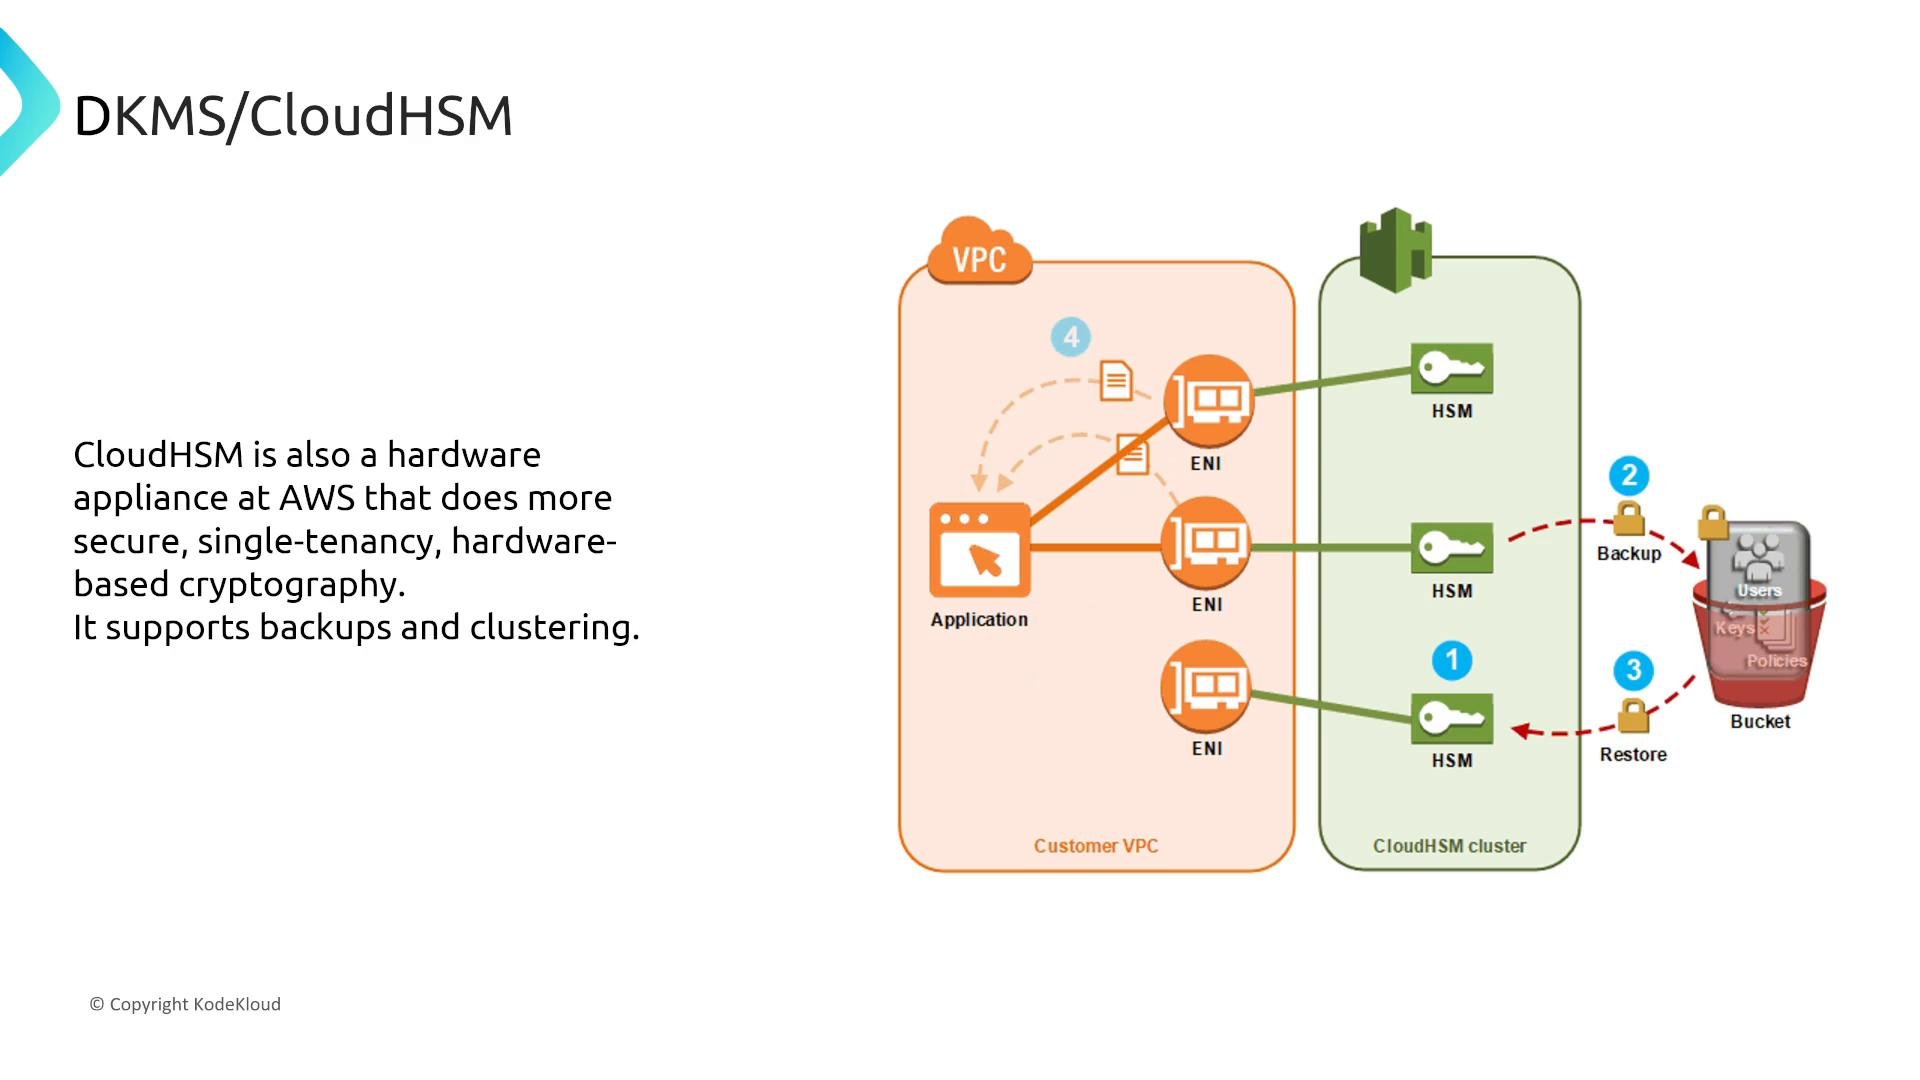
If you choose CloudHSM to retain full control of key material, plan for operational overhead: multi‑AZ cluster design, automated backups (to encrypted S3), monitoring for node health, and documented recovery procedures.
Certificates and private PKI
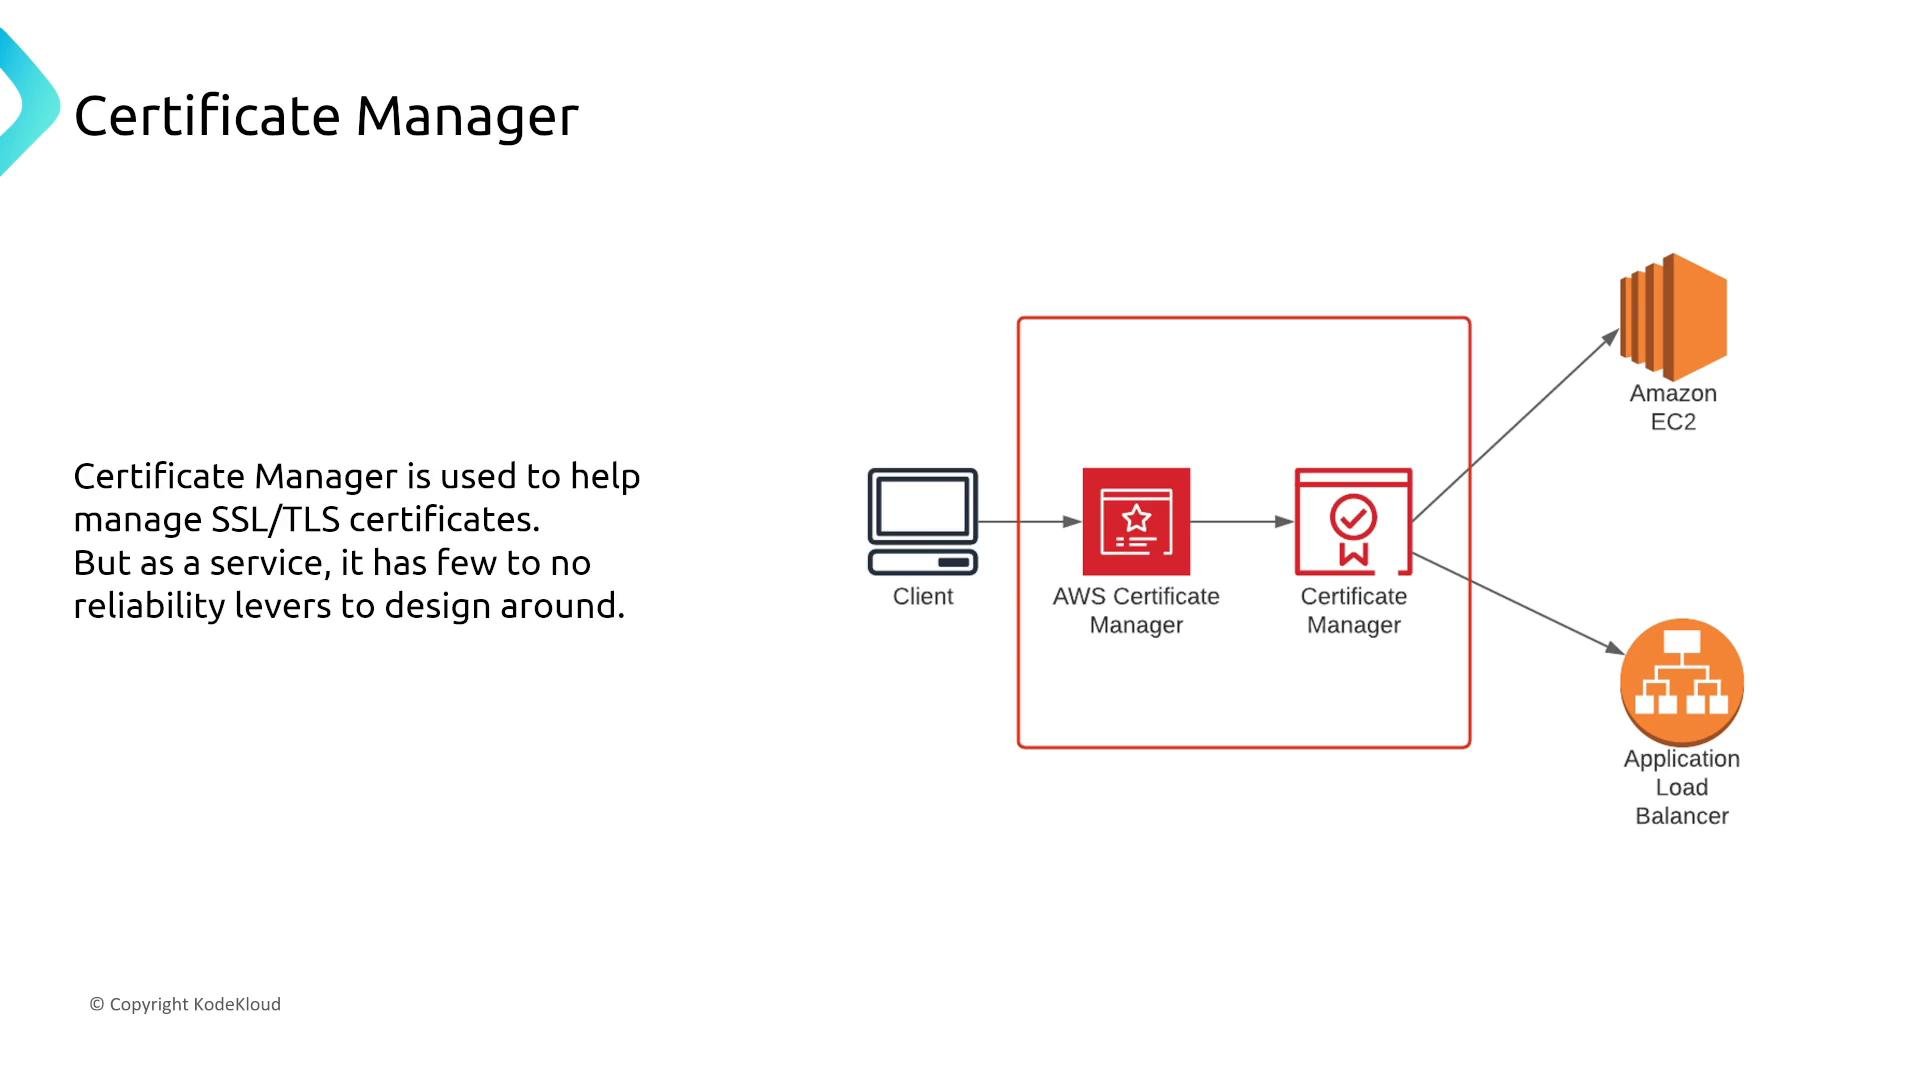
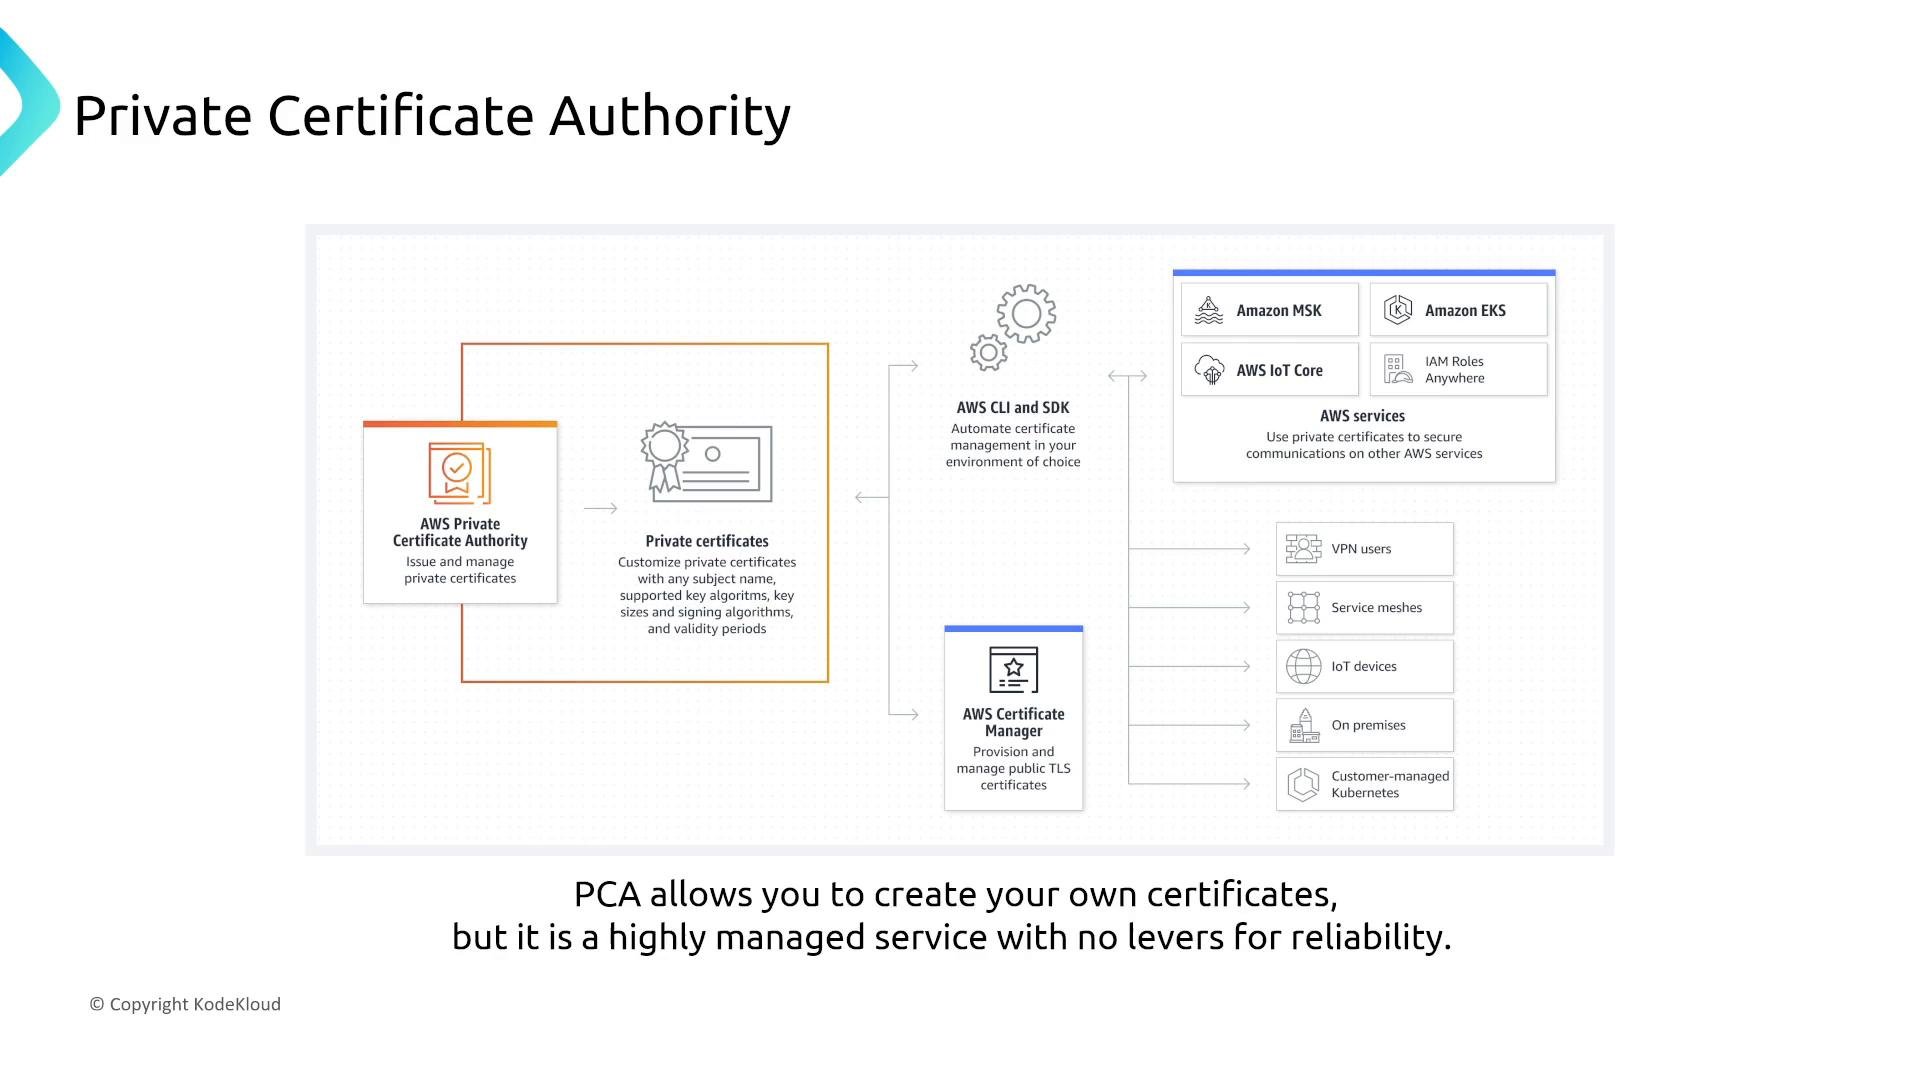
- AWS Certificate Manager (ACM): Fully managed certificate issuance and renewal. Availability is managed by AWS.
- AWS Private Certificate Authority (Private CA): Managed private PKI. High availability is provided by AWS; focus on certificate lifecycles and automation.
Secrets and cross‑Region resilience
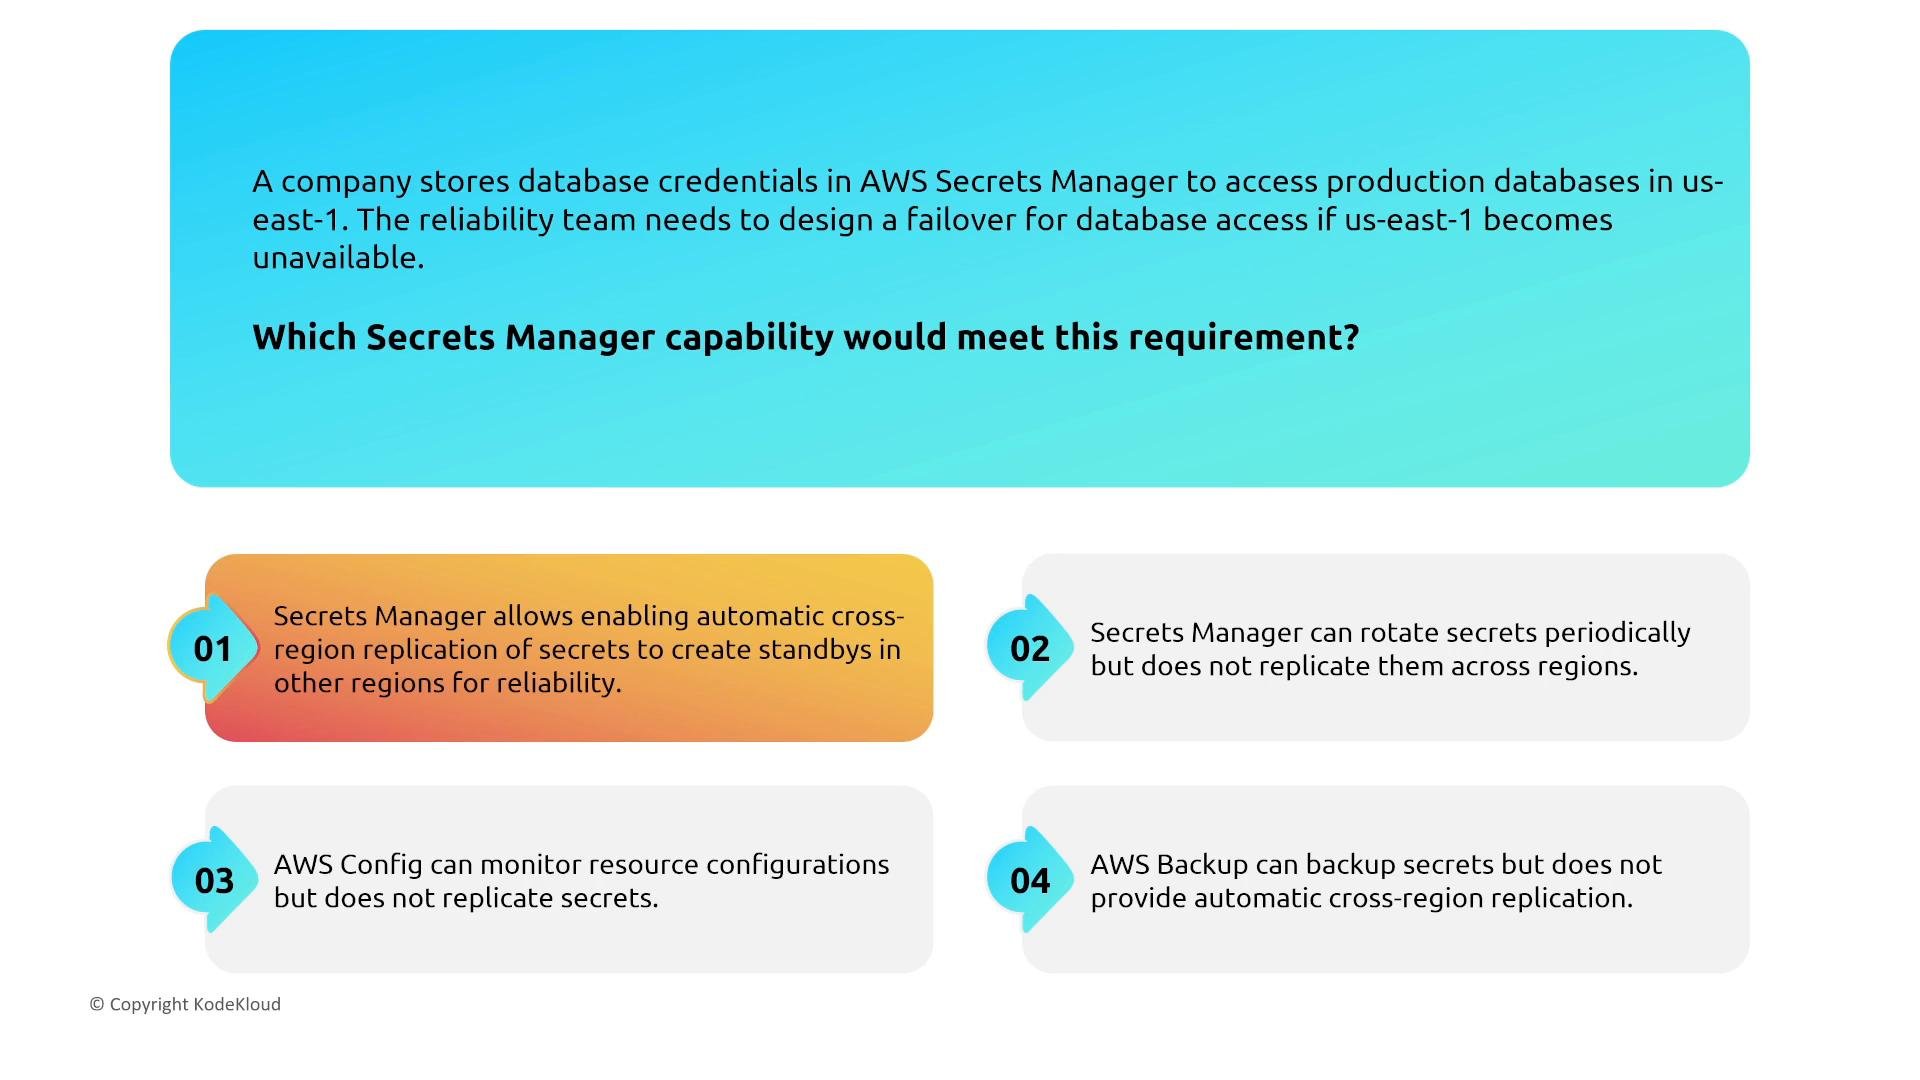
- AWS Secrets Manager: Stores, rotates, and optionally replicates secrets. Default operation is highly available within a Region; Secrets Manager supports automatic cross‑Region replication to create standby copies for DR scenarios.
Networking security: groups, NACLs, firewalls, and DDoS
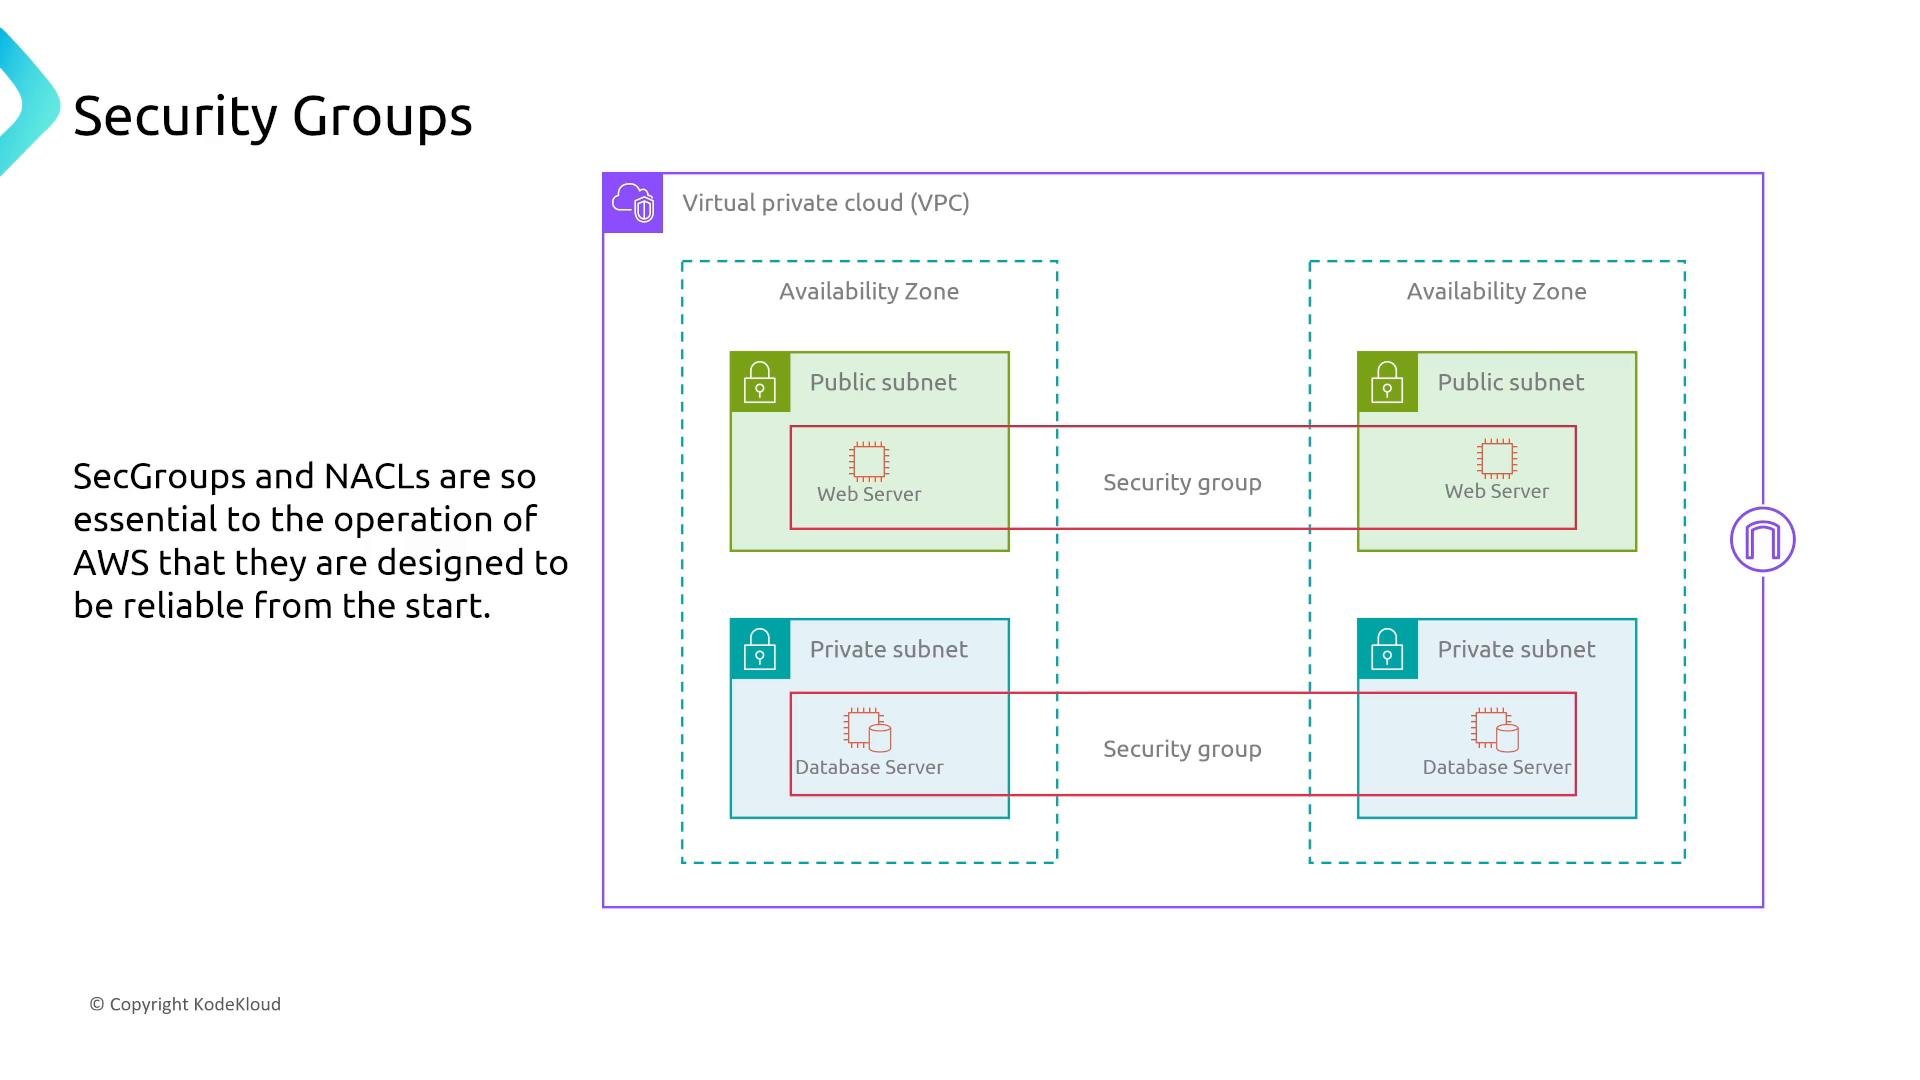
- Security Groups and Network ACLs: Native VPC controls; AWS manages their resilience as part of the VPC control plane.
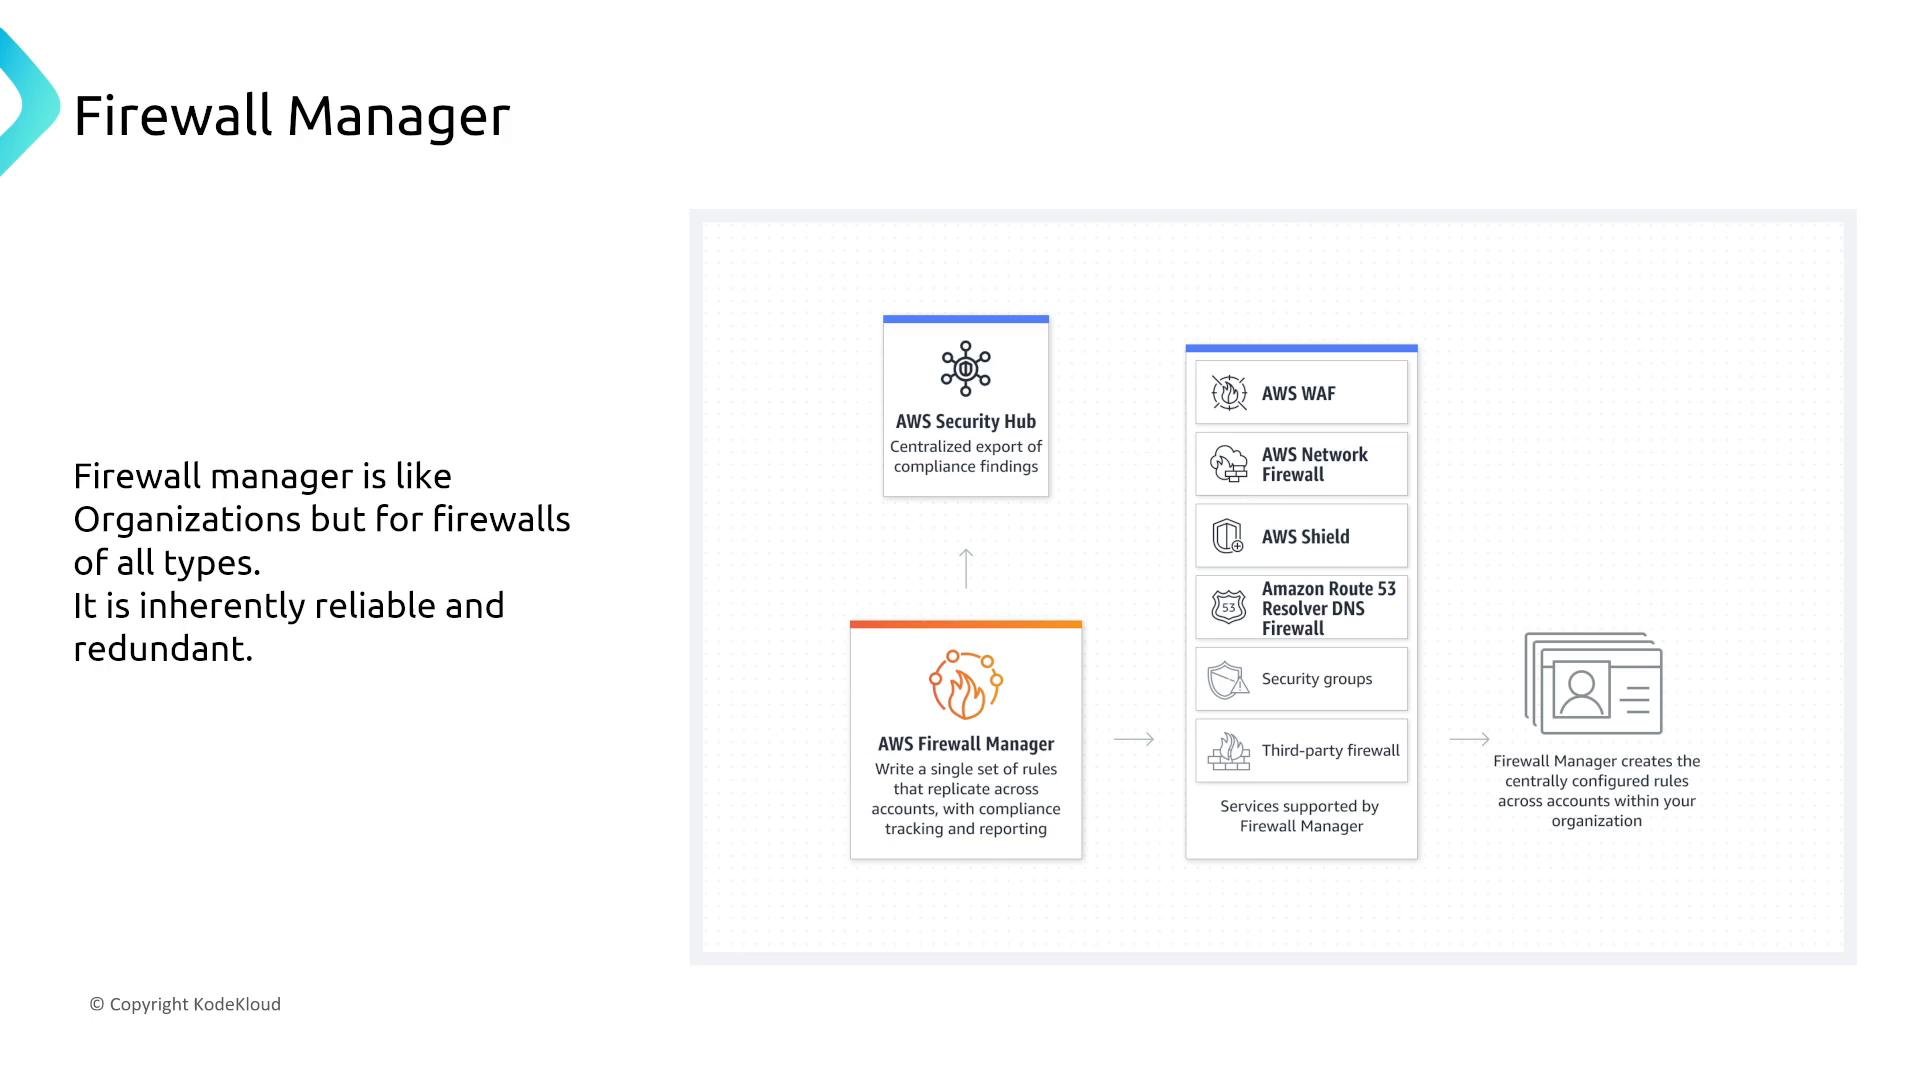
- AWS Firewall Manager: Centralized enforcement for security groups, WAF rules, Network Firewall policies, and Shield protections—helps improve operational reliability by maintaining consistency across accounts and resources.
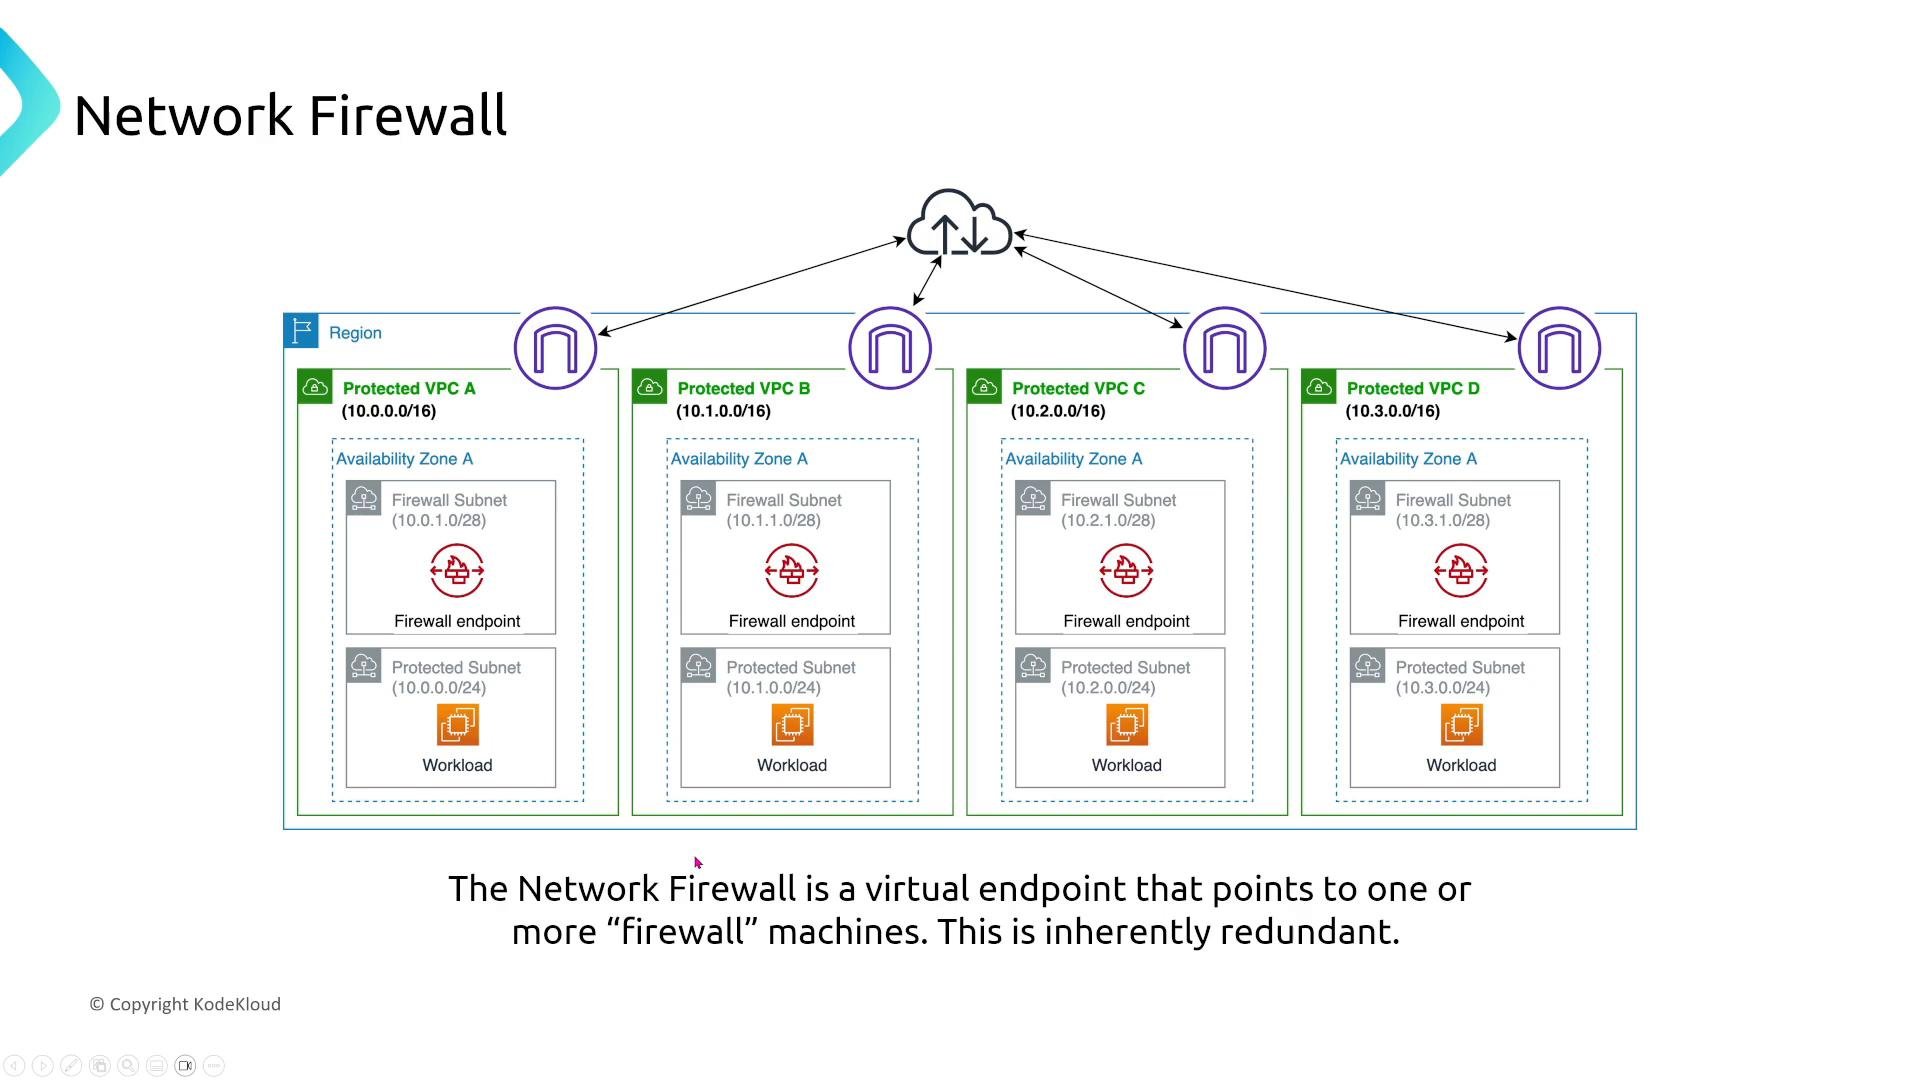
- AWS Network Firewall: Managed stateful inspection for VPC traffic. Deploy across AZs in active‑active for redundancy; use Firewall Manager for centralized policy.
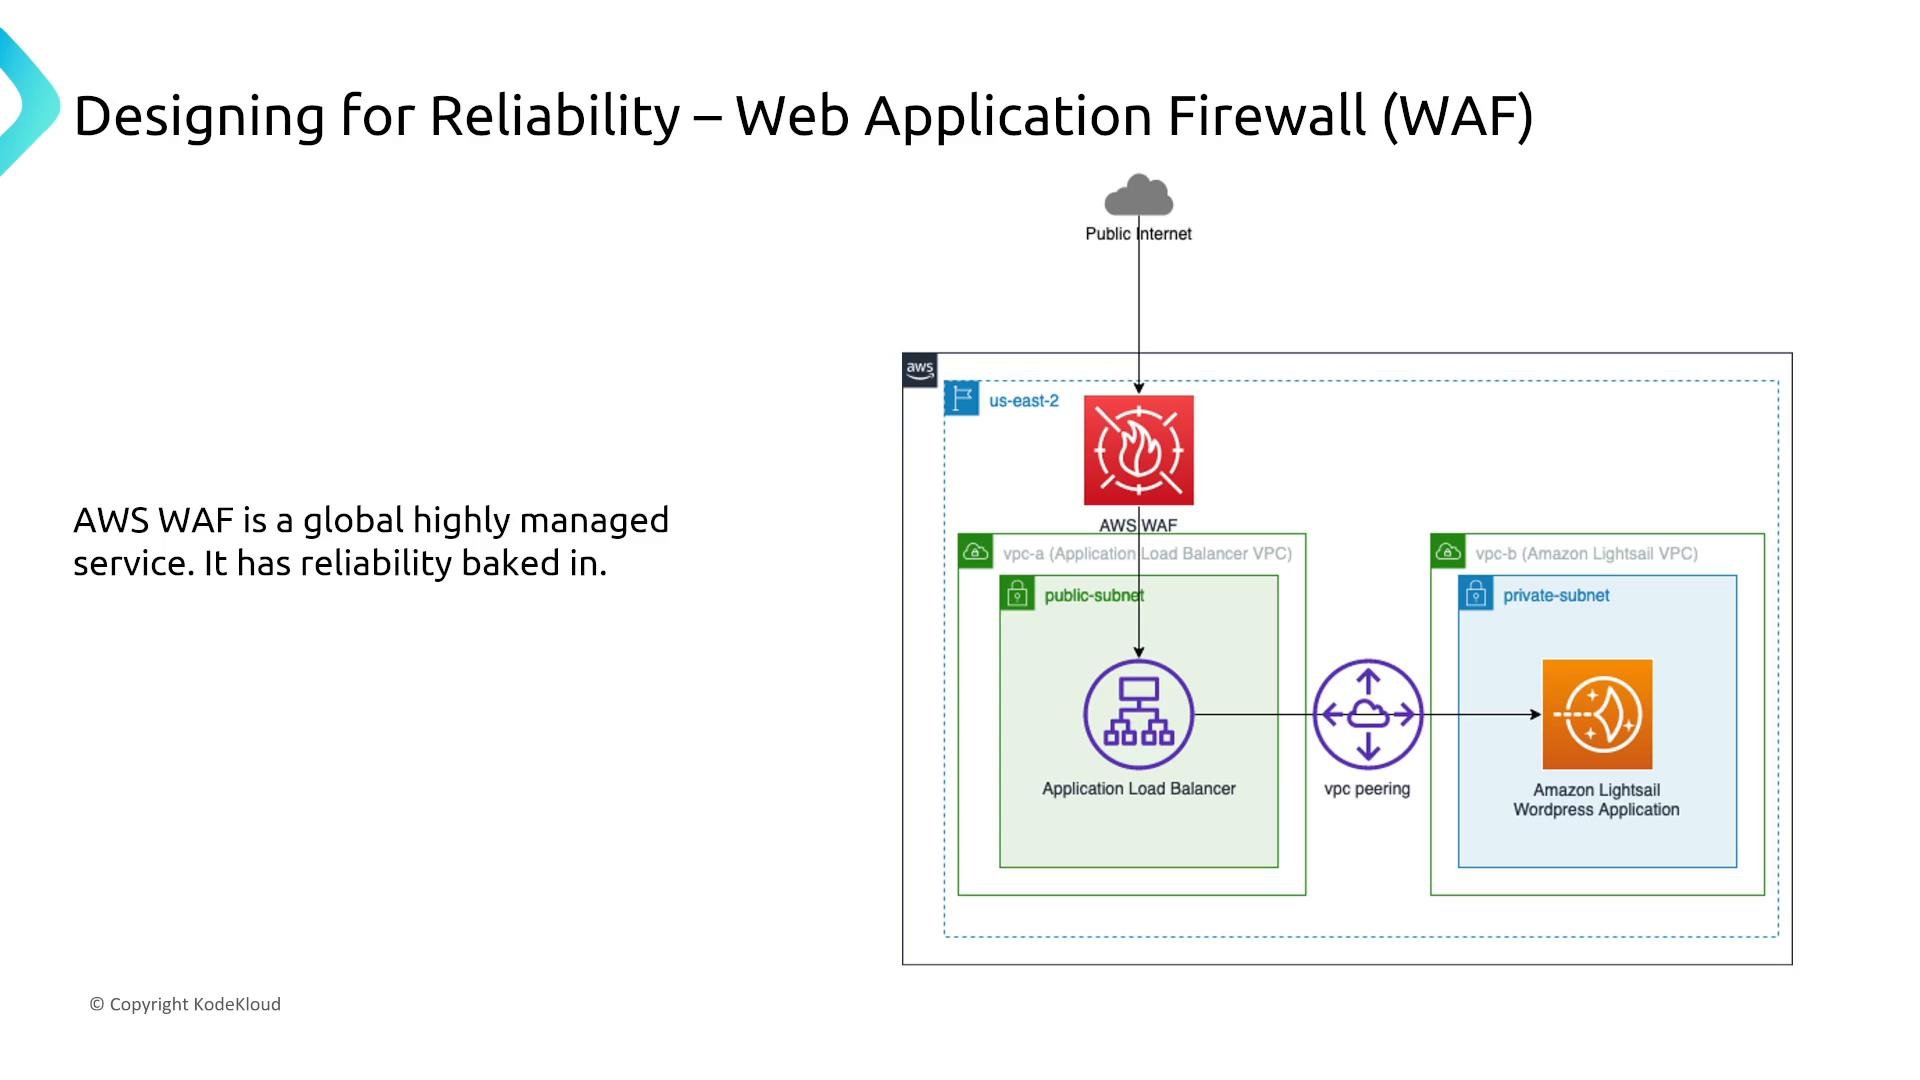
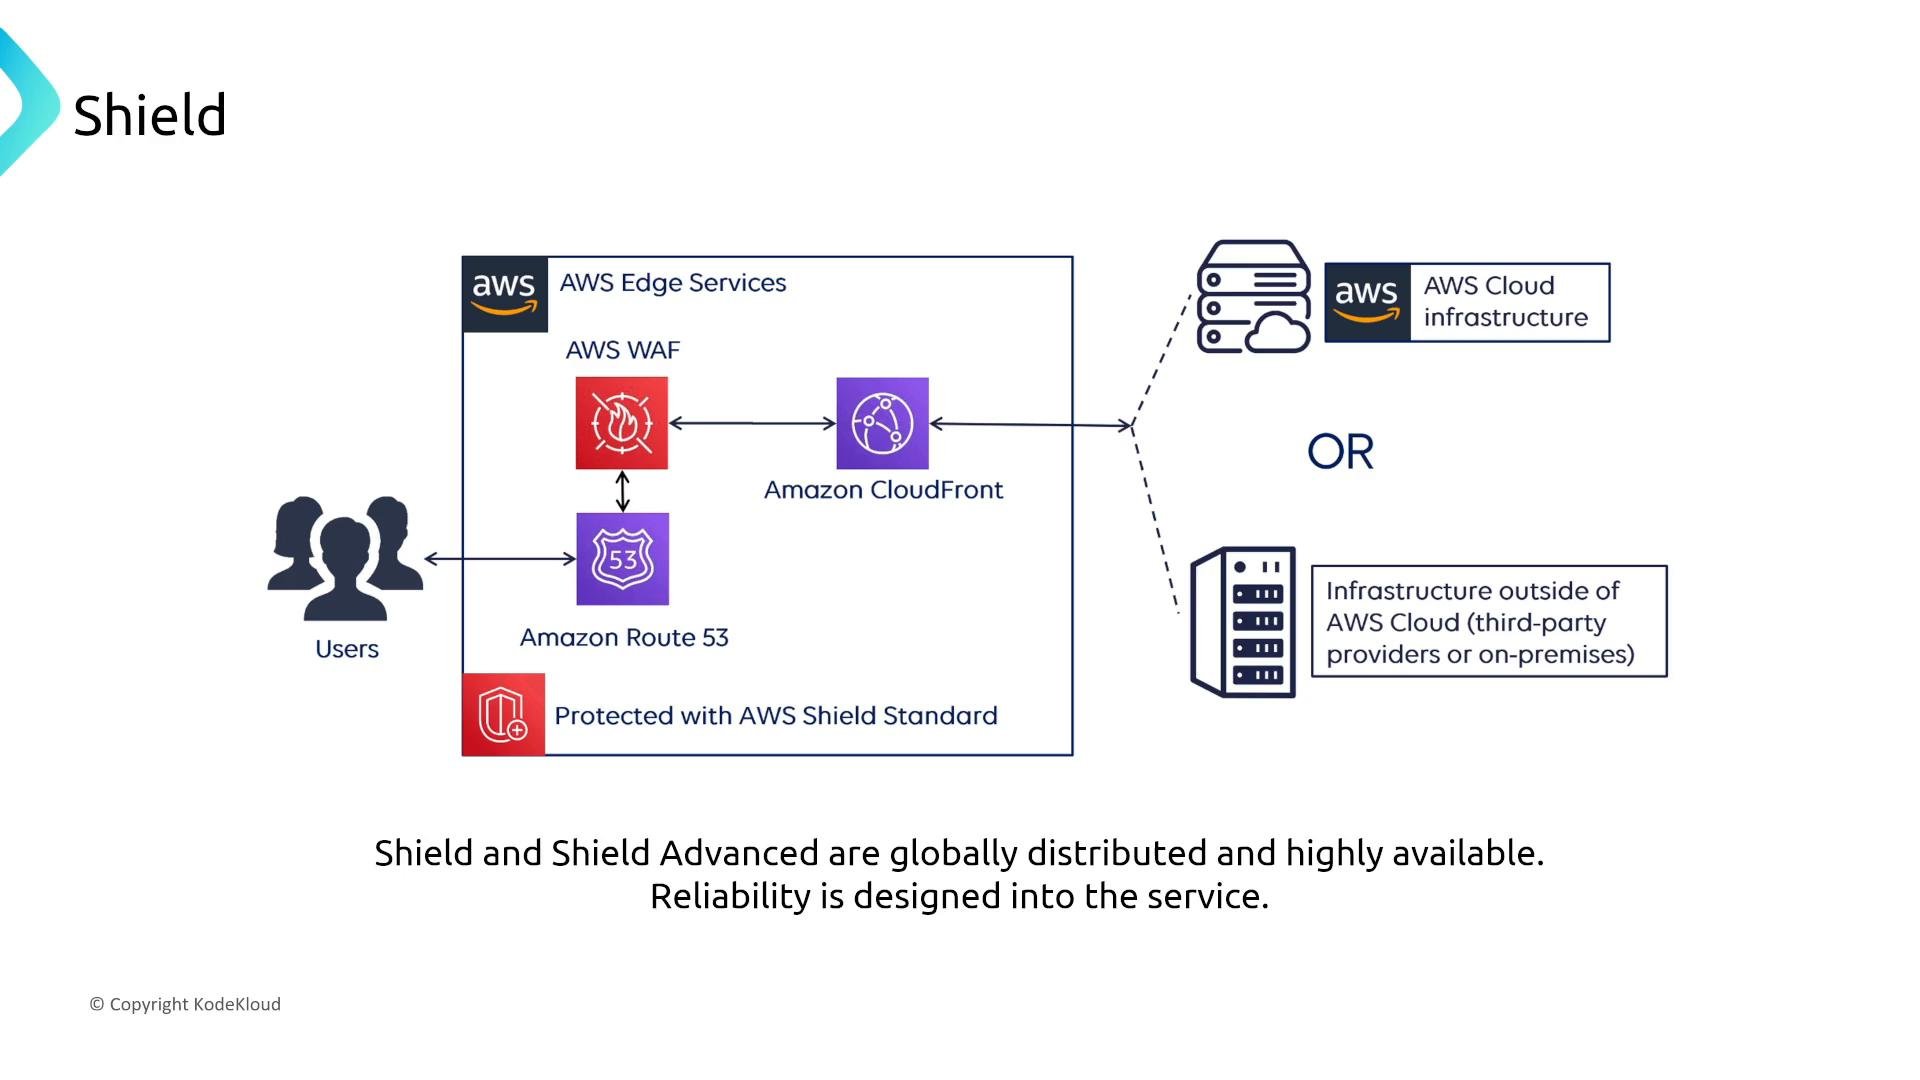
- AWS WAF: Highly available, globally distributed; deploy at CloudFront edge for global coverage, or in front of regional endpoints (ALB, API Gateway).
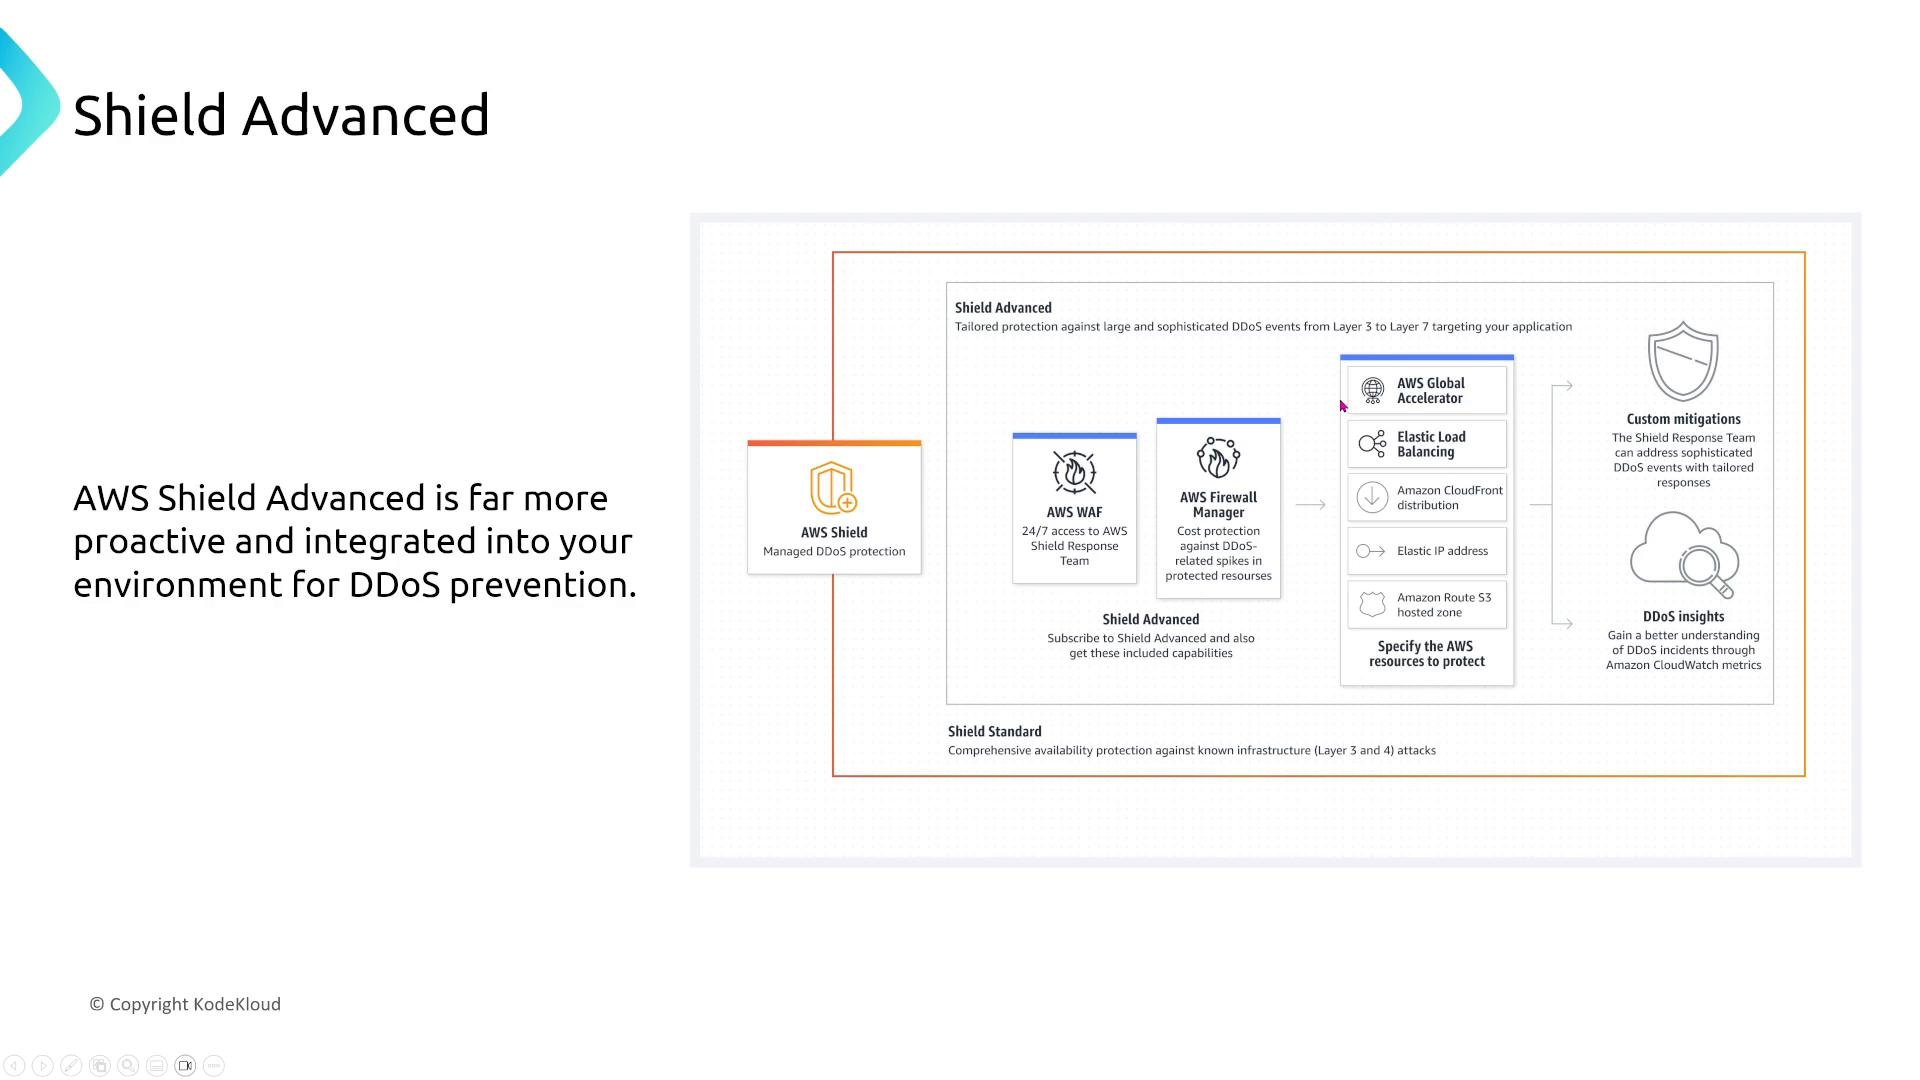
- AWS Shield: Shield Standard provides baseline DDoS protection at no cost; Shield Advanced is a paid service with enhanced mitigations, DRT access, and Firewall Manager/WAF integrations for high‑risk workloads.
Centralized telemetry and investigations
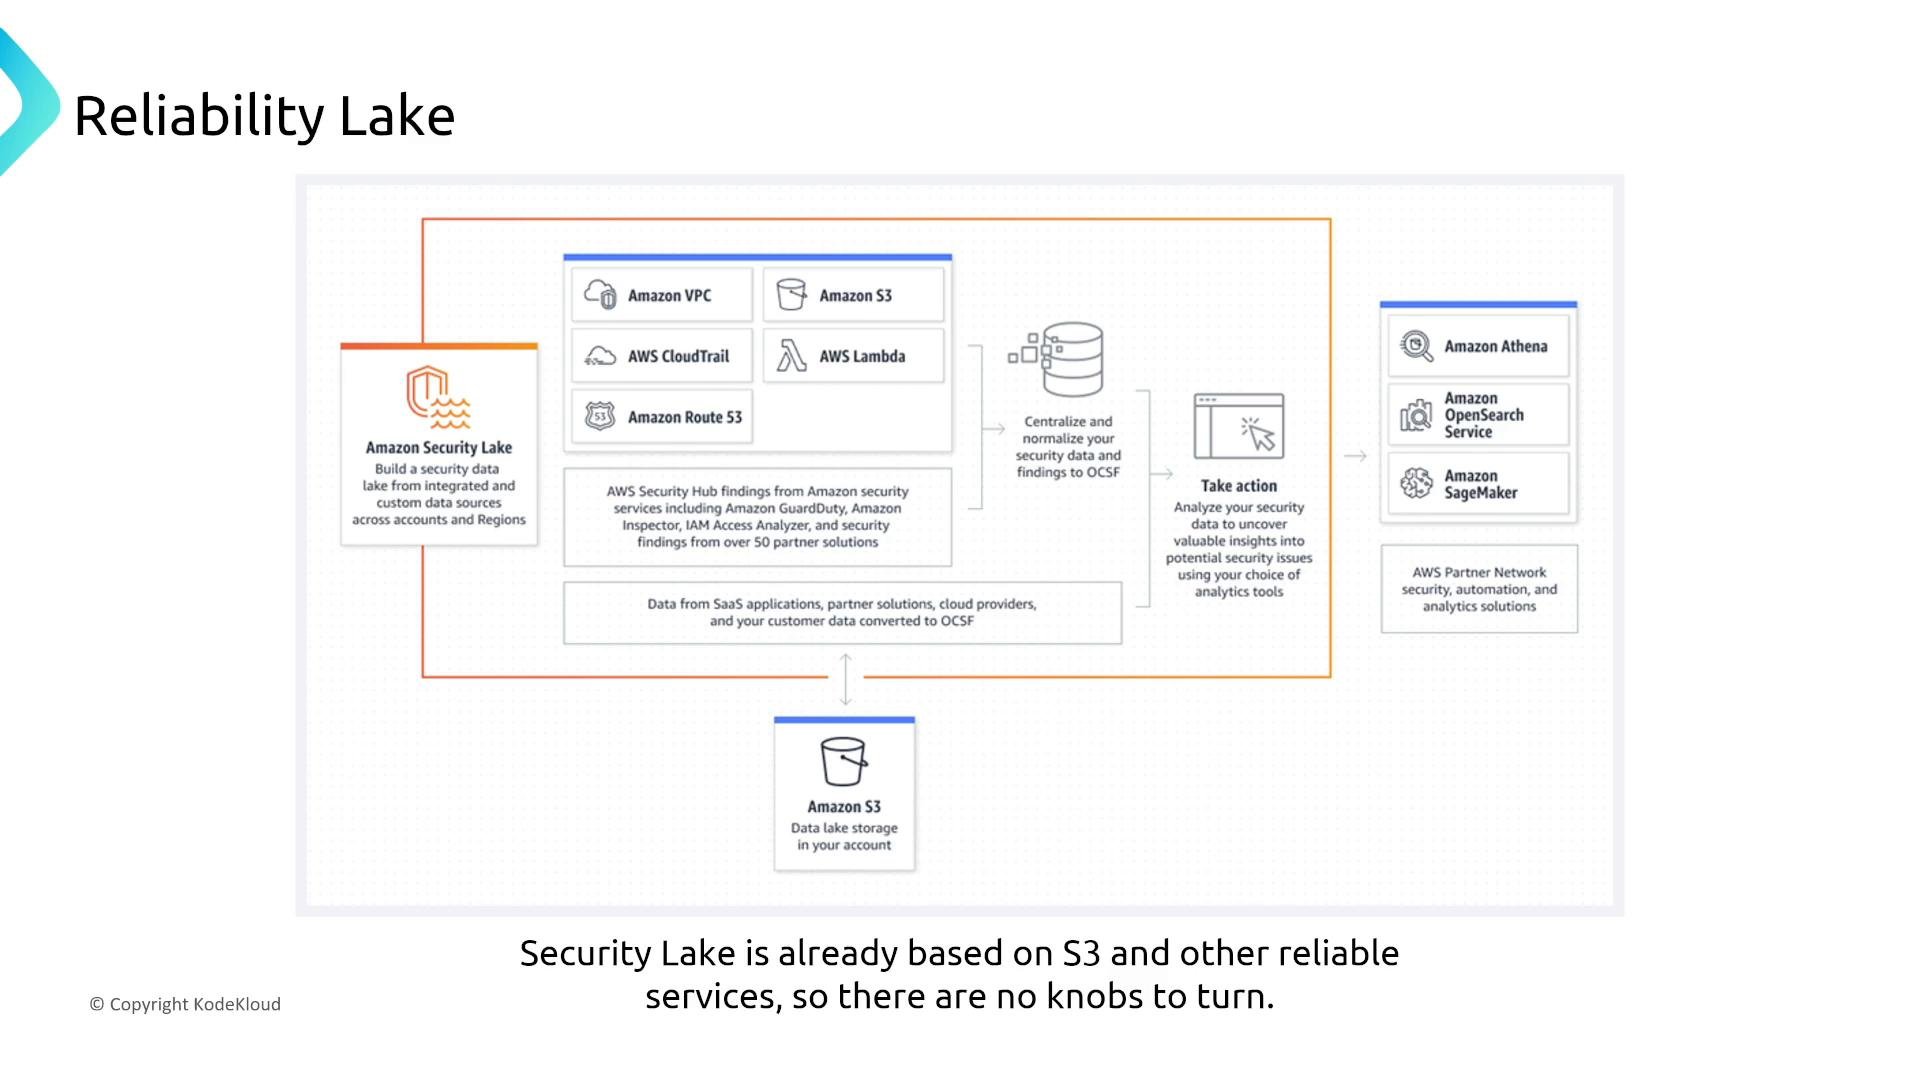
- Amazon Security Lake: Aggregates security telemetry into an S3-based data lake for analytics (Athena, OpenSearch, SageMaker) and security tools. Security Lake is managed and provides centralized data to improve detection, investigation, and recovery workflows.
Quick reference table — Service reliability models and customer controls
Key takeaways
- Many AWS security services are fully managed and designed for availability — you often won’t have direct “reliability knobs.”
- When controls exist, they usually involve: enabling multi‑AZ or cross‑Region replication, deploying clustered hardware (CloudHSM), or creating standby copies (Secrets Manager).
- Focus on integration: centralize telemetry into CloudTrail, CloudWatch, Security Hub, and Security Lake; build event-driven detection/remediation using EventBridge, Lambda, and automated runbooks.
- Use centralized policy and governance tools (Firewall Manager, Verified Permissions) to improve operational consistency and reliability across accounts.
Links and references
- IAM: https://docs.aws.amazon.com/iam/
- Amazon Cognito: https://docs.aws.amazon.com/cognito/
- AWS Directory Service: https://docs.aws.amazon.com/directoryservice/
- AWS KMS: https://docs.aws.amazon.com/kms/
- AWS CloudHSM: https://docs.aws.amazon.com/cloudhsm/
- Secrets Manager: https://docs.aws.amazon.com/secretsmanager/
- GuardDuty: https://docs.aws.amazon.com/guardduty/
- AWS WAF & Shield: https://docs.aws.amazon.com/waf/
- AWS Network Firewall: https://docs.aws.amazon.com/network-firewall/
- Amazon Security Lake: https://docs.aws.amazon.com/security-lake/