

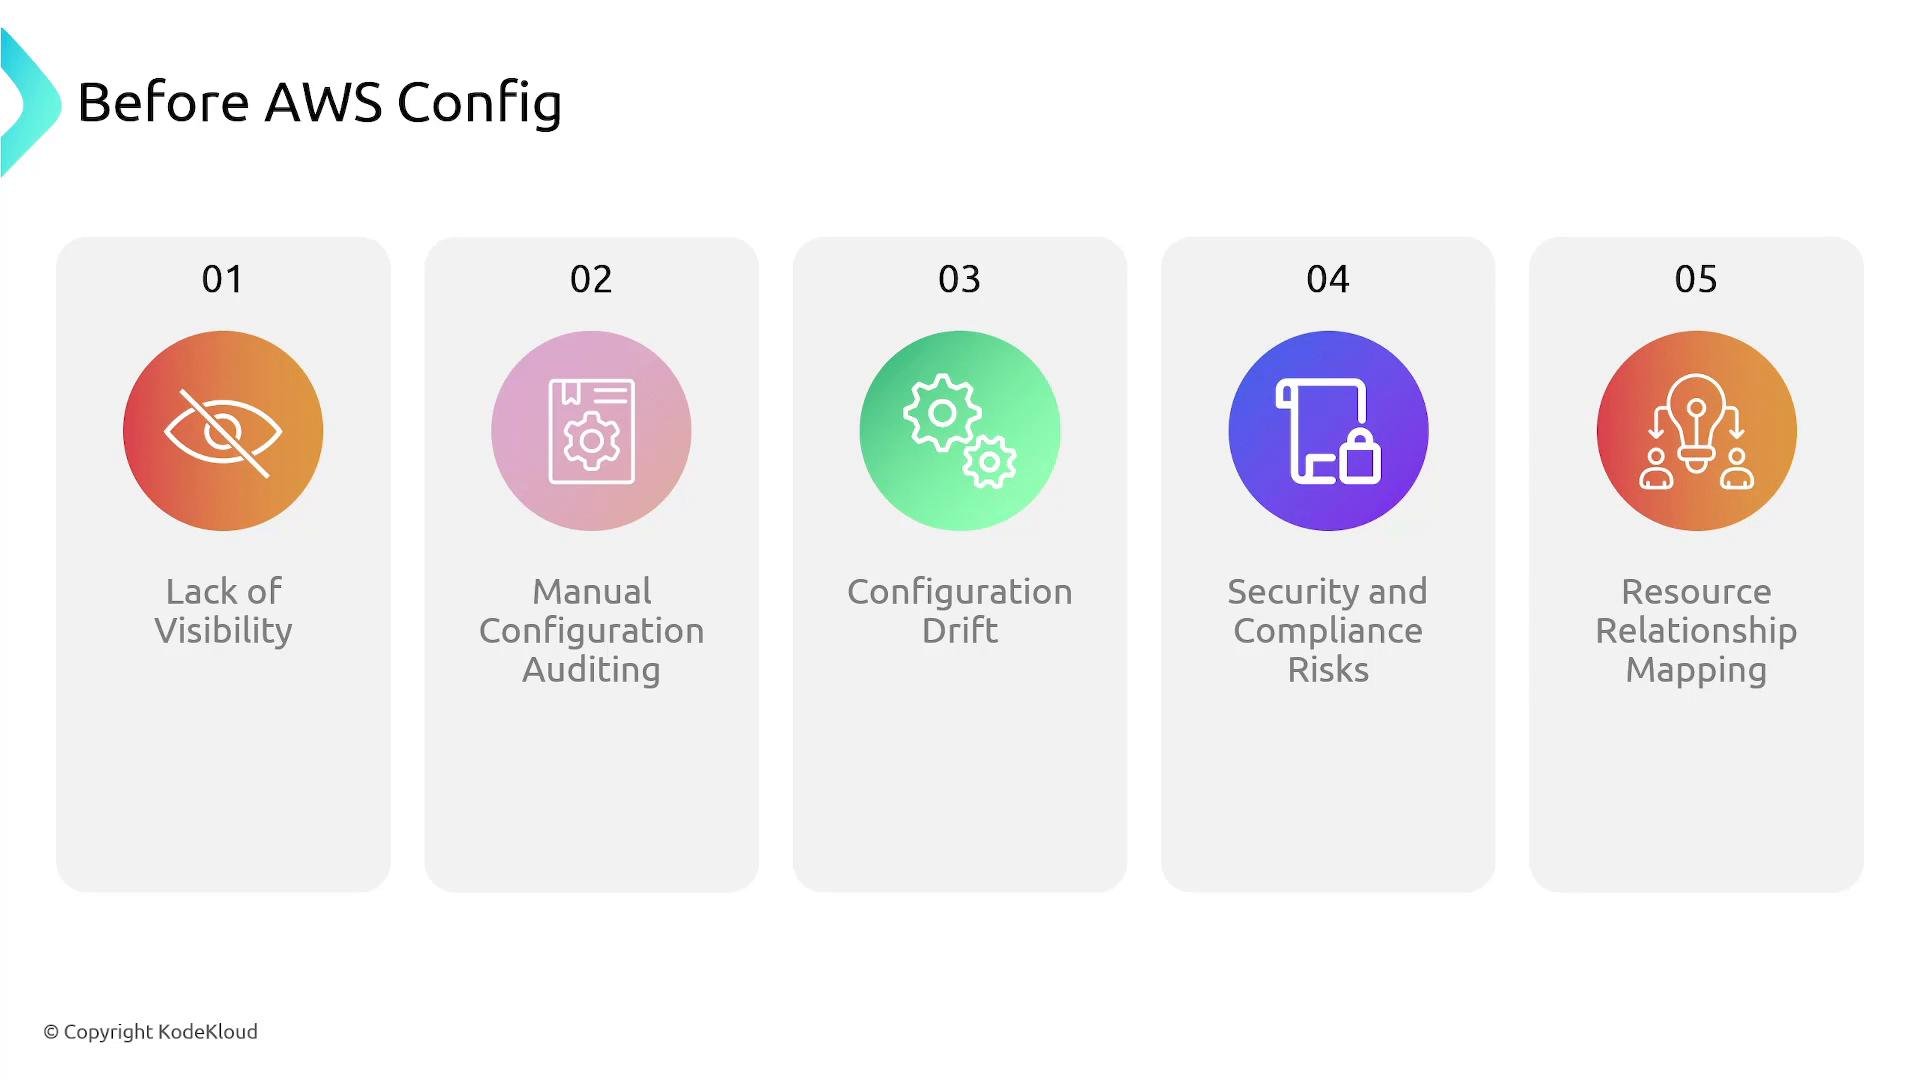
Key capabilities
You configure rules to define the desired configuration state or compliance checks. Rules can be AWS-managed or custom (Lambda-backed). When a rule detects a noncompliant resource, AWS Config generates findings, sends notifications, and can kick off automated remediation.
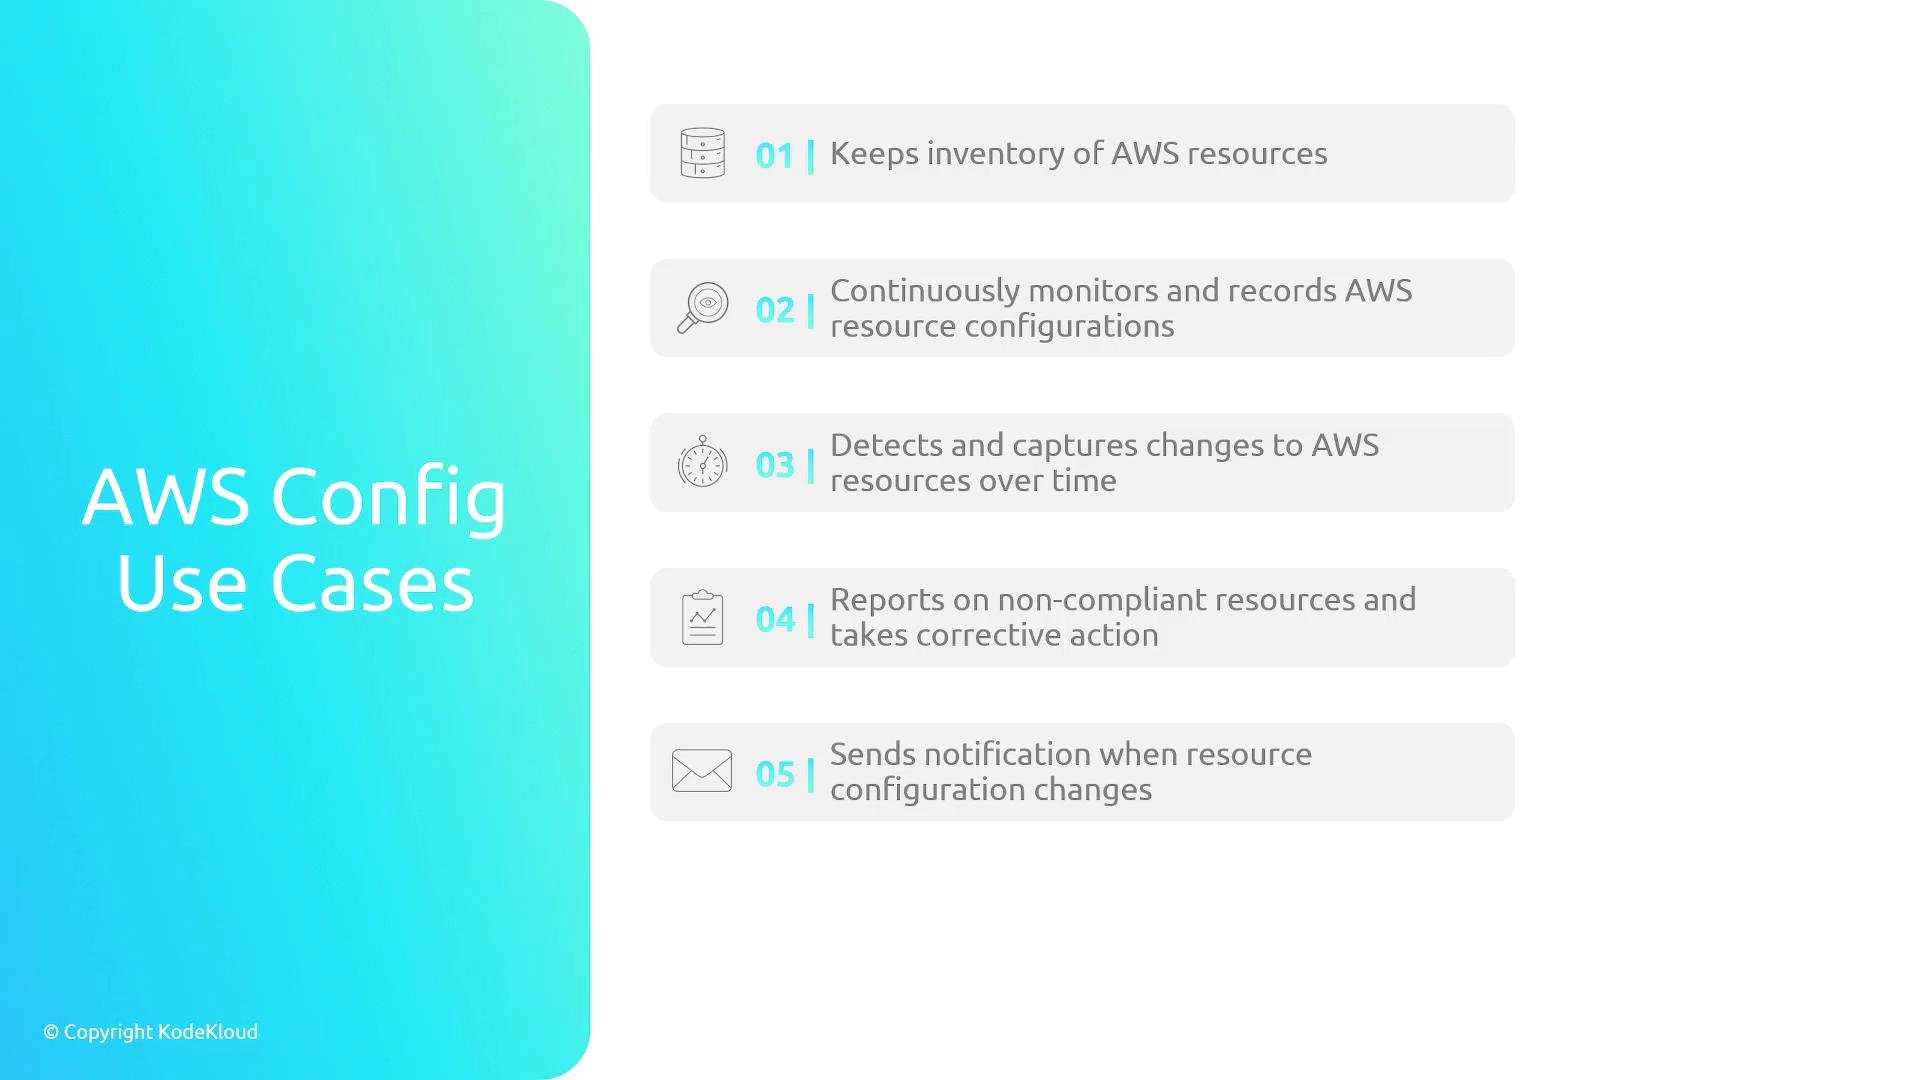
How AWS Config fits into your environment
When enabled for a region, AWS Config starts recording configuration items (CIs) for supported resource types. Each CI includes:- Resource configuration and metadata
- Relationships and dependencies to other resources
- A timestamped change history
- Store snapshots and historical CI data in an S3 bucket for long-term retention and auditing.
- Route change notifications to Amazon EventBridge or Amazon SNS to build alerting streams.
- Invoke AWS Lambda functions or Systems Manager Automation to filter, analyze, or remediate changes programmatically.
- S3 documentation: https://docs.aws.amazon.com/AmazonS3/latest/userguide/Welcome.html
- Lambda documentation: https://docs.aws.amazon.com/lambda/latest/dg/welcome.html
- EventBridge documentation: https://docs.aws.amazon.com/eventbridge/latest/userguide/what-is-amazon-eventbridge.html
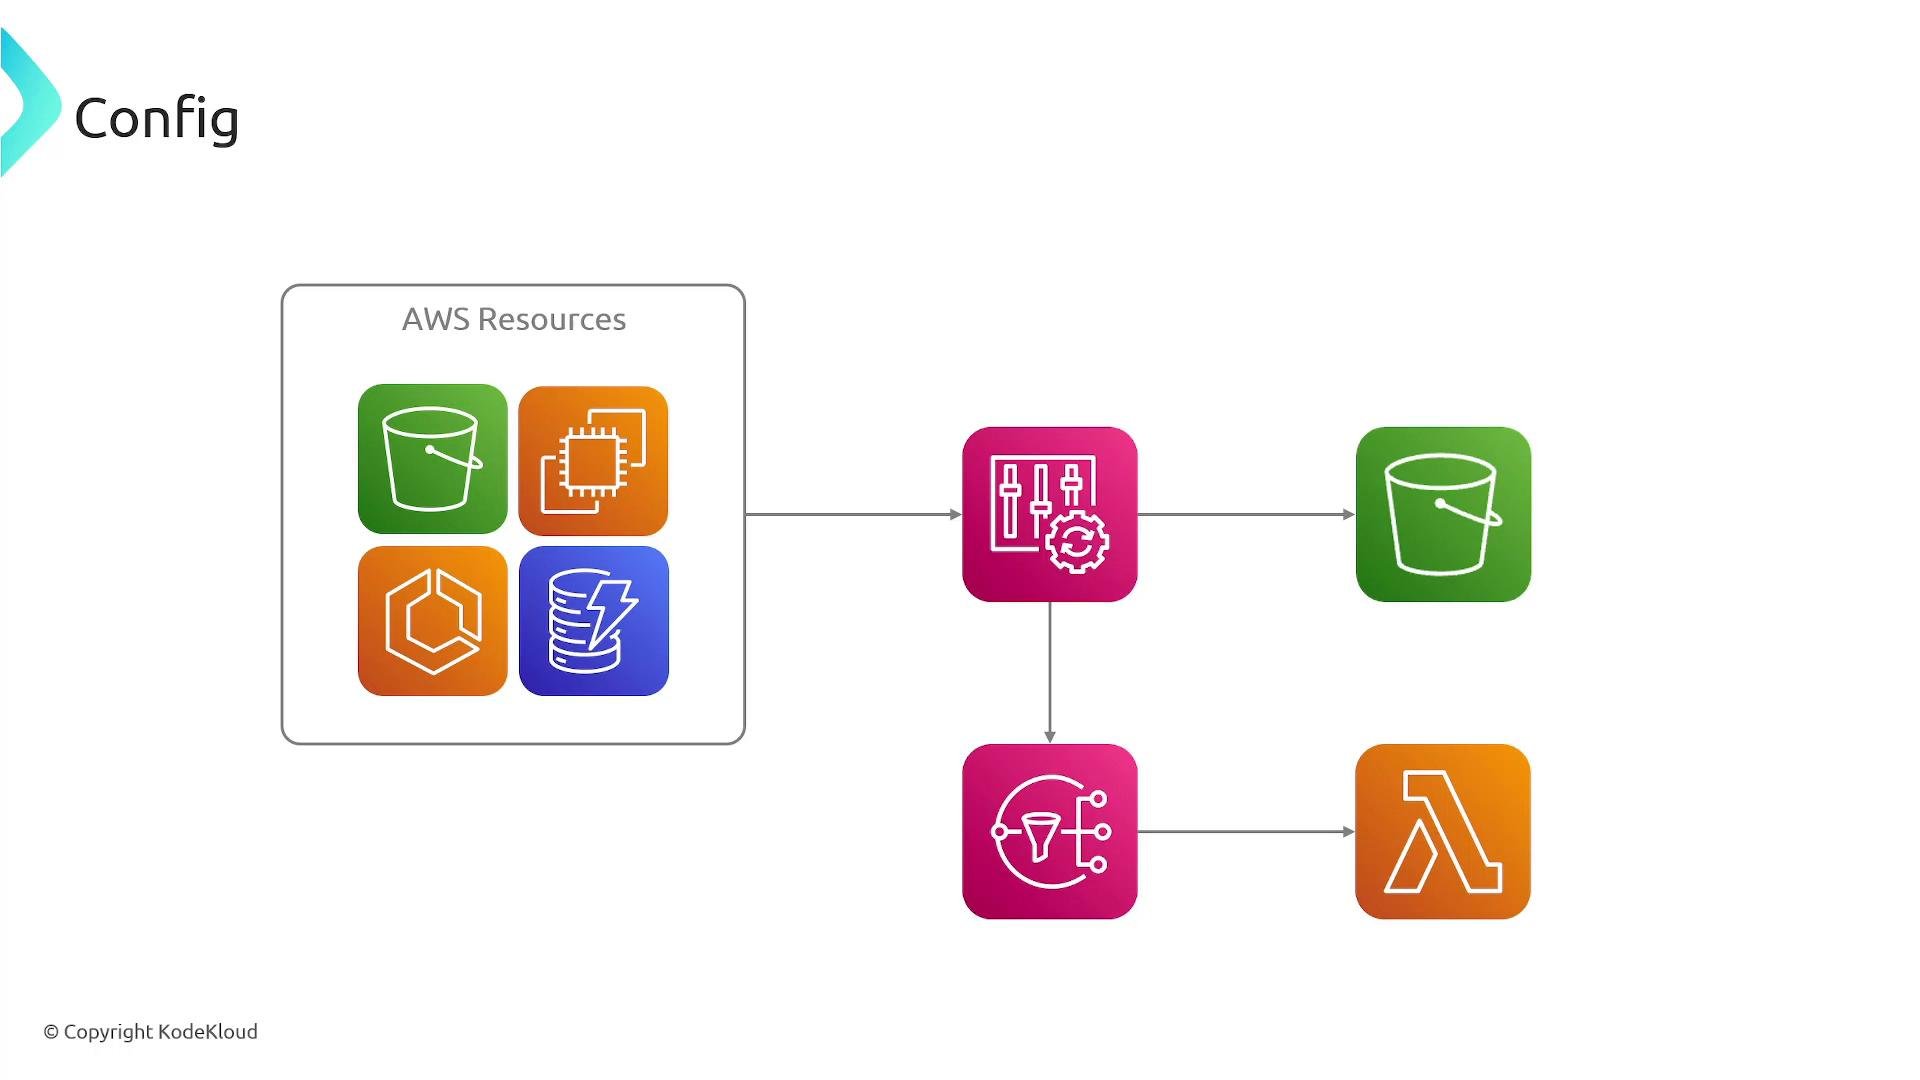
AWS Config rules
Rules evaluate whether resources meet your desired configuration or organizational policies. There are two primary rule types:
Rules support two evaluation modes:
- Configuration change-triggered: Evaluates when a relevant resource changes.
- Periodic (scheduled) evaluation: Runs on a schedule to catch drift or non-event-based issues.
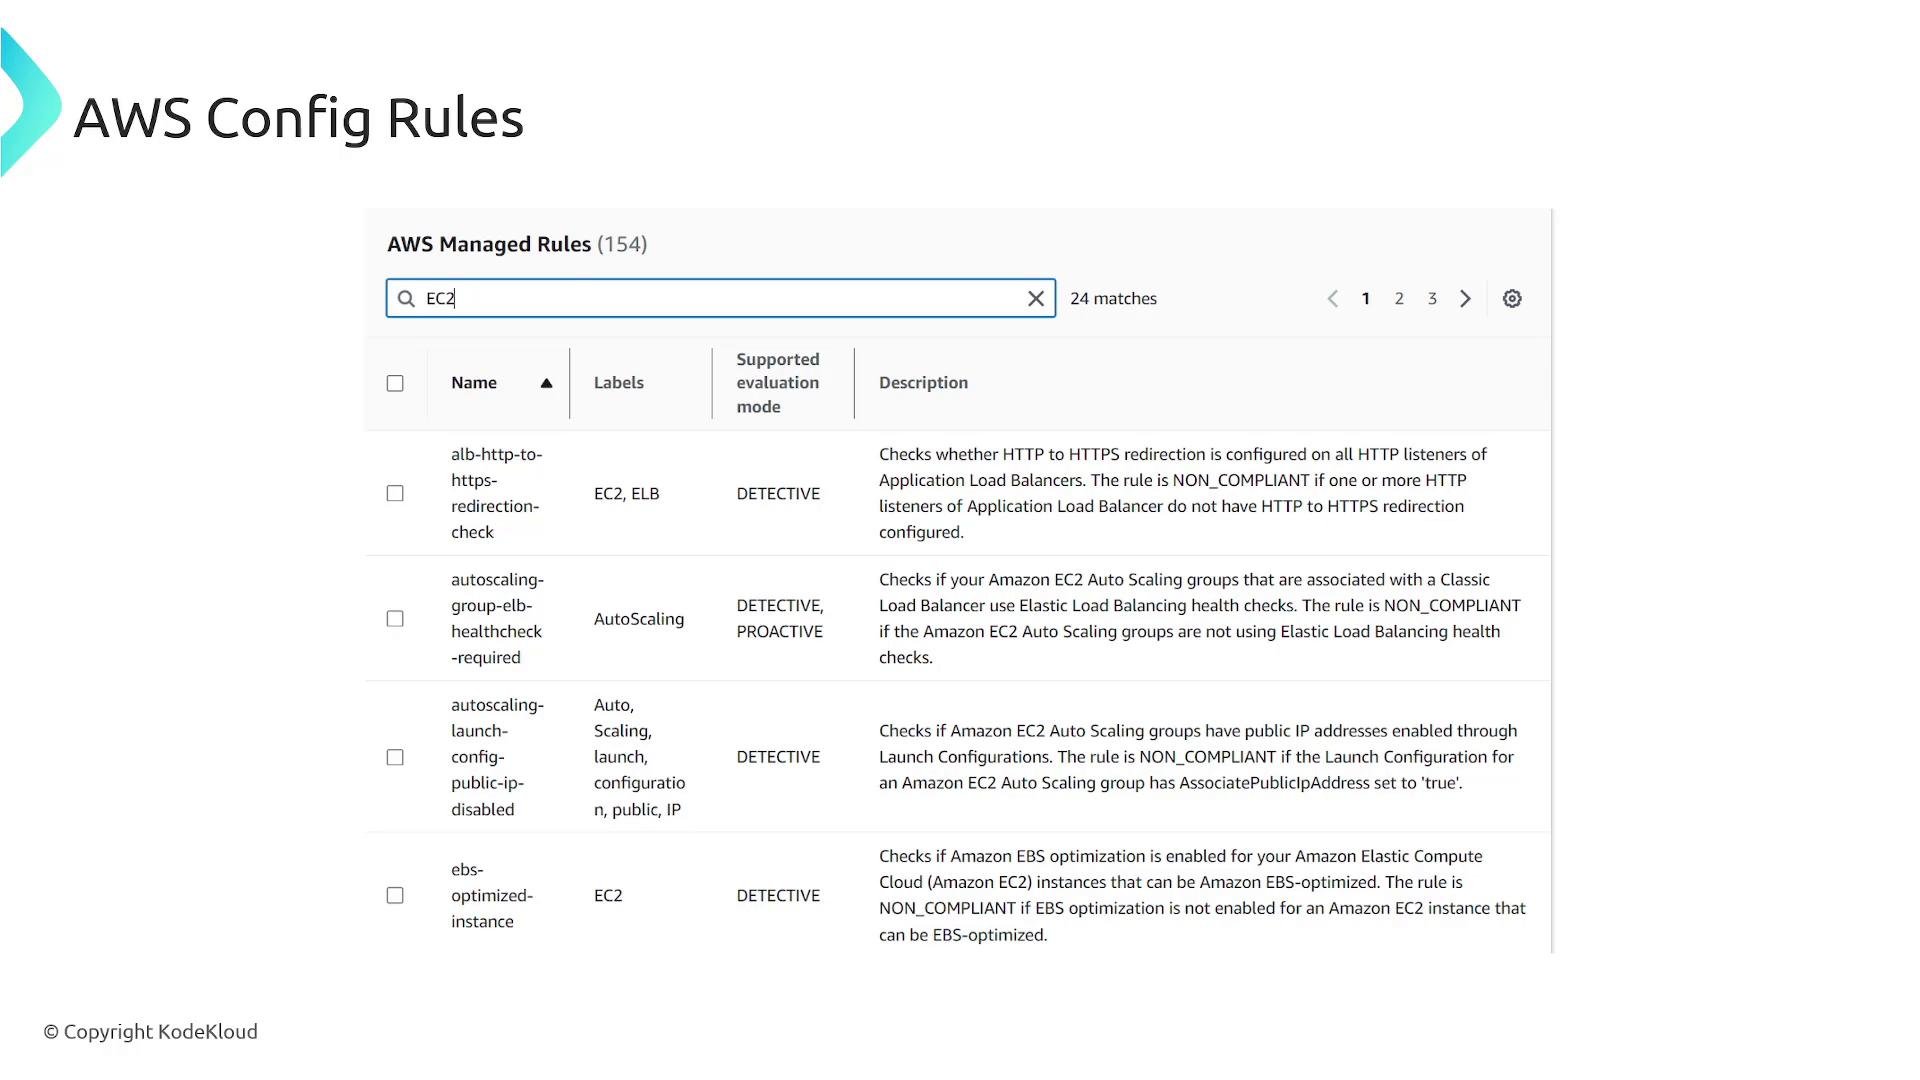
Example: ALB HTTP → HTTPS redirection rule
A common managed rule verifies that Application Load Balancer (ALB) HTTP listeners redirect traffic to HTTPS. If any HTTP listener lacks a redirect action to HTTPS, the rule reports the ALB as noncompliant. Enforcing this rule helps eliminate unencrypted HTTP traffic and enforce secure-by-default configurations.Use AWS managed rules to cover common security and best-practice checks quickly. For organization-specific or more complex checks, author custom rules (Lambda-backed). Combine Config rules with EventBridge, SNS, Lambda, or Systems Manager Automation to implement scalable alerting and automated remediation.
Links and references
- AWS Config Developer Guide
- AWS Lambda Developer Guide
- Amazon S3 User Guide
- Amazon EventBridge Developer Guide